
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/dustblessnotdust/cve-2024-53677-s2-067-thread
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubdustblessnotdust/cve-2024-53677-s2-067-thread

CVE-2024-53677-S2-067-thread

Multi-threaded exploit for CVE-2024-53677 (Apache Struts S2-067) with file upload endpoint targeting, path traversal testing, and custom JSP payload injection.

View Repository
2201 year agoNot yet reviewed
Share

Disclaimer

Do not use the related technologies in this article for illegal testing. Any direct or indirect consequences and losses caused by the dissemination or use of the information or tools provided in this article are solely the responsibility of the user. All adverse consequences arising from this are unrelated to the author. This article is for learning purposes only.

CVE-2024-53677-S2-067-thread

Proof of Concept, https://github.com/TAM-K592/CVE-2024-53677-S2-067/ The following versions of Apache Struts are affected: 2.0.0 to 2.5.33, 6.0.0 to 6.3.0.2

According to the recent history of the PoC over the past few days, the final version circulating online is the base64 obfuscated version, which emerged yesterday in Chinese (2024.12.18 noon). image
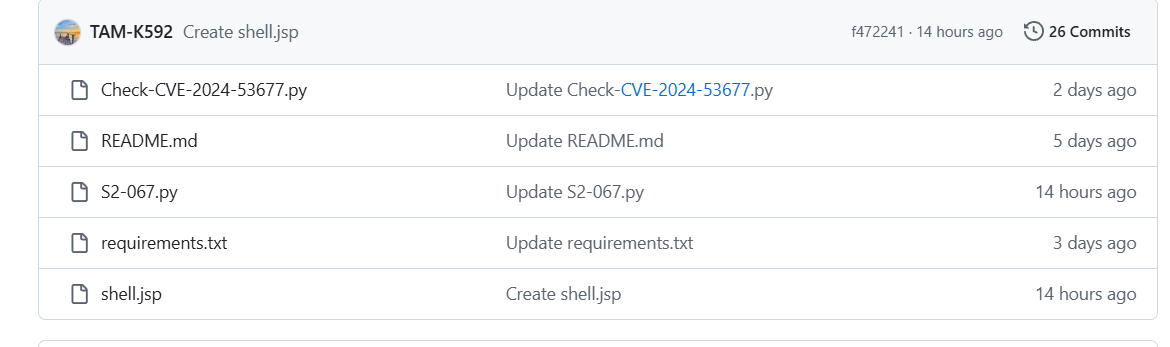
I made some modifications based on the original PoC

  • Changed to multi-threading
  • Explanation changed to Chinese
usage: CVE-2024-53677-S2-067-thread.py [-h] (-u URL | -f FILE) --upload_endpoint UPLOAD_ENDPOINT [--paths PATHS [PATHS ...]]
                                       [--filenames FILENAMES [FILENAMES ...]] [--payload PAYLOAD] [-s THREADS] [-o OUTPUT]

S2-067 Exploit - 多线程文件上传支持并从文件中读取URL

options:
  -h, --help            show this help message and exit
  -u URL, --url URL     目标基础URL(例如:http://example.com)
  -f FILE, --file FILE  包含目标基础URL的文件路径,每行一个URL
  --upload_endpoint UPLOAD_ENDPOINT
                        上传端点路径(例如:/uploads.action)
  --paths PATHS [PATHS ...]
                        路径遍历测试路径
  --filenames FILENAMES [FILENAMES ...]
                        自定义载荷文件名
  --payload PAYLOAD     自定义JSP载荷内容
  -s THREADS, --threads THREADS
                        使用的线程数量(默认: 5)
  -o OUTPUT, --output OUTPUT
                        输出成功URL的文件路径(默认:success.txt)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    930
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    349
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





