 delivr-to/detections
A home for detection content developed by the delivr.to team

This repo serves as a home for detection content developed by the delivr.to team.
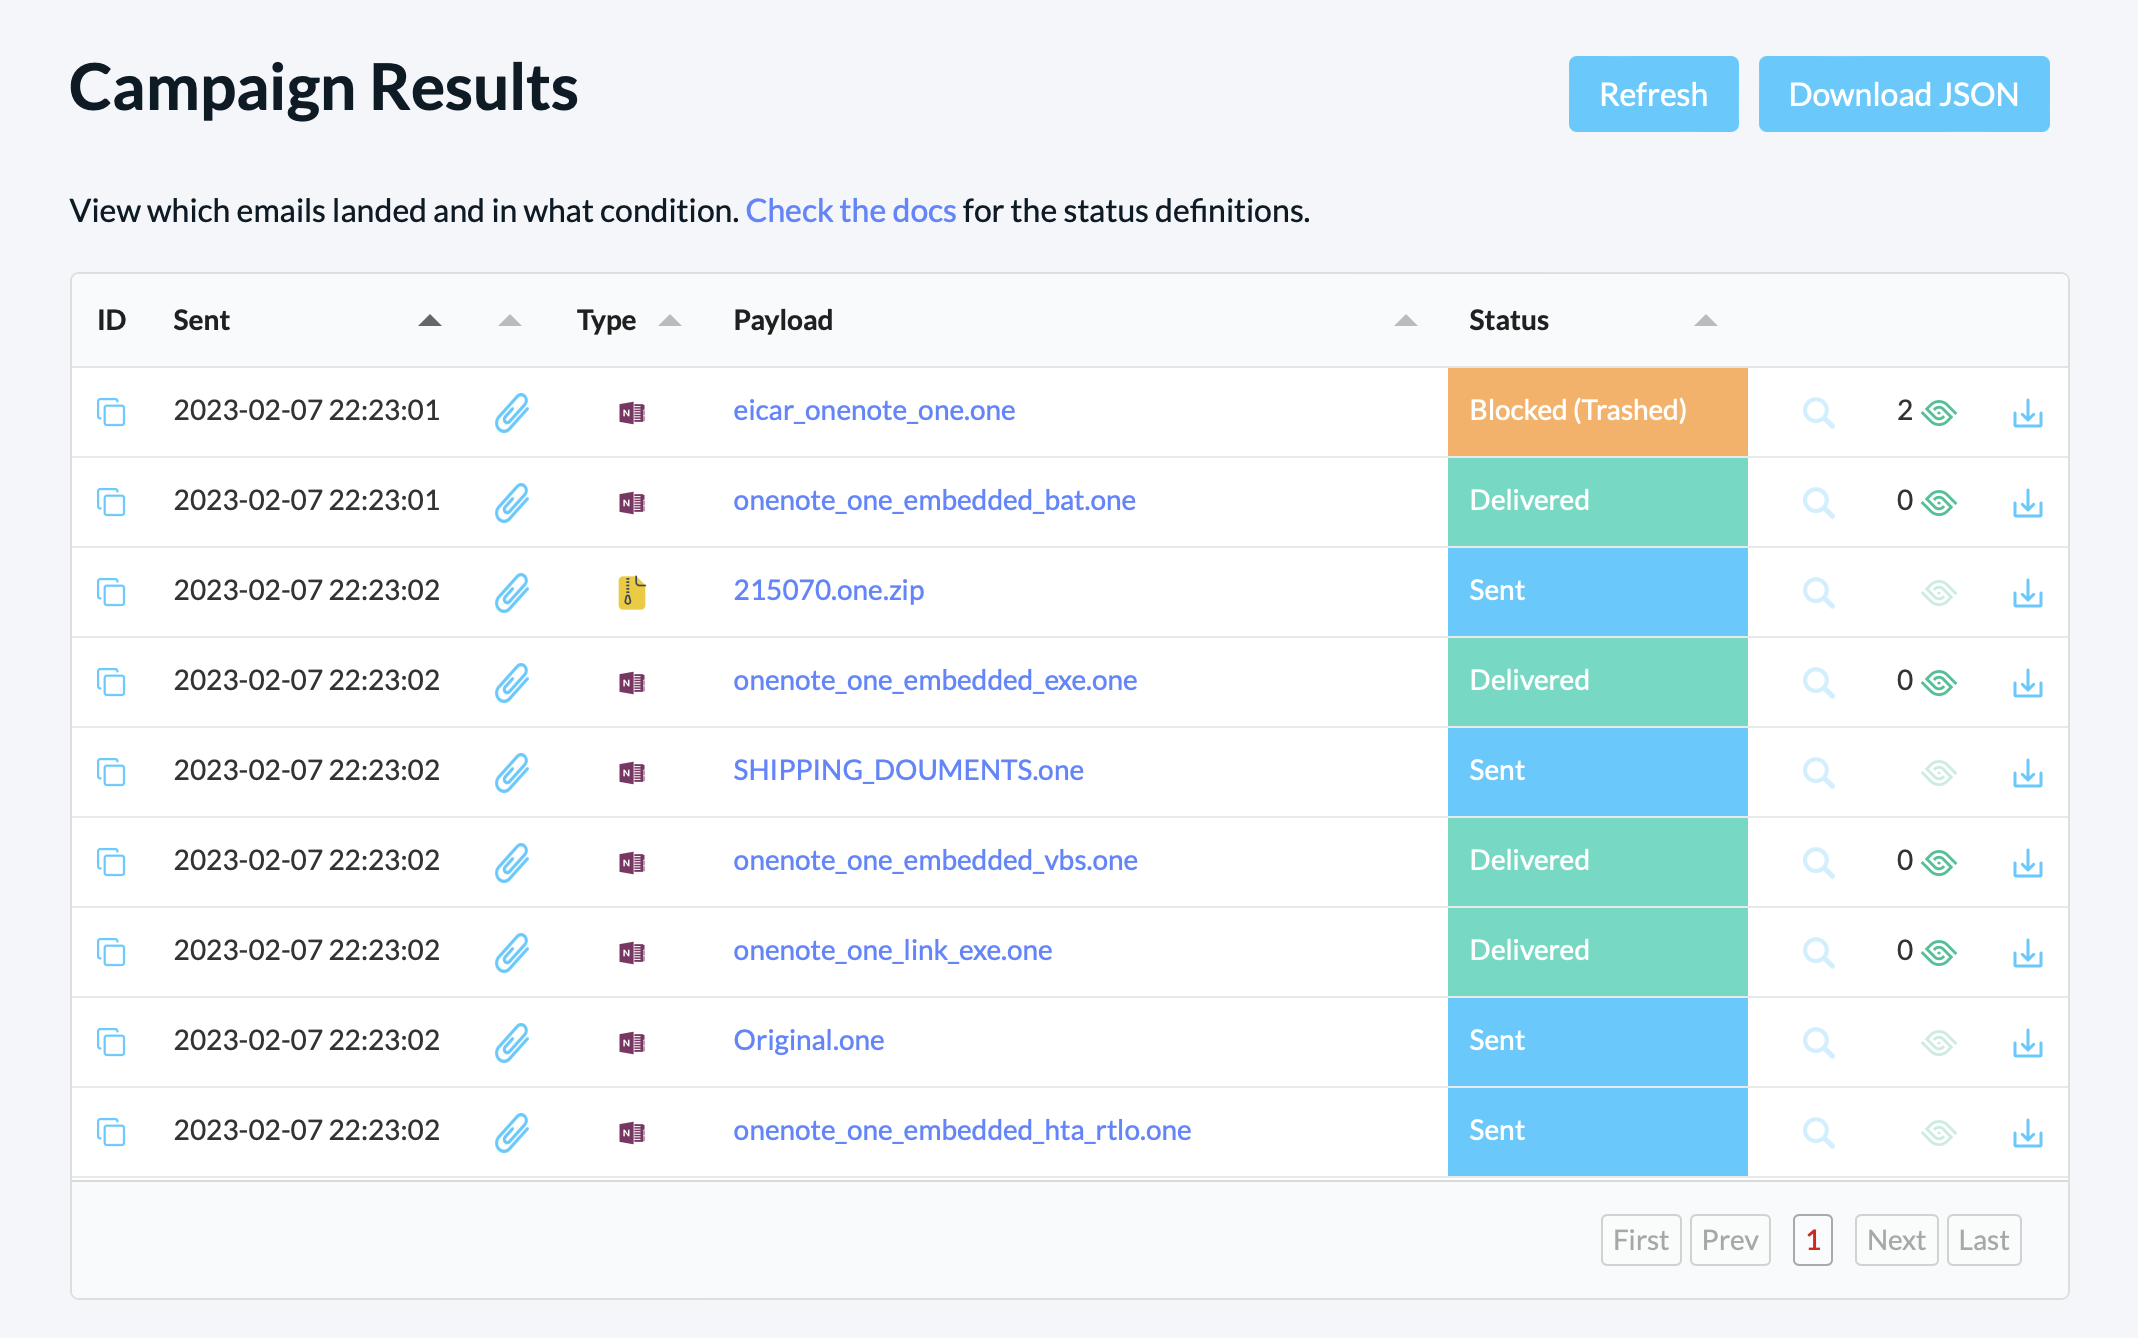
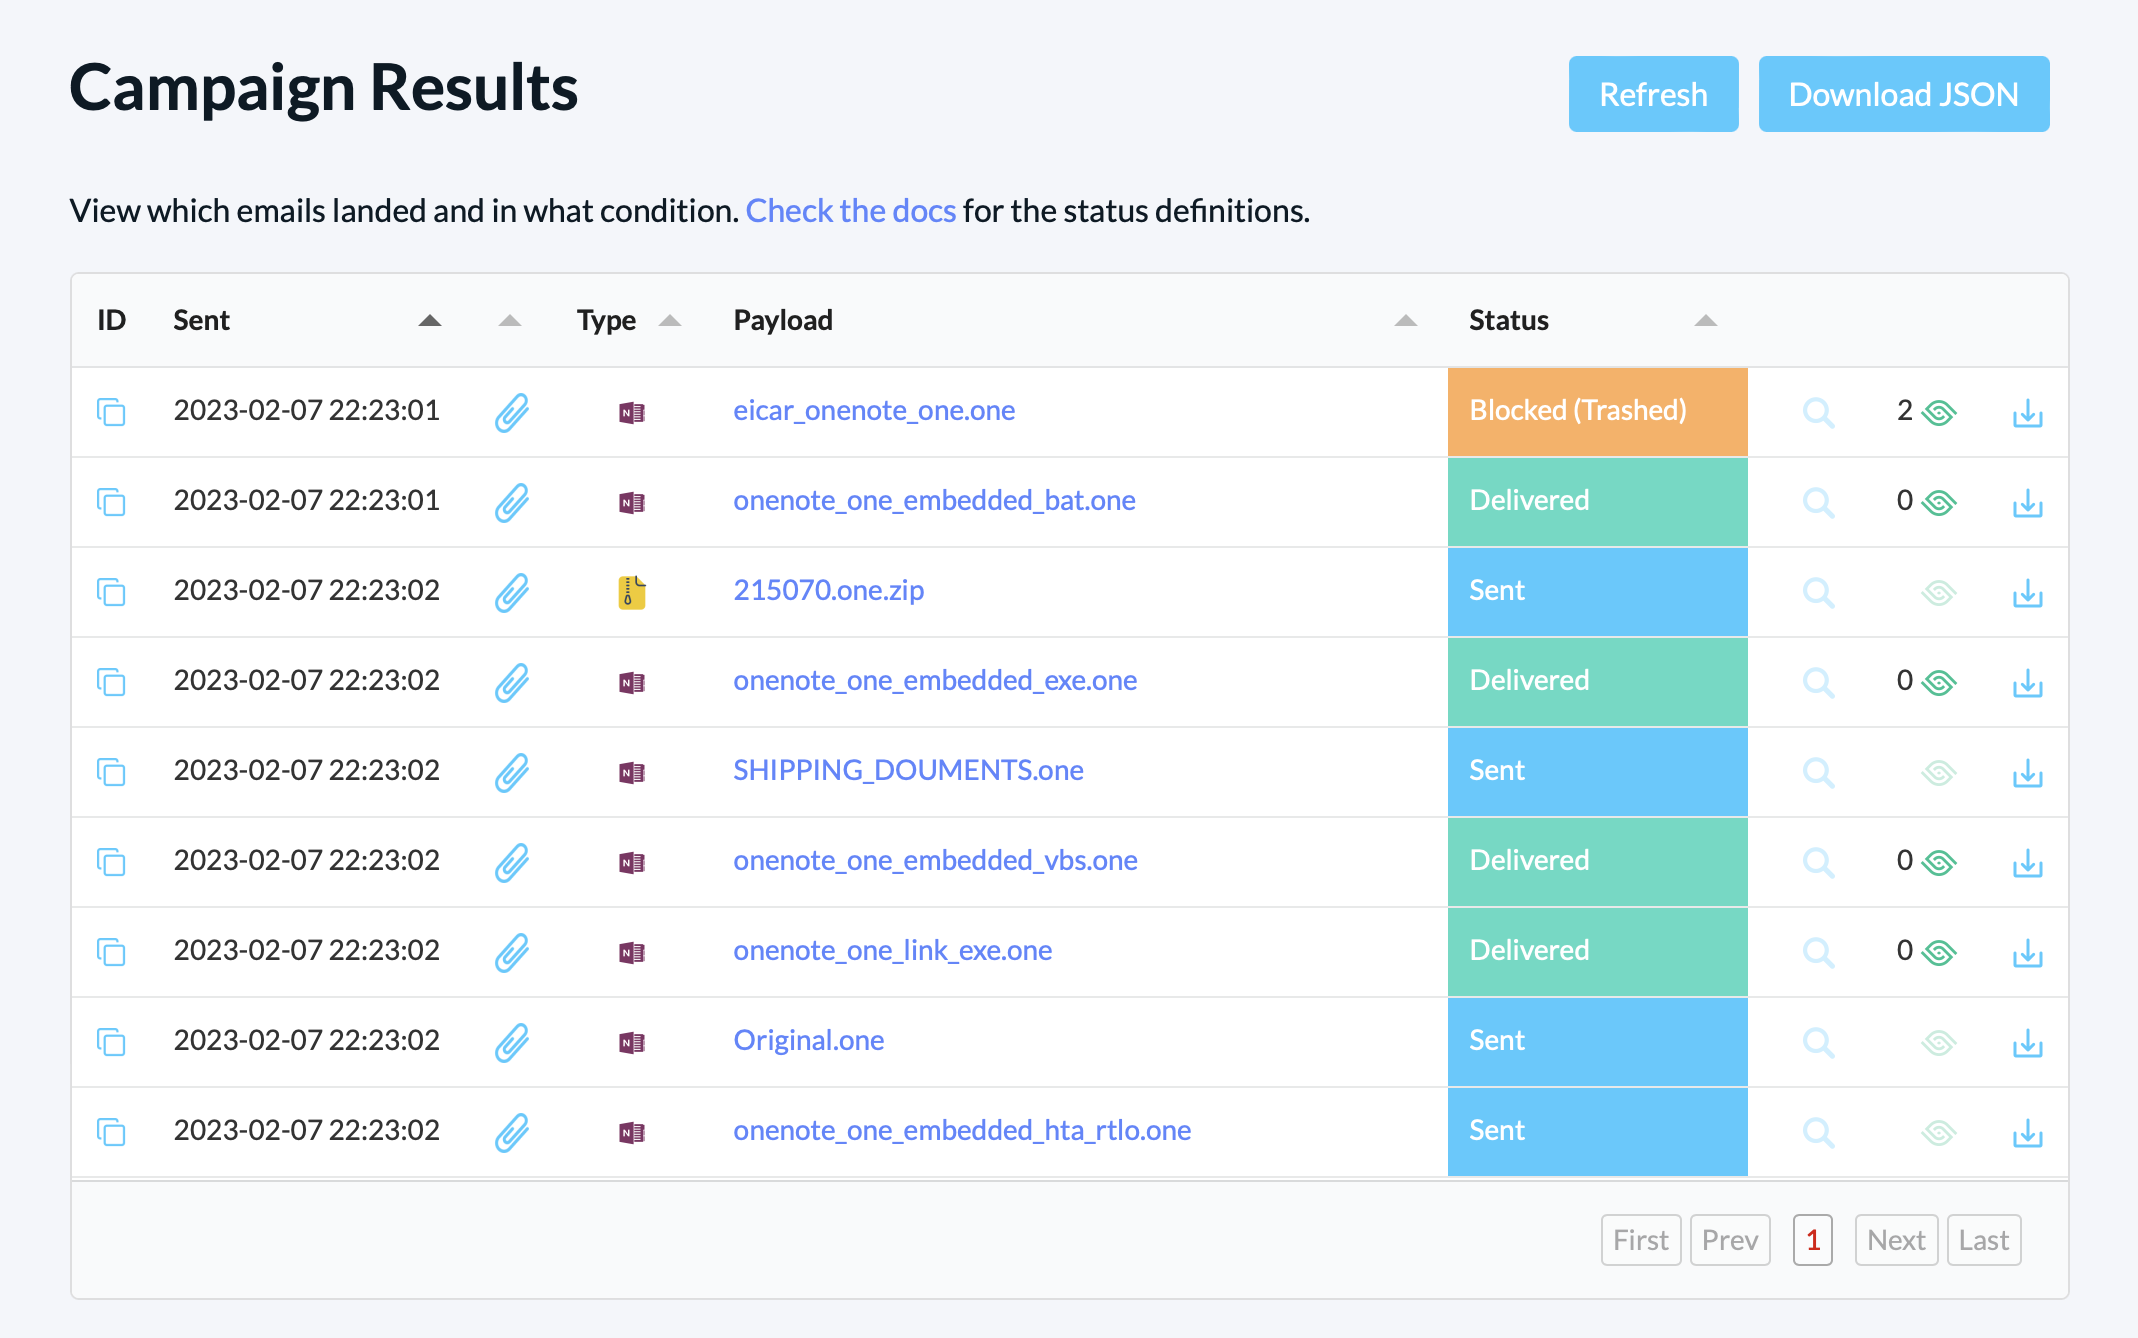
All rules present in this repo have corresponding payloads (linked in references and shown below) that can be used to test detection content.
The repo currently holds the following types of detections:
Below is the list of rules for Sublime Security, organised into General and Threat Intel specific folders.
You can also integrate delivr.to directly with Sublime as mentioned here and documented here.