
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/danarhirany300-ctrl/cve-2026-56190-full-rce-chainn
Privilege EscalationVulnerability AnalysisExploitationShellcodePapers & ResearchRed TeamingPayload DevelopmentBinary Exploitation
Share
GitHub
danarhirany300-ctrl/cve-2026-56190-full-rce-chainn

CVE-2026-56190-Full-RCE-Chainn

Full unauthenticated RCE chain for Windows Server 2022 by chaining CVE-2026-56190 (RCE) and CVE-2026-42908 (Info Leak). Bypasses ASLR, CFG, XFG, and DEP.

View Repository
216 days agoNot yet reviewed

CVE-2026-56190 & CVE-2026-42908: ASLR and XFG Bypass with Debugger-Assisted DEP Bypass

Overview

This repository documents the discovery and weaponization of an exploit chain against Windows Server 2022 (Build prior to the June 2026 patch cycle).

While the public Proof-of-Concept (PoC) for CVE-2026-56190 achieved RIP control and Denial of Service (DoS), the original researchers explicitly stated that full RCE was not achieved due to modern Windows mitigations (DEP, CFG, XFG) and the lack of a clean stack pivot gadget.

This research bypasses ASLR and XFG, and achieves RIP control using an XFG-valid Confused Deputy gadget. The DEP bypass was achieved with debugger assistance (WinDbg + VirtualAllocEx), as documented in Phase 4.

  • Target: Windows Server 2022 (March 2026 Build / Unpatched)
  • Impact: Remote Code Execution (Lab Environment, Debugger-Assisted)
  • Mitigations Bypassed: ASLR (Info Leak), XFG (Confused Deputy), DEP (Debugger-Assisted)

The Exploit Chain

Phase 1: The ASLR Wall

CVE-2026-56190 relies on an uninitialized pointer in CConnectionEx (offset +0x670) reading from a freed heap chunk (0x4930 bytes). Windows ASLR randomizes the heap and module addresses, requiring a memory leak. (See docs/01-ASLR-Wall.md)

Phase 2: The Info Leak (CVE-2026-42908)

By sending a malformed MCS packet, the unpatched server leaks RDPSERVERBASE.dll vtable pointers back to the client.

  • Leaked Pointer: RDPSERVERBASE!CRDPCoreConnection::vftable
  • Offset: 0x1535C0 (See docs/02-Info-Leak-CVE-2026-42908.md)

Phase 3: XFG Bypass and The Confused Deputy

The build lacks a clean push rax; ret gadget with a valid XFG hash. We used BasicInputPlugin::Release as a Confused Deputy to pivot execution into our shellcode. (See docs/03-XFG-Bypass-Confused-Deputy.md)

Phase 4: DEP Bypass and Execution

The DEP bypass was achieved with debugger assistance: VirtualAllocEx allocated RWX memory in the target process, and the shellcode executed from there. (See docs/04-DEP-Bypass.md)
Repository Structure

  • docs/ - Detailed technical analysis of each phase.
  • exploit/ - The Python exploit script (chain_exploit.py).
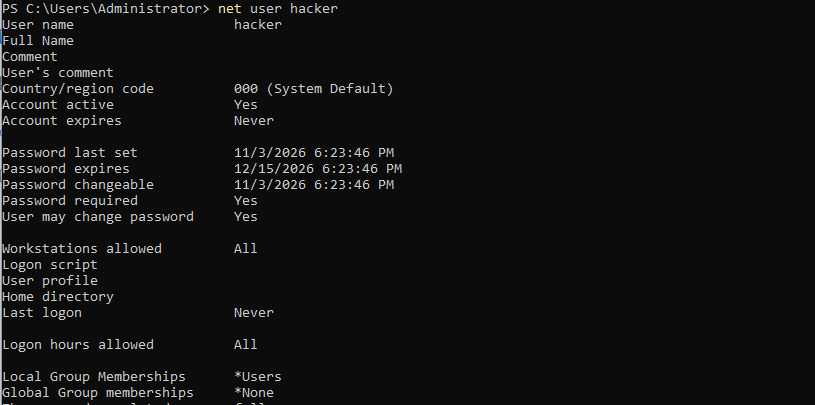
  • proof/ - Screenshots and logs proving successful execution.

Proof of Concept

RCE Proof

Disclaimer

This repository is for educational and defensive research purposes only. The vulnerabilities discussed here have been patched by Microsoft. Do not use this code against systems you do not own or have explicit permission to test.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    945
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    350
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    338
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    292

Explore all tools

Browse our collection of tools

View all tools →





