Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/cybertechajju/r2c-cve-2025-55182-66478
ReconnaissanceVulnerability ScannersPayload GenerationExploitationWeb Application ExploitationInformation GatheringPenetration TestingCommand and ControlLearning & Education
Share
Red Teaming
Payload Development
GitHubcybertechajju/r2c-cve-2025-55182-66478

R2C-CVE-2025-55182-66478

πŸ”₯ React2Shell Toolkit - CVE-2025-55182 & CVE-2025-66478

View RepositoryWebsite
242811 months agoReviewed by Kitploit

πŸ”₯React2Shell Toolkit-CVE-2025-55182 & CVE-2025-66478

React2Shell Banner CVE-2025-55182 CVE-2025-66478 CVSS

🚨 Critical RCE in React Server Components & Next.js 🚨

Professional Red Team Toolkit for CVE-2025-55182 Detection & Exploitation

πŸ” Features β€’ ⚑ Quick Start β€’ πŸ“š Documentation β€’ 🀝 Connect


🎯 About CVE-2025-55182 & CVE-2025-66478

πŸ› What is React2Shell?

React2Shell is a critical unauthenticated Remote Code Execution (RCE) vulnerability affecting React Server Components (RSC) and Next.js applications.

CVE IDComponentCVSS ScoreImpact
CVE-2025-55182React Server Components10.0 πŸ”΄Complete Server Takeover
CVE-2025-66478Next.js Server Actions10.0 πŸ”΄Full System Compromise

🎭 Attack Vector

// Attacker sends malicious Flight protocol payload
POST / HTTP/1.1
Next-Action: exploit
Content-Type: multipart/form-data

{"__proto__": "pollution", "then": "gadget_chain"} 
    ↓
Unsafe Deserialization
    ↓
Prototype Pollution
    ↓
πŸ’₯ Remote Code Execution πŸ’₯

🎯 Affected Versions

  • React: 19.0.0, 19.1.0, 19.1.1, 19.2.0
  • Next.js: 15.x, 16.x (with App Router)
  • Frameworks: React Router, Waku, Vite RSC, Parcel, RedwoodSDK

βœ… Patched Versions

  • React: 19.0.1+, 19.1.2+, 19.2.1+
  • Next.js: 15.0.5+, 15.1.9+, 15.2.6+, 16.0.7+

πŸ“Έ Proof of Concept

🎯 Live Exploitation Demonstrations

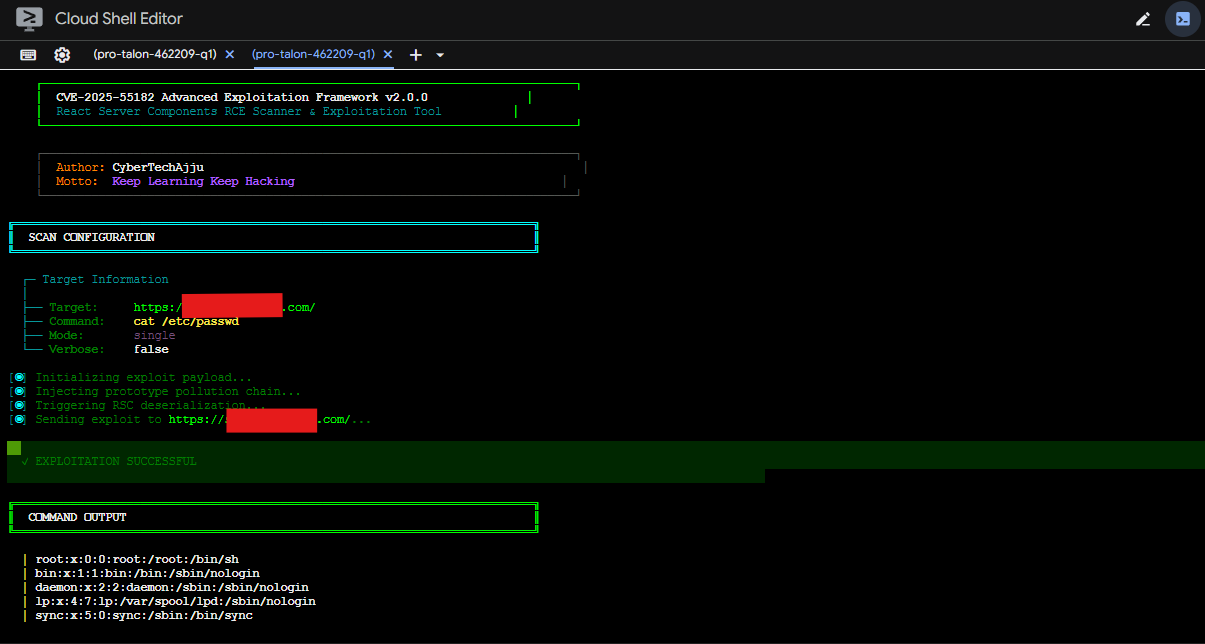
πŸ”“ Successful RCE Exploitation

POC 3 - RCE Demonstration

Command execution via React2Shell vulnerability

πŸ’₯ Vulnerability Confirmation

POC 4 - Exploitation Proof

Server compromise through Flight protocol

⚠️ These screenshots demonstrate real exploitation in controlled environments
Use responsibly and only with proper authorization


πŸ› οΈ Toolkit Components

This repository contains 4 professional-grade tools for CVE-2025-55182 detection and exploitation:

πŸ” Nuclei Template

Advanced Scanner

Nuclei

βœ… 5 Payloads
βœ… Zero False Positives
βœ… Math Validation
βœ… Batch Scanning

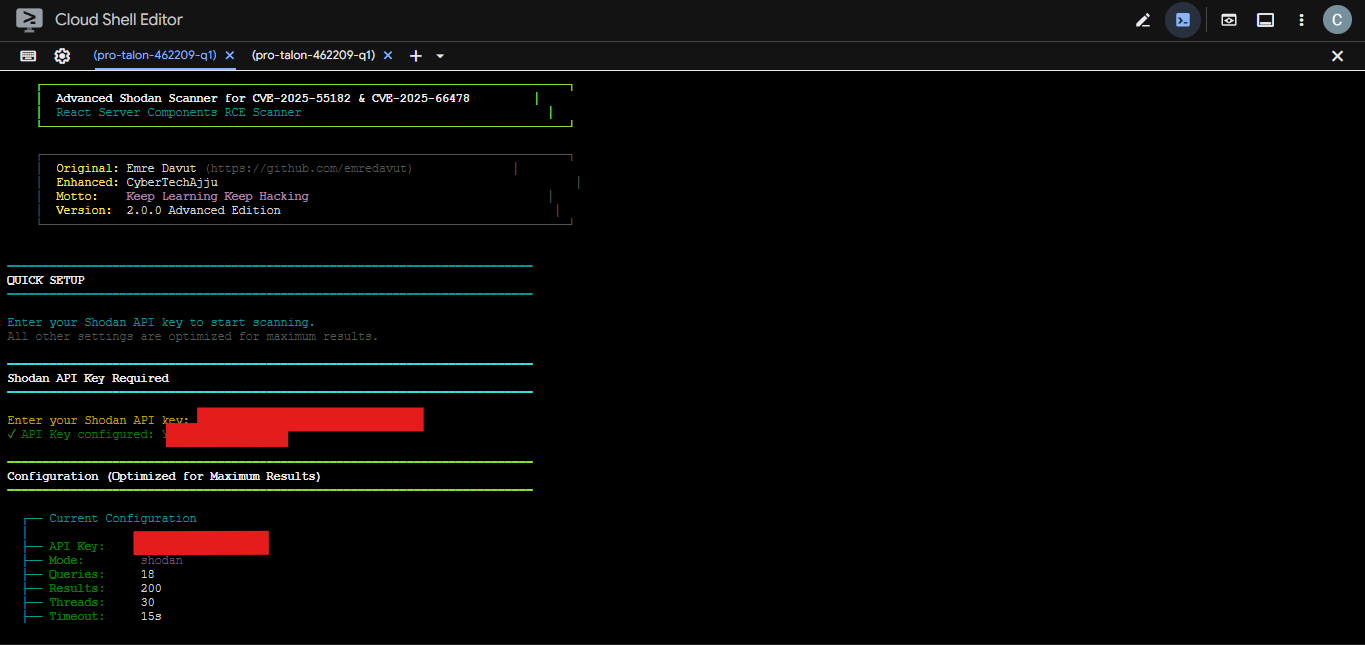
🐍 Shodan Scanner

Target Discovery

Python

βœ… Automated Search
βœ… Mass Scanning
βœ… 50+ Shodan Queries
βœ… Interactive Wizard

πŸ’» Bash Exploit

CLI Framework

Bash

βœ… 8 Predefined Payloads
βœ… Interactive Mode
βœ… Multi-Target Support
βœ… Cyberpunk UI

πŸ”§ Burp Extension

Manual Testing

Burp

βœ… 30+ Payloads
βœ… Active + Passive Scan
βœ… GUI Interface
βœ… Collaborator Integration


⚑ Quick Start

πŸ“¦ Installation

# Clone the repository
git clone https://github.com/cybertechajju/R2C-CVE-2025-55182-66478.git
cd R2C-CVE-2025-55182-66478

# Install Python dependencies
pip install -r requirements.txt
pip install -r exploits/requirements.txt

πŸš€ Usage Examples

1️⃣ Nuclei Scanner (Fastest Detection)

# Scan single target
nuclei -t nuclei-templates/cve-2025-55182.yaml -u https://target.com

# Scan multiple targets
nuclei -t nuclei-templates/cve-2025-55182.yaml -l targets.txt

2️⃣ Shodan Scanner (Mass Discovery)

# Interactive wizard mode
python exploits/shodan_scanner_advanced.py

# Or with API key directly
python exploits/shodan_scanner_advanced.py --api YOUR_SHODAN_API_KEY

3️⃣ Bash Exploit (Direct Exploitation)

# Interactive mode
bash exploits/scanner_advanced.sh -i

# Quick exploitation
bash exploits/scanner_advanced.sh -d https://target.com -p 2

4️⃣ Burp Extension (Manual Testing)

  1. Open Burp Suite β†’ Extensions β†’ Add
  2. Select burp-extension/React2Shell_Burp.py
  3. Check "React2Shell Pro" tab for GUI

πŸ“ Repository Structure

cve-2025-55182/
β”œβ”€β”€ πŸ“‚ nuclei-templates/          # Nuclei YAML templates
β”‚   └── cve-2025-55182.yaml       # Advanced detection template
β”œβ”€β”€ πŸ“‚ exploits/                  # Exploitation tools
β”‚   β”œβ”€β”€ shodan_scanner_advanced.py   # Shodan mass scanner
β”‚   β”œβ”€β”€ scanner_advanced.sh          # Bash exploitation framework
β”‚   └── requirements.txt             # Python dependencies
β”œβ”€β”€ πŸ“‚ burp-extension/            # Burp Suite extension
β”‚   β”œβ”€β”€ React2Shell_Burp.py       # Main extension (30+ payloads)
β”‚   β”œβ”€β”€ payloads.json             # Payload library
β”‚   └── detection_rules.json      # Detection patterns
β”œβ”€β”€ πŸ“‚ burp bechek/               # BCheck files for Burp Scanner
β”‚   β”œβ”€β”€ CVE-2025-55182-React2Shell-Active.bcheck
β”‚   └── CVE-2025-66478-NextJS-React2Shell-Active.bcheck
└── πŸ“„ README.md                  # This file

🎨 Features Showcase

✨ Nuclei Template Features

  • βœ… 5 Exploitation Payloads: Linux, Windows, alternative endpoints
  • βœ… Mathematical Validation: 41 * 271 = 11111 (zero false positives)


  • βœ… Multi-Stage Detection: Framework fingerprinting β†’ RSC discovery β†’ RCE validation
  • βœ… Multiple Matchers: Math validation, error patterns, execution proof

πŸ”₯ Shodan Scanner Features

  • βœ… 50+ Shodan Queries: Maximum vulnerable target discovery
  • βœ… Smart Extraction: Both IPs and domain names
  • βœ… Interactive Wizard: Guided setup for beginners
  • βœ… Cyberpunk UI: Neon-themed terminal with animations
  • βœ… Batch Scanning: Multi-threaded target scanning
  • βœ… JSON Reports: Detailed vulnerability reports

πŸ’ͺ Bash Exploit Features

  • βœ… 8 Predefined Payloads: System info, AWS metadata, container detection, etc.
  • βœ… Interactive Mode: Menu-driven exploitation
  • βœ… Multi-Target Scanning: Scan from file list
  • βœ… Rich Output: Color-coded results with animations
  • βœ… Error Analysis: Detailed failure diagnostics

πŸš€ Burp Extension Features

  • βœ… 30+ Payload Library: Organized in 5 categories
  • βœ… Dual Scanners: Passive monitoring + active exploitation
  • βœ… 8-Tab GUI: Dashboard, scanner, exploitation, payloads, results, config, about
  • βœ… Burp Collaborator: Out-of-band RCE confirmation
  • βœ… Export Options: JSON and CSV reports
  • βœ… Confidence Scoring: Certain (95%), Firm (75%), Tentative (50%)

πŸ“š Documentation

πŸ“– Detailed Guides

  • Nuclei Template Usage
Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    962
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    348
  • 4

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    344
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    297

Explore all tools

Browse our collection of tools

View all tools β†’