
 completetech-security/tinypool-options-rce-check
Offline Tinypool evidence checker for CVE-2026-104849. Worker-pool package and options evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.





Offline evidence checker for CVE-2026-104849 — Tinypool worker-options prototype-pollution gadget (alias GHSA-85c8-ppgw-ccpr).
It compares operator-reported tinypool versions with the reviewed advisory rules and writes CSV, JSON or HTML reports. It is version-evidence triage only: it never contacts websites, imports application code, runs a package manager, or executes exploit payloads, and exploitability is always reported as not_tested.
This repository covers only CVE-2026-104849. The checker does not scan deployed systems, fetch package inventories, analyze source code, or test exploitability. It reads versions and optional observations that you supply and reports what those claims imply under the reviewed rules.
A public URL cannot provide installed package inventory. Obtain each deployed package instance's exact version and provenance; declarations and local workstation versions are not deployment evidence. Use it only with inventories you are authorized to assess.
tinypool_options_rce_check.py can be copied and run on its own; no companion repository is needed at runtime..github/workflows/tests.yml) runs the local-only tests and --help on Python 3.10 and 3.14 on Ubuntu and Windows.# Assess one reported version; the default format is csv
python tinypool_options_rce_check.py --version 2.1.2 --format json
# Assess a JSON inventory and save an HTML report to a new file
python tinypool_options_rce_check.py --inventory examples/inventory.example.json --format html --output report.html
# Assess a CSV list and exit 1 if any entry is potentially affected
python tinypool_options_rce_check.py --csv-list inventory.csv --fail-on-finding
# Show all options, then run the local tests
python tinypool_options_rce_check.py --help
python -m unittest -v
examples/inventory.example.json is a synthetic entry (2.1.2, label example-package-instance, all observations null). Without --output, the report goes to stdout.
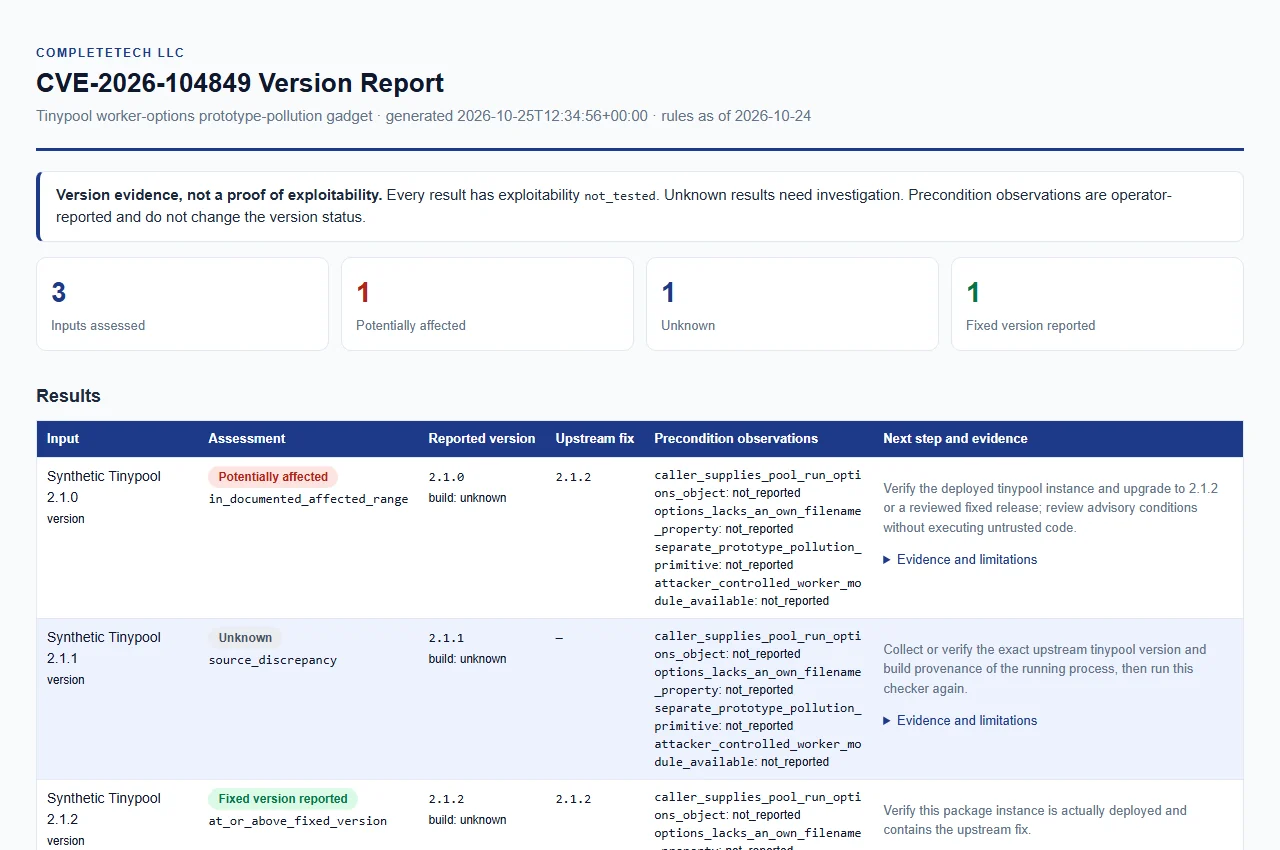
Open the synthetic example report. Example data only; this is not a live assessment.
The primary advisory and reviewed database were retrieved on 2026-10-24 (rules_as_of in every report).
| Example reported version | Result |
|---|---|
| 2.0.9 | potentially_affected |
| 2.1.0 | potentially_affected |
| 2.1.1 | unknown |
| 2.1.2 | fixed_version_reported |
| 2.1.3 | fixed_version_reported |
| 2.2.0 | unknown |
| 3.0.0 | unknown |
0.0.0 through 2.1.0 inclusive.2.1.x, fixed in 2.1.2. Future lines remain unknown rather than extrapolating a patch claim.2.1.1. The maintainer range (<=2.1.0) and the GitHub Reviewed range (<2.1.2) disagree there, so it is reported as unknown and never as clean. Obtain maintainer evidence.pool.run(task) alone is not the documented trigger.Only plain stable MAJOR.MINOR.PATCH versions are compared. A single leading v and surrounding ASCII whitespace are accepted.
| Status | Meaning |
|---|---|
potentially_affected | The reported version is in the documented affected interval. This is not confirmed exploitability: preconditions and exploitability were not established. |
fixed_version_reported | The reported version is at or above the fix within the reviewed 2.1.x line. This describes a version claim only; it never attests an installed patch or safety. |
unknown | Evidence is insufficient to classify. This is neither a clean result nor a finding. |
Every result retains exploitability: not_tested. evidence_type is operator_reported_version; evidence_confidence is insufficient for unknown and low otherwise.
Each result also carries a more specific version_status:
version_status | Status | Cause |
|---|---|---|
in_documented_affected_range | potentially_affected | Version is within 0.0.0–2.1.0. |
at_or_above_fixed_version | fixed_version_reported | Version is 2.1.2 or later within 2.1.x. |
source_discrepancy | unknown | Version is 2.1.1, where the sources disagree. |
outside_reviewed_range | unknown | Version is outside the affected interval and the reviewed fixed line; no safety or other-vulnerability conclusion is made. |
vendor_build_unverified | unknown | build_source is a custom or vendor build, which needs independent patch evidence. |
qualified_version_unverified | unknown | Prerelease, nightly/rc or suffixed versions need vendor verification. |
unrecognized_or_partial_version | unknown | Version text is malformed or partial. |
version_not_disclosed | unknown | No version was reported. Missing metadata does not establish that the runtime is unaffected. |
Operational failures (bad arguments, unreadable or invalid input, output errors) are not assessment results. They exit with status 2 and are never reported as unknown or clean.
The advisory describes conditions that must hold for the gadget to matter. You can record your own observations of them:






