 completetech-security/php2shell-check
Passive PHP2Shell (CVE-2026-109618, CVE-2026-109619) exposure checker with branded HTML reports. Single-file Python, no dependencies, no exploit payloads.





Passive triage for websites that advertise a PHP version affected by PHP2Shell
CVE-2026-109618 · CVE-2026-109619 · single-file, dependency-free
php2shell-check reads the PHP version a website already advertises in its public response headers and compares it with the official upstream fix for each PHP branch. It sends no exploit payloads, respects robots.txt, and reports uncertainty honestly: a hidden, conflicting or vendor-built version is unknown, never "safe".
robots.txt, with verified TLS and a descriptive User-Agent.php2shell_exploitability=not_tested.wordpress_check.py uses only the Python standard library. The filename and default User-Agent are retained for compatibility; WordPress is not required for the PHP2Shell assessment.[!IMPORTANT] Potential exposure is not confirmed exploitability. Headers cannot reveal the PHP SAPI, vendor backports, or real patch status. Treat every result as a prompt for an administrator to check. Check only websites you are authorized to assess.
Requires Python 3.10 or newer on Windows, macOS, or Linux. There is nothing to install: no pip package, API key, browser, or database. Use python3 where that is how Python is named on your system.
git clone https://github.com/CompleTetech-Security/php2shell-check.git
cd php2shell-check

python wordpress_check.py example.com                       # CSV to the terminal
python wordpress_check.py --input websites.txt --format html --output report.html
websites.txt is a text file with one authorized website per line; websites.example.txt shows the format using reserved example domains. See Usage for input rules and options.
Every website result includes php2shell_status:
| Status | Meaning |
|---|---|
potentially_affected | A complete, unqualified PHP version below its branch's fix is advertised. Ask the administrator to verify. |
fixed_version_reported | The advertised version meets its branch's fix. This is a reported version, not a verified patch or clean bill of health. |
unknown | Version hidden, partial, conflicting, pre-release, vendor-qualified, or outside the covered 8.2–8.5 branches. |
| PHP branch | 8.2 | 8.3 | 8.4 | 8.5 |
|---|---|---|---|---|
| Fixed in | 8.2.35 | 8.3.36 | 8.4.27 | 8.5.12 |
Thresholds come from the PHP project's advisories for CVE-2026-109618 and CVE-2026-109619, checked on 2026-10-21. The table is embedded in the script and is not refreshed from the internet. Distributions such as Ubuntu backport fixes without changing the upstream version number, so packaged builds are always unknown.
Operational outcomes are separate from assessment results. A completed run can contain targets that were blocked, timed out, or out of scope; those rows have an unknown assessment, not a negative finding. See the full reference for the detection status and fetch_status values and every output field, and the assessment methodology for how each version is classified.
--format html produces a single offline file with your logo, summary tiles, and every result sorted by risk. It follows the reader's light or dark theme and prints cleanly.
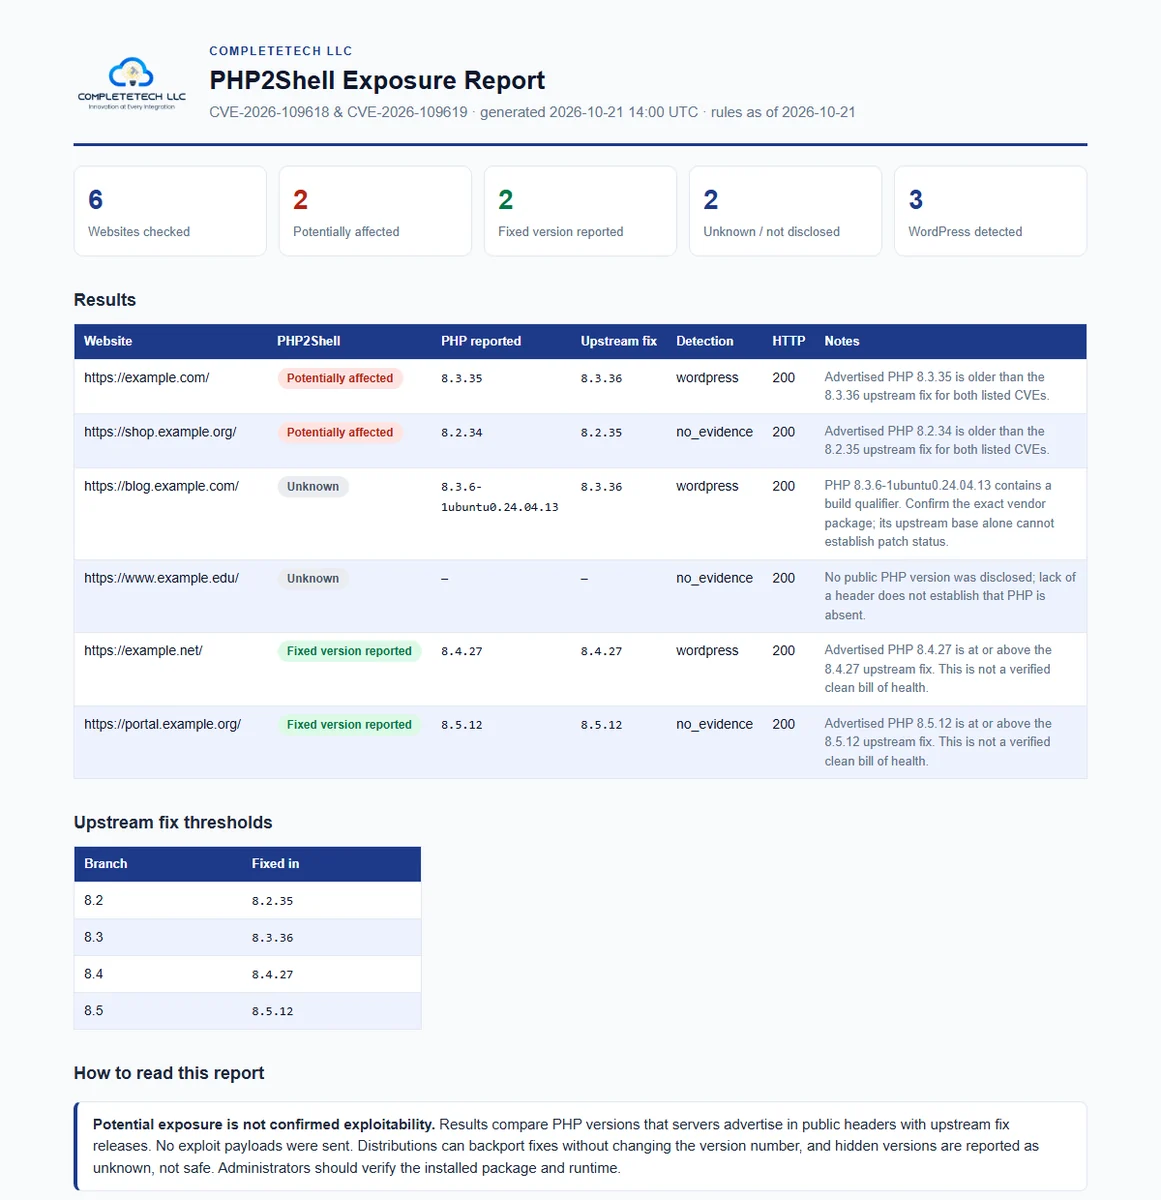
Synthetic example built from reserved example.* domains. View the HTML.
Use --logo path/to/logo.png and --brand "Your Company" to brand the report for your own organization. CSV and JSON remain available for spreadsheets and pipelines.
/robots.txt and stops if the page is disallowed.GET request to the page, with verified TLS and an honest User-Agent.X-Powered-By and Server headers, plus WordPress markers in the HTML already returned.Redirect scope. Redirects stay within each supplied origin (scheme, hostname and effective port). Only same-host HTTP port 80 to HTTPS port 443 is implicitly allowed. Additional origins, including www names or different ports, require explicit authorization via repeatable --authorized-origin https://approved.example:8443. Page and robots redirects outside that scope stop before any destination request and report fetch_status=out_of_scope; robots permission is not authorization.







