
 completetech-security/node-cve-2026-58045-check
Offline Node.js evidence checker for CVE-2026-58045: zlib synchronous API spoofed TypedArray crash. Single-file Python; JSON/CSV/HTML reports; no exploit payloads.





Offline version-evidence checker for CVE-2026-58045 — Node.js: zlib synchronous API spoofed TypedArray crash.
It compares Node.js runtime versions that you report against the fixed releases named in the Node.js security advisory, and writes the result as CSV, JSON or a self-contained HTML report. Python 3.10+, standard library only; the executable is a single file and can be copied on its own.
This repository covers only CVE-2026-58045. The checker is triage evidence, not a runtime assessment.
unknown.exploitability: not_tested.node --version on that runtime, with a leading v accepted).CI runs the test suite and --help on Python 3.10 and 3.14, on Ubuntu and Windows.
# Assess one reported version and print JSON to stdout
python node_cve_2026_58045_check.py --version 22.23.2 --format json

# Assess the synthetic example inventory and save an HTML report
python node_cve_2026_58045_check.py --inventory examples/inventory.example.json --format html --output report.html

# Assess your own CSV list (CSV to stdout by default); exit 1 on a finding
python node_cve_2026_58045_check.py --csv-list inventory.csv --fail-on-finding

# Show all options, then run the local tests
python node_cve_2026_58045_check.py --help
python -m unittest -v
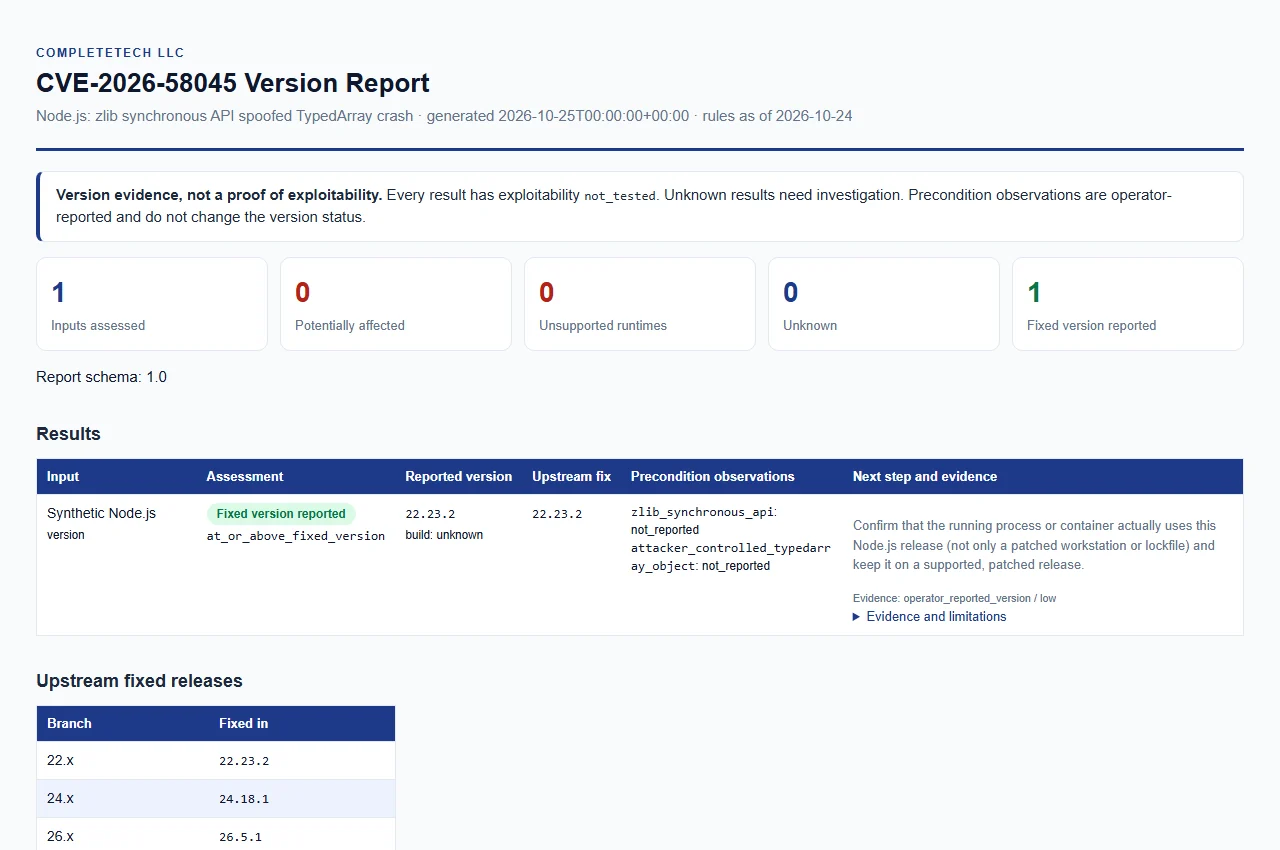
Open the synthetic example report. Example data only; this is not a live assessment.
Provide at least one of --version, --inventory or --csv-list; otherwise the checker reports a usage error. The three sources can be combined in one run, and every input becomes one result row. JSON, CSV and HTML are rendered from the same evidence.
| Option | Description |
|---|---|
--version VERSION (alias --node-version) | Assess an explicitly supplied Node.js version. Repeatable; each value describes a separate runtime. A leading v is accepted. |
--build-source SOURCE | Provenance of the --version builds, at most 512 characters. unknown (the default), upstream, official or official_upstream are compared as upstream; any other value, such as a vendor name, yields unknown with vendor_build_unverified. |
--zlib-synchronous-api {true,false} | Operator-reported observation applied to the --version inputs. |
--attacker-controlled-typedarray-object {true,false} | Operator-reported observation applied to the --version inputs. |
--inventory FILE | JSON object or array of entries. Repeatable. |
--csv-list FILE | CSV with a node_version column. Repeatable. |
--format {csv,json,html} | Report format. Default: csv. |
--output FILE | Save the report to a new file. Default: stdout. |
--force | Replace an existing output file. Without it, an existing file is never overwritten. |
--brand NAME | Organization name shown in the HTML report, at most 512 characters. Default: CompleteTech LLC. |
--fail-on-finding | Exit 1 when any result is potentially_affected or unsupported_runtime. See exit codes. |
--tool-version | Print the tool name and version. |
Output protections:
--output must name a file in an existing directory. An existing report is protected unless --force is explicit, and an input file cannot be overwritten even with --force.--force the checker publishes with a hard link and fails with an error rather than overwrite if the filesystem cannot do that.--build-source apply only to --version inputs; inventory and CSV entries carry their own values.Inventories are optional; --version needs none. Inventory entries may include operator-reported precondition observations. These never change the version result or establish reachability.
| Observation key | Meaning |
|---|---|
zlib_synchronous_api | Operator-reported: zlib synchronous API |
attacker_controlled_typedarray_object | Operator-reported: attacker-controlled TypedArray object |
Each observation is true, false or unreported, and appears in results as reported_true, reported_false or not_reported.
--inventory)





