Offline Node.js evidence checker for CVE-2026-105481: HTTP keep-alive premature-response acceptance. Single-file Python; JSON/CSV/HTML reports; no exploit payloads.





Offline, version-only triage for CVE-2026-105481: Node.js HTTP keep-alive premature-response acceptance.
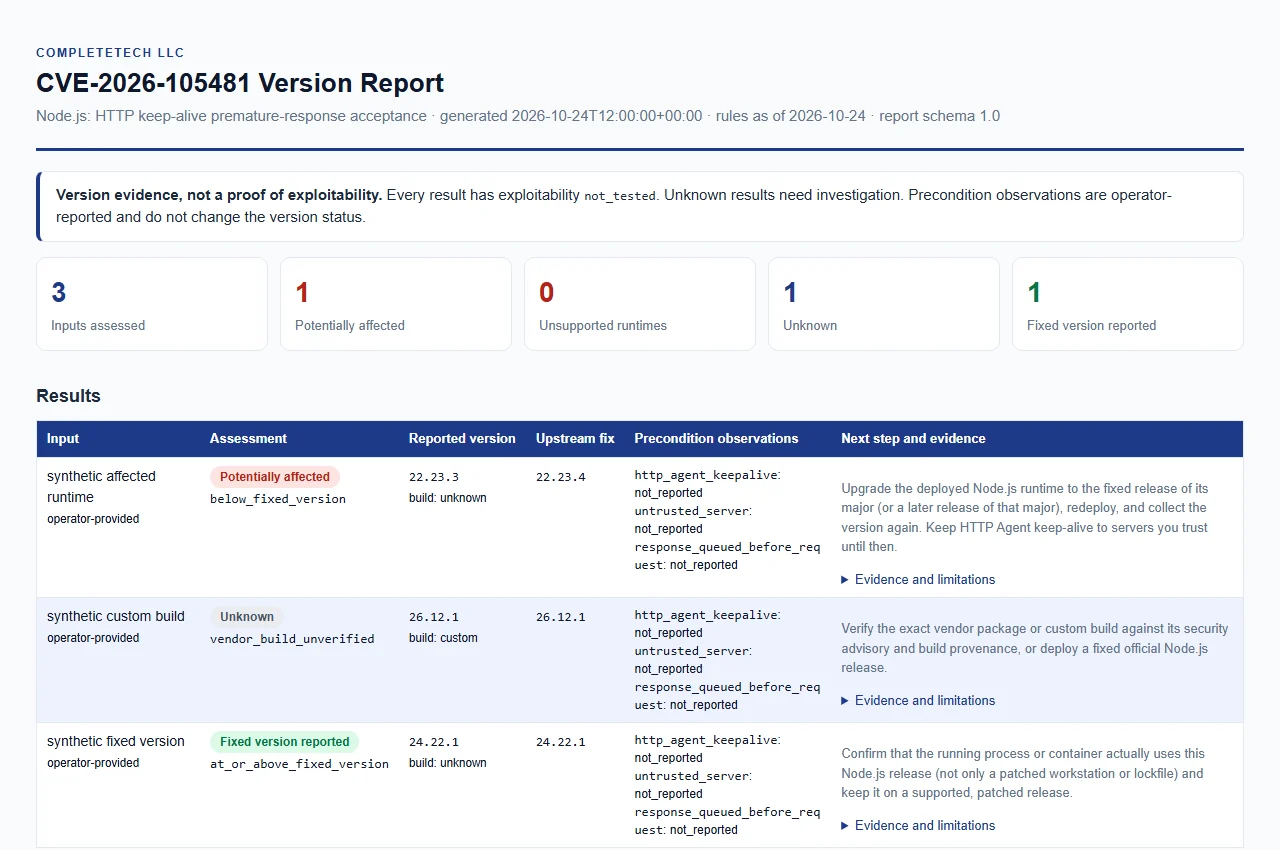
node-cve-2026-105481-check compares Node.js versions that you report with the upstream fixed releases for CVE-2026-105481. The flaw is in HTTP Agent connection reuse and can make a client accept a response that was written before its request was sent. The vendor rates it medium severity. The checker is a single Python file with no dependencies.
The checker is offline. It never connects to a target, runs Node.js, inspects a host, or sends a payload. The advisory is version-only, so there is deliberately no network mode.
[!IMPORTANT] A version report is evidence, not an assessment. The checker cannot see what actually runs, what a vendor has backported, or whether the vulnerable path is reachable. The vendor does not state an introduced version, so every release below a fix is only "potentially affected". Unlisted, custom, vendor, and prerelease builds are never labelled safe. Every result carries
exploitability: not_tested.
Python 3.10 or later on Windows, macOS, or Linux. The checker uses only the standard library, so there is nothing to install. CI runs the tests on Ubuntu and Windows with Python 3.10 and 3.14.
git clone https://github.com/CompleTetech-Security/node-cve-2026-105481-check.git
cd node-cve-2026-105481-check

# Check versions given on the command line (CSV to stdout by default)
python node_cve_2026_105481_check.py --version v22.23.3 --version 24.22.1

# Check the synthetic example inventory and write an HTML report
python node_cve_2026_105481_check.py --inventory examples/inventory.example.json --format html --output report.html

# Check a CSV list, write JSON, and exit 1 if anything needs attention
python node_cve_2026_105481_check.py --csv-list runtimes.csv --format json --output report.json --fail-on-finding
Run the tests with python -m unittest -v.
At least one of --version, --inventory, or --csv-list is required. You can combine them, and each entry becomes one result row. A run is limited to 10,000 entries and 100 input files in total.
| Option | Meaning |
|---|---|
--version VERSION (alias --node-version) | Reported Node.js version. Repeatable. A leading v is accepted. |
--build-source SOURCE | Provenance of every --version value, at most 512 characters. See build source. |
--http-agent-keepalive, --untrusted-server, --response-queued-before-request true|false | Operator observations applied to the --version values. They never change status. |
--inventory FILE | JSON object or array of entries. Repeatable. |
--csv-list FILE | CSV with a header row. Repeatable. |
--format csv|json|html | Output format. The default is csv. |
--output FILE | Write the report to a new file instead of stdout. The file is published atomically. |
--force | Allow --output to replace an existing file. The output may never replace an input file. |
--brand TEXT | Organization name shown in the HTML report, at most 512 characters. The default is CompleteTech LLC. |
--fail-on-finding | Exit 1 when a result is potentially_affected or unsupported_runtime. |
--tool-version, --help | Print the tool version or usage. |
Input fields, validation rules, and limits are in docs/REFERENCE.md. A synthetic inventory is in examples/inventory.example.json.
--build-source is an operator claim, not verified provenance. The default unknown, and also upstream, official, official_upstream, or an empty value, all allow the normal comparison. An unlabelled version is therefore compared as an upstream build. Any other value is treated as a vendor or custom build, and the result stays unknown.
| Code | Meaning |
|---|---|
| 0 | Completed and the report was written. |
| 1 | Completed with --fail-on-finding and at least one potentially_affected or unsupported_runtime result. |
| 2 | Usage or operational error, such as bad or oversized input, an existing output without --force, or an unwritable output. No partial output file is left. |
| 130 | Interrupted (Ctrl-C). Depending on the stage, completed results are written once and marked incomplete, or nothing is written. A report that was already published is left as written and is not retried. |
Exit 2 means the run itself failed. It is not an assessment result. The stage-by-stage behavior of exit 130 is in docs/REFERENCE.md.
status | Meaning |
|---|---|
potentially_affected | The reported upstream version is below the fixed release of its listed major (22.x, 24.x, 26.x). This is not confirmed exploitability. |
fixed_version_reported | The reported upstream version is at or above that fixed release. This is not a guarantee of safety or of what the deployed binary contains. |
unsupported_runtime | The major is past end-of-life in the Node.js release schedule. The vendor states that End-of-Life versions are always affected by a security release. |
unknown | The version is missing, malformed, a prerelease/nightly/rc, a vendor or custom build, conflicting, or in an uncovered major (for example 27.x). |
| Node.js major | 22.x | 24.x | 26.x |
|---|---|---|---|
| Fixed in | 22.23.4 | 24.22.1 | 26.12.1 |
version_status gives the specific reason for each status.precondition_*) are reported in their own fields and never change status.exploitability is always not_tested.evidence_type is always operator_reported_version. evidence_confidence is low, or insufficient when status is unknown. It is never high, because the checker cannot inspect the runtime.The full field list and the version-parsing rules are in docs/REFERENCE.md.