 completetech-security/netscaler-cve-2026-88773-check
Offline NetScaler ADC / Gateway evidence checker for CVE-2026-88773. Reported firmware and configuration evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.





Offline triage of operator-reported NetScaler build and configuration evidence for CVE-2026-88773, an HTTP request smuggling vulnerability in Citrix NetScaler ADC and Gateway.
The checker is a standalone, standard-library Python script. It compares reported builds against the vendor's fixed builds and records explicit configuration observations. It has no appliance access, application execution, exploit payload or network mode, and it follows the reporting conventions of node2shell-check and php2shell-check.
potentially_affected is not confirmed exploitability.fixed_version_reported is a reported version, not a verified deployed patch or a safety guarantee.unknown is never safe.exploitability: not_tested.Python 3.10 or later. No installation and no third-party dependencies. Use python3 where python is not available.
python netscaler_cve_2026_88773_check.py --version 14.1-73.36 --variant standard
python netscaler_cve_2026_88773_check.py --inventory docs/example-inventory.json --format html --output report.html
python netscaler_cve_2026_88773_check.py --csv-list inventory.csv --format json --fail-on-finding
Run with --help to list every option, or --tool-version to print the checker version. The synthetic example input uses invented labels only.
Inputs can be combined in one run. Full limits, field rules and schemas are in the reference.
| Option | Purpose |
|---|---|
--version BUILD | Reported NetScaler build; repeatable |
--variant standard|fips|ndcpp | Variant for all --version builds; an unstated ambiguous variant stays unknown |
--build-source SOURCE | Build provenance for all --version builds. Only unknown (default), official and citrix allow comparison; other provenance stays unknown |
--inventory FILE | Strict UTF-8 JSON inventory (schema_version: 1); repeatable |
--csv-list FILE | Strict UTF-8 CSV with a version header; repeatable |
--http-or-ssl-vserver true|false|unknown | Configuration observation, see below |
--format json|csv|html | Report format; default json |
--output FILE | Report file; default stdout. The directory must exist |
--force | Replace an existing report; otherwise existing reports are refused |
--fail-on-finding | Exit 1 on a finding, see exit codes |
Build, variant and provenance values are operator claims. Output cannot resolve or hard-link to any input, even with --force. Reports are written owner-only (0600 on POSIX; inherited ACLs on Windows) and published atomically.
Affected means strictly before the fixed build for the same branch and variant. No lower bound or lifecycle conclusion is invented. Other branches and 14.1 NDcPP remain unknown. An unstated 13.1 variant remains unknown where standard and FIPS/NDcPP comparisons disagree.
| Branch and variant | Vendor fixed build |
|---|---|
| 14.1 standard | 14.1-73.37 |
| 13.1 standard | 13.1-64.23 |
| 14.1 FIPS | 14.1-73.37 |
| 13.1 FIPS/NDcPP | 13.1-37.279 |
Accepted build formats include 14.1-73.37, 14.1.73.37 and NS14.1: Build 73.37.nc, optionally marked FIPS/NDcPP before an optional nc marker. Supply only the build text. Malformed, qualified, non-ASCII, conflicting, custom-build and uncovered evidence remains unknown.
Supply explicit observations as true, false or unknown CLI flags, JSON booleans/null or documented CSV values. They remain separate from version status and do not prove reachability. No local configuration or process data is collected.
| CLI observation | Meaning | Exposure condition expects |
|---|---|---|
--http-or-ssl-vserver | An LB, CS, VPN or authentication virtual server of type HTTP or SSL is configured | true |
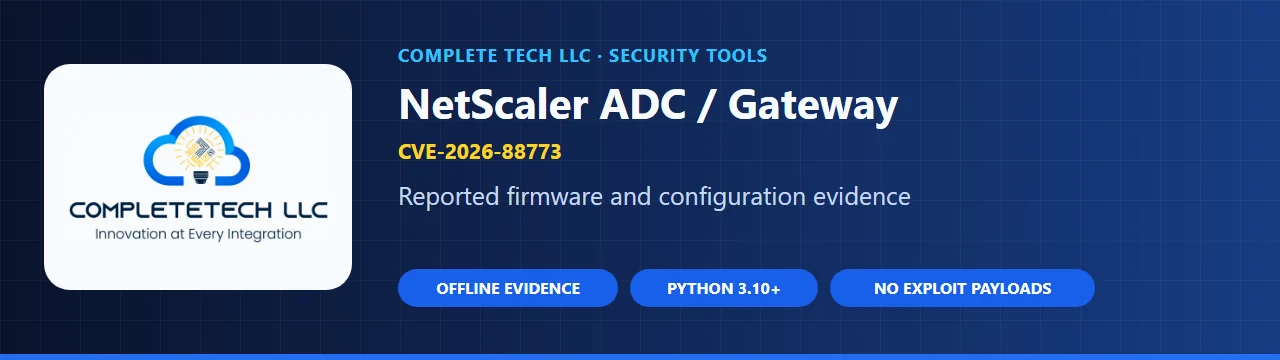
Each result row carries these independent statuses:
| Field | Values |
|---|---|
version_status | potentially_affected, fixed_version_reported, unknown |
precondition_status | conditions_observed, condition_not_observed, unknown (summarizes operator observations only; never a verified exposure or clean result) |
remediation_status | firmware_update_required, version_verification_required, version_requirement_reported (independent of exploitability) |
exploitability | Always not_tested |
| Exit code | Meaning |
|---|---|
0 | Report written. unknown does not change the exit code and is never a clean bill |
1 | --fail-on-finding with affected firmware or a required enhanced-ISN configuration change |
2 | Usage, input or output error (operational failure, not an assessment result) |
130 | Interrupted |
An interrupted run preserves completed observations where possible, with explicit completeness metadata. The shared enhanced-ISN check is not enabled for this CVE's rules. See the reference for publication and interruption semantics.
JSON, formula-safe CSV and self-contained script-free HTML. The generated example report describes no real systems.