completetech-security/http2shell-check
Offline Brotli / HTTP2Shell (CVE-2026-111497) exposure and inventory checker across verified ecosystems. Python 3.10+, no dependencies or exploit payloads.

Brotli decoder exposure, with evidence.
http2shell-check assesses reported versions and component inventories for CVE-2026-111497, the Google Brotli decoder vulnerability also called HTTP2Shell or Node2Shell. These names describe the same underlying flaw. HTTP/2 is not required.
It covers native Brotli, Node.js, Bun, Python Brotli/brotlicffi, Brotli4j, Envoy, Istio, and exact Debian source-package snapshots. The standalone Python checker makes no network requests, imports no decoder, and sends no exploit payloads. Version comparisons are triage, not proof: exploitability is always not_tested, and a reported fixed version is not a verified deployed patch.
Python 3.10+ on Windows, Linux, or macOS. There is nothing to install: the checker and its tests use only the standard library. Use python3 where python is not available.
git clone https://github.com/CompleTetech-Security/http2shell-check.git
cd http2shell-check

# Assess explicit versions
python http2shell_check.py --component brotli=1.2.0 --format json
python http2shell_check.py --component python-brotli=1.2.1 --component bun=1.4.3

# Assess an inventory and write an offline HTML report
python http2shell_check.py --inventory examples/inventory.json --format html --output report.html

# Assess the current Python environment's installed packages
python collect_python.py > runtime.json
python http2shell_check.py --inventory runtime.json --format json
Existing output files are refused unless --force is given. Keep real inventories and reports outside Git. The checker file also works when copied elsewhere; supply --logo approved-logo.png if you want a logo in HTML reports.
Supply at least one input. --component, --inventory, --pip-list, and --node-inventory are repeatable and combinable; each creates independent observations.
| Input | Source |
|---|---|
--component PRODUCT=VERSION | A single version supplied on the command line. |
--inventory PATH | Canonical multi-component JSON inventory. |
--pip-list PATH | Output of python -m pip list --format=json; only Brotli/brotlicffi entries are assessed. |
--node-inventory PATH | An existing node2shell-check collector v1 file. |
Common options:
| Option | Default | Behavior |
|---|---|---|
--format csv|json|html | csv | Output format; all formats carry the same component findings and report metadata. |
--output PATH | stdout | Atomically publish a completed report. |
--force | off | Replace an existing output file. Inputs, the checker, and logo files stay protected. |
--brand NAME | CompleteTech LLC | HTML organization label. |
--logo PATH | bundled assets/logo.png for the default brand, if present | Embed a PNG up to 1 MiB. A custom brand omits the default logo. |
--fail-on-finding | off | Exit 1 for potentially_affected or unsupported_runtime results. |
--version, --help | Print the tool version or usage. |
The canonical inventory schema, adapter details, field limits, and the complete option and exit-code reference are in docs/REFERENCE.md. Product identifiers and version rules are in the methodology. Unknown identifiers produce unknown coverage, not a guessed match.
| Code | Meaning |
|---|---|
0 | The report was written without operational errors. |
1 | With --fail-on-finding, at least one result is potentially_affected or unsupported_runtime. |
2 | Operational failure: invalid arguments, or an input, collection, or output error. Valid observations from other inputs are kept where possible. |
130 | Interrupted. |
An interruption during assessment publishes the completed component observations with complete=false. An interruption during output preserves an existing destination and may leave no new report. Operational errors are not assessment results, and a partial report is not a complete one.
The HTML report is one offline, script-free file. It includes an embedded logo, summary counts, prioritized component observations, evidence, unknowns, coverage gaps, remediation, branch fixes, and source links. It adapts to light and dark themes and prints cleanly. Use --brand "Your Organization" --logo approved-logo.png for custom branding.
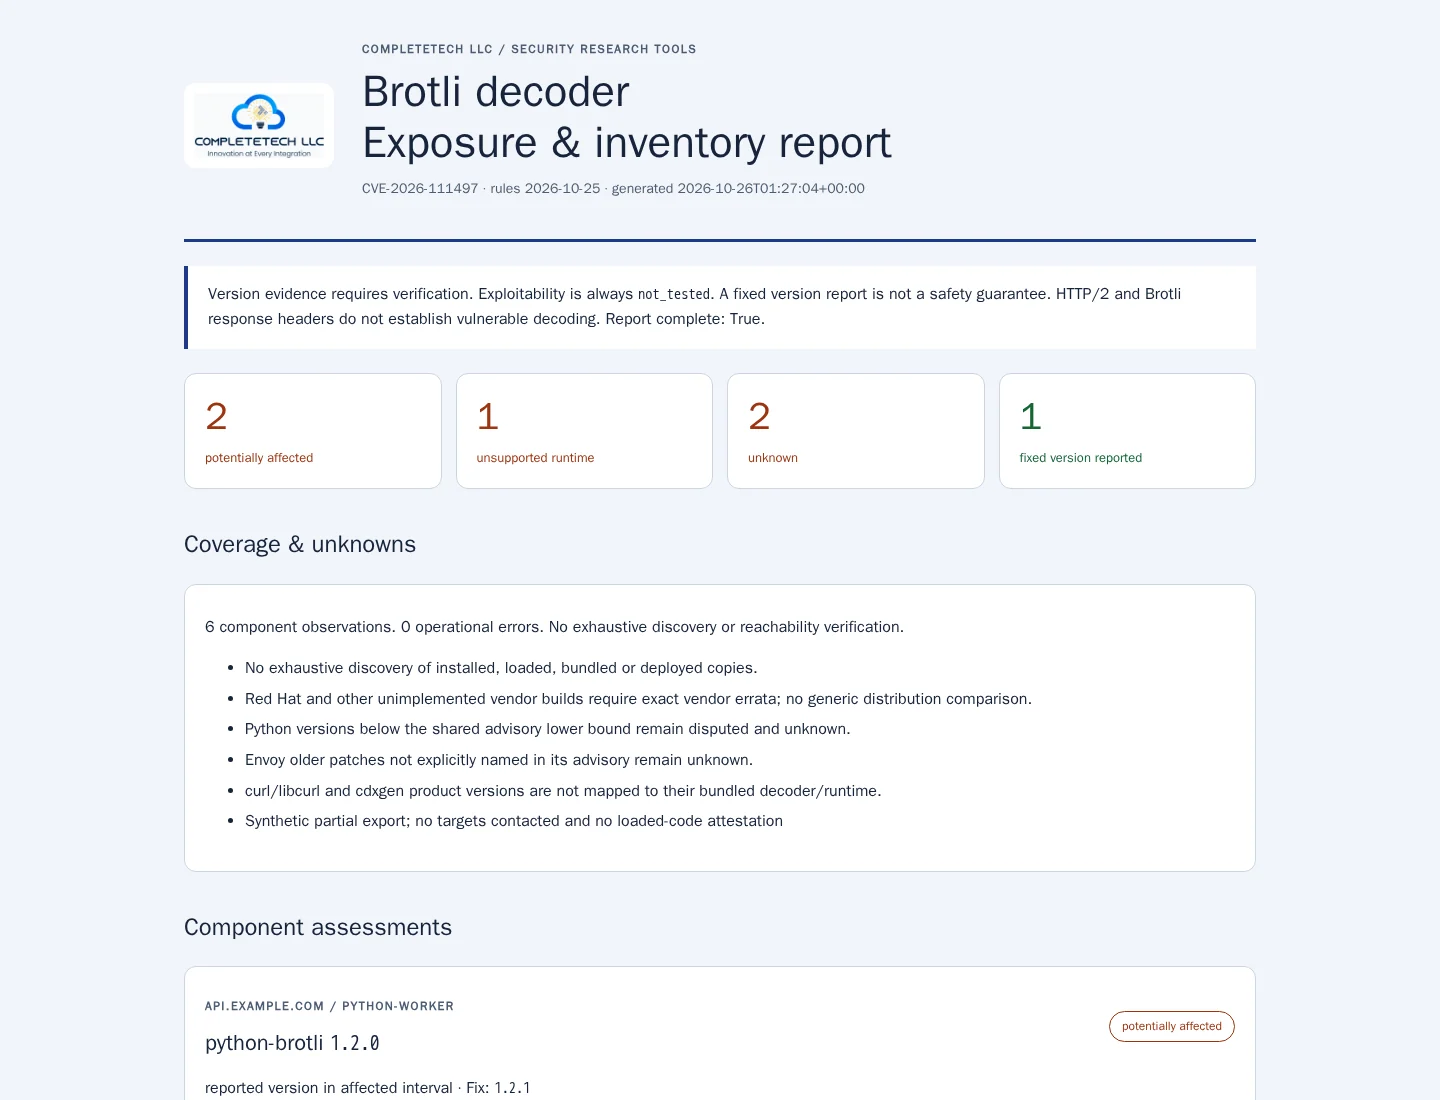
Open the synthetic example. The screenshots show actual generated output; no targets were scanned. See also the narrow layout and print preview.
| Status | Meaning |
|---|---|
potentially_affected | The reported version matches a verified affected interval or exact vendor package. Validate the actual deployed copy and input paths. |
fixed_version_reported | The version meets the applicable rule. Deployed patch state and safety remain unverified. |
unsupported_runtime | An older, unsupported Node.js line needs an upgrade or vendor review. This is not CVE confirmation. |
unknown | Missing, disputed, qualified, custom, conflicting, or uncovered evidence needs review. |
Unknown results do not trigger exit code 1 but are prominently counted. A successful command is not a clean security assessment, and report counts are not an asset safety verdict. Each component copy is assessed separately, so a fixed result never erases an affected or unknown copy.
Rules are embedded and dated 2026-10-25; they are offline snapshots, not an automatically refreshed feed. Each product identifier below is assessed by its own rule: