

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/charlie-goldenowl/cve-2026-122006-check
Defensive ToolsVulnerability ScannersWeb Vulnerability ScannersConfiguration AuditingDevSecOpsSupply Chain Security
GitHubcharlie-goldenowl/cve-2026-122006-check

cve-2026-122006-check

Share

Read-only Bash script that scans Rails projects for CVE-2026-122006, flagging vulnerable activestorage versions, mini_magick variant processing, and permissive ImageMagick coder policies.

View Repository
15 days agoNot yet reviewed

cve-2026-122006-check

Detection script for CVE-2026-122006 — Rails Active Storage hands uploads to ImageMagick with unrestricted coders, so a crafted SVG/MSL upload can read/write arbitrary files on the server (CVSS 9.8). Fixed in activestorage 8.0.5.2 and 8.1.4.1. The script only reports — it changes nothing.

Source: Rails Active Storage CVE-2026-122006: Patching, Detection and Hunting
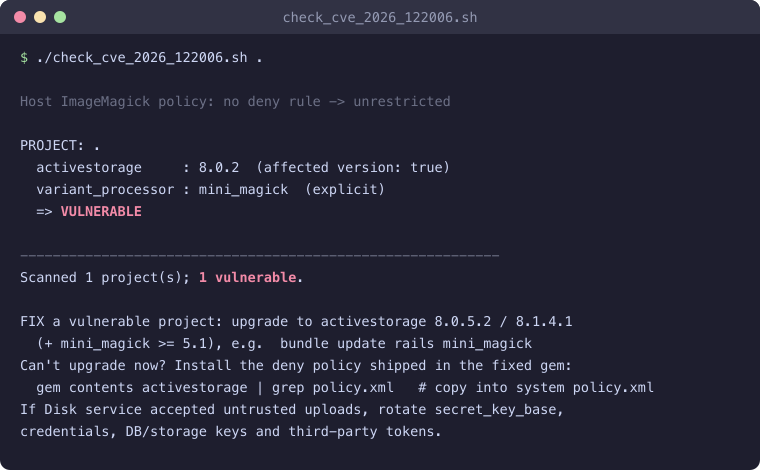
Example run flagging a vulnerable Rails project

Quick run (no download)

Run it straight from GitHub in the current directory:

curl -fsSL https://raw.githubusercontent.com/charlie-goldenowl/cve-2026-122006-check/master/check_cve_2026_122006.sh | bash

Scan a specific folder (pass the root after --):

curl -fsSL https://raw.githubusercontent.com/charlie-goldenowl/cve-2026-122006-check/master/check_cve_2026_122006.sh | bash -s -- ~/projects

Run from a local copy

chmod +x check_cve_2026_122006.sh
./check_cve_2026_122006.sh [ROOT]      # ROOT defaults to the current directory
  • Recurses under ROOT and checks every Rails app it finds (any dir with config/application.rb + a Gemfile.lock pinning activestorage), printing a per-project verdict and a summary. Point it at a parent folder to scan many projects at once: ./check_cve_2026_122006.sh ~/projects.
  • Exit code: 0 = none vulnerable, 2 = at least one vulnerable (CI-friendly).
  • NO_COLOR=1 ./check_cve_2026_122006.sh disables colored output.
  • Works on Linux and macOS. Needs bash + ruby; magick/convert optional (used only to check the host ImageMagick policy).

A project is flagged VULNERABLE when all three hold

  1. activestorage older than 8.0.5.2 (8.1 line: older than 8.1.4.1).
  2. variant_processor is :mini_magick (Rails 8 default :vips is not affected). Read from your config, falling back to the load_defaults default.
  3. The host ImageMagick has no policy denying the risky coders (MSL/PS/PDF/...).

Fix

bundle update rails mini_magick        # -> activestorage 8.0.5.2 / 8.1.4.1, mini_magick >= 5.1

Can't upgrade yet? Install the deny policy shipped inside the fixed gem onto every host/image/container:

gem contents activestorage | grep policy.xml   # copy into your system policy.xml

If the Disk service accepted untrusted uploads, assume secrets may have been read: rotate secret_key_base, credentials, DB/storage keys and third-party tokens.

Note

The script reads versions from Gemfile.lock and config files (no app boot), so it is fast and safe to run across many repos. It does not detect apps that patch MiniMagick internals or use GraphicsMagick; review those manually.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    989
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    576
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    315

Explore all tools

Browse our collection of tools

View all tools →





