

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-2699 — Detection scripts, technical analysis, and proof-of-concept for CVE-2026-2699, a critical pre-auth authentication bypass in Progress ShareFile Storage Zones Controller. | Kitploit
Tools/GitHubGitHub/ashrafzaryouh/cve-2026-2699
Vulnerability ScannersVulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityAuthenticationPapers & Research
GitHubashrafzaryouh/cve-2026-2699

CVE-2026-2699

Detection scripts, technical analysis, and proof-of-concept for CVE-2026-2699, a critical pre-auth authentication bypass in Progress ShareFile Storage Zones Controller.

View Repository
7 months agoNot yet reviewed
Share

CVE-2026-2699 — Progress ShareFile Storage Zones Controller Authentication Bypass

License: MIT GitHub stars GitHub issues

Critical Authentication Bypass (CVSS 9.8) in customer-managed Progress ShareFile Storage Zones Controller (SZC) ≤ 5.12.3.


📋 Overview

CVE-2026-2699 is a severe authentication bypass vulnerability affecting the web interface of Progress ShareFile Storage Zones Controller (customer-managed deployments).

An unauthenticated remote attacker can access restricted configuration pages, which can lead to system configuration changes and, when chained with CVE-2026-2701, full pre-auth remote code execution (RCE).

  • Affected Product: Progress ShareFile Storage Zones Controller (SZC) 5.x (up to 5.12.3)
  • Not Affected: ShareFile 6.x and cloud-hosted instances
  • Fixed In: Storage Zones Controller 5.12.4 (released March 2026)

This repository contains detection scripts, technical analysis, and proof-of-concept materials (where legally and ethically permitted).
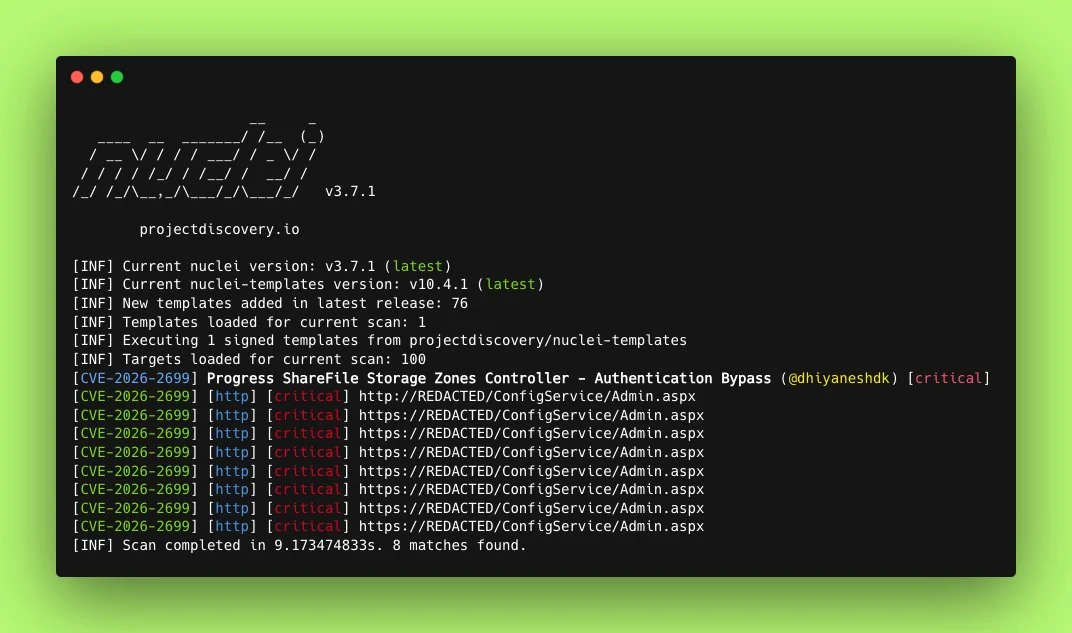

🎯 Vulnerability Details

HFTRzKMbQAAdLZ5

  • CVE ID: CVE-2026-2699
  • Severity: Critical (CVSS v3.1 Base Score: 9.8)
  • Vector: AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
  • Type: Authentication Bypass / Improper Access Control (CWE-284) with Execution After Redirect (EAR)
  • Impact: Unauthenticated access to administrative configuration endpoints → potential full system compromise when chained

Root Cause

The vulnerability stems from insufficient access control and flawed redirect handling in the SZC web management interface, allowing unauthenticated users to reach sensitive configuration functionality.


🛠️ Repository Contents

  • detection/ — Non-destructive detection scripts (Python)
  • analysis/ — Detailed technical write-up and root cause explanation
  • poc/ — Proof-of-concept (educational / authorized testing only)
  • exploit-chain/ — Demonstration of chaining with CVE-2026-2701 (RCE)
  • assets/ — Screenshots, diagrams, and logs

🚨 Affected Versions

VersionStatus
≤ 5.12.3Vulnerable
5.12.4+Patched
6.xNot affected

Note: Only customer-managed (on-premises) Storage Zones Controller deployments are impacted.


✅ Remediation

  1. Upgrade immediately to Storage Zones Controller 5.12.4 or later.
  2. Restrict public internet exposure of SZC management interfaces (use VPN, firewall rules, or zero-trust access).
  3. Monitor logs for suspicious access to /Configuration/ or similar endpoints.
  4. Apply the official security patch from Progress Software.

Official Advisory:
Progress ShareFile Security Vulnerability – February 2026


🔍 Detection

This repository includes a lightweight detection script:

python3 watchTowr-vs-Progress-ShareFile-CVE-2026-2699.py -t https://target-sz-controller.example.com

Inspired by the official watchTowr detection artifact.


📚 References

  • NVD Detail — CVE-2026-2699
  • watchTowr Labs Full Analysis
  • Progress Official Advisory
  • Tenable CVE Page
  • GitHub Advisory: GHSA-ppf9-6x38-42wv

⚠️ Legal & Ethical Notice

All materials in this repository are provided for educational, research, and defensive security purposes only.

Unauthorized exploitation against systems you do not own or have explicit permission to test is illegal and unethical.


⭐ Star History & Contributions

Contributions, improved detections, or additional write-ups are welcome via Pull Requests.


Made with ❤️ for the security community

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →





