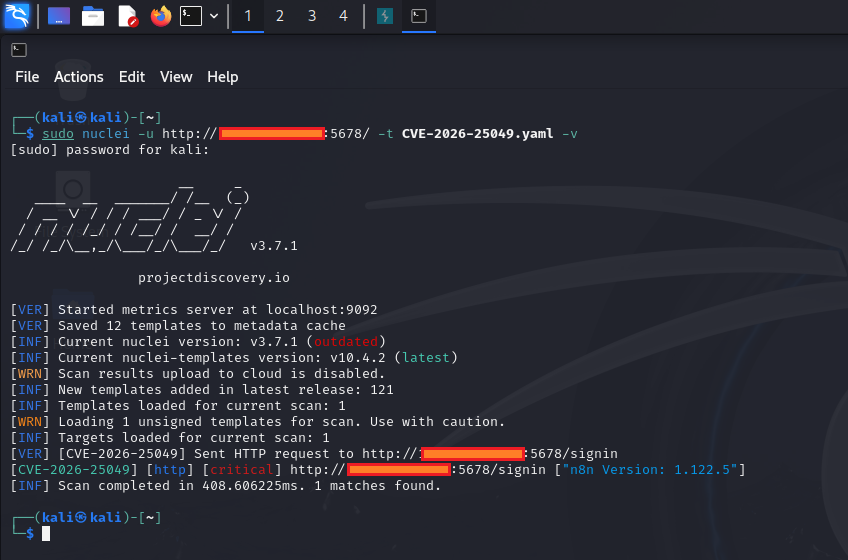
Advisory and verification notes for CVE-2026-25049, an unauthenticated information disclosure in n8n's /rest/settings endpoint, with impact, affected versions, and mitigation.



This vulnerability allows unauthenticated access to internal configuration data via a REST API endpoint in certain n8n deployments.
In vulnerable configurations, the following endpoint is accessible without authentication:
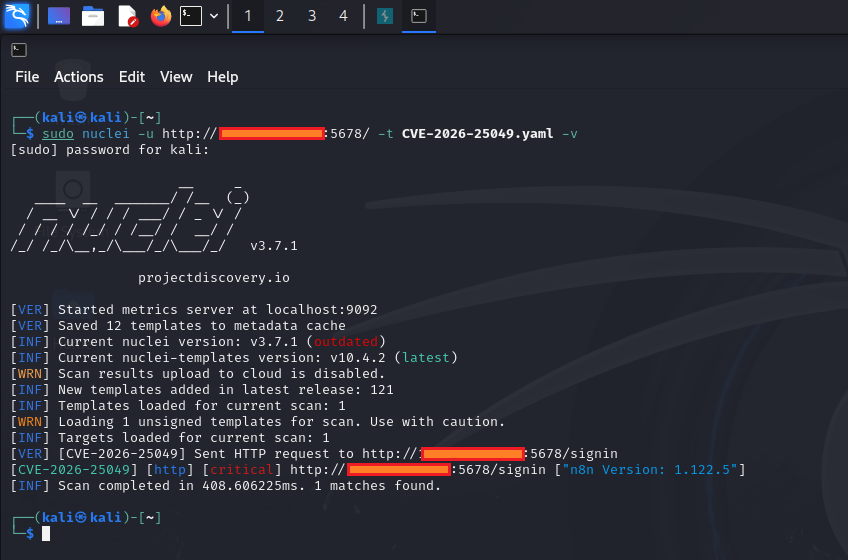
GET /rest/settings
public)This endpoint should normally be restricted to authenticated users, but misconfigurations or vulnerable versions may expose it publicly.
While not directly leading to full system compromise, this vulnerability can:
💡 Even limited information disclosure can significantly weaken overall security posture.
n8n v1.123.5⚠️ Always verify against official advisories and changelogs.
To verify the vulnerability:
Send a request to:
/rest/settings
Observe the response behavior.
401 Unauthorized200 OKTo secure your instance of n8n:
5678 (VPN, firewall, IP allowlist)| Factor | Assessment |
|---|---|
| Attack Complexity | Low |
| Privileges Required | None |
| User Interaction | None |
| Impact Scope | Partial (Info Leak) |
| Exploitability | High (if exposed) |
⚠️ This project is intended for educational purposes and authorized security testing only. Do not test or scan systems without explicit permission.
If you find this useful: