
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/ashrafzaryouh/cve-2026-11499
Embedded Systems SecurityIoT SecurityVulnerability AnalysisHardware & IoT SecurityPapers & ResearchLearning & Education
GitHubashrafzaryouh/cve-2026-11499

CVE-2026-11499

Advisory and technical analysis of CVE-2026-11499, a stack-based buffer overflow (CWE-121) in Tenda HG7, HG9 and HG10 routers, covering impact, affected models and mitigations.

View Repository
215 months agoNot yet reviewed
Share

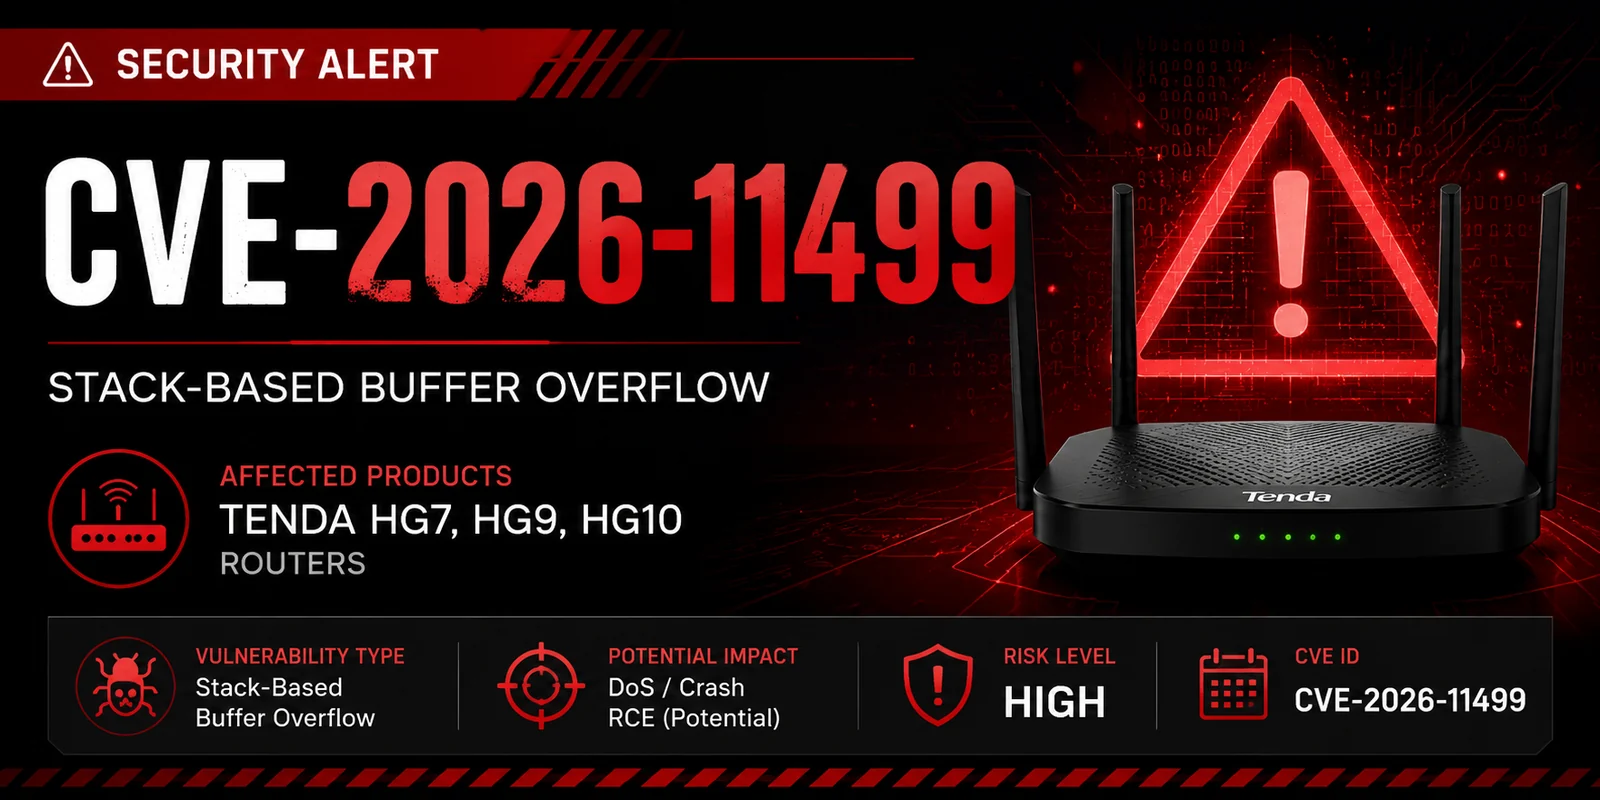
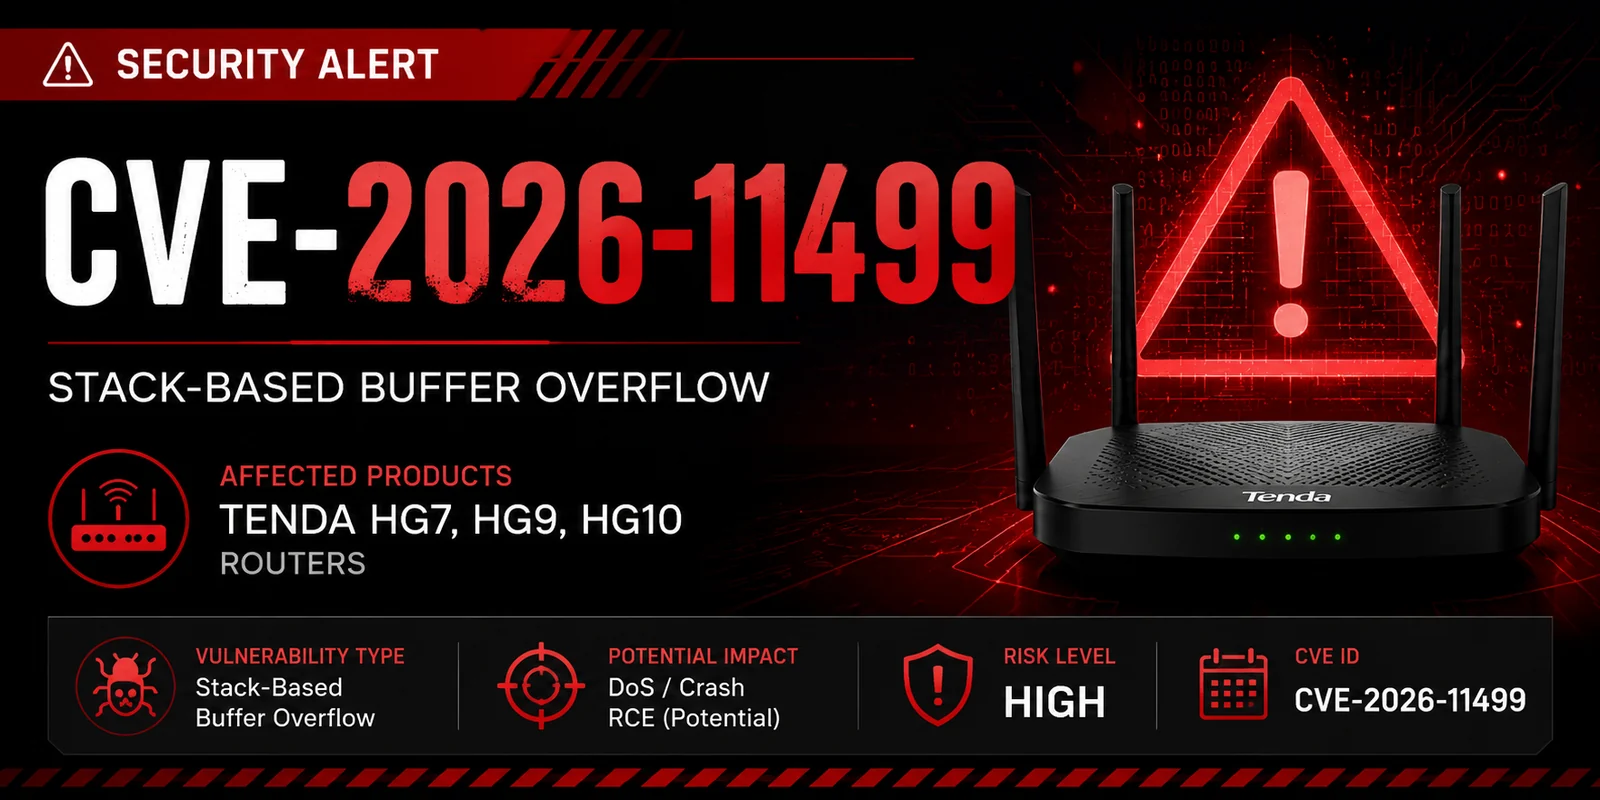
🚨 CVE-2026-11499

Stack-Based Buffer Overflow in Tenda HG7 / HG9 / HG10 Routers

ChatGPT Image Jun 8, 2026, 11_53_47 AM

Security CVE Severity Status


📖 Overview

CVE-2026-11499 is a reported stack-based buffer overflow vulnerability affecting several Tenda router models, including:

  • HG7
  • HG9
  • HG10

Successful exploitation may allow an attacker to trigger a crash, denial of service, or potentially achieve Remote Code Execution (RCE) depending on the vulnerable code path and deployment configuration.

⚠️ Technical details are currently limited and public disclosure appears to be ongoing.


🎯 Affected Products

VendorProductStatus
TendaHG7Vulnerable
TendaHG9Vulnerable
TendaHG10Vulnerable

🛠 Vulnerability Details

FieldValue
CVE IDCVE-2026-11499
TypeStack-Based Buffer Overflow
CWECWE-121
ImpactDoS / Potential RCE
Attack VectorUnknown
AuthenticationUnknown
SeverityHigh (Pending CVSS)

⚡ Potential Impact

An attacker may be able to:

  • Cause device crashes
  • Trigger denial of service conditions
  • Corrupt process memory
  • Execute arbitrary code
  • Gain unauthorized access to the device
User Input
     │
     ▼
┌───────────────┐
│ Vulnerable    │
│ Function      │
└──────┬────────┘
       │
       ▼
 Buffer Overflow
       │
       ▼
 Memory Corruption
       │
       ▼
 Potential RCE

🔬 Technical Analysis

Vulnerability Class

The issue has been categorized as a:

char buffer[256];
strcpy(buffer, attacker_input);

When input exceeds the allocated buffer size, adjacent memory may be overwritten.

Possible consequences include:

  • Application crashes
  • Stack corruption
  • Control-flow hijacking
  • Arbitrary code execution

🧪 Proof of Concept

🚫 No public PoC has been released at the time of writing.

When a PoC becomes available, testing should be performed only in authorized laboratory environments.


🛡 Mitigation

Immediate Actions

  • Update firmware once patches become available
  • Restrict administrative access
  • Disable remote management if unnecessary
  • Monitor router logs
  • Isolate vulnerable devices from untrusted networks

📅 Timeline

DateEvent
2026CVE Reserved
2026Public Disclosure
PendingVendor Advisory
PendingPatch Release

📚 References

  • MITRE CVE Program
  • NVD (National Vulnerability Database)
  • Tenda Security Advisories

⚠️ Disclaimer

This repository is intended for:

  • Security research
  • Vulnerability analysis
  • Educational purposes

Do not use this information against systems without explicit authorization.


🔥 Cybersecurity Research • Vulnerability Analysis • Responsible Disclosure

⭐ If you found this repository useful, consider starring it.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    603
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    390
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    321
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    301
  • 6

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    263

Explore all tools

Browse our collection of tools

View all tools →





