Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-48849-Roundcube-Webmail-Stored-XSS β€” CVE-2026-48849 β€” Stored XSS, HTML & CSS injection in Roundcube Webmail (1.6.x/1.7.x) via unsanitized draft subject field. Auto-executes on login. CVSS 4.4. Discovered by Anand Jogawade. | Kitploit
Tools/GitHubGitHub/anandjogawade/cve-2026-48849-roundcube-webmail-stored-xss
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPapers & ResearchLearning & Education
GitHubanandjogawade/cve-2026-48849-roundcube-webmail-stored-xss

CVE-2026-48849-Roundcube-Webmail-Stored-XSS

CVE-2026-48849 β€” Stored XSS, HTML & CSS injection in Roundcube Webmail (1.6.x/1.7.x) via unsanitized draft subject field. Auto-executes on login. CVSS 4.4. Discovered by Anand Jogawade.

View RepositoryWebsite
1423 days agoNot yet reviewed

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    985
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    571
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    309

Explore all tools

Browse our collection of tools

View all tools β†’
Share

πŸ”“ CVE-2026-48849

Stored XSS, HTML Injection & CSS Injection in Roundcube Webmail

CVE CVSS CWE Roundcube Fixed

An unsanitized subject field in draft/session restoration allows stored XSS, HTML injection, and CSS injection β€” executing automatically on login without user interaction.

Discovered and reported by Anand Jogawade (zazy)


πŸ“– Table of Contents

  • Vulnerability Summary
  • Attack Flow
  • Impact
  • Affected Versions
  • Reproduction Steps
  • Payload
  • Proof of Concept
  • Video Demonstration
  • Disclosure Timeline
  • Mitigation
  • References
  • Disclaimer

πŸ” Vulnerability Summary

FieldDetails
CVE IDCVE-2026-48849
TypeStored XSS / HTML Injection / CSS Injection
CWECWE-79 β€” Improper Neutralization of Input During Web Page Generation
CVSS v3.14.4 / Medium β€” AV:N/AC:H/PR:L/UI:R/S:C/C:L/I:L/A:N
ProductRoundcube Webmail
Affected1.6.x before 1.6.16, 1.7.x before 1.7.1
Fixed In1.6.16, 1.7.1
DiscovererAnand Jogawade (zazy)
GHSAGHSA-2m7q-4j9m-89vh

⚑ Attack Flow

                            ATTACKER                                        VICTIM
                           ─────────                                       ────────

  β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
  β”‚  1. Compose email with XSS payload  β”‚
  β”‚     in the Subject field            β”‚
  β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”¬β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜
                 β”‚
                 β–Ό
  β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
  β”‚  2. Trigger background action       β”‚
  β”‚     (attach image, auto-save)       β”‚
  β”‚     β†’ draft saved server-side       β”‚
  β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”¬β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜
                 β”‚
                 β–Ό
  β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
  β”‚  3. Invalidate session              β”‚      β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
  β”‚     (delete/modify session cookie)  β”‚      β”‚  4. Victim sees "session     β”‚
  β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”¬β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜      β”‚     expired" β†’ logs back in  β”‚
                 β”‚                              β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”¬β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜
                 β”‚                                             β”‚
                 β”‚                                             β–Ό
                 β”‚                              β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
                 β”‚                              β”‚  5. Session restore triggers β”‚
                 └─────────────────────────────▢│     draft recovery           β”‚
                                                β”‚     β†’ XSS EXECUTES          β”‚
                                                β”‚     β†’ HTML/CSS injected     β”‚
                                                β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜

                                                  ⚠️  NO USER INTERACTION
                                                     REQUIRED AFTER LOGIN

πŸ’₯ Impact

Successful exploitation enables:

  • Arbitrary JavaScript execution in an authenticated user's browser session
  • HTML content injection β€” phishing forms, fake login pages, overlays
  • CSS-based UI manipulation β€” visual defacement, hiding legitimate UI elements
  • DOM manipulation β€” modifying page content in real-time
  • Redirection to attacker-controlled websites
  • Session token theft via document.cookie exfiltration
  • Payload persistence β€” stored in draft/session data until explicitly removed

Key severity factor: The payload executes automatically during session restoration after login β€” no clicks, no links, no additional user interaction required.


πŸ“‹ Affected Versions

Version RangeStatus
1.6.0 β€” 1.6.15❌ Vulnerable
1.6.16βœ… Fixed
1.7.0❌ Vulnerable
1.7.1βœ… Fixed
1.5.x and earlier⚠️ Vulnerable (tested on 1.5.9)

πŸ”¬ Reproduction Steps

  1. Login to Roundcube Webmail
  2. Click Compose to open a new email
  3. Insert the payload (below) into the Subject field
  4. Trigger a background action (e.g., attach an image) and capture the request in Burp Repeater
  5. Send the original request and render the response β€” it will show the image
  6. Invalidate the session by modifying or deleting the roundcube_sessauth cookie in Repeater, then send and render β€” it will show the login page
  7. Confirm session expiration by sending the same request with original (valid) cookies β€” response still shows the login page (200 OK)
  8. Check the bottom-right corner: "Your session is invalid or expired" message appears
  9. Reload the page β€” redirects to login
  10. Login again with the same credentials
  11. βœ… XSS fires automatically on session restore + CSS injection + HTML injection visible

πŸ§ͺ Payload

'"><script>alert("XSS")</script> <h1>HTML</h1><h2>Injection</h2> <b/style=position:fixed;top:0;left:0;font-size:200px>CSS Injection<!--

Payload breakdown:

ComponentPurpose
'">Breaks out of attribute context (single quote, double quote, closing tag)
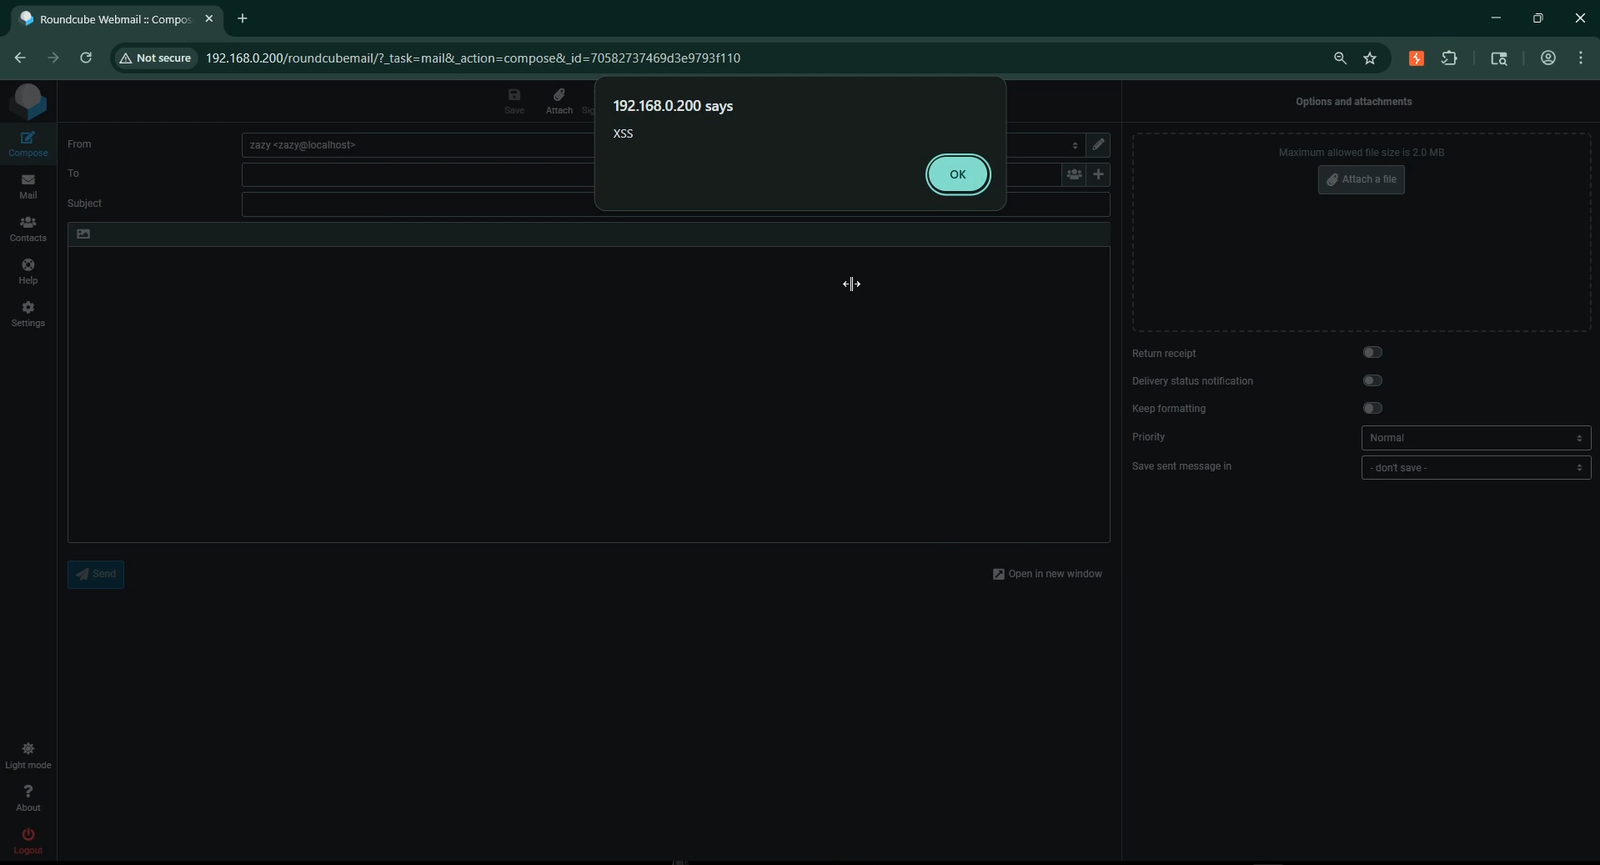
<script>alert("XSS")</script>JavaScript execution β€” Stored XSS
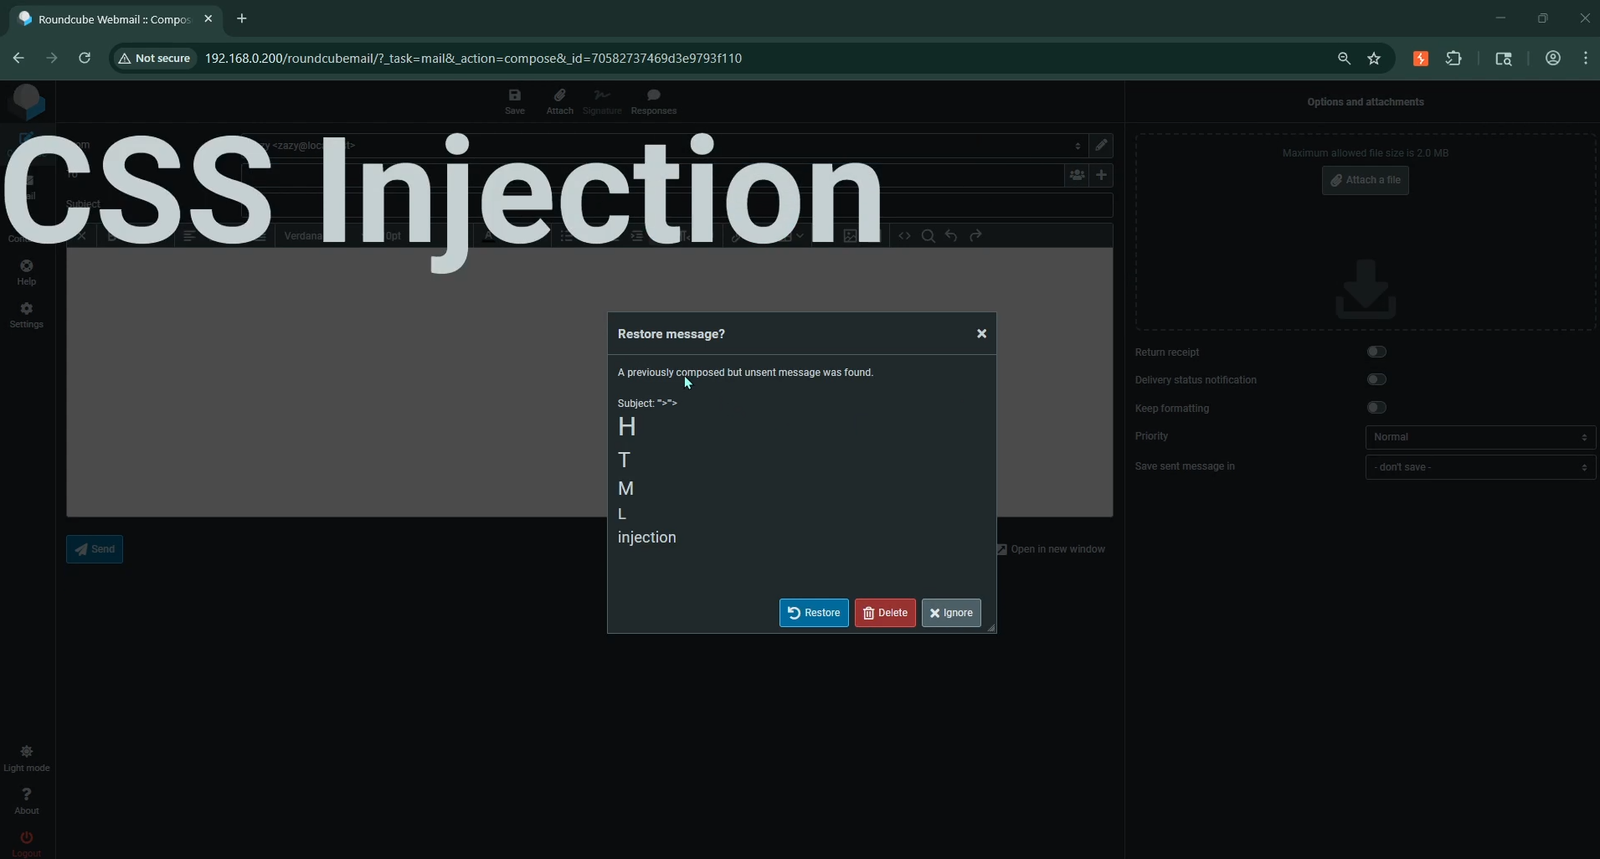
<h1>HTML</h1><h2>Injection</h2>HTML injection β€” arbitrary HTML rendering
<b/style=position:fixed;top:0;left:0;font-size:200px>CSS injection β€” fixed overlay covering the page
<!--HTML comment to suppress rendering of remaining page content

πŸ“Έ Proof of Concept

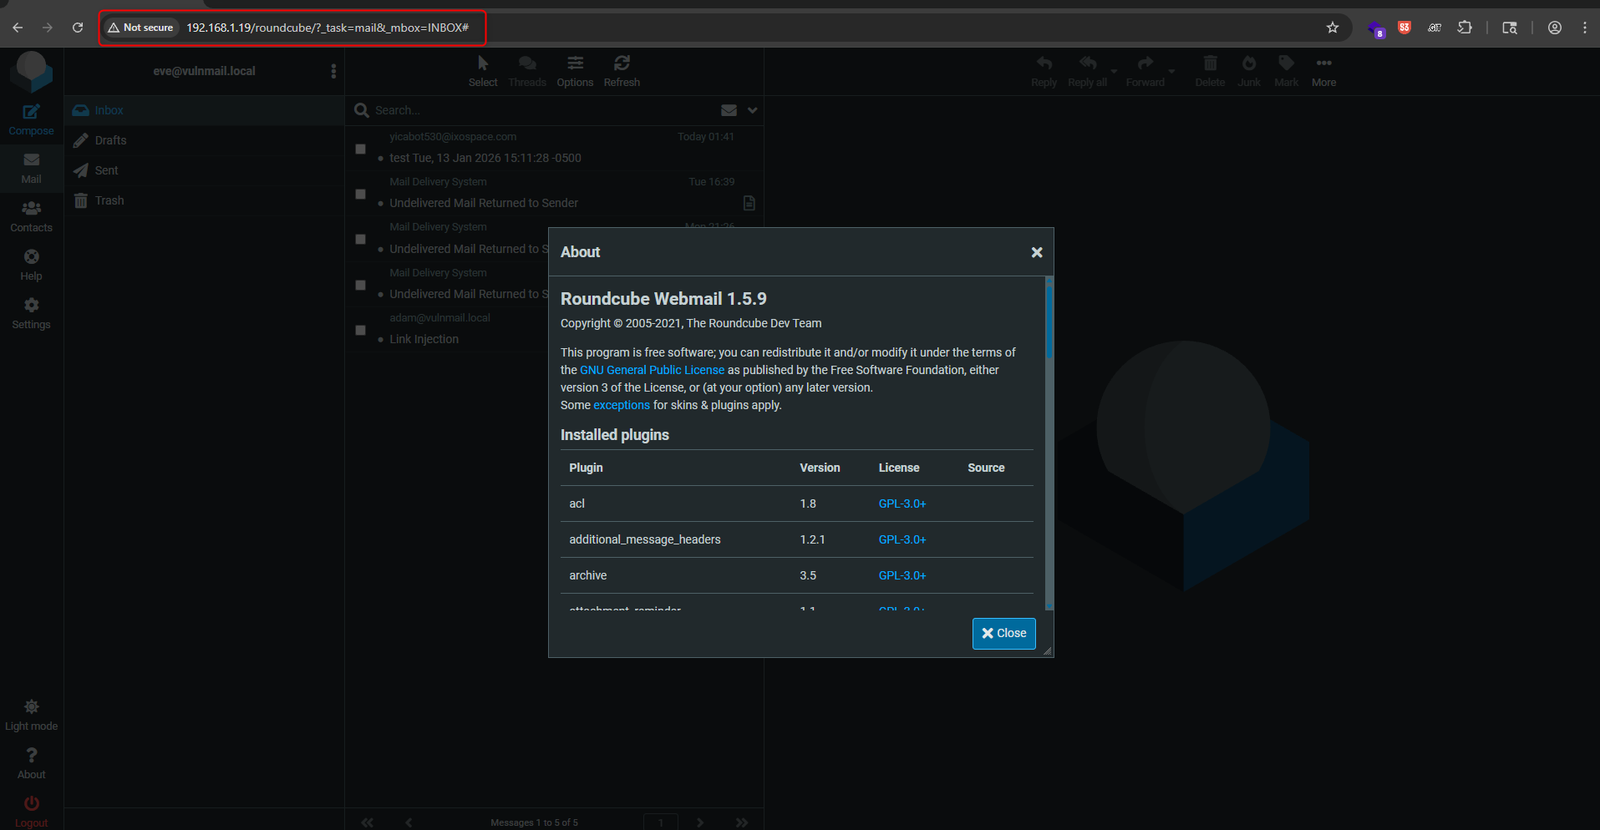
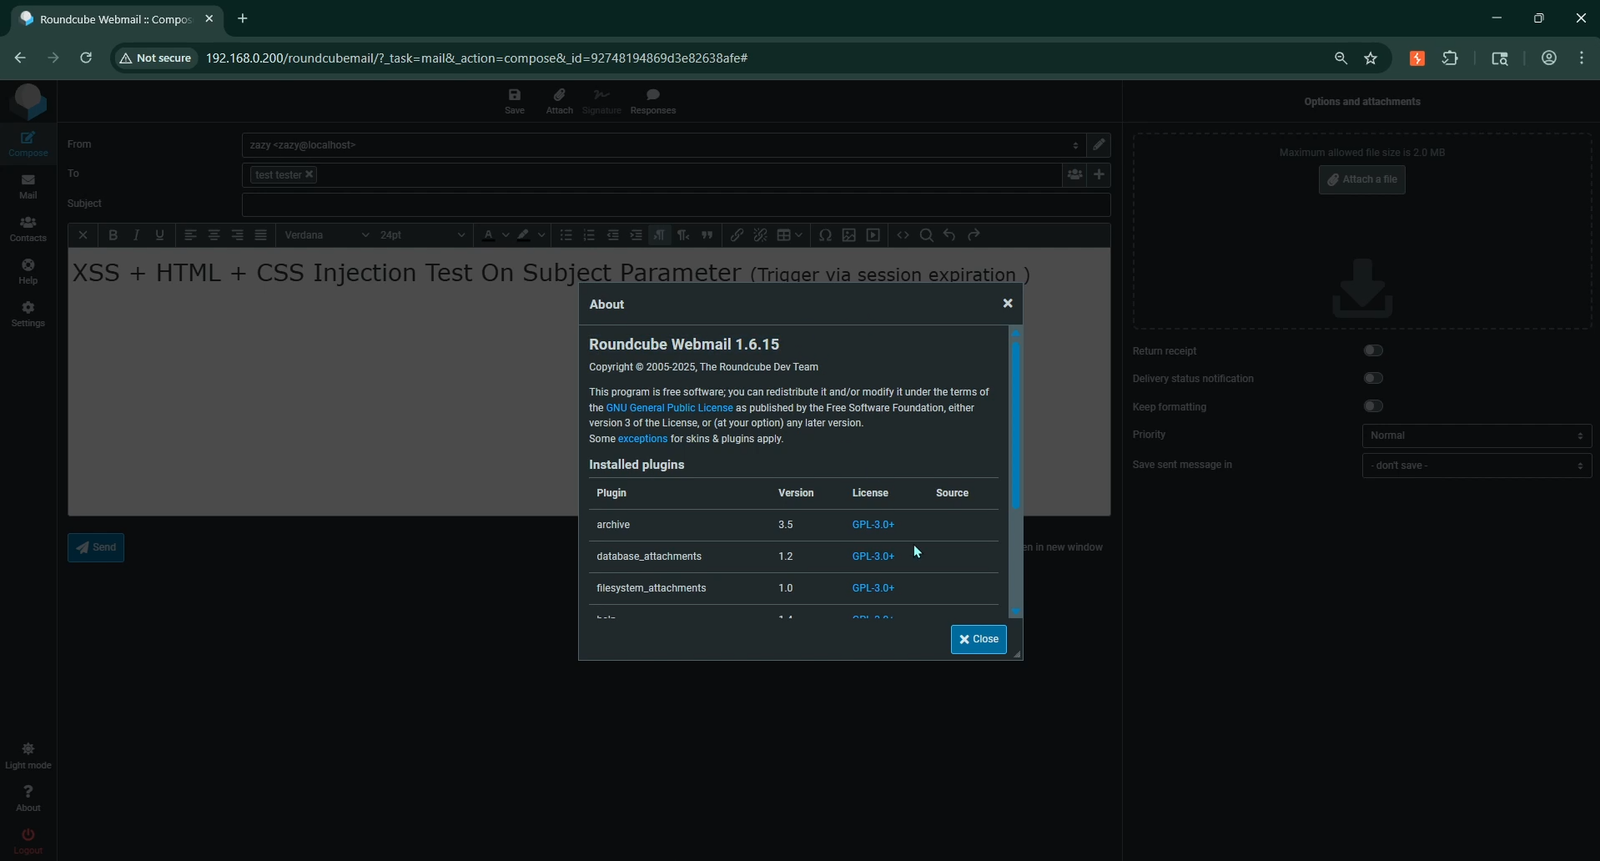
Tested on Roundcube 1.5.9

POC-0

Tested on Roundcube 1.6.15

POC-1

Stored XSS β€” JavaScript Alert Execution

POC-2

HTML + CSS Injection β€” UI Overlay

POC-3


🎬 Video Demonstration

πŸ“Ή Full exploitation walkthrough: Composing the payload β†’ session invalidation β†’ re-login β†’ automatic XSS + HTML + CSS injection

https://github.com/AnandJogawade/CVE-2026-48849-Roundcube-Webmail-Stored-XSS/raw/main/Video-POC/RoundCube%20XSS+CSS+HTML%20Injection.mp4

Download Tool