
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-21974 — 自研针对ESXI 堆栈溢出的CVE-2021-21974 POC,只支持项目给出的的目标和环境,用于学习和研究 | Kitploit

Tools/GitHubGitHub/aiyakami/cve-2021-21974
Vulnerability AnalysisExploitationCTFLearning & EducationRemote Access ToolBinary Exploitation
GitHubaiyakami/cve-2021-21974

CVE-2021-21974

自研针对ESXI 堆栈溢出的CVE-2021-21974 POC,只支持项目给出的的目标和环境,用于学习和研究

View Repository
4474 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    936
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    353
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    348
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    288

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2021-21974

VMware ESXi OpenSLP Heap Overflow Remote Code Execution PoC

Author: Aiyakami

Overview

CVE-2021-21974 is a heap overflow vulnerability in the OpenSLP service in VMware ESXi. An unauthenticated attacker can send specially crafted packets over the network to the target ESXi host's SLP service (default port 427), achieving remote code execution (RCE).

This repository provides a single-file Python PoC that can reliably reproduce the vulnerability on a real ESXi 6.7 environment. It exploits purely over the network, requiring no local credentials or SSH access to trigger command execution.

Test Environment

ItemInformation
Target SystemVMware ESXi 6.7.0 Update03
Build Number14320388
Vulnerable ServiceOpenSLP (slpd), port 427
Test Success Rate100%

Target Image Download

Official VMware-VMvisor-Installer 6.7.0 update03 build-14320388 ISO:

https://dn711004.ca.archive.org/0/items/vmware-installer-6.7.0-update-03/VMware-VMvisor-Installer-6.7.0.update03-14320388.x86_64.iso

This image is the original installation image used in the above test environment and can fully reproduce the 100% success rate of this PoC.

Test Results

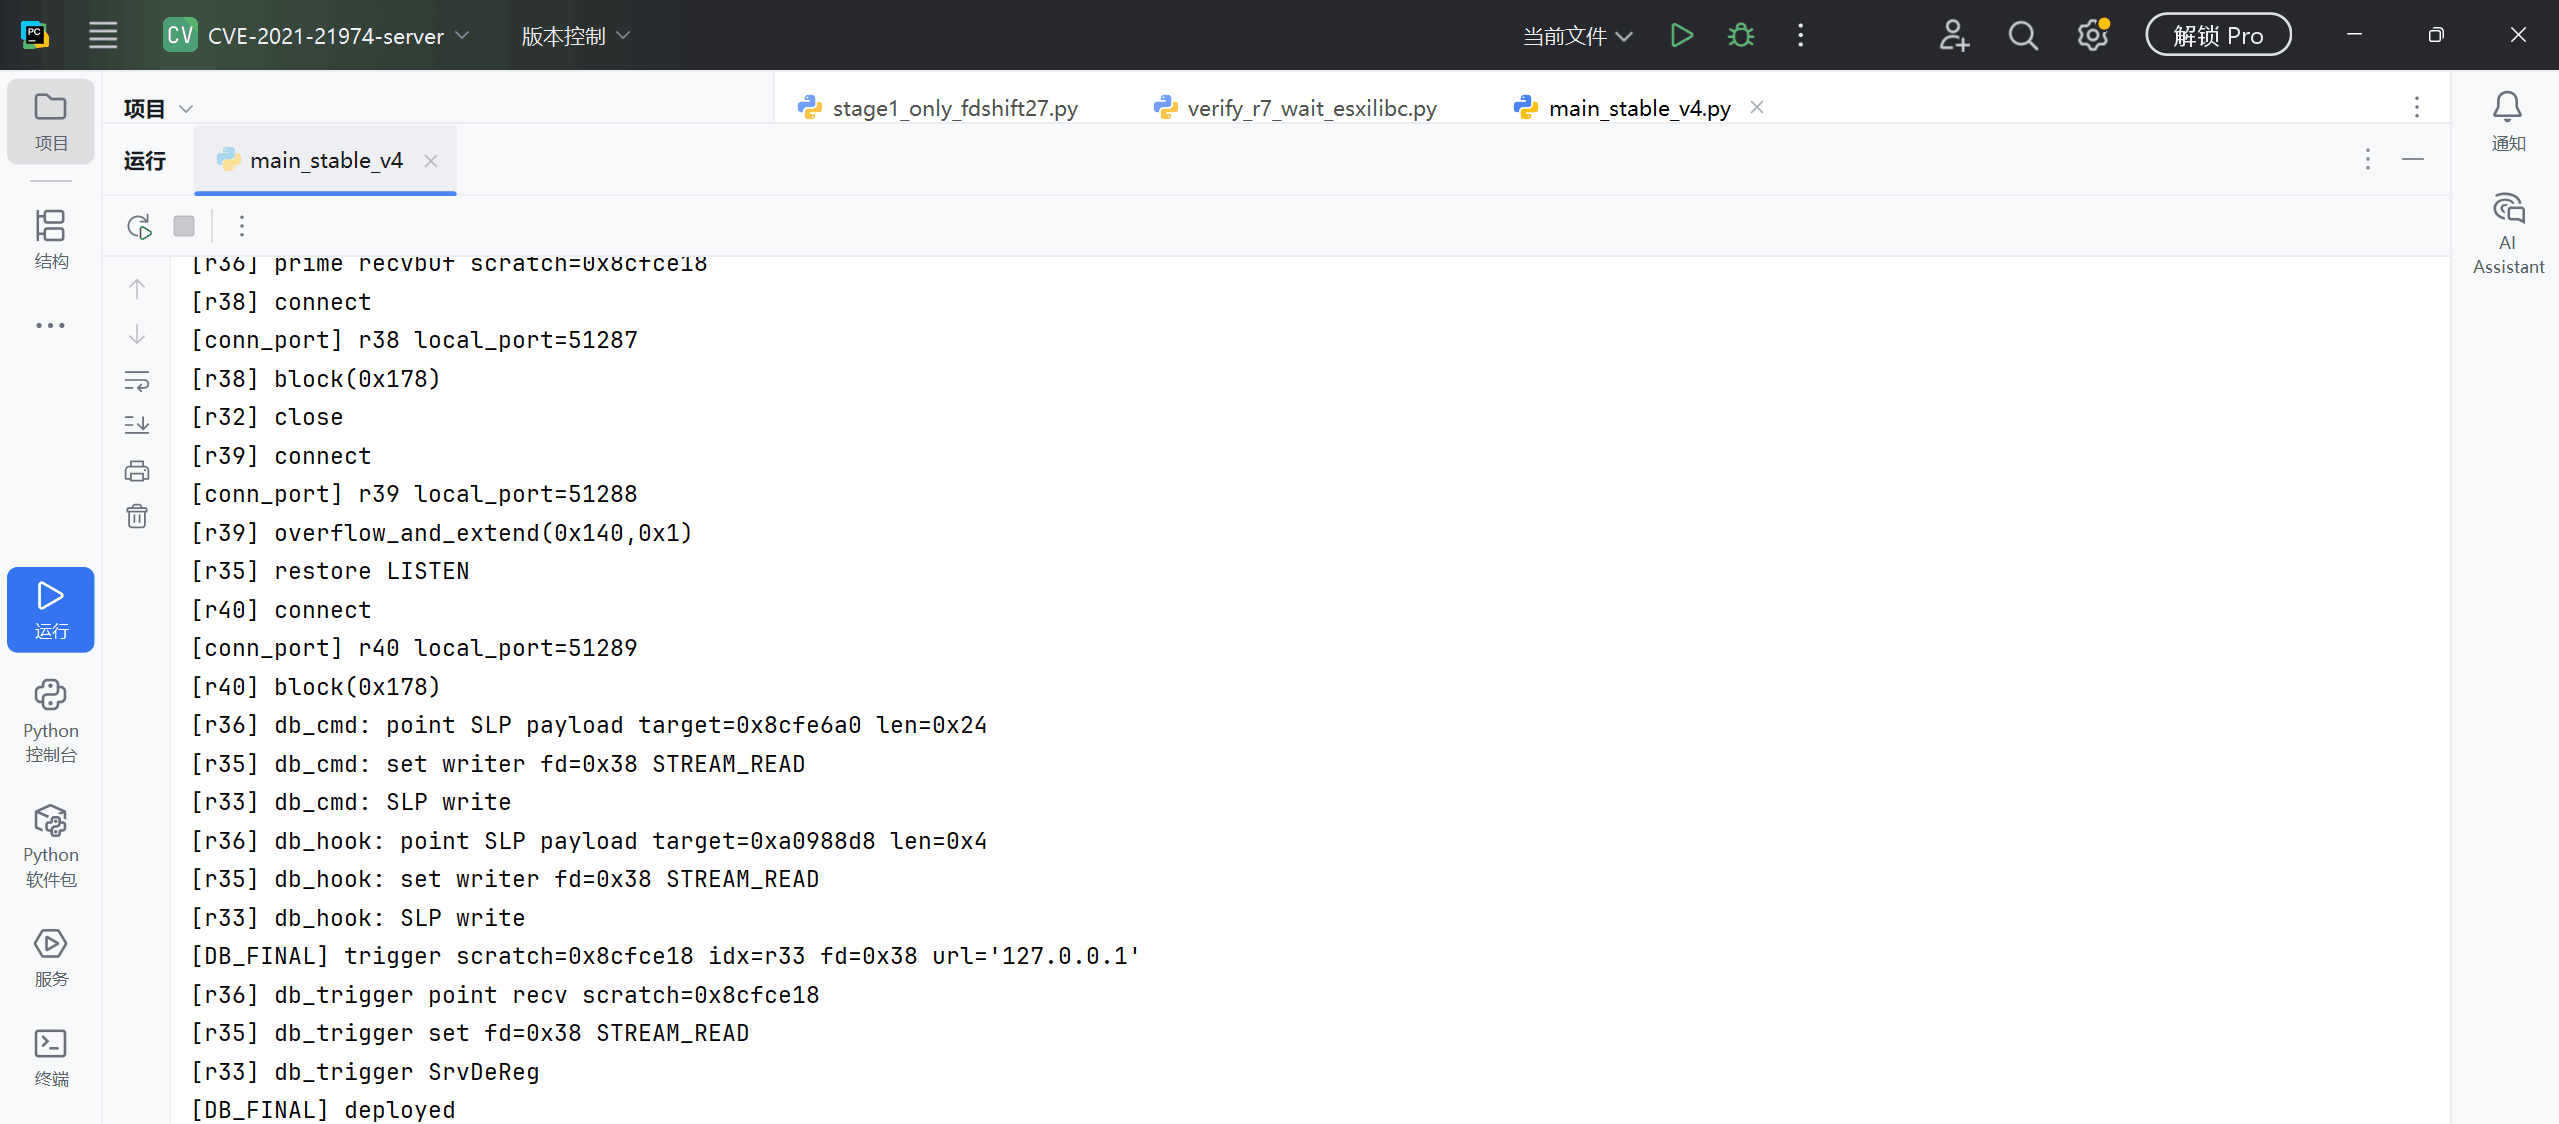
The following two screenshots show the actual execution results of this PoC on ESXi 6.7 build-14320388:
Test Result 1

test result 1

Test Result 2

test result 2

Usage

# 目标 ESXi 主机需运行 slpd 服务(默认 427 端口)
python CVE-2021-21974.py

When the script runs, it prints the author's signature and then executes the full exploit chain: stage1 information leak → arbitrary address read → libc base leak → DB buffer location → overwrite __free_hook with system → SrvDeReg triggers command execution.

Default COMMAND is:

echo PWNED_BY_CVE_2021_21974>/tmp/p

On success, you can see PWNED_BY_CVE_2021_21974 in /tmp/p on the target host.

Note: This PoC is based on fixed heap layout parameters and depends on the slpd/glibc version of the target ESXi 6.7 build-14320388. When switching environments, the fd/size/pacing parameters must be adjusted accordingly.

Disclaimer

This project is intended only for authorized security research and CTF/AWD teaching scenarios, to be verified in isolated sandbox environments. Do not use on unauthorized real systems. Users assume all legal responsibilities arising from its use.


Acknowledgments

  • Author: Aiyakami
Download Tool




