Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-36537-EXPLOIT — CVE-2022-36537 | Kitploit
Tools/GitHubGitHub/agnihackers/cve-2022-36537-exploit
Authentication & AuthorizationVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubagnihackers/cve-2022-36537-exploit

CVE-2022-36537-EXPLOIT

CVE-2022-36537

View Repository
92383 years agoNot yet reviewed
Share
Website

CVE-2022-36537

Summary

R1Soft Server Backup Manager uses the ZK framework as the main framework. Its security requires all Web3 project parties to pay more attention to the security vulnerabilities of various Web3 infrastructures and patch them in time to avoid potential security risks and digital asset losses. We will dig out in time, track various security risks on web3, and provide leading security solutions to ensure that the web3 world chain and off-chain are safe and sound.

Preface

ZK is the leading open-source Java Web framework for building enterprise Web applications. With over 2,000,000 downloads, ZK empowers a wide variety of companies and institutions, ranging from small to Fortune Global 500 in multiple industries.

R1Soft Server Backup Manager (SBM) offers service providers a flexible, server-friendly solution that takes the hassle out of running traditional backups. Users can run backups every 15 minutes without impacting server performance. Nearly 1,800 service providers use it to protect 250,000 servers.

Affected Versions

ZK Framework v9.6.1, 9.6.0.1, 9.5.1.3, 9.0.1.2 and 8.6.4.1.

ConnectWise Recover v2.9.7 and earlier versions are impacted.

R1Soft Server Backup Manager v6.16.3 and earlier versions are impacted.
ZK Framework Auth Bypass

ZK ZK-5150

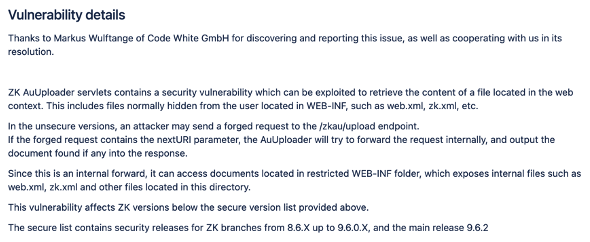
From the vulnerability description, if the route /zkau/upload contains the nextURI parameter, the ZK AuUploader servlet will forward the forward request, which can bypass the identity authentication and return the files in the web context, such as obtaining web.xml, zk page, applicationContext -security.xml configuration information, etc.

Install

You need python3, pip3, git.

git clone https://github.com/agnihackers/CVE-2022-36537-EXPLOIT.git
cd CVE-2022-36537-EXPLOIT
pip3 install -r requirements.txt
chmod +x mysql-connector-java-5.1.48.jar
python3 CVE-2022-36537.py
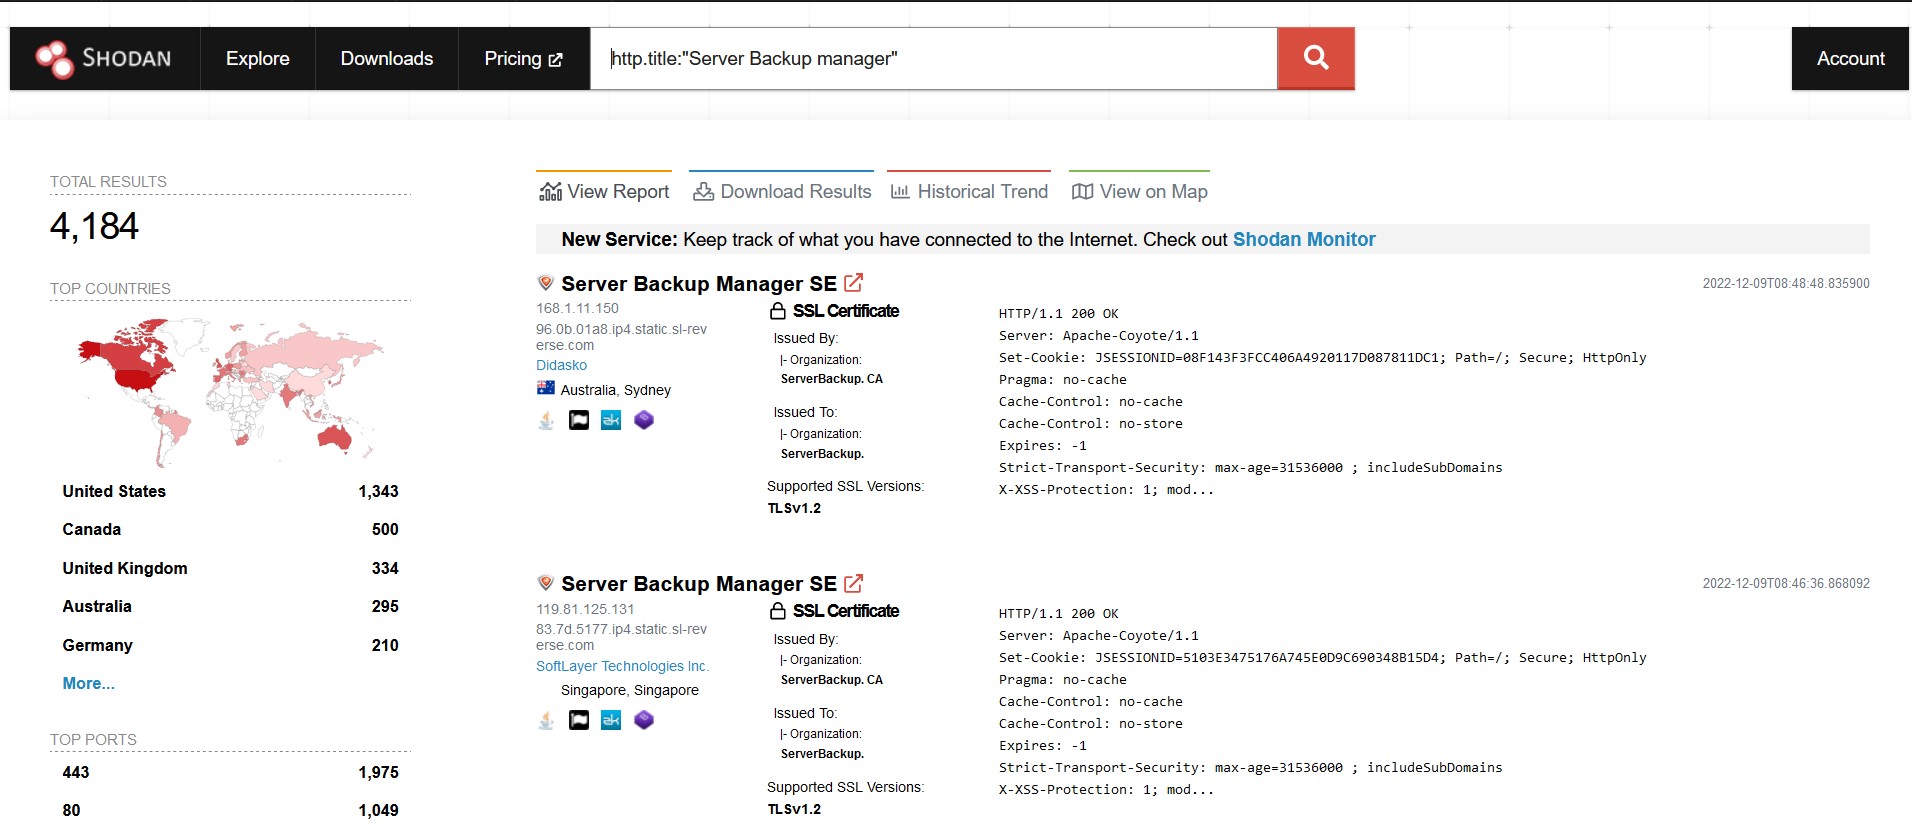
Shodan Dork

shodan

CVE-2022–36537 Vulnerability More Details

https://twitter.com/AGNIHACKERS1/status/1601162549084696579?s=20&t=ncMMG7XNNZDns4Wn5CfPoA

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →