
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Dnsrr — Bash-based DNS enumeration tool performing forward/reverse bruteforce, cache snooping, and zone transfer to extract DNS records and subdomains. | Kitploit
Tools/GitHubGitHub/a3h1nt/dnsrr
ReconnaissanceDNS & Subdomain EnumerationInformation GatheringDNS Analysis
GitHuba3h1nt/dnsrr

Dnsrr

Bash-based DNS enumeration tool performing forward/reverse bruteforce, cache snooping, and zone transfer to extract DNS records and subdomains.

View Repository
12222434 years agoReviewed by Kitploit
Share

DNSrr

DNSrr is a tool written in bash, used to enumerate all the juicy stuff from DNS records, it uses different techniques like

  • DNS Forward Bruteforce
  • DNS Reverse Bruteforce
  • DNS Cache Snooping
  • DNS Zone Transfer

To get you all the information that you can get, from a DNS server.

Installation

Install it using git

git clone https://github.com/A3h1nt/Dnsrr

Get Started

./dnsrr.sh --help

Usage

------------------- USAGE ------------------
-z    : Attempt Zone Transfer
        Syntax: ./dns.sh -z [Nameserver] [Domain Name]
-fb   : Forward Lookup Bruteforce
        Syntax: ./dns.sh [Domain Name]
        Syntax: ./dns.sh [Domain Name] [Wordlist]
-rb   : Reverse Lookup Bruteforce
        Syntax: ./dns.sh [Domain Name]
-cs   : Perform DNS Cache Snooping
        Syntax: ./dns.sh [Name Server] [Wordlist]
-x    : Explain A Particular Option
        Syntax: ./dns.sh -x [Option_Name]
------------------------------------------------

DNSrr supports five different options, including the one that explains the other four options. So just incase you don't know what a particular option is doing, you can simply use -x option, to understand the technique behind it.

Example:

# To explain zone transfer
./dnsrr -x z
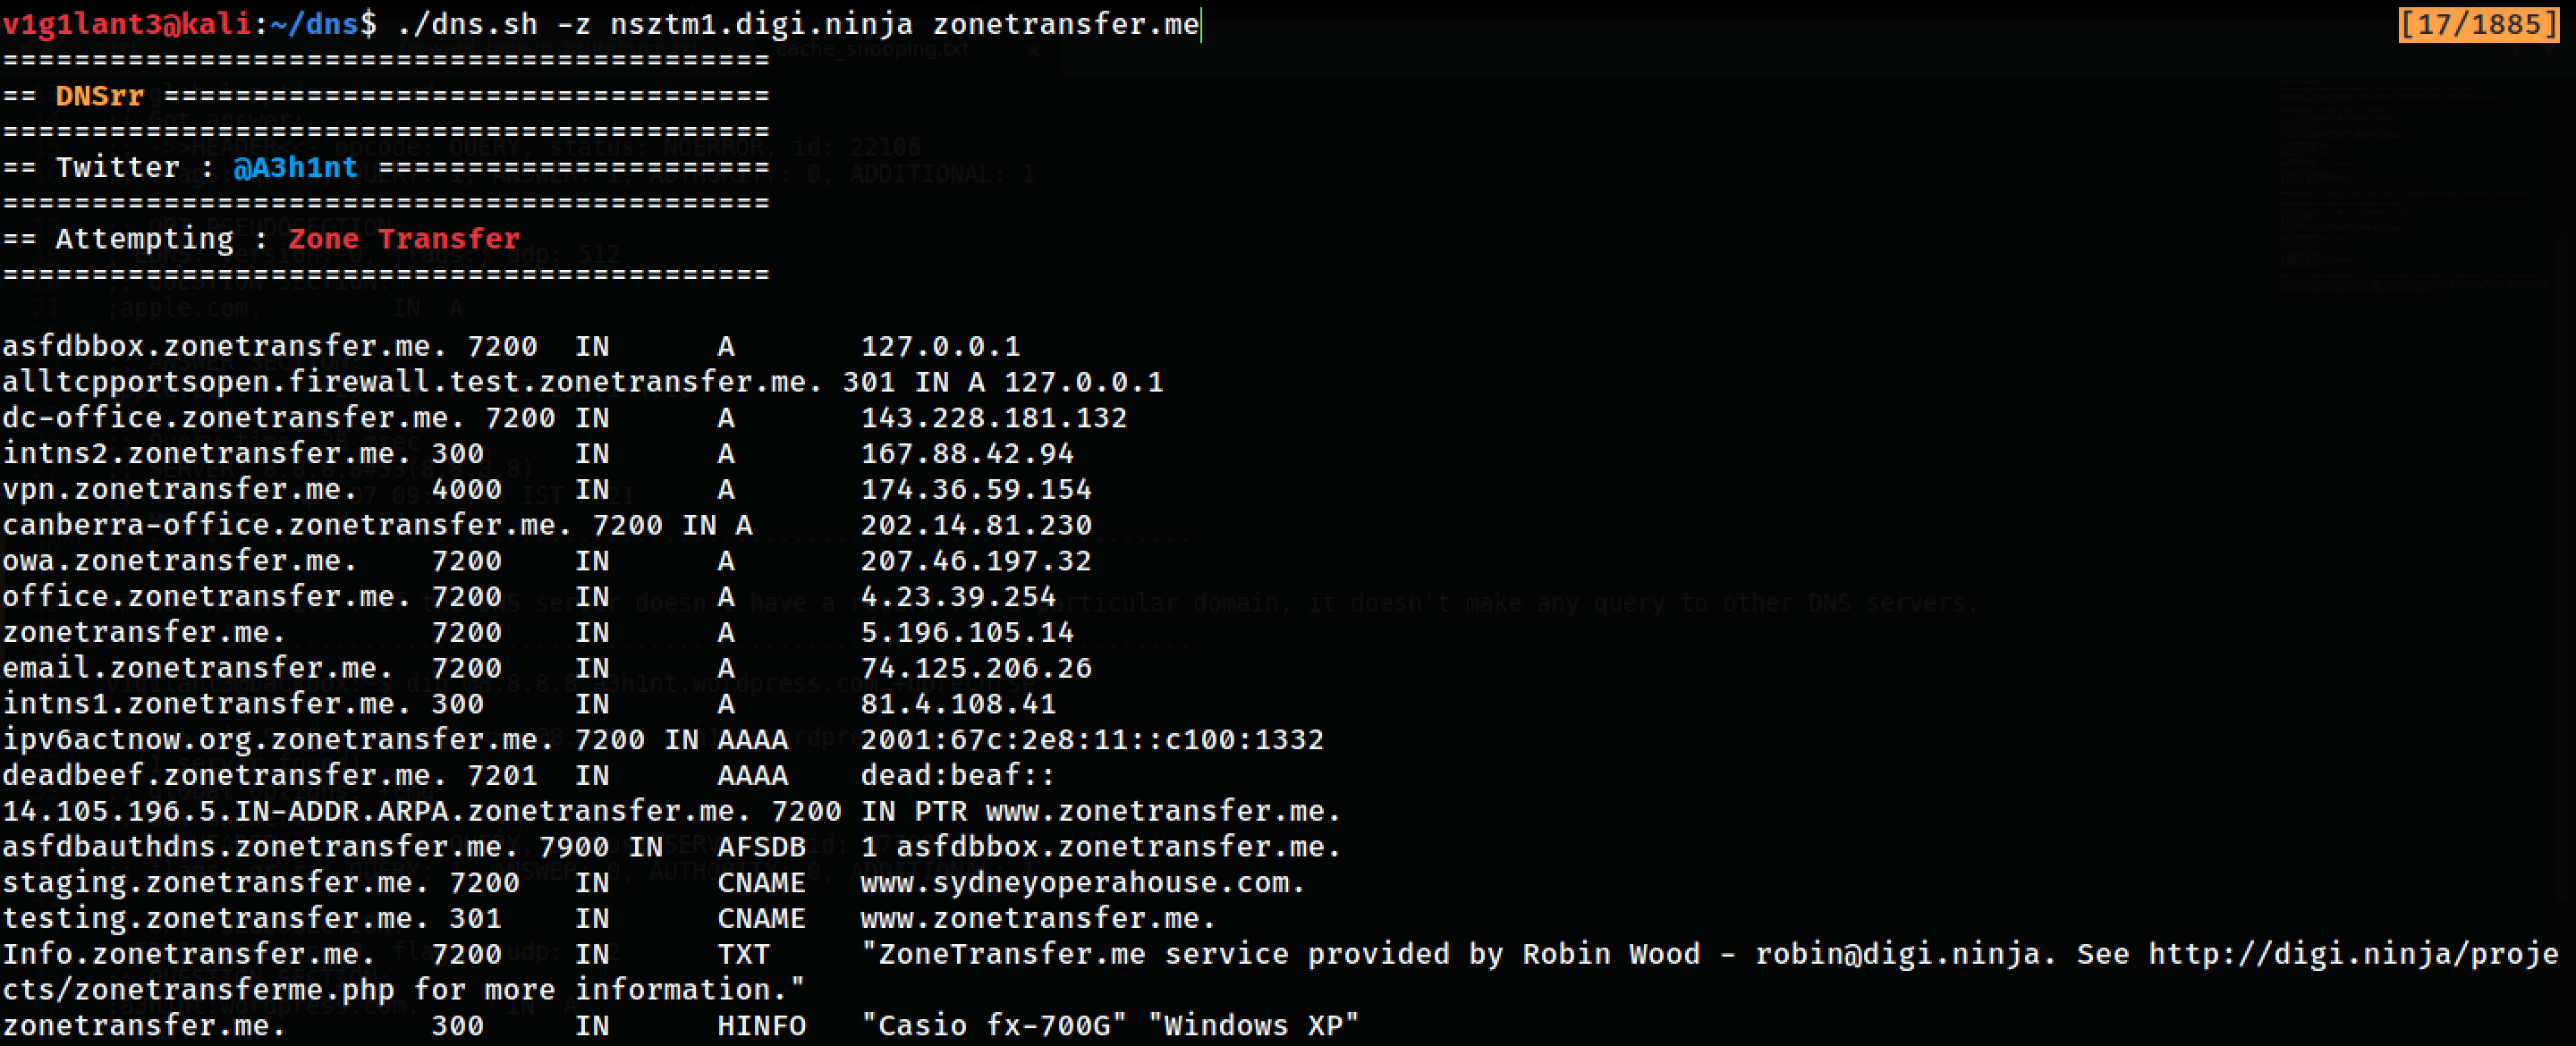
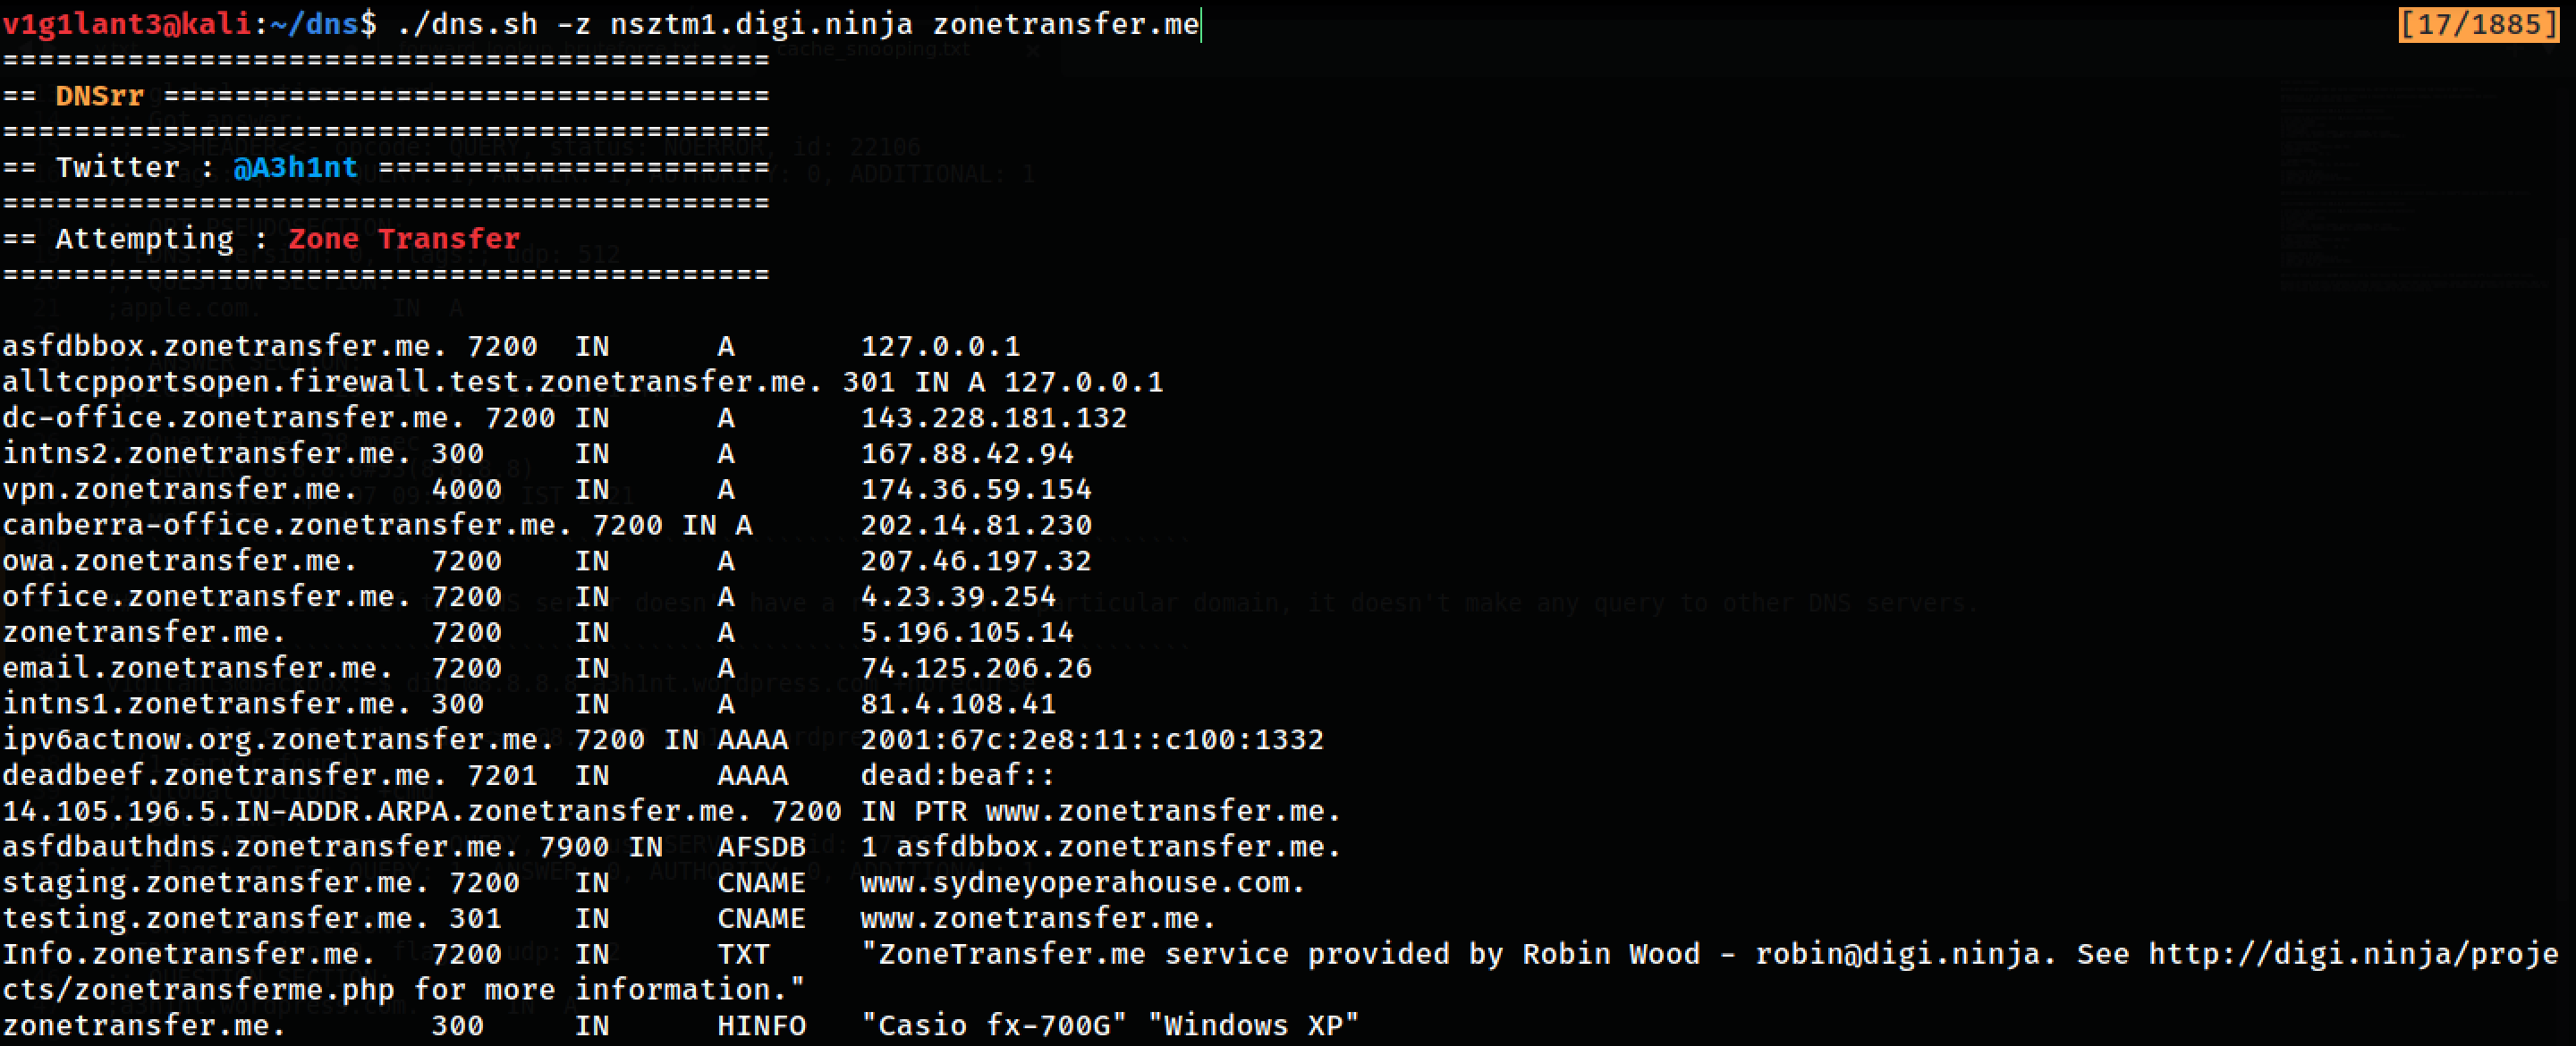
Sample Execution

Zone Transfer

execution

Forward Lookup Bruteforce

execution

To Do

  • Add new techniques that can be used to enumerate data from DNS.
  • Report Bugs
  • Add any new/missing feature.

Contact Me

Ping me at A3h1nt.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →






