Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
poc-cve-xss-encoded-wp-inventory-manager-plugin — PoC for CVE-2023-2123 | Kitploit
Tools/GitHubGitHub/0xn4d/poc-cve-xss-encoded-wp-inventory-manager-plugin
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringWeb SecurityPenetration Testing
GitHub0xn4d/poc-cve-xss-encoded-wp-inventory-manager-plugin

poc-cve-xss-encoded-wp-inventory-manager-plugin

PoC for CVE-2023-2123

View RepositoryWebsite
2223 years agoNot yet reviewed
Share

Update - 5/10/2023

The CVE-2023-2123 ID was reserved and the PoC was published in the WPScan website: https://wpscan.com/vulnerability/44448888-cd5d-482e-859e-123e442ce5c1

Details

Title: Unauthenticated Reflected Cross-Site Scripting in WP Inventory Manager Plugin for WordPress CMS
Date: 2023-04-15
Author: Danilo Albuquerque
Vendor Homepage: https://wordpress.org
Software Link: https://wordpress.org/download
Version: WordPress 6.2
Plugin's Name and Version: WP Inventory Manager 2.1.0.12
Tested on: Brave (Version 1.50.119 Chromium: 112.0.5615.121 (Official Version) 64 bits)

PoC for Reflected XSS vulnerability in WP Inventory Manager 2.1.0.12

  1. Go to the page that has the inventory items;
  2. Access the item that you want;
  3. Fill the form in the "Reserve This Item" section of the page and click on "Reserve" button;
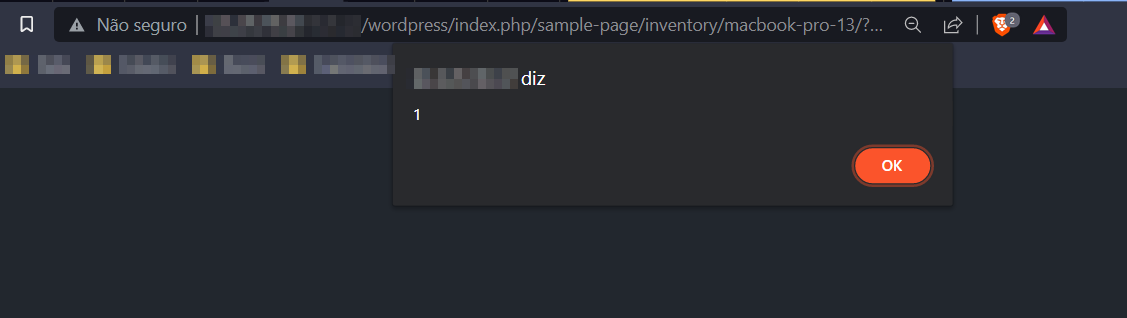
  4. Once you have been redirected to the "Your reservation has been submited" page, add the ENCODED payload %3Cscript%3Ealert%281%29%3C%2Fscript%3E in the message parameter in the URL;
  5. Press enter to do the request and voilá.

When you do all that and update the current page, it will bring you the alert pop-up with the message in it.

Screenshots below

  1. Go to the page that has the inventory items:
    image

  2. Access the item that you want:
    image

  3. Fill the form in the "Reserve This Item" section of the page and click on "Reserve" button:
    image

  4. Once you have been redirected to the "Your reservation has been submited" page, add the ENCODED payload %3Cscript%3Ealert%281%29%3C%2Fscript%3E in the message parameter in the URL:
    image

5.The alert pop-up: image

Bonus

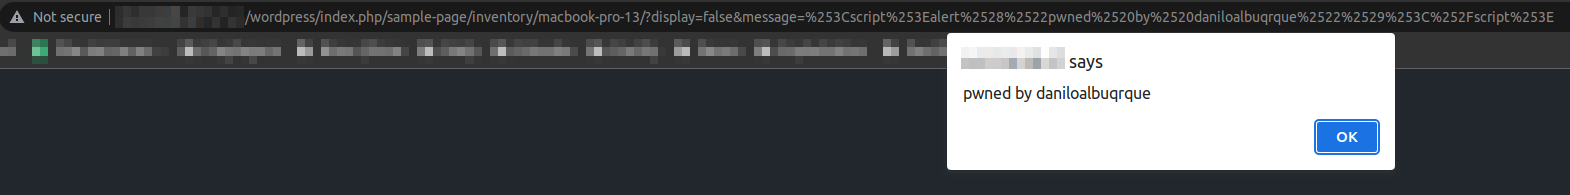
You can also add a DOUBLE ENCODED malicious payload, and the attacker will be able to bypass some security controls such as not accept quotes.

The payload I used: %253Cscript%253Ealert%2528%2522pwned%2520by%2520daniloalbuqrque%2522%2529%253C%252Fscript%253E

Screenshot below:
image

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →