
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-7574 β€” CVE-2026-7574 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-7574
Persistence MechanismsVulnerability AnalysisExploitationPapers & ResearchLearning & EducationCurated Resources
GitHub0xblackash/cve-2026-7574

CVE-2026-7574
CVE-2026-7574

View Repository
1344 months agoNot yet reviewed
Share

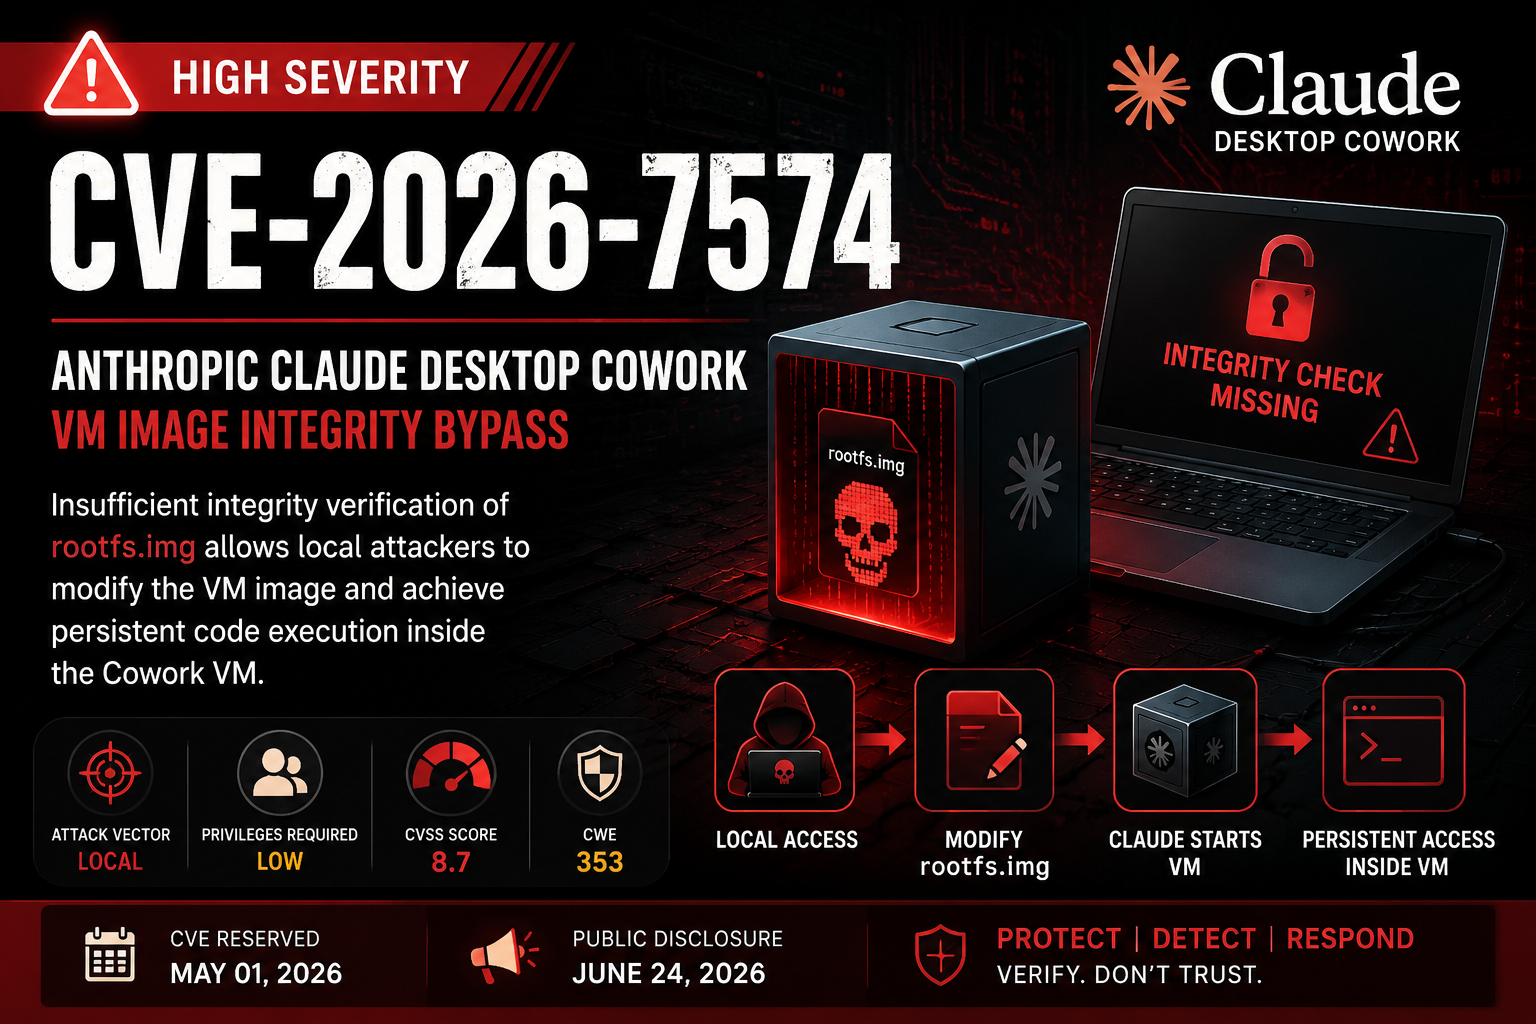
🚨 CVE-2026-7574 β€” Claude Desktop Cowork VM Integrity Bypass

ChatGPT Image Jun 25, 2026, 09_16_52 AM

Anthropic Claude Desktop Cowork VM Image Integrity Bypass

πŸ”₯ Local Persistence Through VM Image Tampering

An integrity validation weakness allowing modification of the Claude Desktop Cowork VM filesystem image (rootfs.img), enabling persistent code execution inside the VM environment.


πŸ“– Overview

CVE-2026-7574 is a high-severity vulnerability affecting Anthropic Claude Desktop Cowork.

The issue arises because the application validates only the existence and version metadata of the virtual machine filesystem image (rootfs.img) before booting the VM. The image contents themselves are not cryptographically verified.

This allows an attacker with local access to replace or modify the VM image and maintain persistent execution capabilities inside the Cowork virtual machine.


🎯 Affected Products

ProductStatus
Claude Desktop CoworkVulnerable
macOS DeploymentsAffected
Linux DeploymentsNot Confirmed
Windows DeploymentsNot Confirmed

Affected Versions

v1.1348.0 – v1.2278.0

⚑ Vulnerability Details

FieldValue
CVECVE-2026-7574
SeverityHigh
CVSS Score8.7
CWECWE-353
Attack VectorLocal
Privileges RequiredLow
User InteractionNone
ScopeChanged
ExploitationPost-Compromise

🧠 Root Cause

The application performs:

βœ“ File Exists
βœ“ Version Matches

βœ— Integrity Validation
βœ— Cryptographic Signature Verification
βœ— Secure Hash Validation

As a result, a modified VM filesystem image is trusted during subsequent launches.


πŸ” Attack Flow

β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
β”‚ Local User Access    β”‚
β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”¬β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜
           β”‚
           β–Ό
β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
β”‚ Modify rootfs.img    β”‚
β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”¬β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜
           β”‚
           β–Ό
β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
β”‚ Claude Starts VM     β”‚
β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”¬β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜
           β”‚
           β–Ό
β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
β”‚ Malicious Image      β”‚
β”‚ Trusted & Executed   β”‚
β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”¬β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜
           β”‚
           β–Ό
β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
β”‚ Persistent Access    β”‚
β”‚ Inside Cowork VM     β”‚
β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜

πŸ’₯ Potential Impact

Persistence

Attackers can maintain code execution across VM restarts.

Data Exposure

Access to directories mounted between the host and VM.

Post-Compromise Activity

Useful for maintaining footholds after initial compromise.

VM Manipulation

Modified environments may execute attacker-controlled services and scripts.


πŸ›  Proof-of-Concept Logic

Educational representation only.

# Locate VM image

rootfs.img

# Modify filesystem image

# Replace startup scripts

# Restart Claude Desktop Cowork

# Modified image executes automatically

πŸ›‘ Detection

Indicators of Compromise

  • Unexpected modification time of rootfs.img
  • Unauthorized VM image replacements
  • Unknown startup scripts inside the VM
  • Persistence surviving application reinstalls
  • Unexpected processes within the Cowork VM

πŸ”’ Mitigation

Immediate Actions

  • Restrict local access.
  • Monitor VM image integrity.
  • Implement filesystem auditing.
  • Review VM startup configurations.
  • Recreate suspicious VM images.

Vendor Recommendation

Implement:

SHA-256 Validation
Cryptographic Signatures
Secure Boot Verification
Image Trust Chains
Runtime Integrity Checks

πŸ“… Timeline

EventDate
CVE Reserved2026-05-01
Public Disclosure2026-06-24
CVE Published2026-06-24

🏷 Classification

CWE-353
Missing Support for Integrity Check

πŸ“š References

  • Public CVE Advisory
  • Vendor Security Bulletin
  • CWE-353 Documentation

⚠ Disclaimer

This repository is intended for:

  • Security Research
  • Vulnerability Awareness
  • Defensive Security Education
  • Incident Response Preparation

Do not use this information to attack systems without explicit authorization.


πŸ”΄ CVE-2026-7574

Claude Desktop Cowork VM Integrity Bypass

Persistence Through Trust Without Verification

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    936
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    353
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    348
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    288

Explore all tools

Browse our collection of tools

View all tools β†’






