 0xblackash/cve-2026-64638
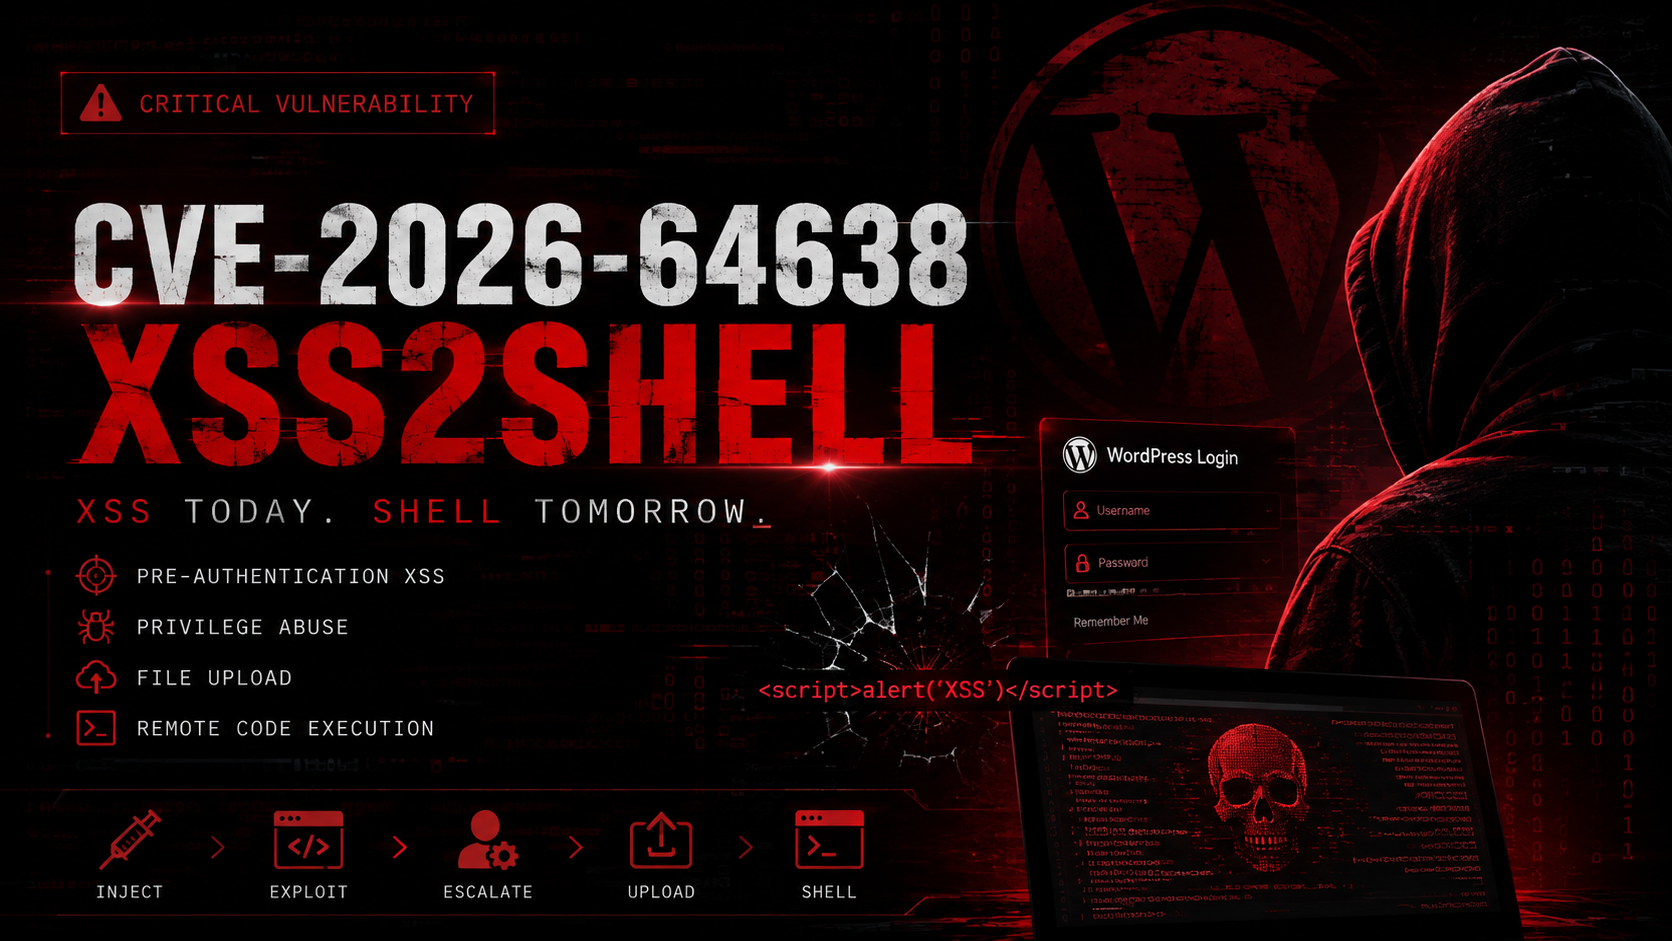
CVE-2026-64638

XSS2Shell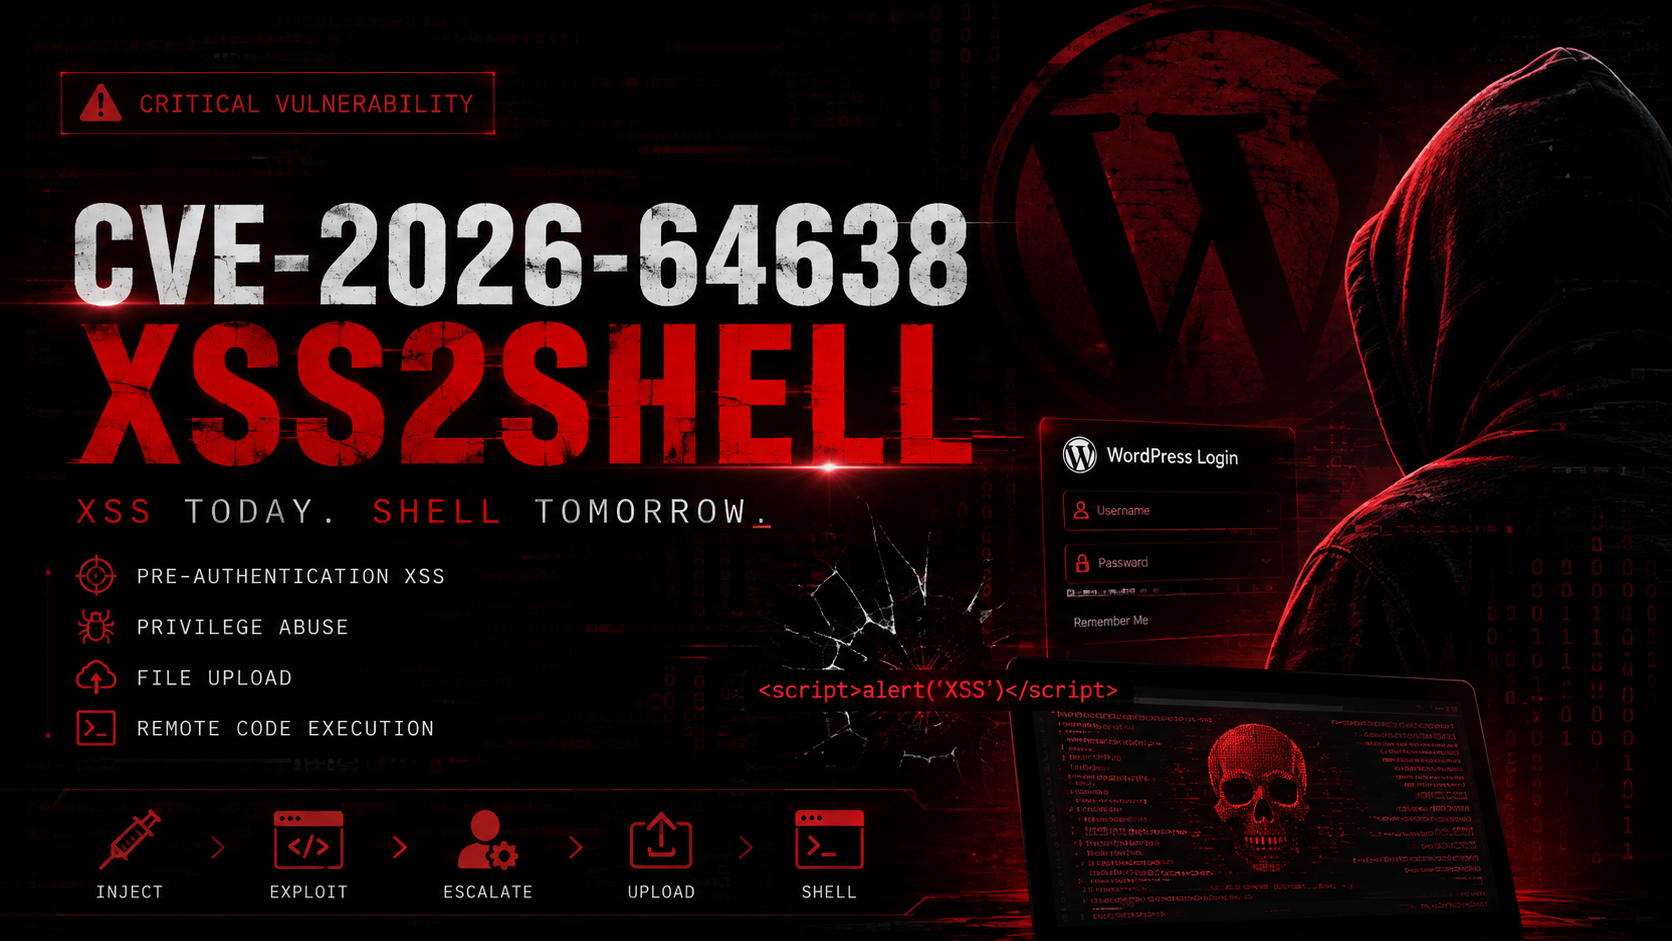
with potential escalation to PHP Code Execution
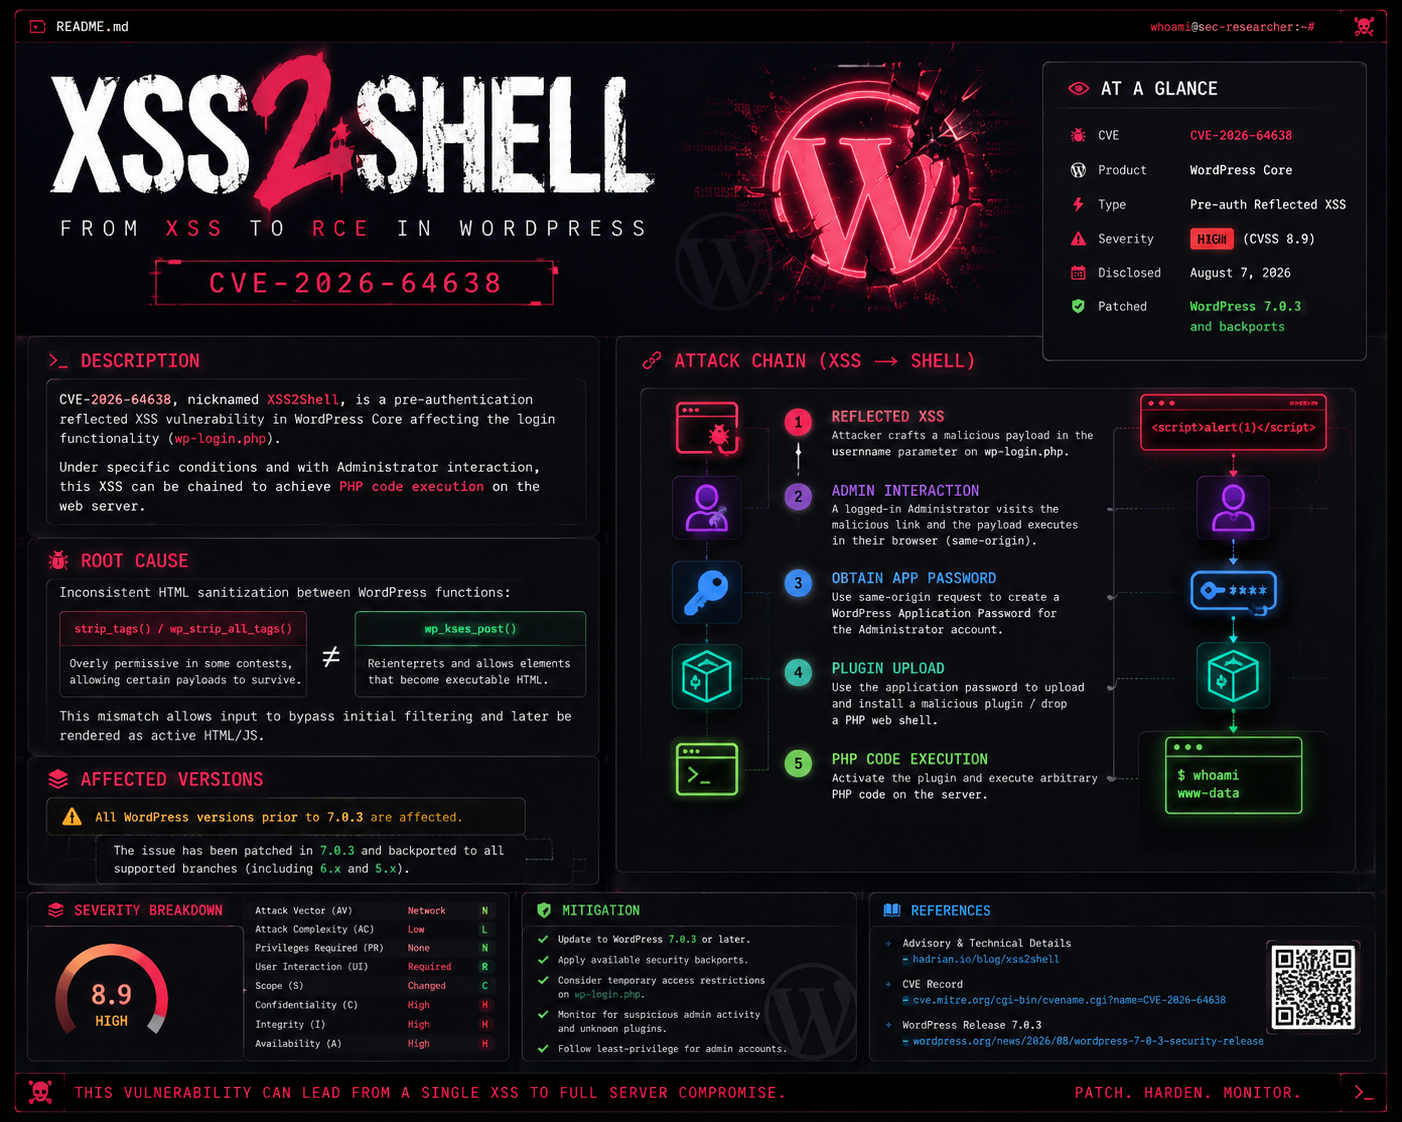
CVE-2026-64638 is a high-severity pre-authentication reflected Cross-Site Scripting (XSS) vulnerability affecting the WordPress login screen.
Under specific conditions, the flaw can be chained into Remote Code Execution (RCE) on the server (researchers call the chain XSS2Shell).
| Attribute | Details |
|---|---|
| CVE ID | CVE-2026-64638 |
| Severity | High (CVSS 8.9) |
| Attack Vector | Network |
| Privileges Required | None |
| User Interaction | Required (for full RCE chain) |
| Impact | Confidentiality • Integrity • Availability |
The vulnerability exists in the way WordPress handles the username on a failed login attempt.
sanitize_user() and wp_strip_all_tags() (which relies on PHP’s strip_tags()).wp_kses_post() allows certain tag-like payloads containing whitespace to survive and become live DOM elements.user-profile.js) loaded on the login page.Full RCE path requires:
⚠️ WordPress notes that successful escalation to RCE depends on conditions outside the attacker’s full control and requires social engineering.
| Branch | Affected Versions | Patched Version |
|---|---|---|
| 7.0.x | 7.0.0 – 7.0.2 | 7.0.3 |
| 6.9.x | 6.9.0 – 6.9.5 | 6.9.6 |
| 6.8.x | 6.8.0 – 6.8.6 | 6.8.7 |
| … | … | … |
| 4.7.x | 4.7.0 – 4.7.33 | 4.7.34 |
GitHub Security Advisory
GHSA-52p2-r8wf-jcrf
WordPress 7.0.3 Release
wordpress.org/news/2026/08/wordpress-7-0-3-release/
Technical Analysis
The Hacker News – New WordPress Pre-Auth XSS
Stay safe. Patch early. Verify your WordPress version today.
wp core version · Check for updates in the admin dashboard