Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-60206 β€” CVE-2026-60206 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-60206
Indicator of Compromise (IOC) ManagementPrivilege EscalationVulnerability AnalysisThreat IntelligenceAuthenticationLearning & EducationIncident Response
GitHub0xblackash/cve-2026-60206

CVE-2026-60206

CVE-2026-60206

View Repository
21363 months agoNot yet reviewed
Share

🚨 CVE-2026-60206 β€” WebLogic SAML Takeover

ChatGPT Image Jul 24, 2026, 02_29_11 AM

Oracle WebLogic Server SAML Authentication Vulnerability

A technical analysis of CVE-2026-60206 affecting Oracle WebLogic Server.


πŸ“– Overview

CVE-2026-60206 is a Critical (CVSS 9.9) vulnerability affecting Oracle WebLogic Server. According to Oracle, a low-privileged authenticated attacker with network access via SAML can exploit the vulnerability to completely compromise a vulnerable WebLogic instance.

⚠️ This repository is intended for educational, defensive, and research purposes only.


πŸ“Š Vulnerability Details

PropertyValue
CVECVE-2026-60206
SeverityCritical
CVSS v3.19.9
Attack VectorNetwork
Attack ComplexityLow
Privileges RequiredLow
User InteractionNone
ScopeChanged
Affected ComponentOracle WebLogic Server (Core)
Access MethodSAML Authentication

🎯 Affected Versions

  • Oracle WebLogic Server 12.2.1.4.0
  • Oracle WebLogic Server 14.1.1.0.0
  • Oracle WebLogic Server 14.1.2.0.0
  • Oracle WebLogic Server 15.1.1.0.0

⚑ Potential Impact

Successful exploitation may allow an authenticated attacker to:

  • Complete server compromise
  • Privilege escalation
  • Unauthorized administrative actions
  • Confidentiality breach
  • Integrity compromise
  • Service disruption
  • Potential lateral movement into connected Oracle infrastructure

πŸ— Attack Flow

Authenticated User
        β”‚
        β–Ό
Network Access via SAML
        β”‚
        β–Ό
Exploit Authentication Logic
        β”‚
        β–Ό
Privilege Escalation
        β”‚
        β–Ό
Full WebLogic Compromise

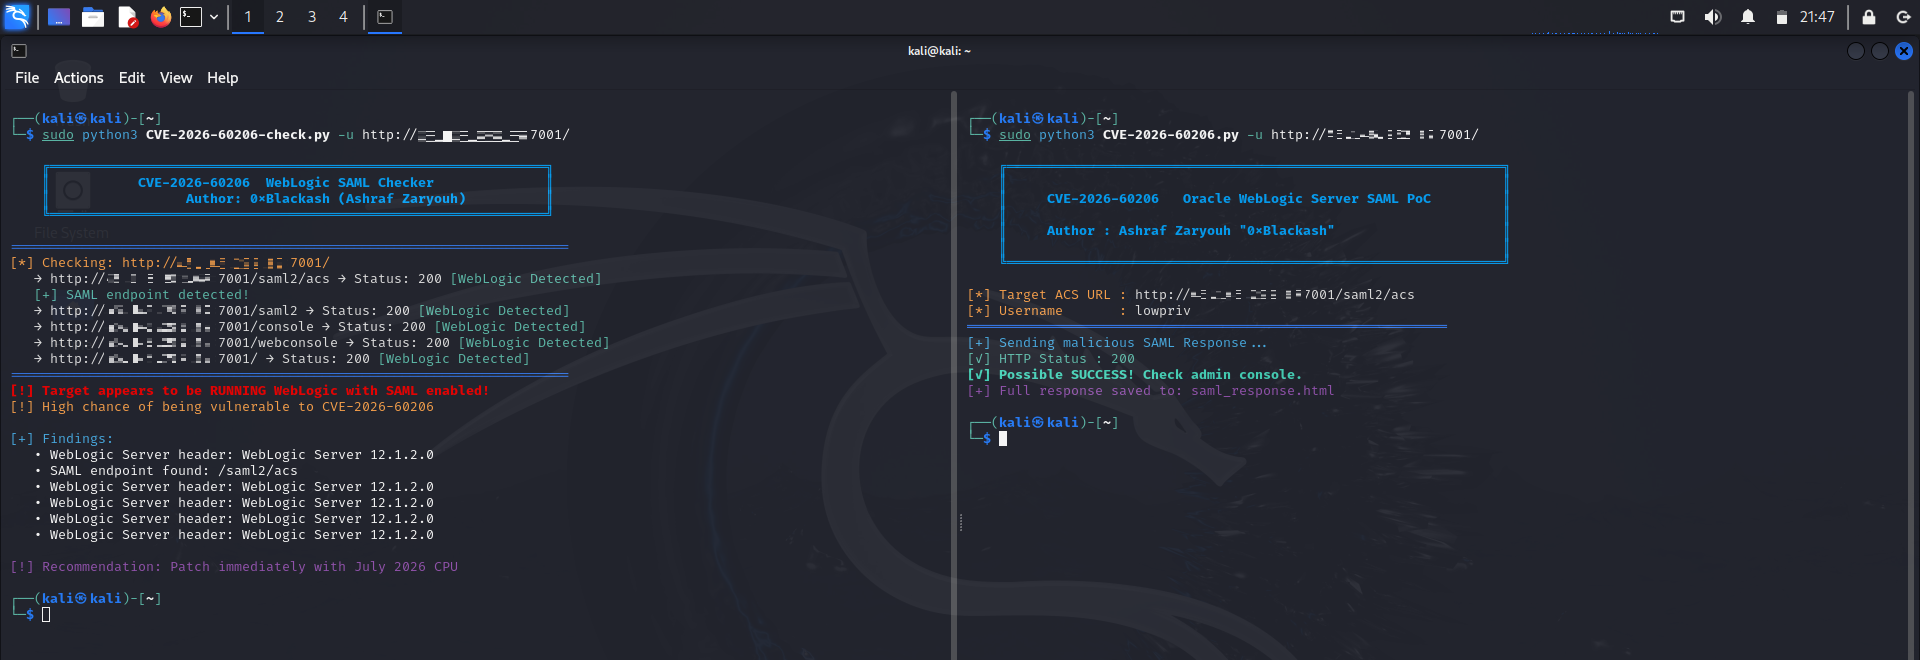
πŸ“Έ Demo

CVE-2026-60206

πŸ” Detection

Security teams should monitor for:

  • Unusual SAML authentication activity
  • Unexpected administrative logins
  • Privilege escalation events
  • Suspicious WebLogic audit logs
  • Authentication anomalies from unfamiliar IP addresses

πŸ›‘ Mitigation

  • Apply Oracle's July 2026 Critical Patch Update.
  • Upgrade to a patched release.
  • Restrict SAML endpoints to trusted identity providers.
  • Limit network exposure of WebLogic administration services.
  • Enable detailed authentication and audit logging.
  • Continuously monitor for suspicious authentication events.

πŸ“ Repository Structure

.
β”œβ”€β”€ README.md
β”œβ”€β”€ LICENSE
β”œβ”€β”€ docs/
β”‚   β”œβ”€β”€ advisory.md
β”‚   β”œβ”€β”€ timeline.md
β”‚   └── references.md
β”œβ”€β”€ detection/
β”‚   β”œβ”€β”€ sigma/
β”‚   └── yara/
β”œβ”€β”€ iocs/
β”‚   └── indicators.md
└── screenshots/

πŸ“š References

  • Oracle Critical Patch Update Advisory
  • Oracle WebLogic Documentation
  • NIST National Vulnerability Database (NVD)
  • MITRE CVE Program

⚠️ Disclaimer

This repository does not include exploit code. It is intended solely for:

  • Security awareness
  • Defensive research
  • Vulnerability management
  • Detection engineering
  • Incident response
  • Patch validation

Users are responsible for complying with all applicable laws and organizational policies.

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools β†’