
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-55200 β€” CVE-2026-55200 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-55200
Vulnerability AnalysisExploitationPapers & ResearchLearning & EducationBinary Exploitation
GitHub0xblackash/cve-2026-55200

CVE-2026-55200

CVE-2026-55200

View Repository
102284 months agoNot yet reviewed
Share

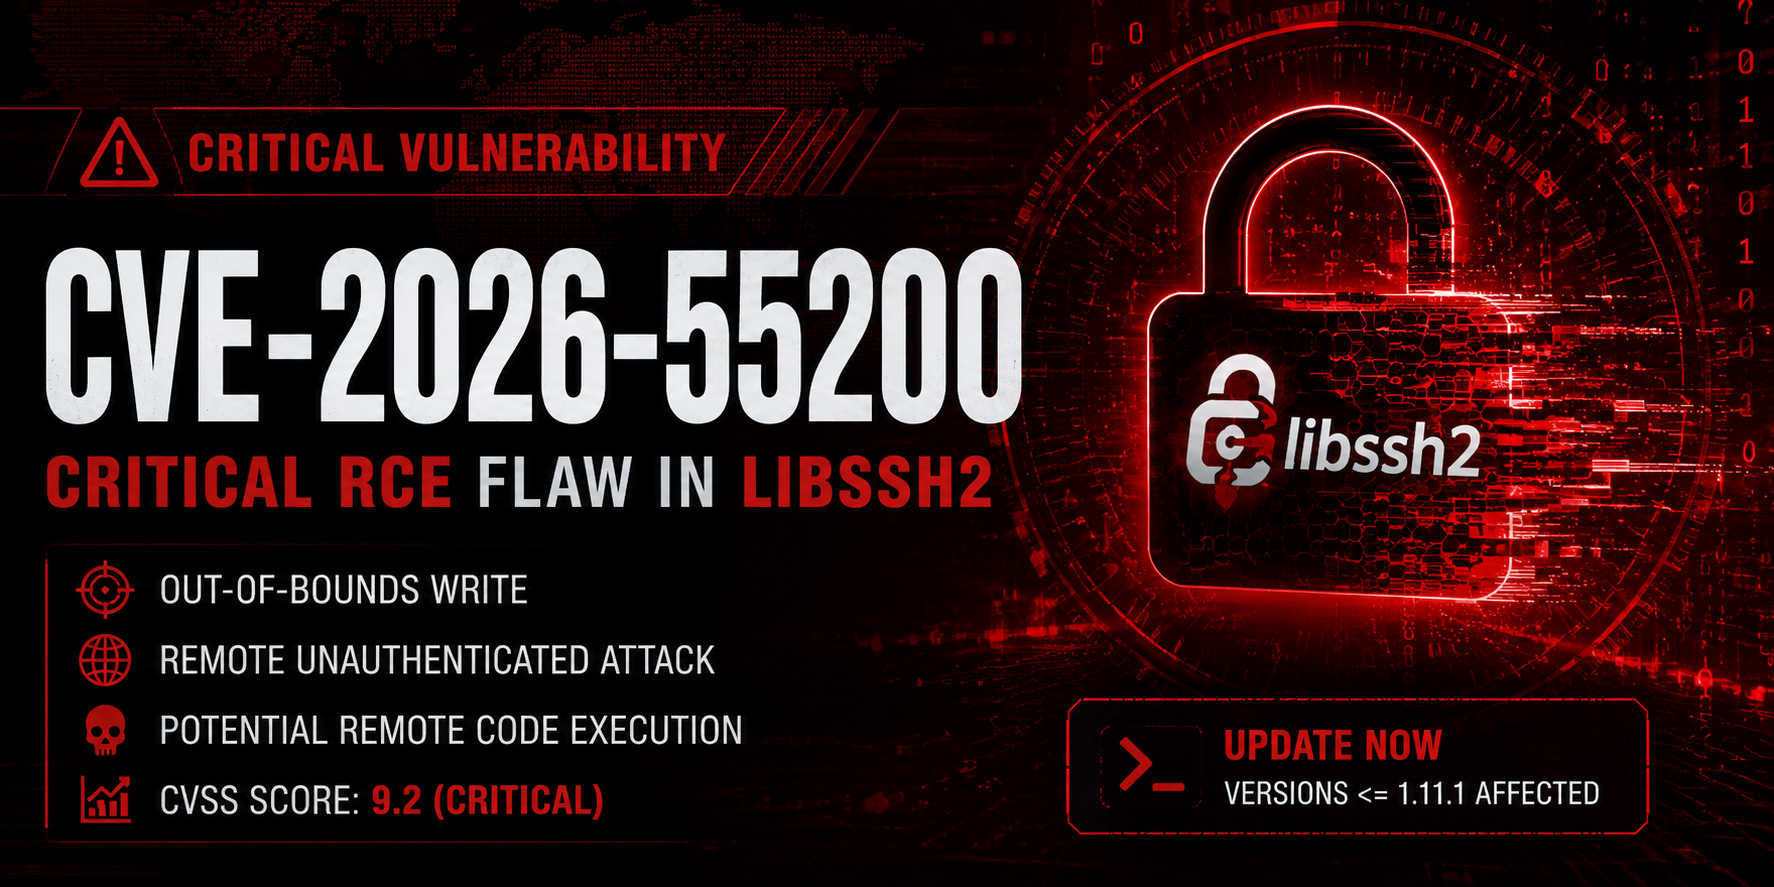
🚨 CVE-2026-55200 - Critical libssh2 Out-of-Bounds Write Vulnerability

ChatGPT Image Jun 23, 2026, 10_27_12 PM

Severity CVSS Type Impact


πŸ“Œ Overview

CVE-2026-55200 is a critical memory corruption vulnerability affecting the widely deployed libssh2 library.

The flaw arises from improper validation of the SSH packet length field during packet processing, potentially allowing a remote attacker to trigger heap corruption and, under certain circumstances, achieve Remote Code Execution (RCE).


πŸ”₯ Severity

MetricValue
CVE IDCVE-2026-55200
SeverityCritical
CVSS Score9.2
Attack VectorNetwork
Privileges RequiredNone
User InteractionNone
ImpactRCE / DoS

🎯 Affected Software

ComponentAffected Versions
libssh2<= 1.11.1

🧠 Technical Details

Vulnerable Function

ssh2_transport_read()

Root Cause

The SSH transport layer fails to properly validate the incoming:

packet_length

field before allocating and processing packet data.

An attacker can send a specially crafted SSH packet containing an oversized length value that causes:

  • Heap corruption
  • Out-of-Bounds Write
  • Process crash
  • Potential arbitrary code execution

πŸ“Έ Demo

CVE-2026-55200

βš”οΈ Attack Flow

Attacker
    β”‚
    β–Ό
Crafted SSH Packet
    β”‚
    β–Ό
Malformed packet_length
    β”‚
    β–Ό
Heap Corruption
    β”‚
 β”Œβ”€β”€β”΄β”€β”€β”
 β–Ό     β–Ό
DoS   RCE

πŸ’₯ Impact

Availability

  • Service crash
  • Denial of Service (DoS)

Integrity

  • Memory corruption
  • Potential code execution

Confidentiality

  • Possible memory disclosure through exploitation chains

πŸ” Detection

Security teams should monitor for:

  • Unexpected crashes in SSH-enabled services
  • Segmentation faults
  • Heap corruption events
  • Abnormal SSH connection attempts
  • Application logs containing packet parsing errors

πŸ›‘οΈ Mitigation

Immediate Actions

  • Upgrade to the latest patched version of libssh2
  • Apply vendor security updates
  • Restrict SSH exposure where possible
  • Review internet-facing services

Hardening Recommendations

βœ“ Enable ASLR
βœ“ Enable Stack Canaries
βœ“ Enable PIE
βœ“ Apply latest security patches
βœ“ Conduct dependency audits

πŸ“Š Risk Assessment

CategoryRating
ExploitabilityHigh
ComplexityLow
AuthenticationNot Required
Remote AttackYes
Public Exposure RiskHigh

πŸ“š References

  • libssh2 Security Advisory
  • Vendor Security Bulletins
  • CVE Database Entries
  • Security Research Publications

🚨 Executive Summary

CVE-2026-55200 is a critical Out-of-Bounds Write vulnerability in libssh2 that may allow unauthenticated remote attackers to corrupt memory, crash services, or potentially execute arbitrary code. Organizations should prioritize patching immediately and assess all systems using vulnerable libssh2 versions.


⭐ If this repository helped your research, consider giving it a star.

Cybersecurity β€’ Vulnerability Research β€’ Threat Intelligence

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools β†’