
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/0xblackash/cve-2026-46300
Privilege EscalationVulnerability AnalysisExploitationPapers & ResearchLearning & EducationBinary ExploitationLabs & Practice
GitHub0xblackash/cve-2026-46300

CVE-2026-46300

CVE-2026-46300

View Repository
158396 months agoNot yet reviewed
Share

🛡️ CVE-2026-46300 - Fragnesia

ChatGPT Image May 16, 2026, 10_19_32 AM

Severity Linux Local Affected

A Clean & Deadly Page-Cache Attack

Variant of the "Dirty Frag" family


📌 Overview

CVE-2026-46300 (Fragnesia) is a high-severity logic flaw in the Linux kernel's socket buffer handling (skb_try_coalesce()) within the XFRM/ESP-in-TCP subsystem (espintcp ULP).

An unprivileged local attacker can achieve arbitrary byte writes into the kernel page cache of any readable file — including system binaries like /usr/bin/su — leading to reliable local root privilege escalation.


✨ Key Highlights

  • ✅ No race condition required
  • ✅ Works purely in page cache (on-disk files untouched)
  • ✅ Uses splice() / sendfile() + controlled AES-GCM decryption
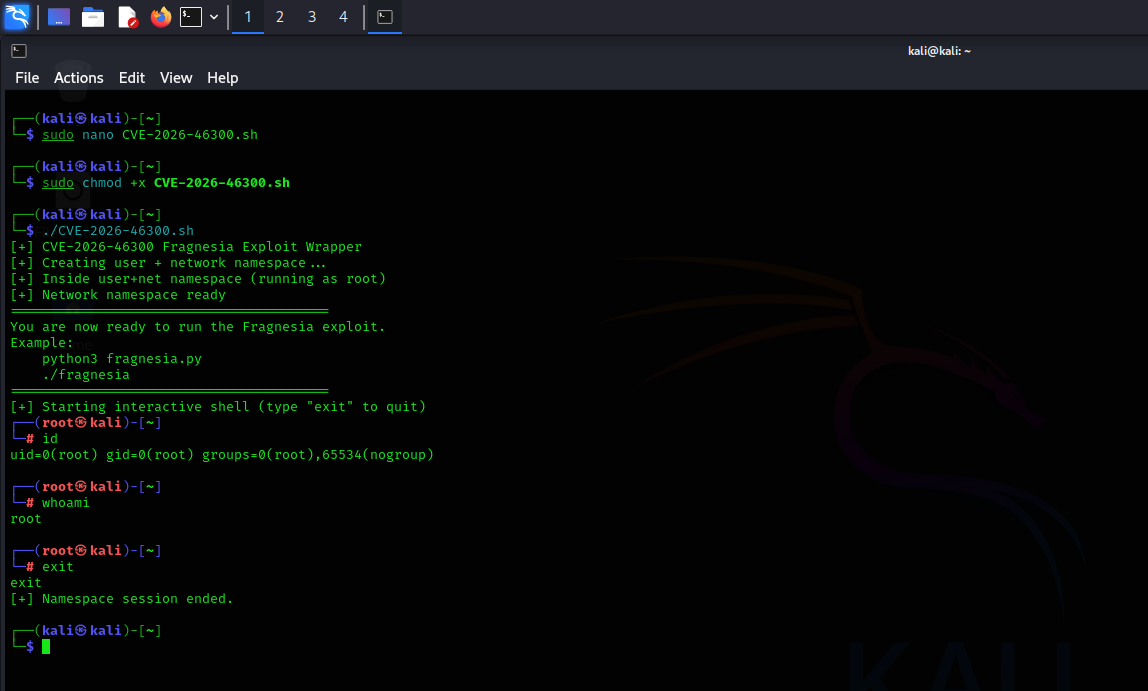
  • ✅ Public Proof-of-Concept available
  • ✅ Affects most major Linux distributions

🛠 Demo

frangnesia

Root Cause: Improper propagation of the SKBFL_SHARED_FRAG marker when coalescing socket buffers, allowing attacker-controlled decryption to corrupt page-cache pages.


🎯 Impact

TargetEffectSeverity
/usr/bin/su, /bin/sudoCode execution as rootCritical
Any readable fileSilent corruption in page cacheHigh
Container environmentsHost escape possibleHigh

🛡️ Mitigation

1. Update (Recommended)

Update to the latest patched kernel from your distribution.

2. Immediate Workaround

sudo sh -c "printf 'install esp4 /bin/false\ninstall esp6 /bin/false\ninstall rxrpc /bin/false\n' > /etc/modprobe.d/fragnesia.conf"
sudo rmmod esp4 esp6 rxrpc 2>/dev/null || true

3. Drop Page Cache (if suspicious)

sudo sh -c 'echo 3 > /proc/sys/vm/drop_caches'

📥 Proof of Concept

Repository: v12-security/pocs - Fragnesia

⚠️ For educational and defensive purposes only.


📚 References

  • AlmaLinux Security Blog
  • Ubuntu Security Notice
  • Red Hat Security Advisory
  • Linux netdev mailing list patch discussion

Made with ❤️ for the security community

Stay safe. Patch fast.

CVE-2026-46300 • May 2026

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →





