Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-45829 β€” CVE-2026-45829 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-45829
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationRemote Access Tool
GitHub0xblackash/cve-2026-45829

CVE-2026-45829

CVE-2026-45829

View Repository
346 months agoNot yet reviewed
Share

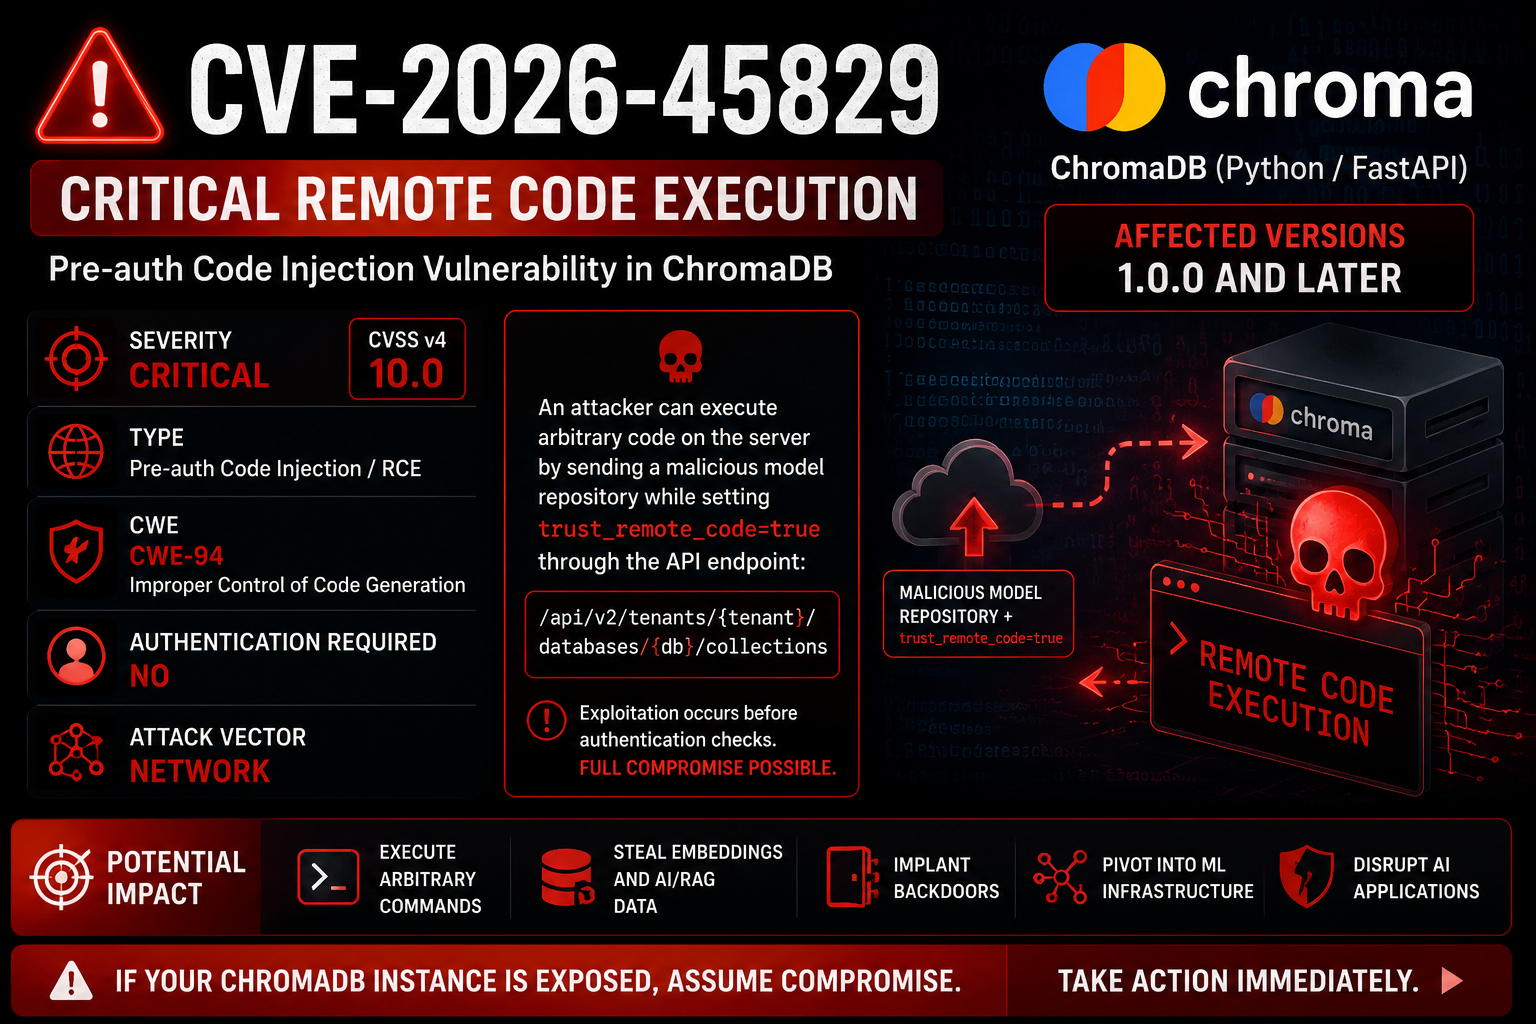
🚨 CVE-2026-45829 - ChromaDB Pre-Auth RCE

ChatGPT Image May 21, 2026, 12_28_26 PM

Critical Remote Code Execution in ChromaDB Vector Database

Critical RCE Unauthenticated


πŸ“Œ Overview

CVE-2026-45829 is a critical pre-authentication Remote Code Execution vulnerability in ChromaDB, a popular open-source AI Vector Database.

An unauthenticated attacker can exploit the way ChromaDB handles embedding function configuration to achieve full remote code execution on the server.

Key Information

ItemDetails
CVE IDCVE-2026-45829
SeverityCritical (CVSS 9.8)
Affected ComponentEmbedding Function Handler
Attack VectorUnauthenticated HTTP Request
ImpactRemote Code Execution (RCE)
Affected VersionsChromaDB β‰₯ 1.0.0 (including latest 1.5.x)

πŸ§ͺ How The Exploit Works

  1. Attacker sends a crafted POST request to collection creation endpoint.
  2. ChromaDB processes the embedding_function configuration before authentication.
  3. trust_remote_code=True allows loading of malicious code.
  4. Attacker can execute arbitrary Python code on the server via model_name field.

🎯 Expected Results (If Exploit Works)

╔══════════════════════════════════════════════════════════════╗
β•‘                 CVE-2026-45829 - ChromaDB RCE                β•‘
β•‘                Pre-Auth Remote Code Execution                β•‘
β•šβ•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•β•

[*] Attacking ChromaDB β†’ http://target:8000

[+] EXPLOIT SUCCESS!
[+] Command executed: whoami
[+] Check /tmp/chromapwned.txt on target

After Success You Can:

  • Read /etc/passwd
  • Get reverse shell
  • Dump environment variables
  • Install backdoors

πŸ›  Mitigation

  • Update ChromaDB immediately when patch is released.
  • Do NOT expose ChromaDB directly to the internet.
  • Disable trust_remote_code if possible.
  • Use strong authentication + network segmentation.

πŸ” Shodan / FoFa Dorks

FoFa:

app="ChromaDB" || title="Chroma"

Shodan:

"ChromaDB" OR "Chroma HTTP Server" port:8000

⚠️ Legal Disclaimer

This information and PoC are provided for educational and authorized security testing purposes only.
Unauthorized scanning or exploitation of systems you do not own is illegal.


Made with ❀️ for security researchers

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    593
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    371
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    336
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    322

Explore all tools

Browse our collection of tools

View all tools β†’