Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/0xblackash/cve-2026-109618
Defensive ToolsVulnerability AnalysisExploitationWeb SecurityThreat IntelligencePapers & ResearchIncident Response
GitHub0xblackash/cve-2026-109618

CVE-2026-109618

Technical advisory on the PHP2Shell RCE flaws (CVE-2026-109618, CVE-2026-109619) covering root cause, exploitation vectors, detection checks, and PHP mitigation guidance.

View Repository
19121 days agoNot yet reviewed
Share

🟣 CVE-2026-109618/19 - PHP2Shell

PHP2Shell Runtime Vulnerabilities

CVE-2026-109618 CVE-2026-109619 PHP Impact License

Technical advisory, threat intelligence, and detection signatures for the PHP2Shell Remote Code Execution vulnerabilities.


📌 Overview

PHP2Shell refers to a pair of zero-day/critical vulnerabilities discovered in the PHP core engine (CVE-2026-109618 and CVE-2026-109619). These vulnerabilities allow unauthenticated attackers to execute arbitrary code (RCE) on servers running vulnerable configurations of PHP.

   ┌───────────────────────────────┐
   │     Unauthenticated Attacker  │
   └───────────────┬───────────────┘
                   │
                   ▼ 🟣 Exploit Payload
   ┌───────────────────────────────┐
   │   PHP Engine Core Processing  │
   │ (Stream Filters / PHAR Arch)  │
   └───────────────┬───────────────┘
                   │
                   ▼ ⚡
   ┌───────────────────────────────┐
   │   Arbitrary Shell Execution   │
   └───────────────────────────────┘

⚡ Vulnerability Details

ParameterDetails
VulnerabilitiesCVE-2026-109618 & CVE-2026-109619
CVSS v4.0 Score9.2 (Critical)
VectorCVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H
ImpactUnauthenticated Remote Code Execution (RCE)
Affected SoftwarePHP 5.x, PHP 7.x, PHP 8.0, 8.1, 8.2, 8.3, 8.4

🟣 Threat Breakdowns

1. CVE-2026-109618: Stream Filter Heap Memory Corruption

  • Mechanism: Memory safety breach triggered during internal buffer processing inside PHP stream filters.
  • Exploit Vector: Manipulation of stream parameters allows an attacker to control memory addresses and achieve code execution.

2. CVE-2026-109619: PHAR Archive Handling Logic Flaw

  • Mechanism: Flaw in the parsing and deserialization logic of PHP Archive (.phar) wrappers.
  • Exploit Vector: Attacker-controlled header inputs lead to arbitrary function invocation.

📸 Demo

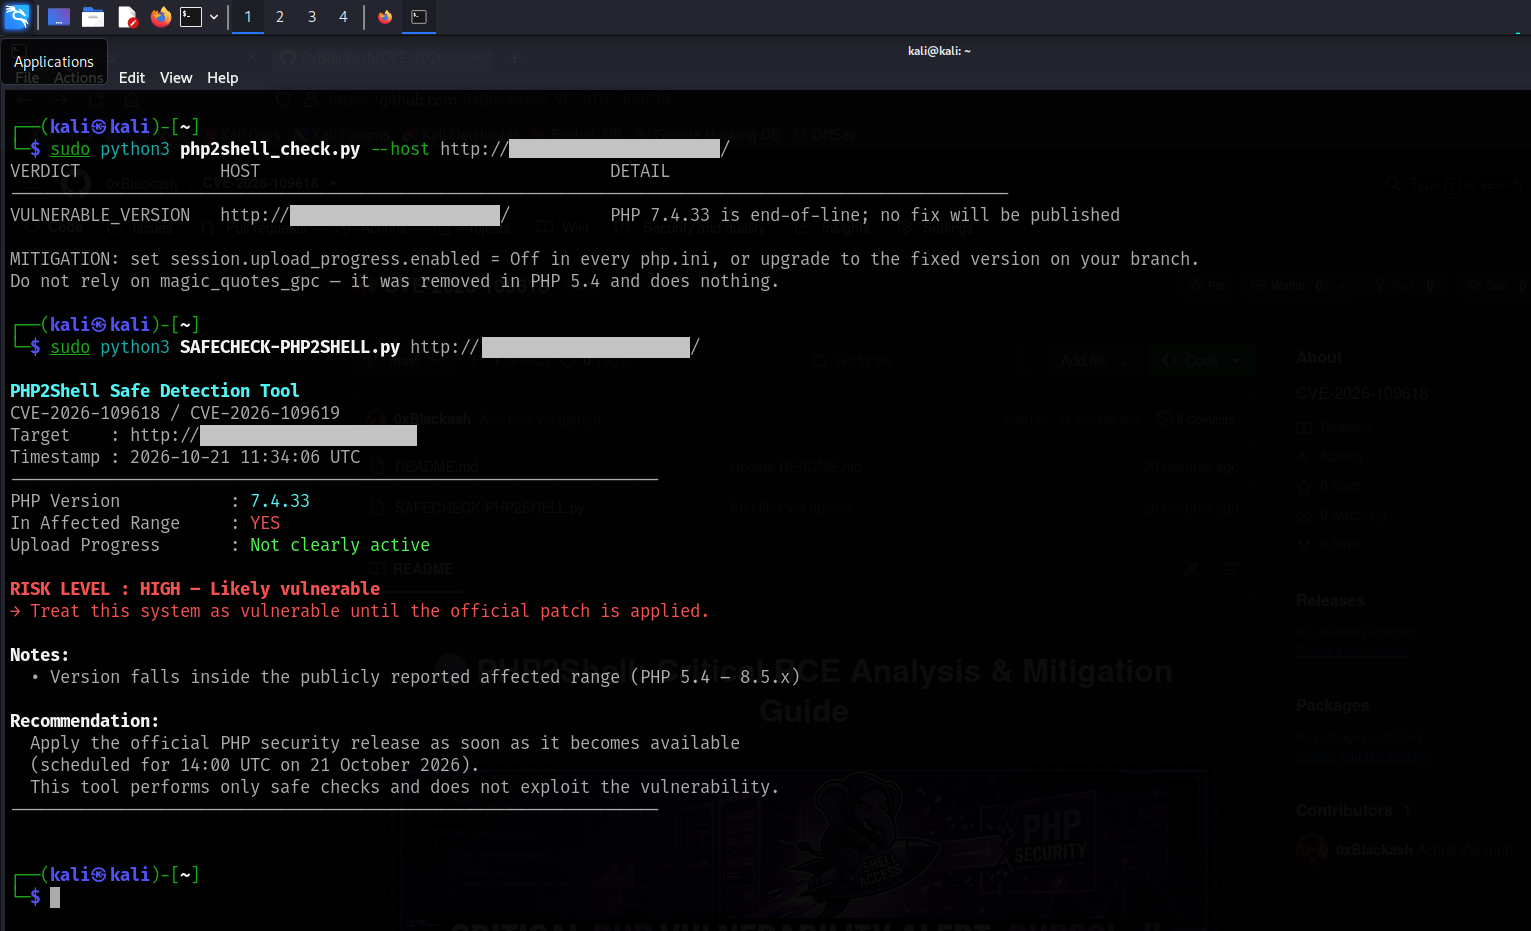
php2shell1 CVE-2026-109618yaml php2shell

🛡️ Mitigation & Remediation

1. Upgrade PHP Packages

The most effective fix is to update your server to the latest patched PHP binaries immediately:

# Debian / Ubuntu
sudo apt update && sudo apt install --only-upgrade php8.3-cli php8.3-fpm

# RHEL / CentOS / Rocky Linux
sudo dnf update php

2. Emergency Workarounds (For EOL Environments)

If your application relies on End-of-Life (EOL) versions (e.g., PHP 7.x or 8.0) that do not receive official security patches:

  • 🟣 Disable Stream Filters / Dangerous Functions: Edit your php.ini file:
disable_functions = exec,passthru,shell_exec,system,proc_open,popen,phar

  • 🟣 WAF / Network Filtering: Implement strict web application firewall (WAF) rules to drop requests containing serialized stream protocols (php://filter/, phar://).
  • 🟣 Network Isolation: Isolate legacy servers behind strict internal networks/VPNs.

🔍 Detection & Verification

To verify if your server running PHP is potentially vulnerable:

# Check running PHP version
php -v

# Check loaded modules and PHAR settings
php -i | grep -i "phar"


🤝 Contributing

Contributions, threat updates, and detection rules (YARA / Sigma) are welcome!

  1. Fork the repository
  2. Create a feature branch (git checkout -b feature/sigma-rule)
  3. Commit your changes (git commit -m 'Add Sigma detection rule')
  4. Push to the branch (git push origin feature/sigma-rule)
  5. Open a Pull Request

📜 Disclaimer

This repository is created purely for educational, defensive, and research purposes. The maintainers are not responsible for misuse or illegal activities performed with the information provided herein.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →