Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/0xblackash/cve-2026-101767
Vulnerability AnalysisExploitationWeb Application ExploitationPapers & ResearchLearning & Education
GitHub0xblackash/cve-2026-101767

CVE-2026-101767

Advisory and technical research analysis of CVE-2026-101767, a critical unauthenticated RCE in Oracle E-Business Suite Application Object Library, with CVSS details and affected versions.

View Repository
11 day agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

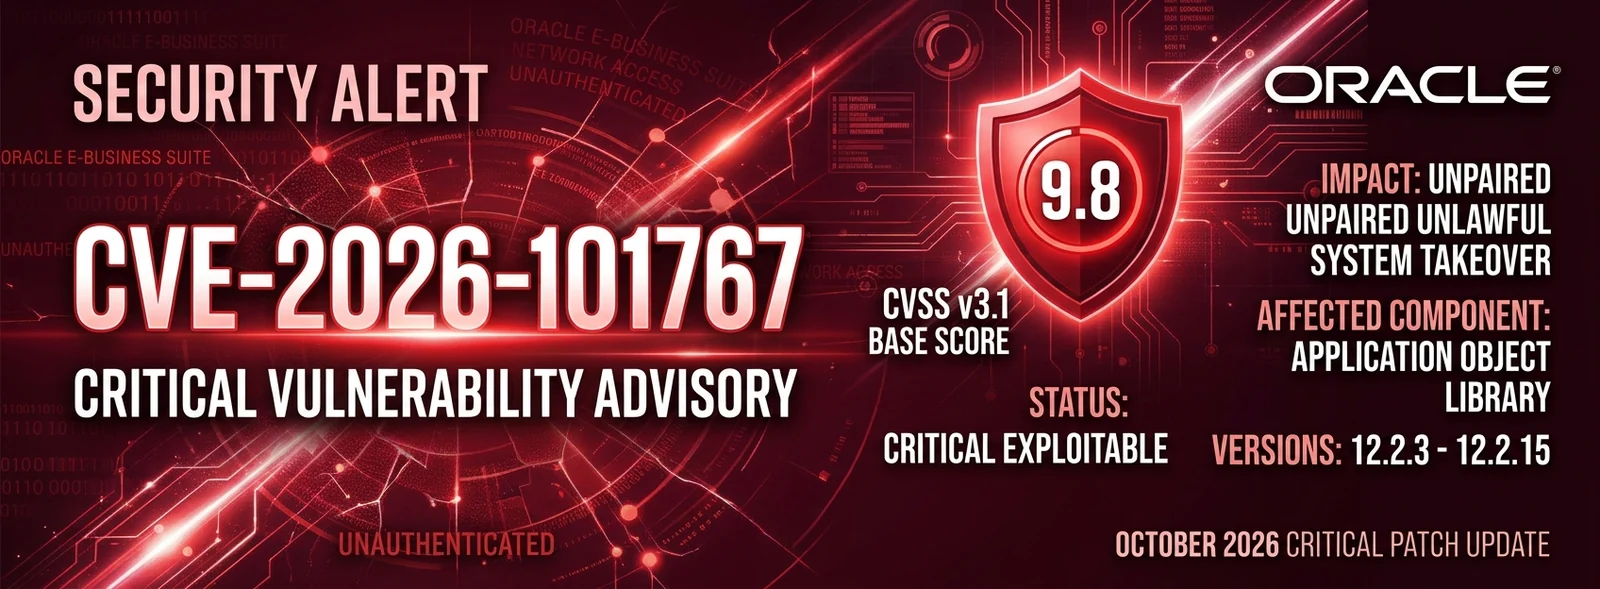
CVE-2026-101767: Oracle E-Business Suite Unauthenticated RCE

Gemini_Generated_Image_8ohgzv8ohgzv8ohg

CVE Badge CVSS Badge Oracle Badge License

An advisory and research analysis on CVE-2026-101767, a critical unauthenticated remote vulnerability in Oracle E-Business Suite (Oracle Application Object Library) disclosed in the Oracle October 2026 Critical Patch Update (CPU).


📋 Overview

  • CVE ID: CVE-2026-101767
  • Vulnerability Type: Unauthenticated Remote Access / Vulnerability in Application Object Library
  • Severity Score: 9.8 (Critical)
  • CVSS v3.1 Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
  • Affected Component: Core / Oracle Application Object Library
  • Patch Availability: Released in Oracle October 2026 CPU

🎯 Target & Affected Versions

This vulnerability impacts all deployments running the following versions of Oracle E-Business Suite:

ProductComponentAffected Versions
Oracle E-Business SuiteApplication Object Library12.2.3 – 12.2.15

🛡️ Technical Summary

CVE-2026-101767 allows an unauthenticated attacker with network access over HTTP to compromise the Oracle Application Object Library.

Attack Properties

  • Attack Vector (AV): Network (N)
  • Attack Complexity (AC): Low (L)
  • Privileges Required (PR): None (N)
  • User Interaction (UI): None (N)
  • Impact: High Confidentiality, High Integrity, High Availability (C:H/I:H/A:H)

Successful exploitation can result in a complete compromise of the underlying application server, enabling arbitrary code execution, sensitive data extraction, or persistent backdoor installation.
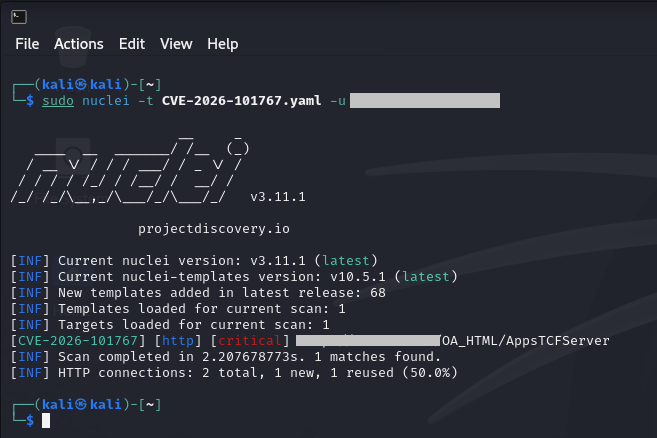

📸 Demo

cve-2026-101767

⚙️ Detection & Testing

(Optional: Insert detection queries, YARA rules, or vulnerability scanning guidance here)

# Example Detection Check / HTTP Endpoint Status (Placeholder)
curl -s -I "http://<target-host>:<port>/OA_HTML/..." | grep "HTTP/1.1"

⚠️ Disclaimer

This repository is provided for educational and research purposes only. The author is not responsible for any misuse of the information or materials contained herein.

Download Tool