

MemProcFS v5.18
MemProcFS
MemProcFS:
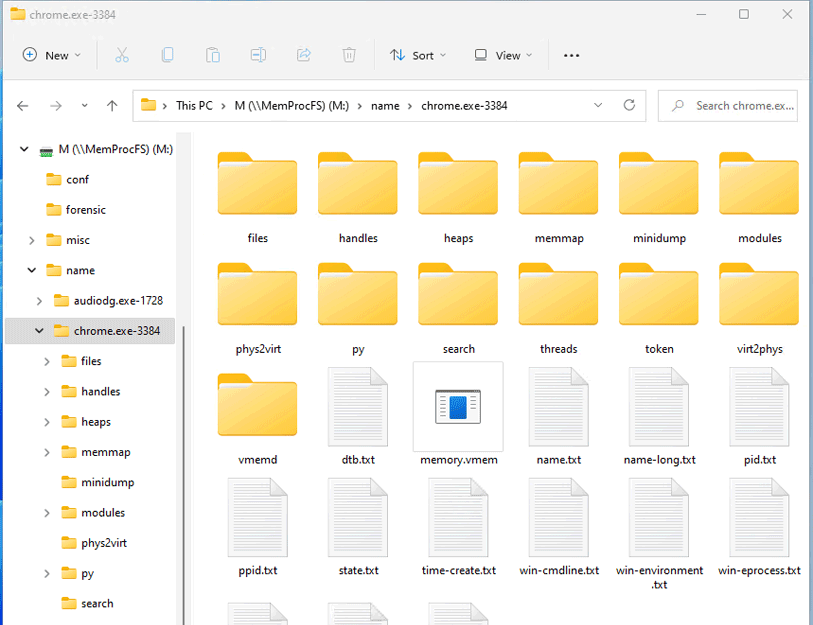
MemProcFS is an easy and convenient way of viewing physical memory as files in a virtual file system.
Easy trivial point and click memory analysis without the need for complicated commandline arguments! Access memory content and artifacts via files in a mounted virtual file system or via a feature rich application library to include in your own projects!
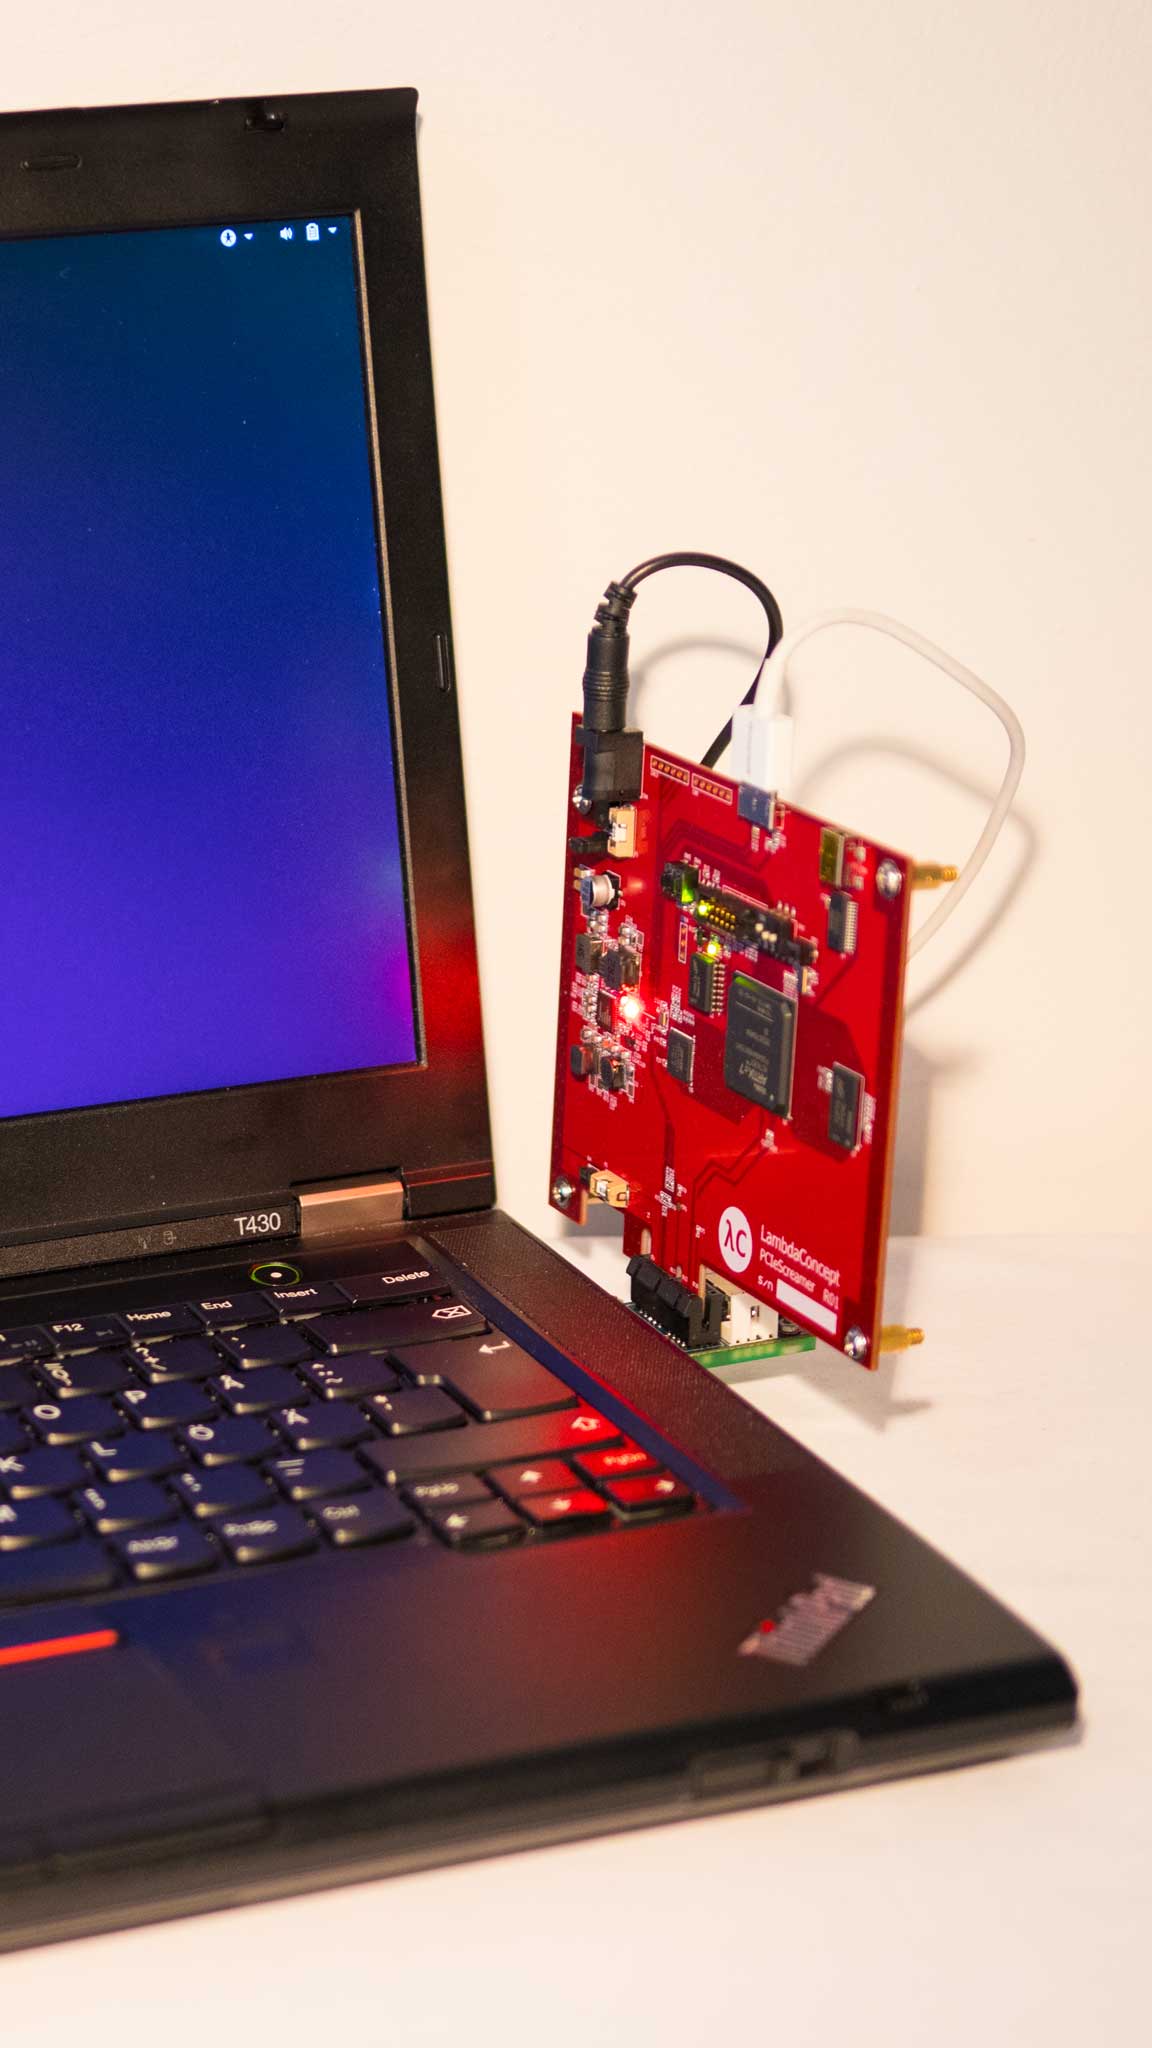
Analyze memory dump files, live memory via DumpIt or WinPMEM, live memory in read-write mode from virtual machines or from PCILeech FPGA hardware devices!
It's even possible to connect to a remote LeechAgent memory acquisition agent over a secured connection - allowing for remote live memory incident response - even over higher latency low band-width connections! Peek into Virtual Machines with MemProcFS, LiveCloudKd or VMware!
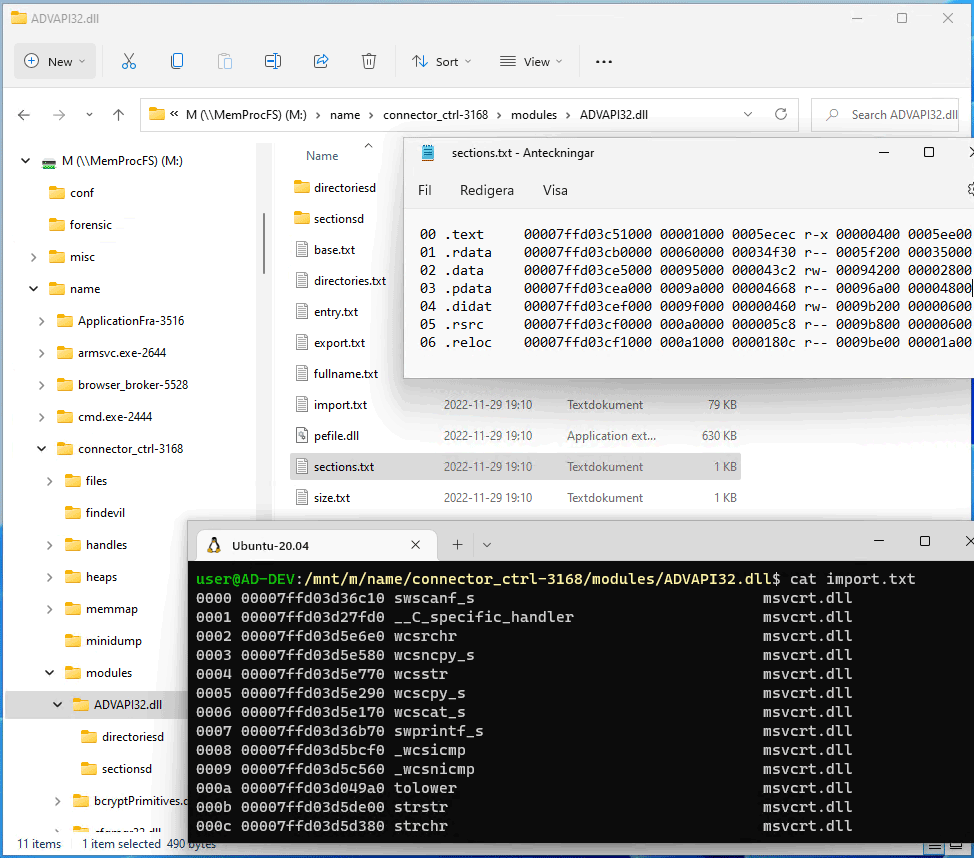
Use your favorite tools to analyze memory - use your favorite hex editors, your python and powershell scripts, WinDbg or your favorite disassemblers and debuggers - all will work trivally with MemProcFS by just reading and writing files!
Get Started!
Check out the excellent quick walkthrough from 13Cubed to get going! Also check out my older conference talks from Disobey and BlueHat.

For additional documentation check out the project wiki for in-depth detailed information about the file system itself, its API and its plugin modules! For additional information about memory acqusition methods check out the LeechCore project or hop into the PCILeech/MemProcFS Discord server!
To get going download the latest binaries, modules and configuration files and check out the guide!
Installing:
Get the latest binaries, modules and configuration files from the latest release. Alternatively clone the repository and build from source.
Windows
Mounting the file system requires the Dokany file system library to be installed. Download and install the latest version of Dokany version 2 at: https://github.com/dokan-dev/dokany/releases/latest
To capture live memory (without PCILeech FPGA hardware) download DumpIt and start MemProcFS via DumpIt /LIVEKD mode. Alternatively, get WinPMEM by downloading the most recent signed WinPMEM driver and place it alongside MemProcFS - detailed instructions in the LeechCore Wiki.
PCILeech FPGA will require hardware as well as FTD3XXWU.dll to be dropped alongside the MemProcFS binaries. Please check out the LeechCore project for instructions.
Linux
MemProcFS should be possible to run out-of-the-box on most Linux distros with FUSE installed. If building from source check out the guide about MemProcFS on Linux.
macOS
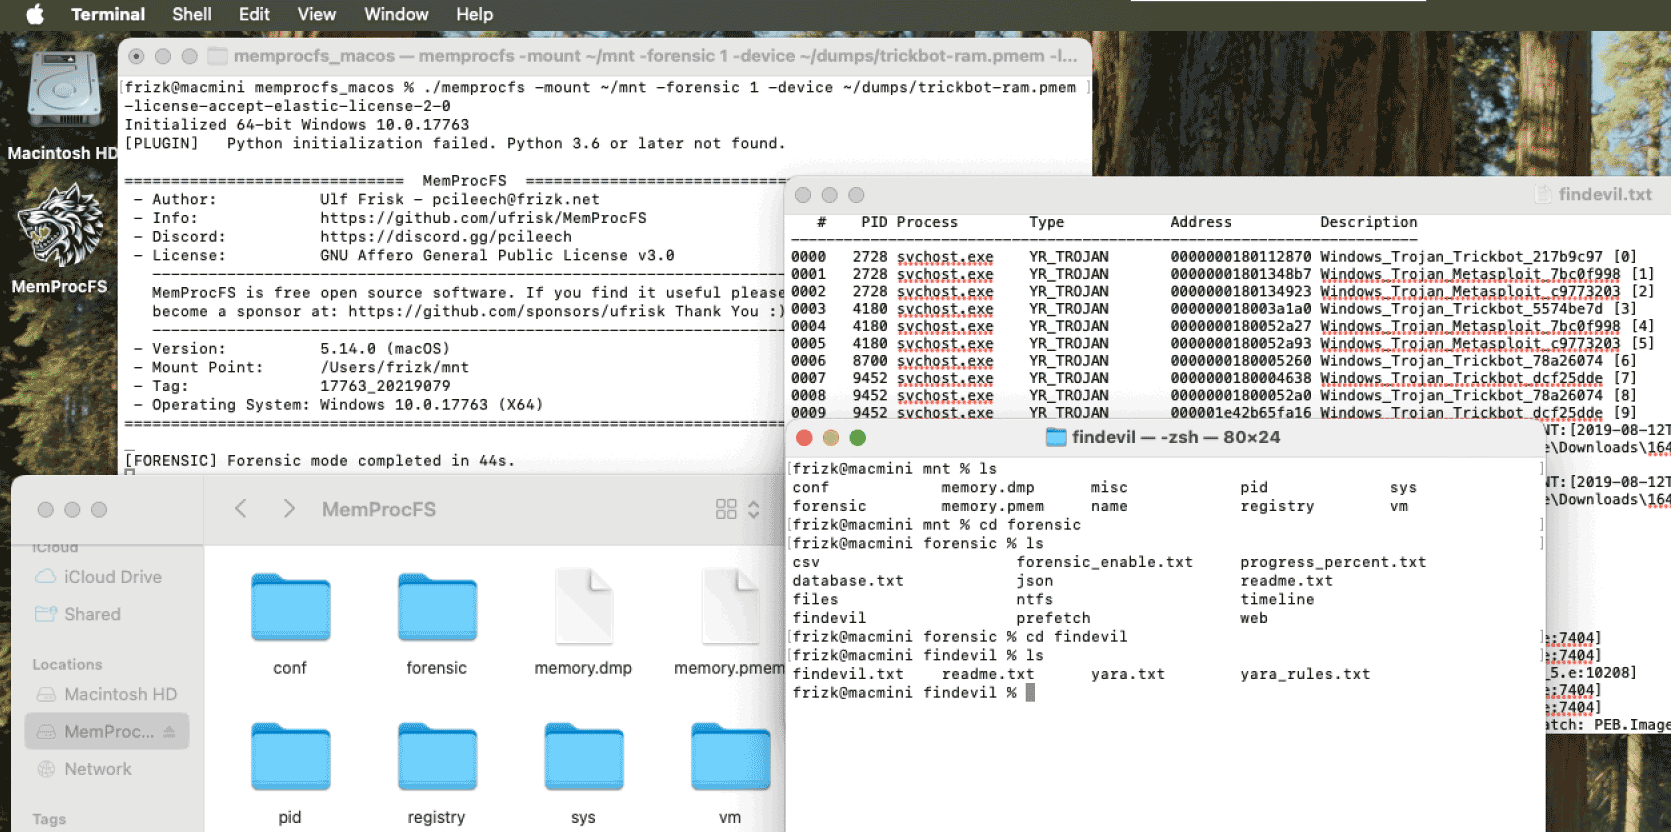
Download the latest MemProcFS release from here. MemProcFS when used as a mounted virtual file system depends on macFuse which requires a .kext. Download and install macFuse here. If MemProcFS is used via the supported C/C++/Rust APIs macFuse is not required.
Extensive Python, Rust, Java, Go, C# and C/C++ API:
Include MemProcFS in your C/C++, C#, Java, Go (3rd party), Python or Rust programming projects! Everything in MemProcFS is exposed via an easy-to-use API for use in your own projects! The Plugin friendly architecture allows users to easily extend MemProcFS with C/C++/Rust/Python plugins!
Everything in MemProcFS is exposed as APIs. APIs exist for both C/C++ vmmdll.h, C# nuget package, Java, Python pip package and Rust crate. The file system itself is made available virtually via the API without the need to mount it. It is possible to read both virtual process memory as well as physical memory! The example below shows reading 0x20 bytes from physical address 0x1000:
>>> import memprocfs
>>> vmm = memprocfs.Vmm(['-device', 'c:/temp/win10_memdump.raw'])
>>> print(vmm.hex( vmm.memory.read(0x1000, 0x20) ))
0000    e9 4d 06 00 01 00 00 00  01 00 00 00 3f 00 18 10   .M..........?...
0010    00 00 00 00 00 00 00 00  00 00 00 00 00 00 00 00   ................
MemProcFS is available as a Python pip package and it's easy to integrate in your Jupyter Notebooks.
Examples:
Start MemProcFS from the command line - possibly by using one of the examples below.
Or register the memory dump file extension with MemProcFS.exe so that the file system is automatically mounted when double-clicking on a memory dump file!