
 #1
Tools for testing, exploiting, and securing web applications and APIs.
Kitploit recommended

 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 ariary/notionterm
Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…
 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
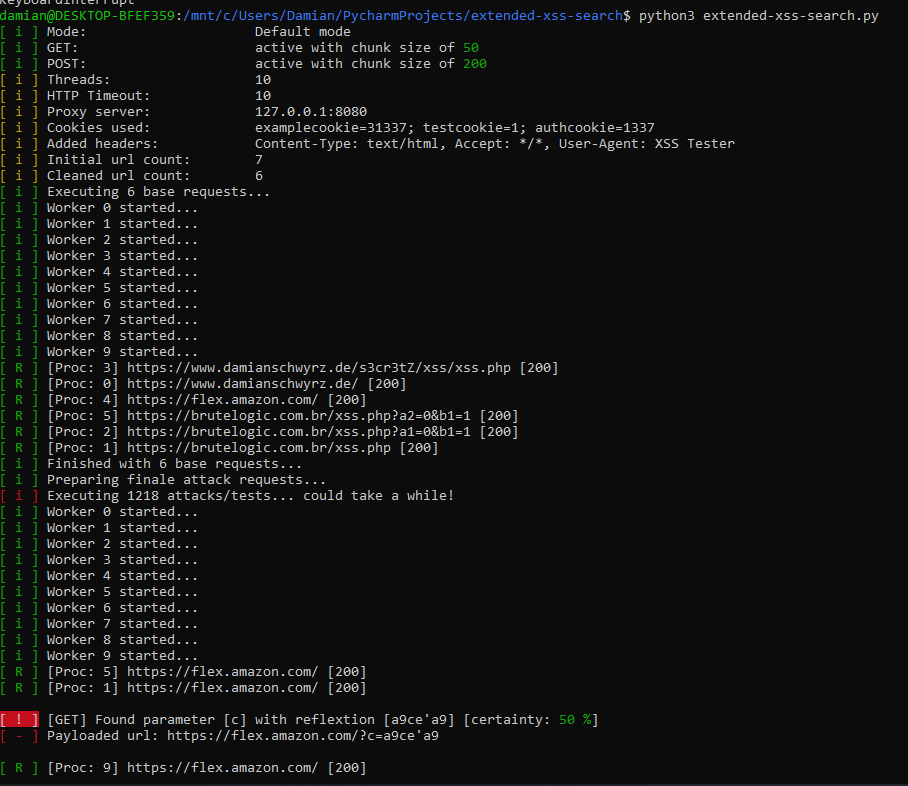 damian89/extended-xss-search
A better version of my xssfinder tool - scans for different types of xss on a list of urls.
 mrmtwoj/apache-vulnerability-testing
Apache HTTP Server Vulnerability Testing Tool | PoC for CVE-2024-38472 , CVE-2024-39573 , CVE-2024-38477 , CVE-2024-38476 , CVE-2024-38475 ,…
 efchatz/http3-attacks
Educational exploit scripts for HTTP/3 attacks (CVE-2022-30592) including HTTP3-loris, HTTP3-stream, and HTTP3-flooding, tested against QUIC-enabled…
 w01fh4cker/screenconnect-authbypass-rce
Exploit script for CVE-2024-1708 and CVE-2024-1709 in ConnectWise ScreenConnect, enabling authentication bypass and remote code execution with user…
 saelo/jscpwn
PoC exploit for CVE-2016-4622
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
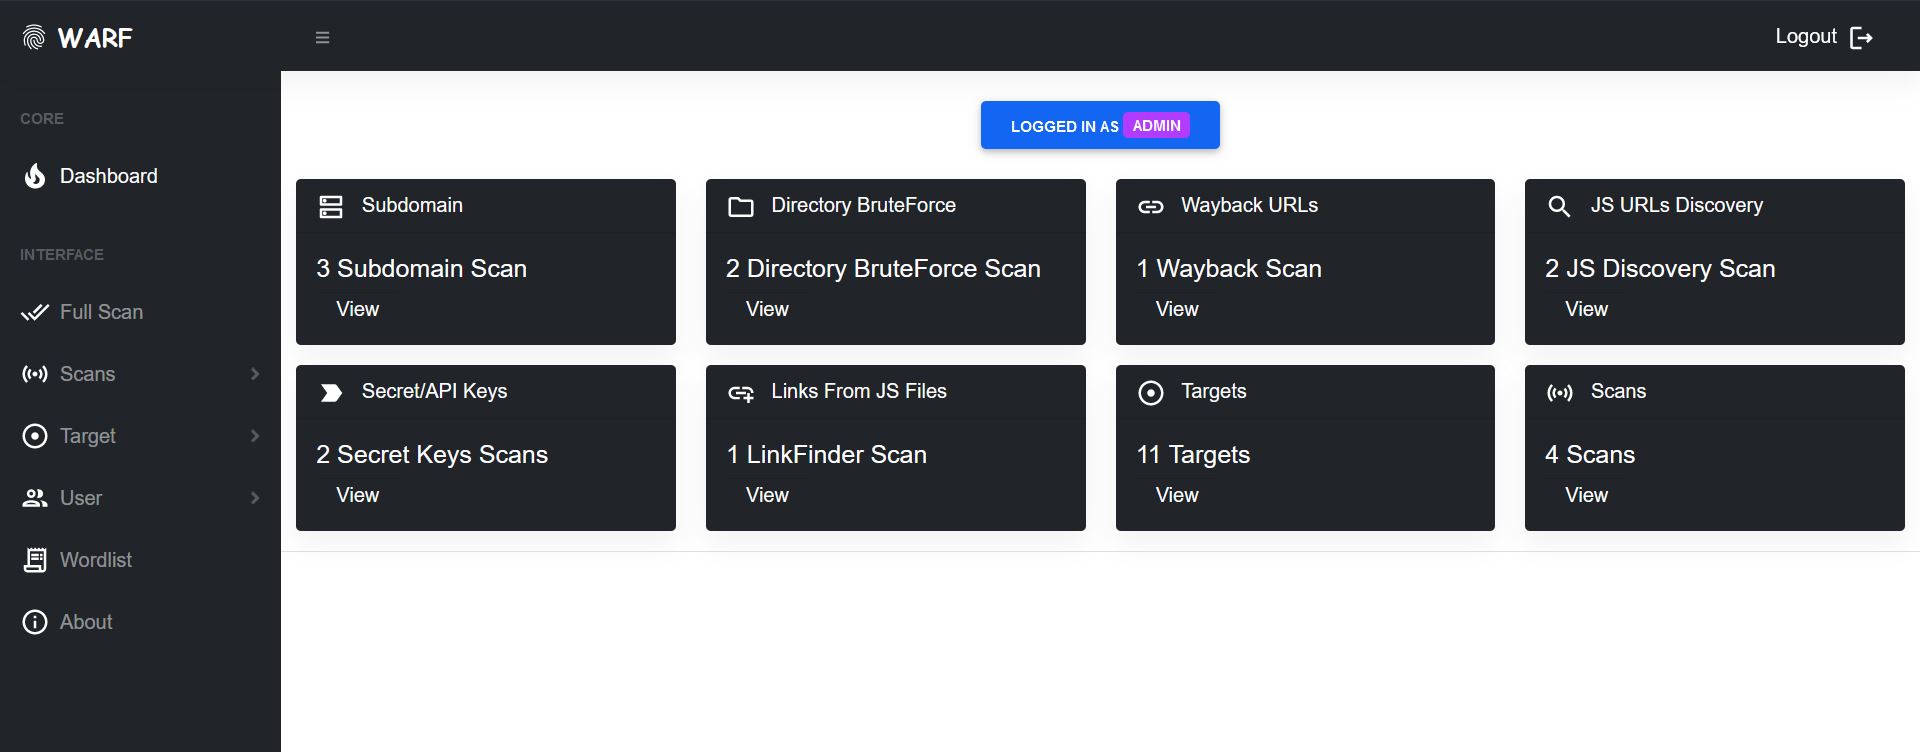 iamnihal/warf
Modular web application reconnaissance framework for automated subdomain enumeration, directory brute-forcing, and extraction of endpoints, JS URLs,…
 eqstlab/cve-2026-94545
Proof-of-concept exploit for CVE-2026-94545, an unauthenticated RCE in Next.js next/og via SVG injection and a ROP chain against the native sharp…
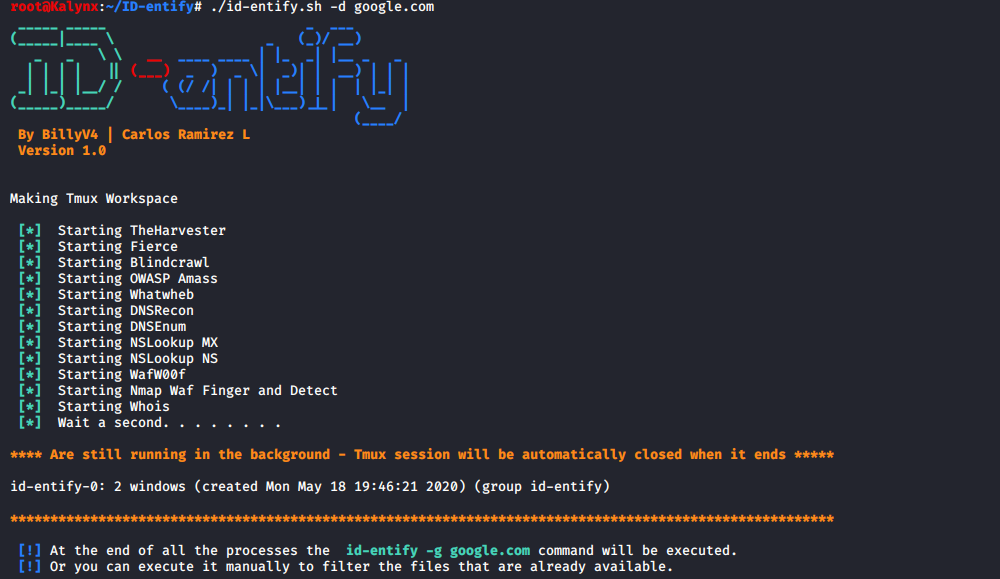 billyv4/id-entify
Search for information related to domain: Emails - IP addresses - Sub-Domains - Information on WEB technology - Type of Firewall - NS and MX records.
 alexbakker/log4shell-tools
Tool that runs a test to check whether one of your applications is affected by the recent vulnerabilities in log4j: CVE-2021-44228 and CVE-2021-45046
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
 gabrielg/cve-2014-1266-poc
Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 polakow/cve-2022-21907
A REAL DoS exploit for CVE-2022-21907
 nccgroup/pcap-burp
Pcap importer for Burp








