
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended
 jarryshaw/darc
Darkweb crawler that uses requests and Selenium workers to fetch pages, capture headers and cookies, extract links, and save rendered screenshots for…
 pion/dtls
Native Go implementation of DTLS 1.2 and 1.3 with ECDHE and PSK key exchange, AEAD ciphers, connection IDs, session resumption, 0-RTT, and Encrypted…
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 googlesky/cve-2026-126274
Differential PoC lab for CVE-2026-126274, a stored XSS in NocoDB's table-deletion dialog, verifying the innerHTML sink in served bundles against…
 completetech-security/php2shell-check
Passive PHP2Shell (CVE-2026-109618, CVE-2026-109619) exposure checker with branded HTML reports. Single-file Python, no dependencies, no exploit…
 googlesky/cve-2026-126269
Differential proof-of-concept lab for CVE-2026-126269, a NocoDB stored XSS via attachment MIME allow-list bypass that serves attacker HTML inline…
 googlesky/cve-2026-126273
Differential PoC lab for CVE-2026-126273: exploits NocoDB's skipped admin bootstrap so the first unauthenticated signup gains Super Admin, and…
 googlesky/cve-2026-128014
Proof-of-concept and differential lab for CVE-2026-128014: a two-chunk Brotli stream pins FrankenPHP 1.13.1 request workers in a non-terminating…
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 ph4ntom-rev/ph4ntom-vitrum
In-vitro static malware dissection pipeline for Telegram, AI agents (Antigravity / Local Ollama / OpenCode), and IDA Pro 9.5 via ph4ntom-ida-bridge
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
 likithmanoj/nhi-risk-analyzer
Discovers, risk-assesses, and remediates non-human identities across AWS, Azure, and GCP using offline rule-based analysis, privilege-escalation…
 rtkwlf/wolf-tools
Scans Windows, Linux, and macOS hosts for Java packages containing JndiLookup.class to detect Log4Shell (CVE-2021-44228, CVE-2021-45046) exposure and…
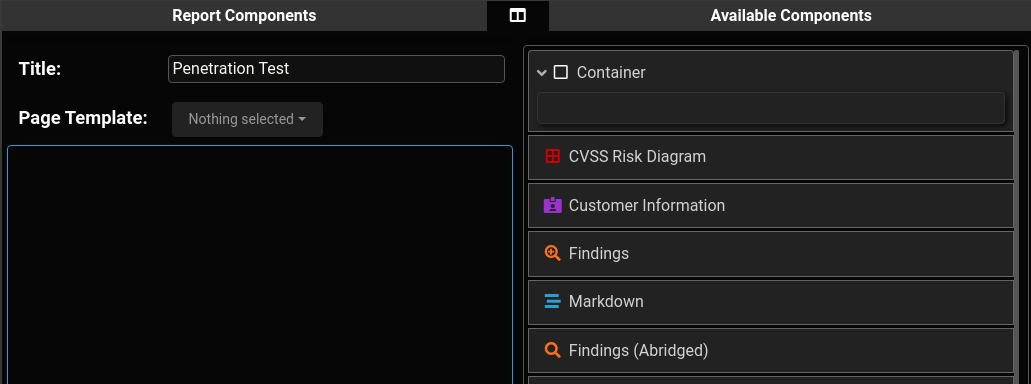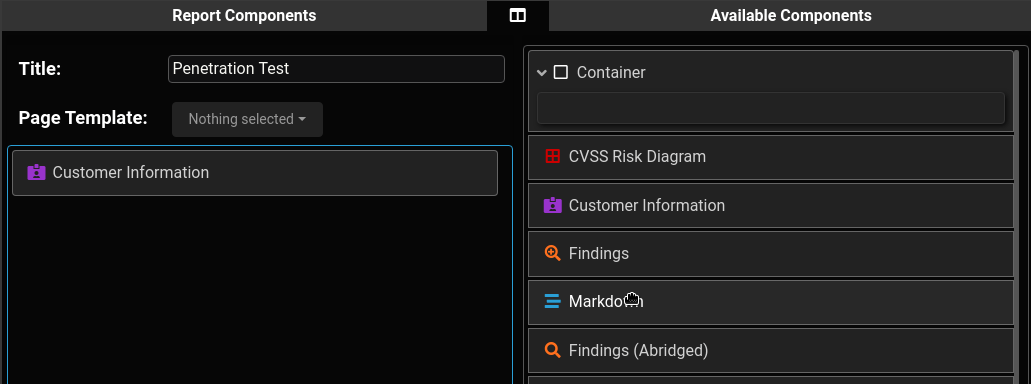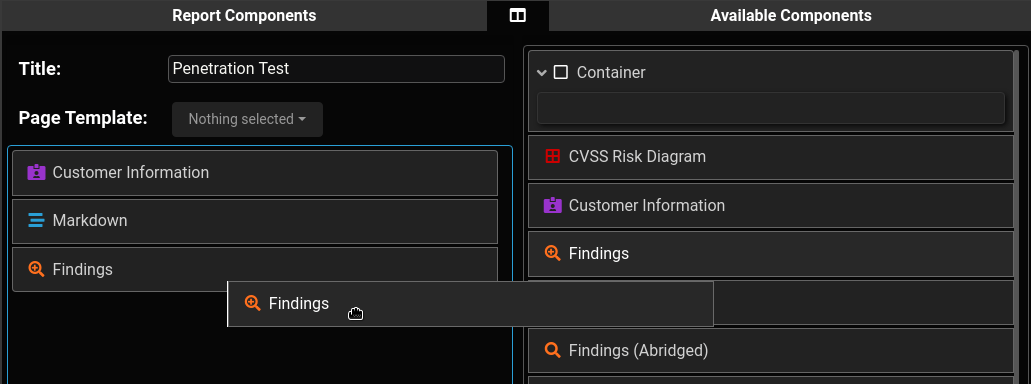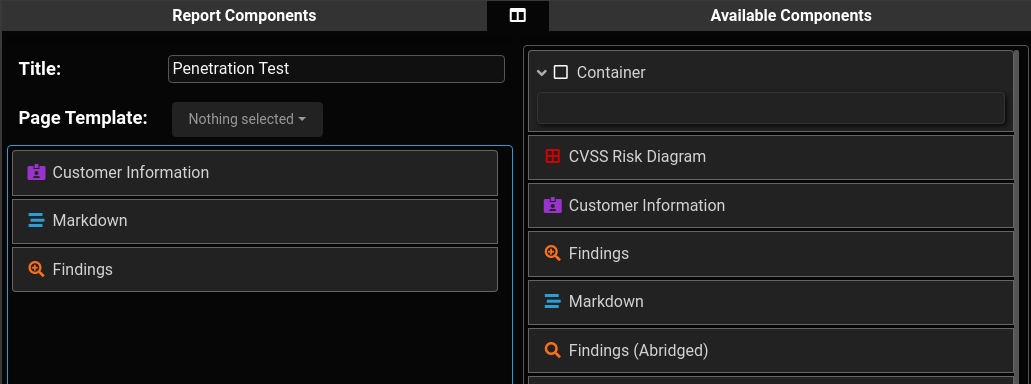 blacklanternsecurity/writehat
A pentest reporting tool written in Python. Free yourself from Microsoft Word.

 brn1337/mailauthcheck
Bash script that audits SPF, DKIM, DMARC, DNSSEC, MTA-STS and DNS hygiene to grade a domain's exposure to email spoofing and phishing.
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…








